
WhatTheHack
 microsoft/whatthehack
A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …
ai-securitycloud-infrastructure-securitycloud-security+6
1.9k
microsoft/whatthehackA collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …
 mondoohq/cnspec
An open source, cloud-native security to protect everything from build to runtime
 dsccommunity/certificatedsc
DSC resources to simplify administration of certificates on a Windows Server.
 prowler-cloud/prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 automatedlab/automatedlab
PowerShell-based provisioning framework for deploying complex lab environments on Hyper-V and Azure. Supports Windows, Linux, and products like AD,…
 mitiga/log4shell-cloud-scanner
we are providing DevOps and security teams script to identify cloud workloads that may be vulnerable to the Log4j vulnerability(CVE-2021-44228) in…
 mlazzarotto/copy-fail-cve-2026-31431-mitigation-ansible-playbook
An Ansible Playbook to mitigate the vulnerability CVE-2026-31431 on RHEL-based and Debian-based OSes.
 iknowjason/purplecloud
A little tool to play with Azure Identity - Azure and Entra ID lab creation tool. Blog: https://medium.com/@iknowjason/sentinel-for-purple-teaming-1…
 mrk336/azure-networking-privilege-escalation-exploit-cve-2025-54914
CVE-2025-54914 exposes a critical flaw in Azure Networking that allows attackers to escalate privileges and control routing across subnets. The…
 oseguera12/cowrie-honeypot-digitalocean
Medium-interaction SSH/Telnet honeypot built with Cowrie, Loki, Promtail, and Grafana - provisioned on DigitalOcean via Terraform with a GitLab CI…
 cloud-custodian/cloud-custodian
Rules engine for cloud security, cost optimization, and governance, DSL in yaml for policies to query, filter, and take actions on resources
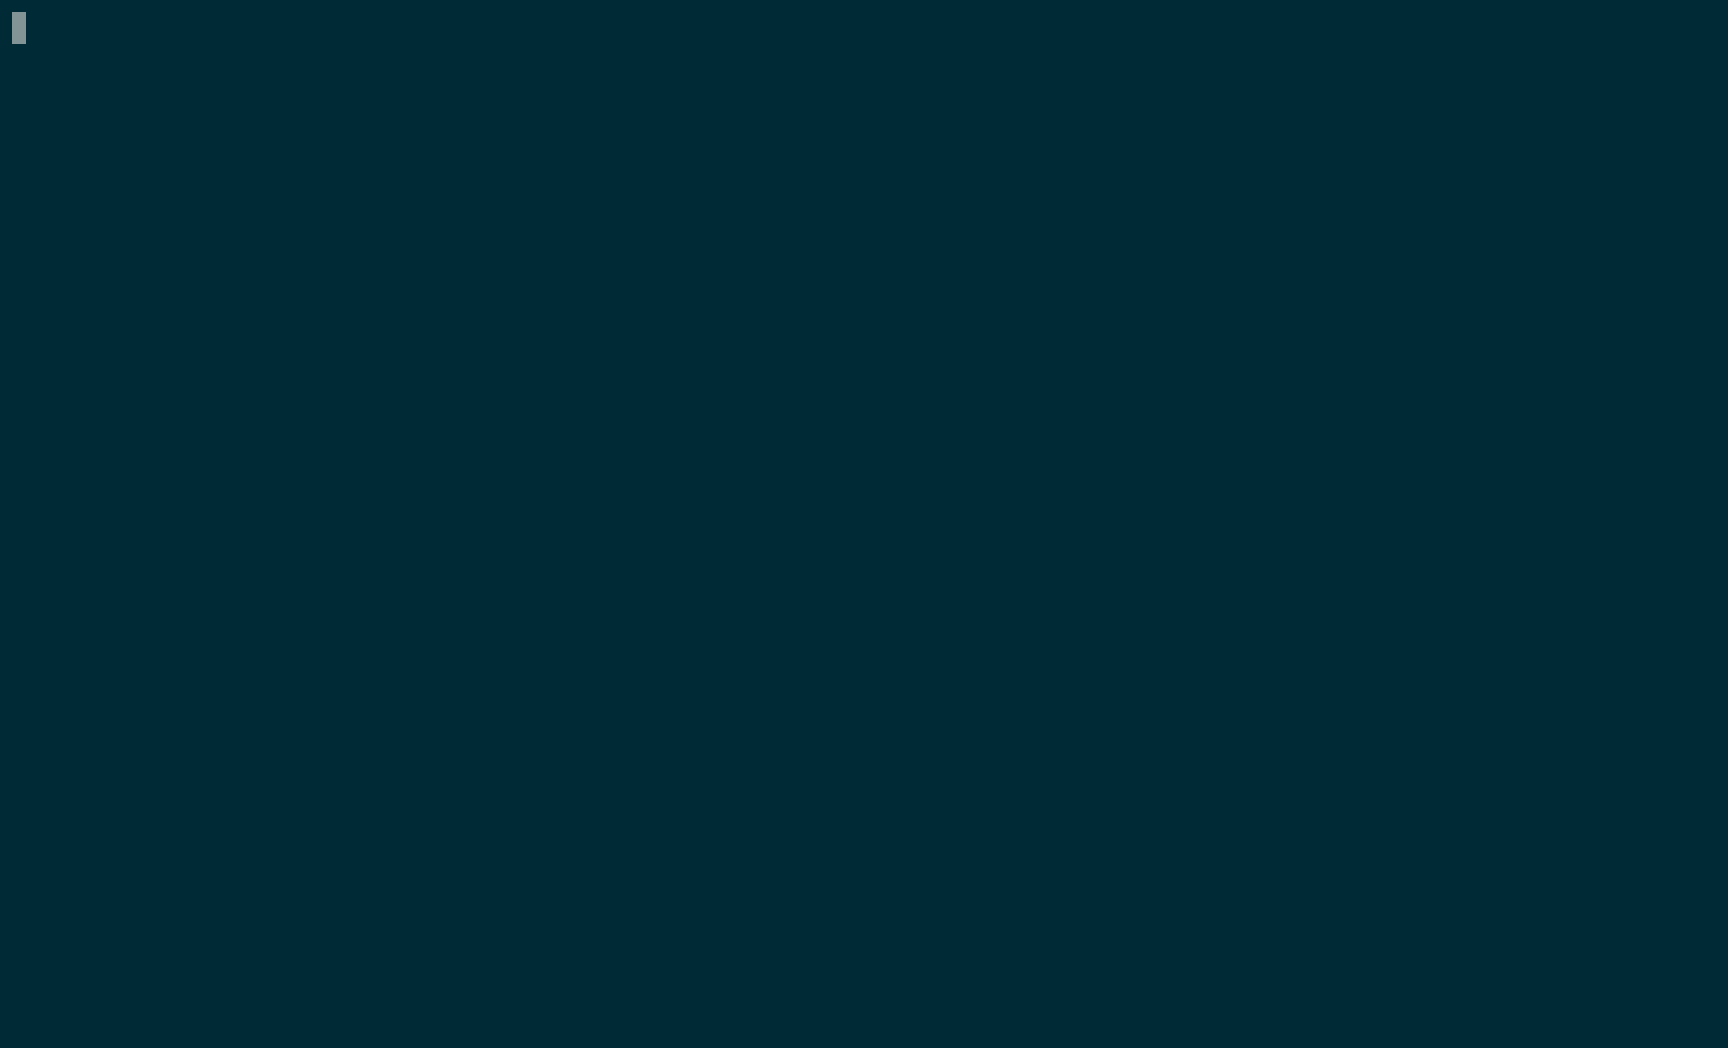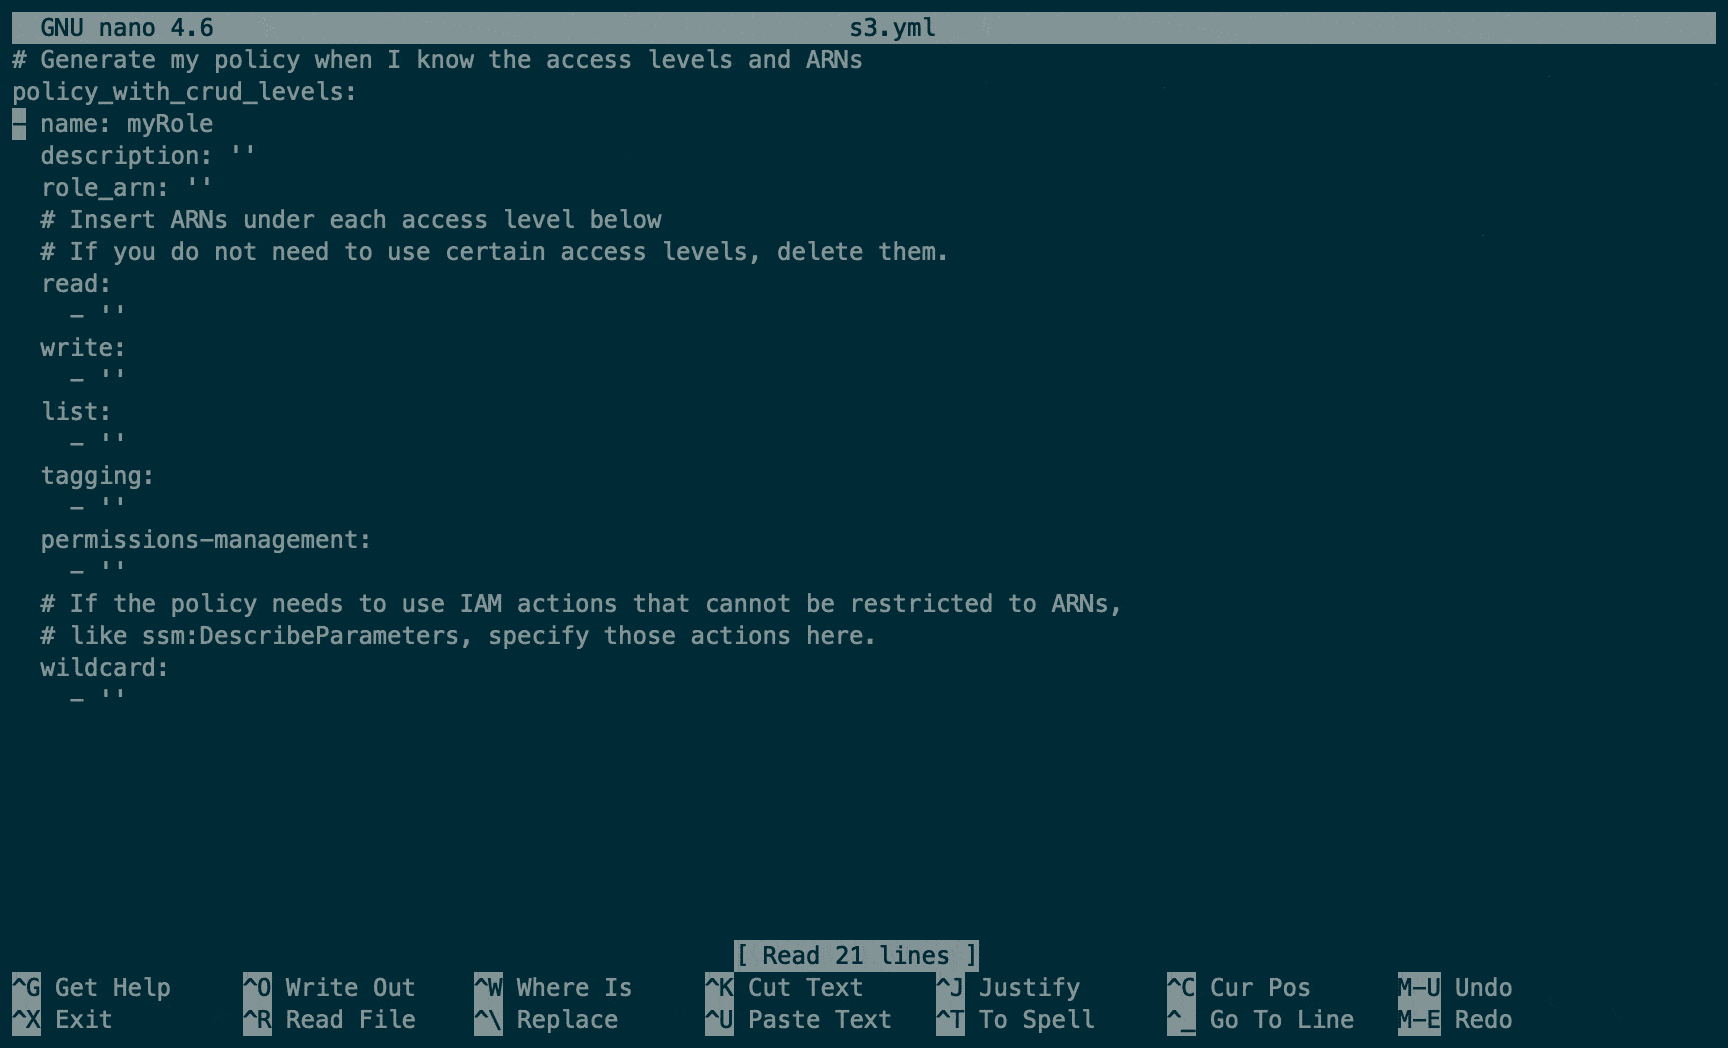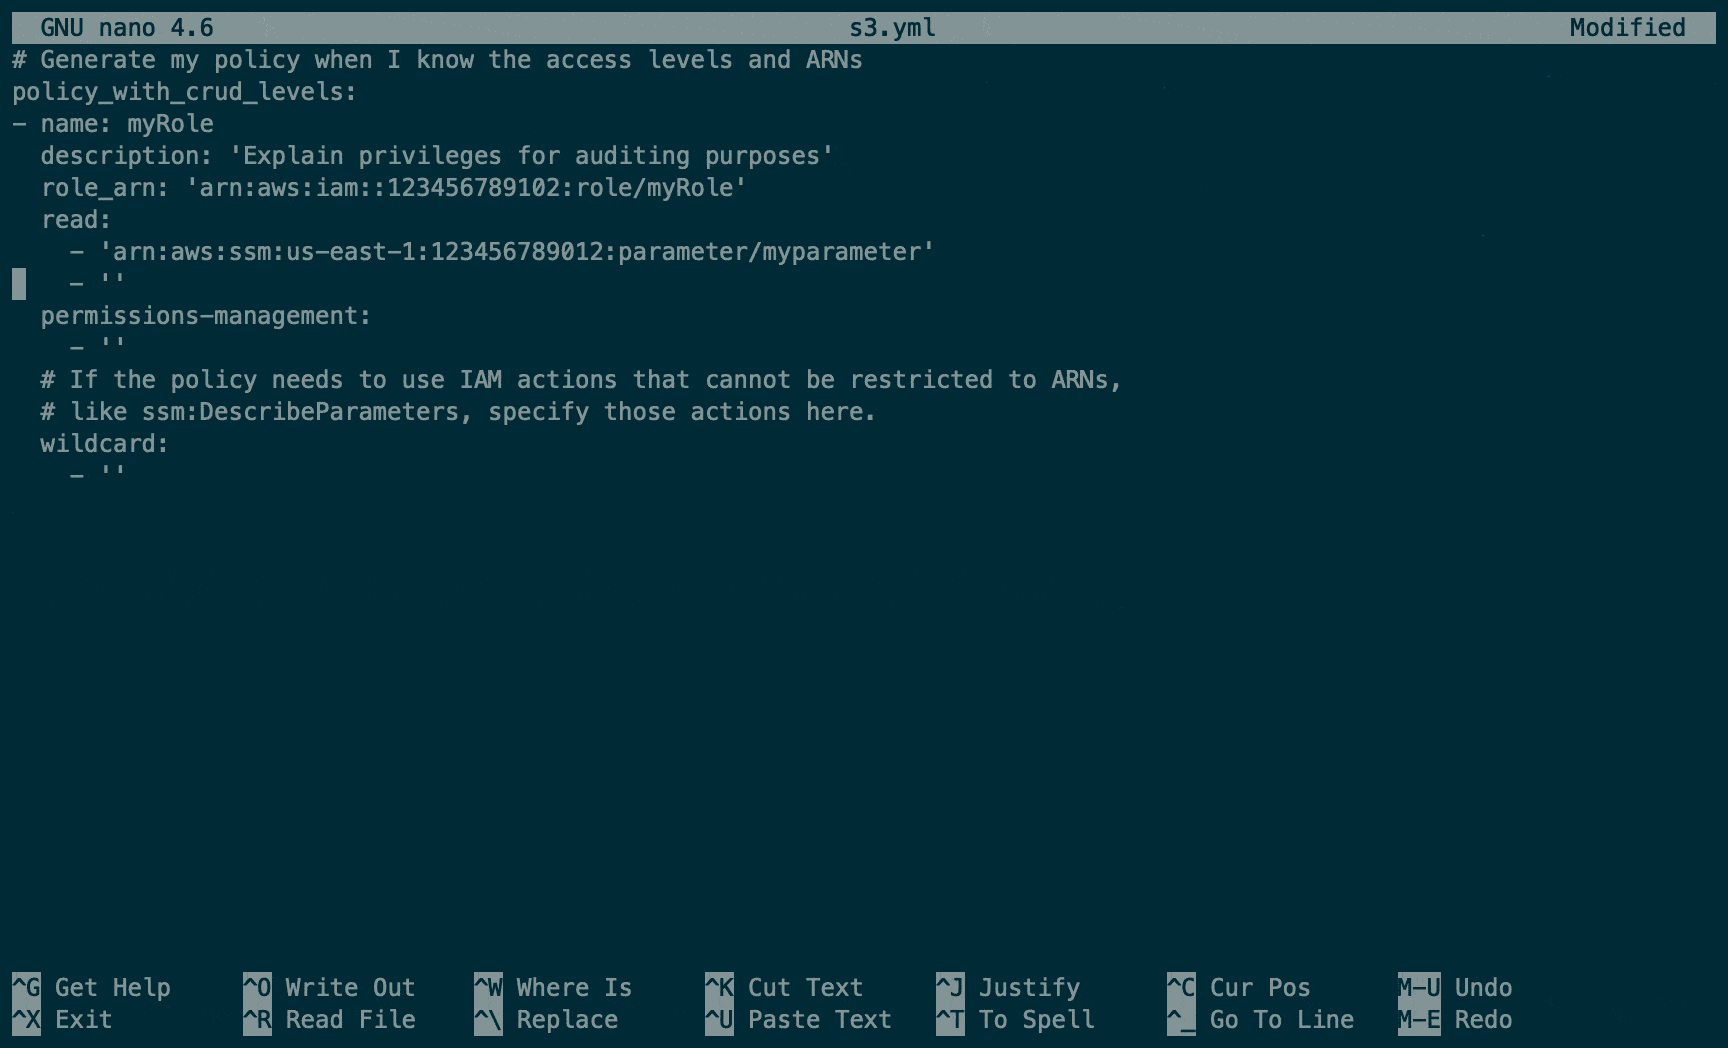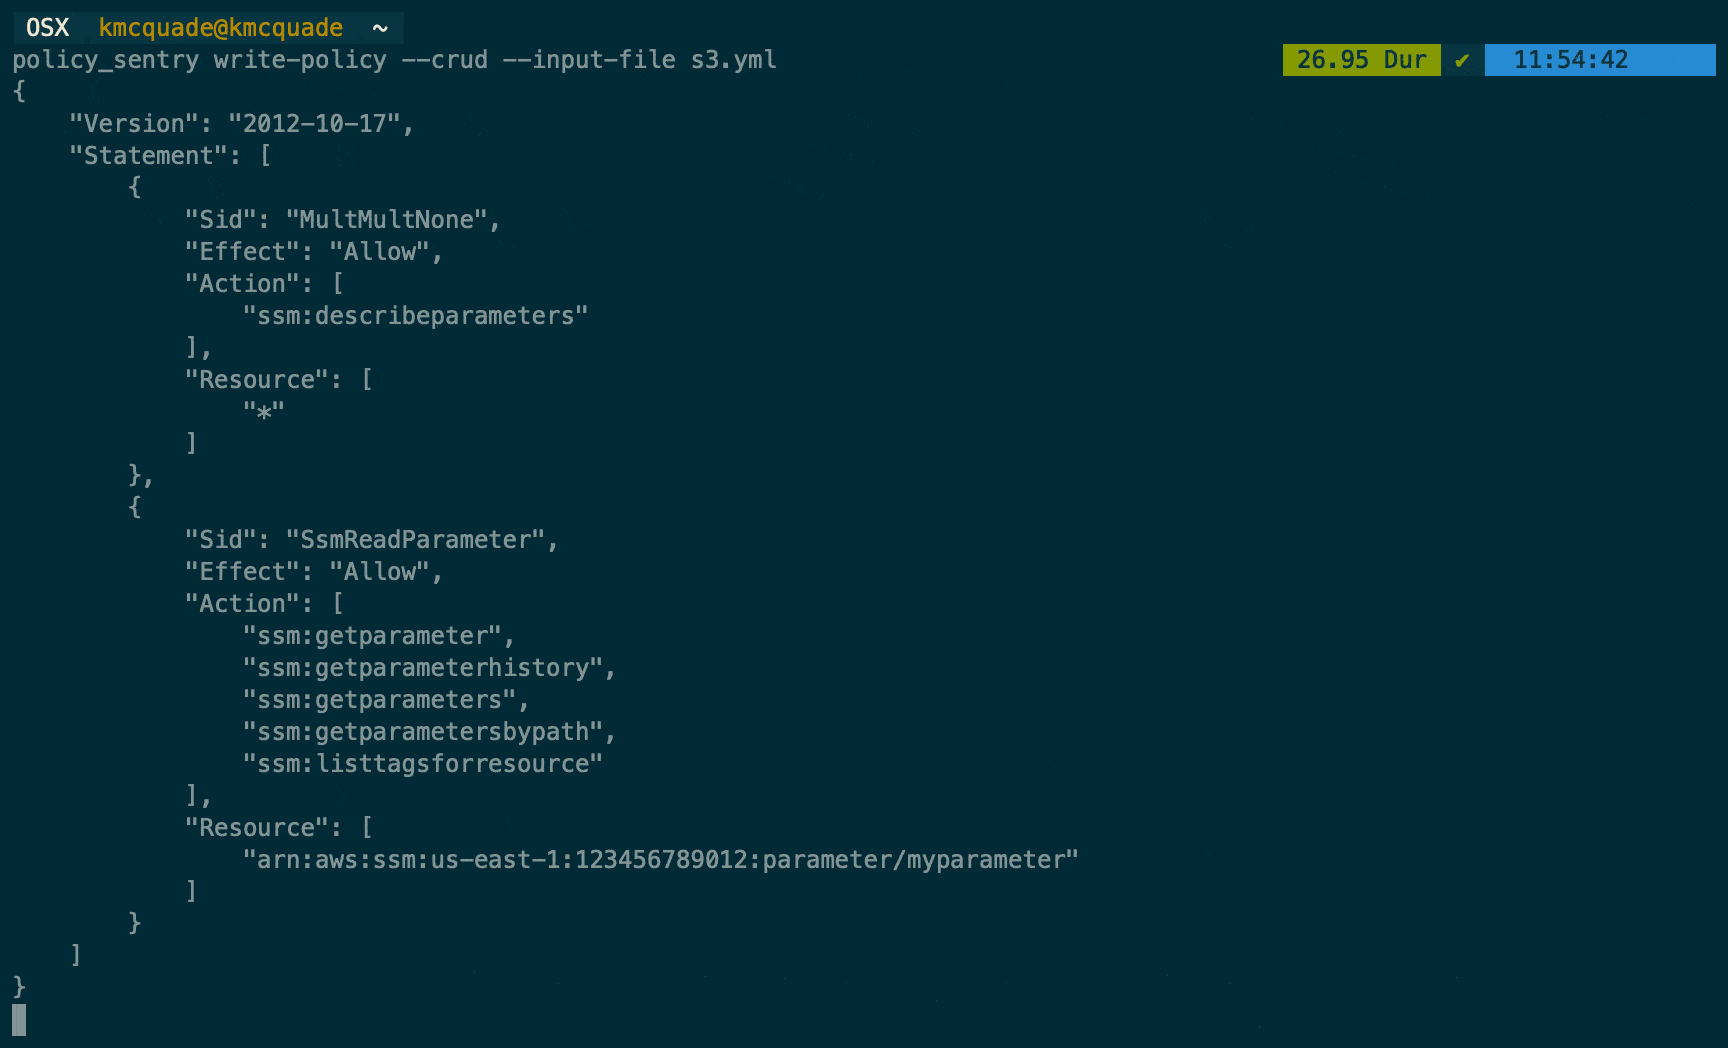 salesforce/policy_sentry
Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.
 eximiait/cve-2026-31431
Ansible playbooks to check and mitigate CVE-2026-31431 on Linux hosts, with scripts for local, remote, and containerized environments, including…
 joshlarsen/aws-recon
Multi-threaded AWS inventory collection tool with a focus on security-relevant resources and metadata.
 anssi-fr/dfir4vsphere
Powershell module for VMWare vSphere forensics
 tailwindrg/cve-2026-0300-audit
Read-only audit tooling for CVE-2026-0300 (PAN-OS User-ID Authentication Portal exposure)
 zzugab/juice-shop-with-kubeadm-and-tf
Automated deployment of OWASP Juice Shop on Kubernetes using kubeadm and Terraform, with integrated Trivy vulnerability scanning for DevSecOps…