Juice Shop With Kubeadm and Tf

Automated deployment of OWASP Juice Shop on Kubernetes using kubeadm and Terraform, with integrated Trivy vulnerability scanning for DevSecOps…

Automated deployment of OWASP Juice Shop on Kubernetes using kubeadm and Terraform, with integrated Trivy vulnerability scanning for DevSecOps…

Lord Of Active Directory - automatic vulnerable active directory on AWS

Prevent SSRF attacks on AWS EC2 via automated upgrades to the more secure Instance Metadata Service v2 (IMDSv2).

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

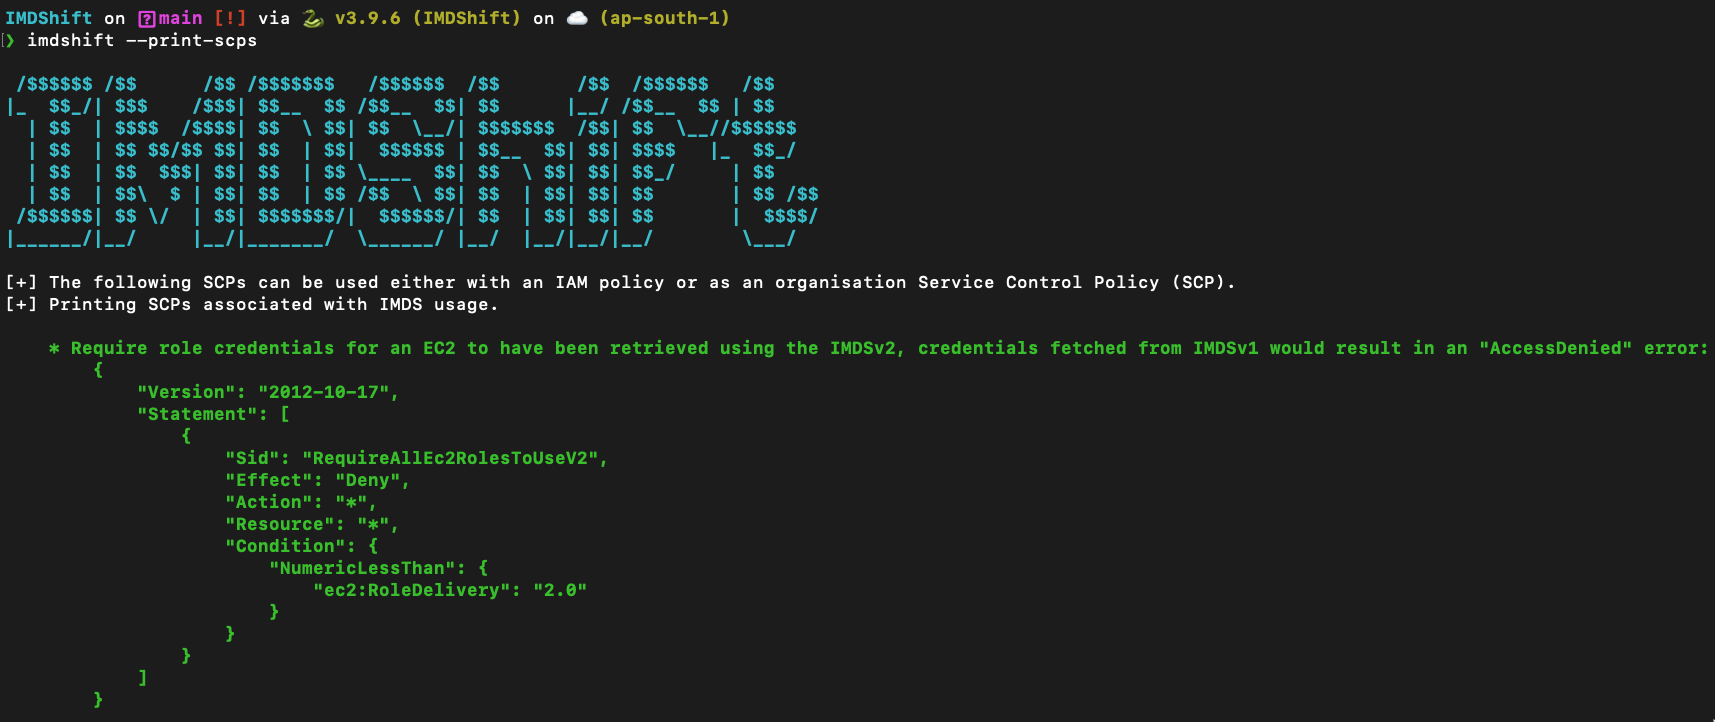
Automates migration of AWS workloads from IMDSv1 to IMDSv2 to mitigate SSRF attacks. Detects IMDSv1 usage across EC2, ECS, EKS, Lightsail, and more,…

DSC resources to simplify administration of certificates on a Windows Server.

Static detection of vulnerable log4j librairies on Windows servers, members of an AD domain.

Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…

A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …

Docker base image with backported Host header validation fix for CVE-2025-12543 in Undertow 1.4.x, enabling secure deployment of WildFly 11…

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…

PowerShell-based provisioning framework for deploying complex lab environments on Hyper-V and Azure. Supports Windows, Linux, and products like AD,…

we are providing DevOps and security teams script to identify cloud workloads that may be vulnerable to the Log4j vulnerability(CVE-2021-44228) in…

An Ansible Playbook to mitigate the vulnerability CVE-2026-31431 on RHEL-based and Debian-based OSes.

A little tool to play with Azure Identity - Azure and Entra ID lab creation tool. Blog: https://medium.com/@iknowjason/sentinel-for-purple-teaming-1…

CVE-2025-54914 exposes a critical flaw in Azure Networking that allows attackers to escalate privileges and control routing across subnets. The…

Medium-interaction SSH/Telnet honeypot built with Cowrie, Loki, Promtail, and Grafana - provisioned on DigitalOcean via Terraform with a GitLab CI…