almalinux-fix-cve-2026-31431

Automates kernel patching for CVE-2026-31431 and Dirty Frag, sets secure kernel as default in GRUB, and disables testing repo for production safety.

Automates kernel patching for CVE-2026-31431 and Dirty Frag, sets secure kernel as default in GRUB, and disables testing repo for production safety.

Companion source for YouTube video "Stop Mounting docker.sock — Run Trivy Without Giving Away Root Access — (inspired by CVE-2026-33634)"

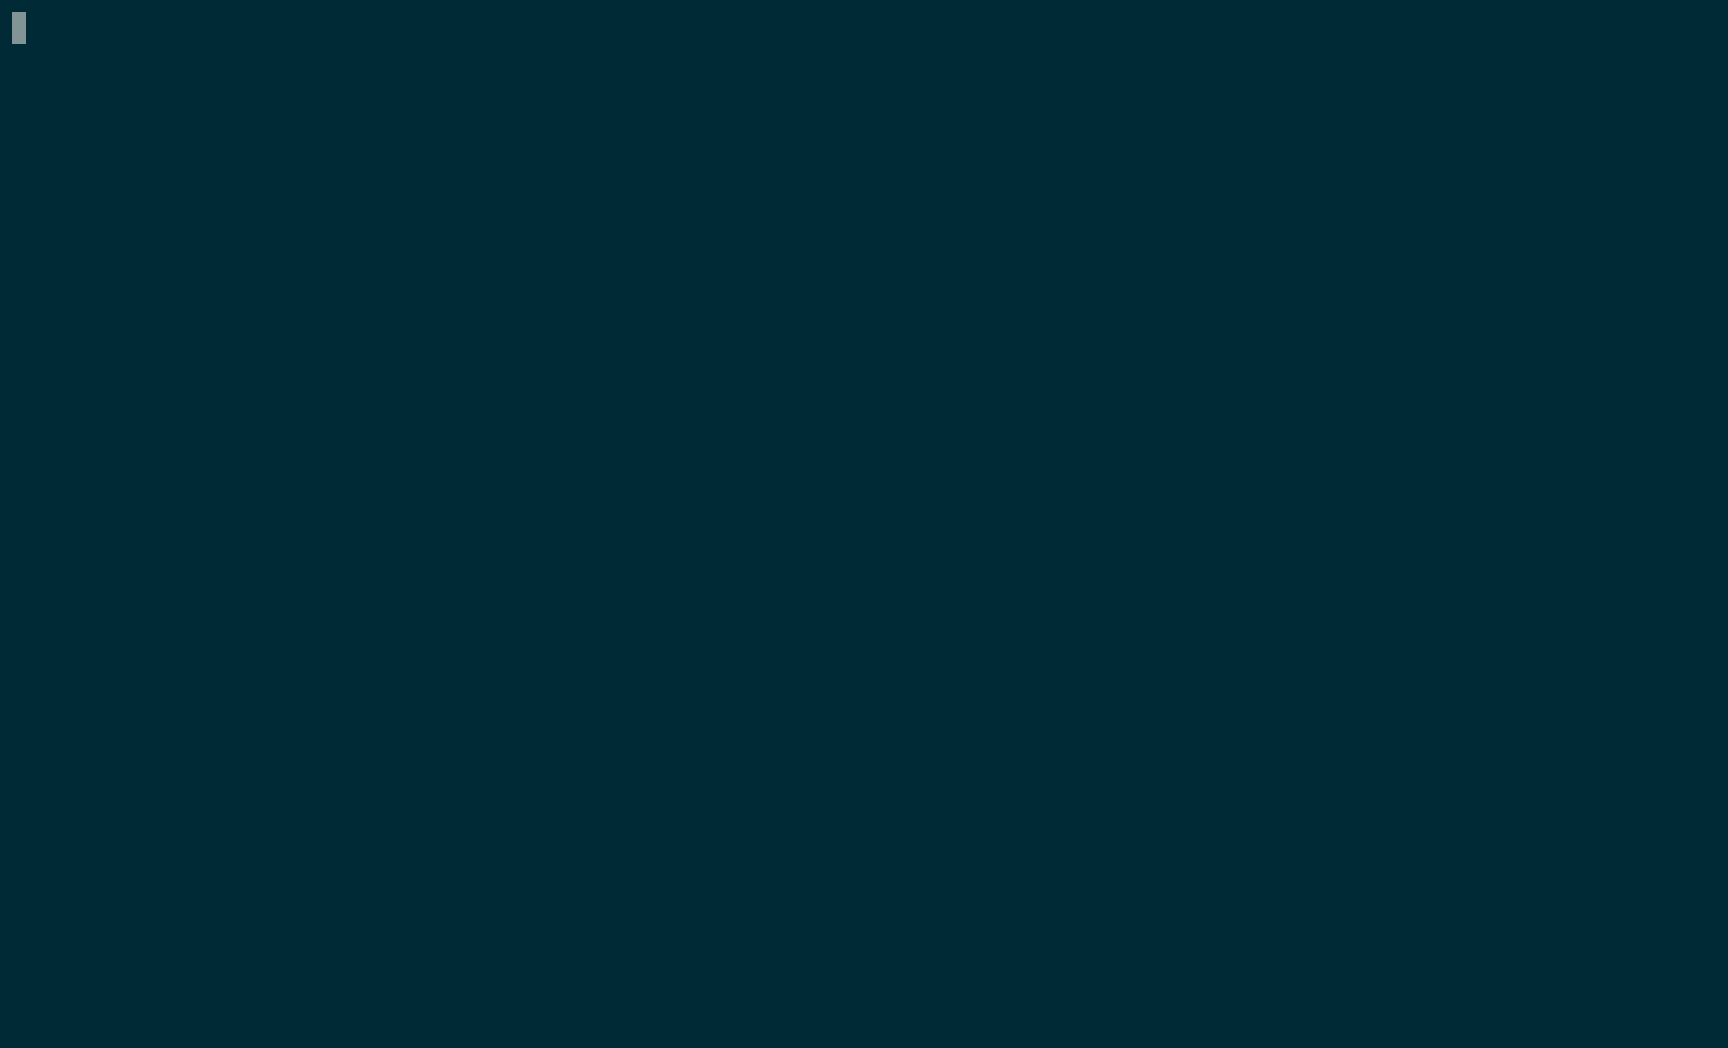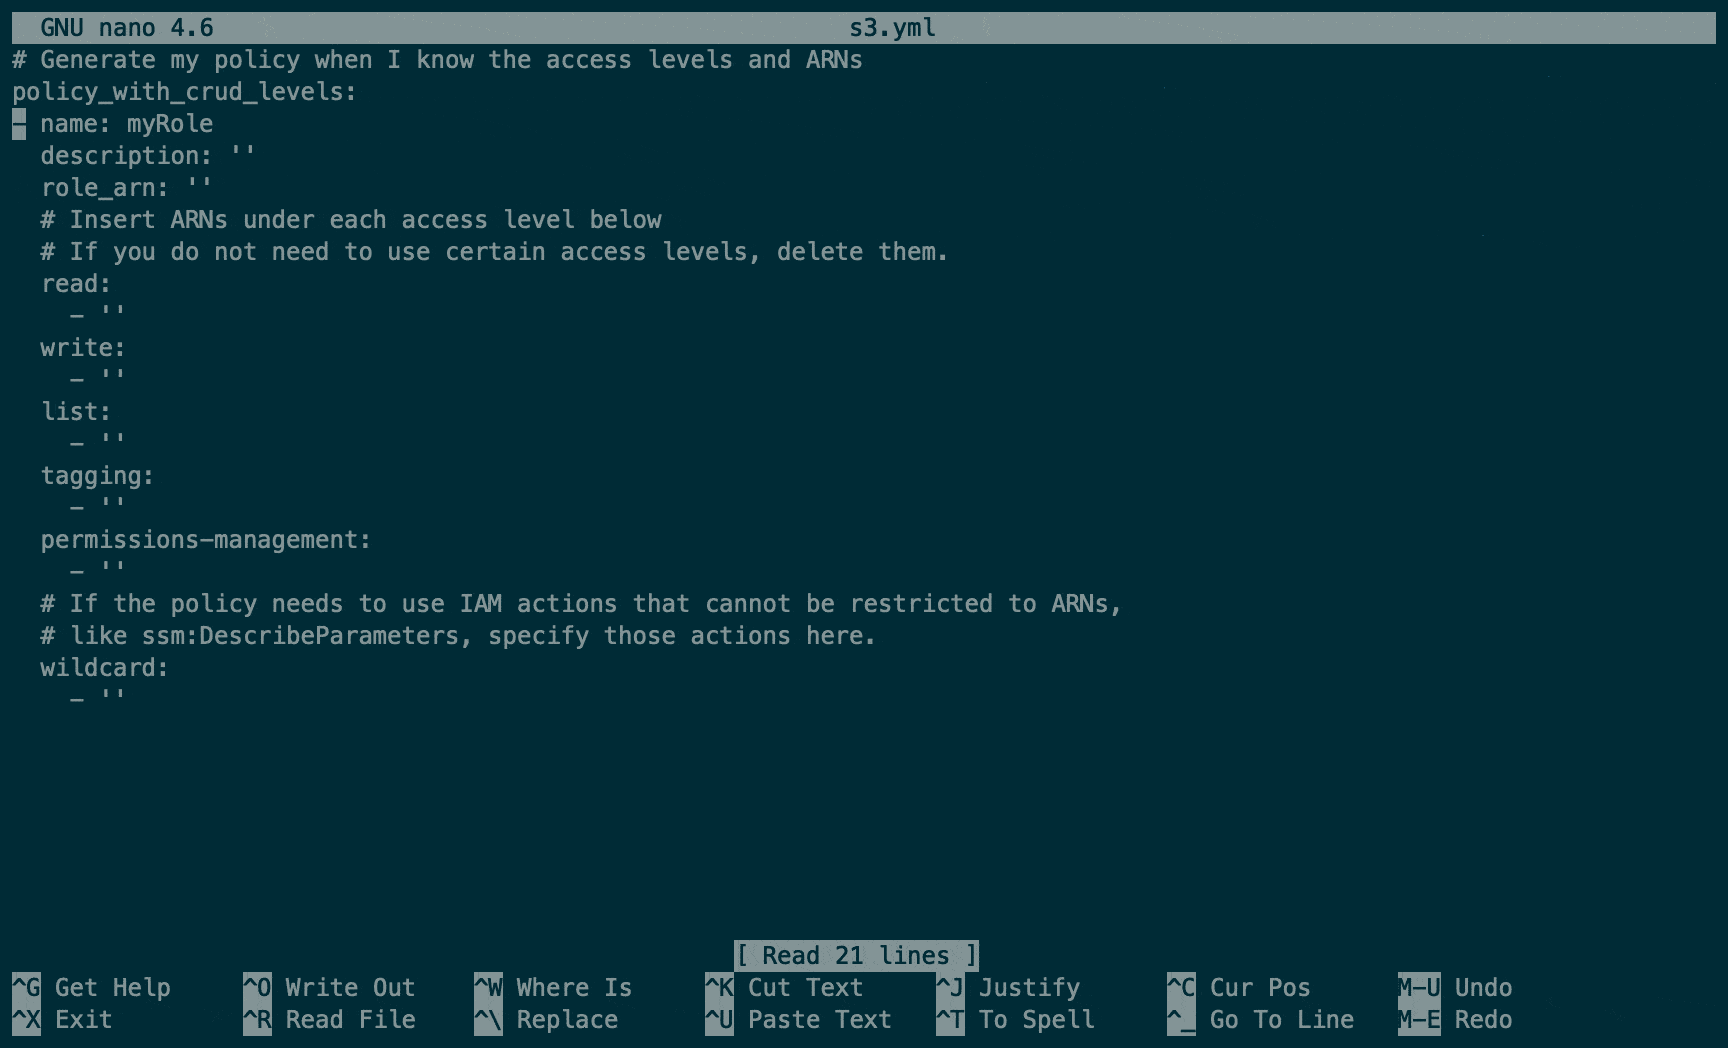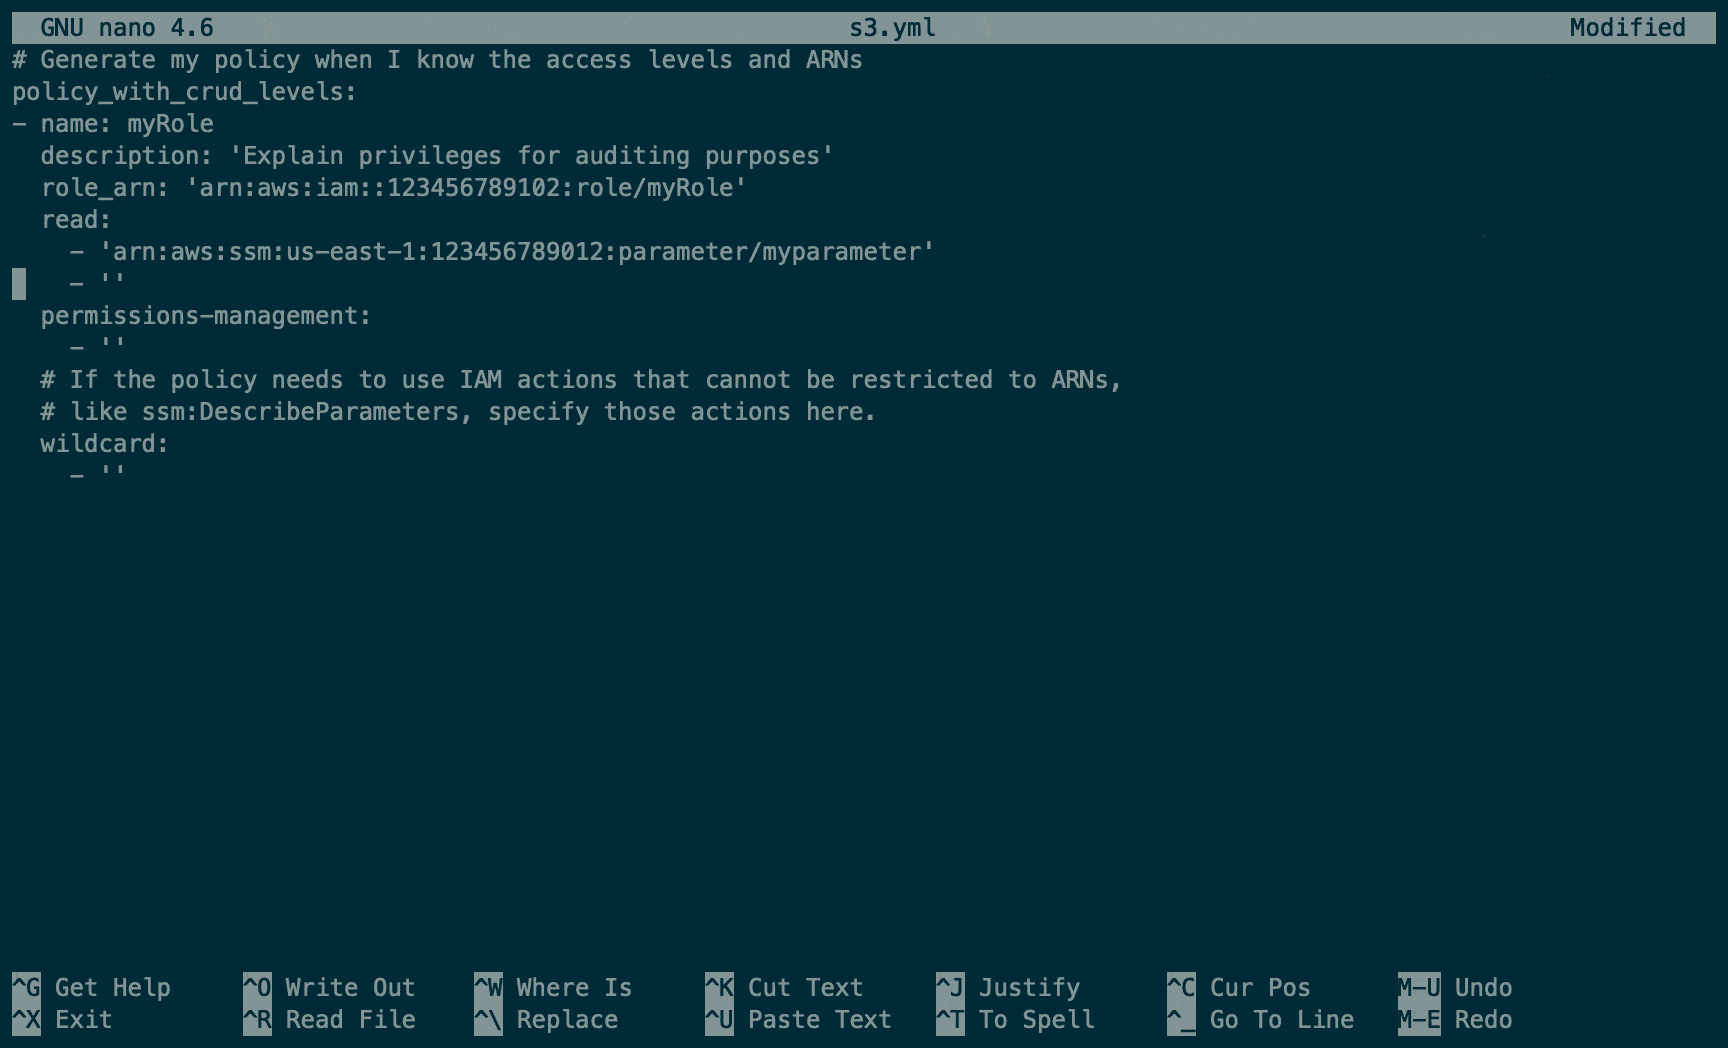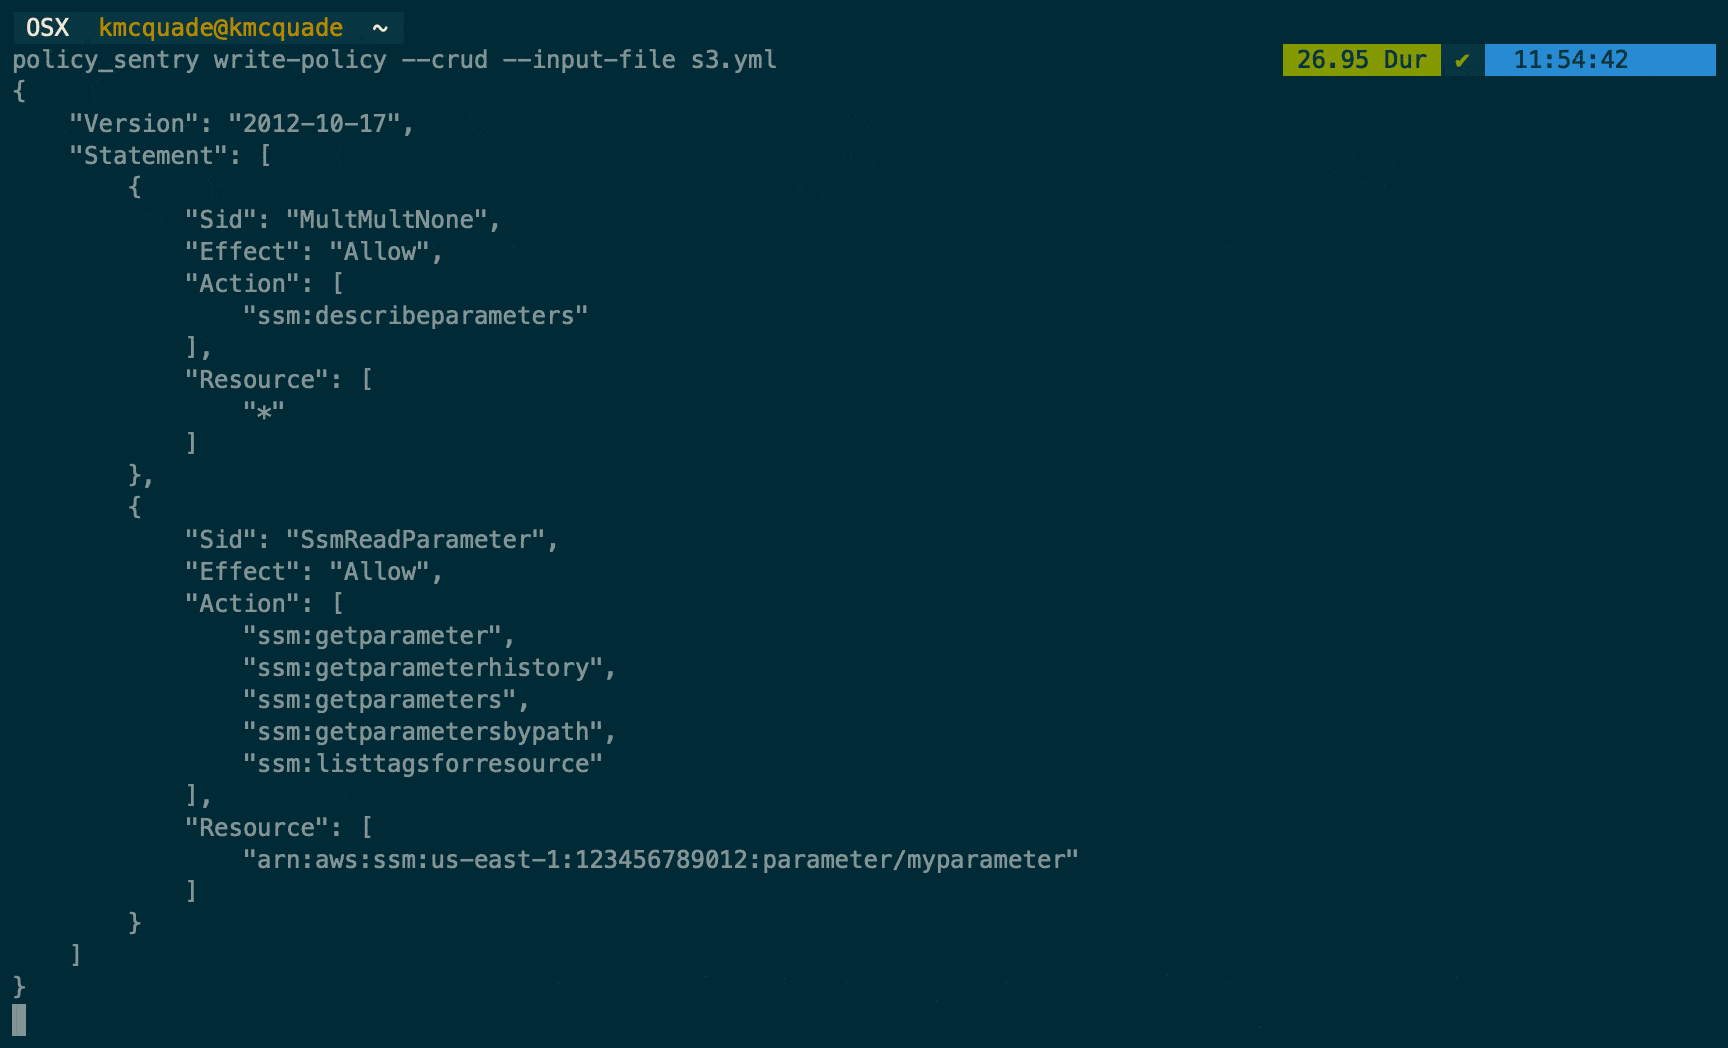
Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.

Infrastructure as code for DNS!

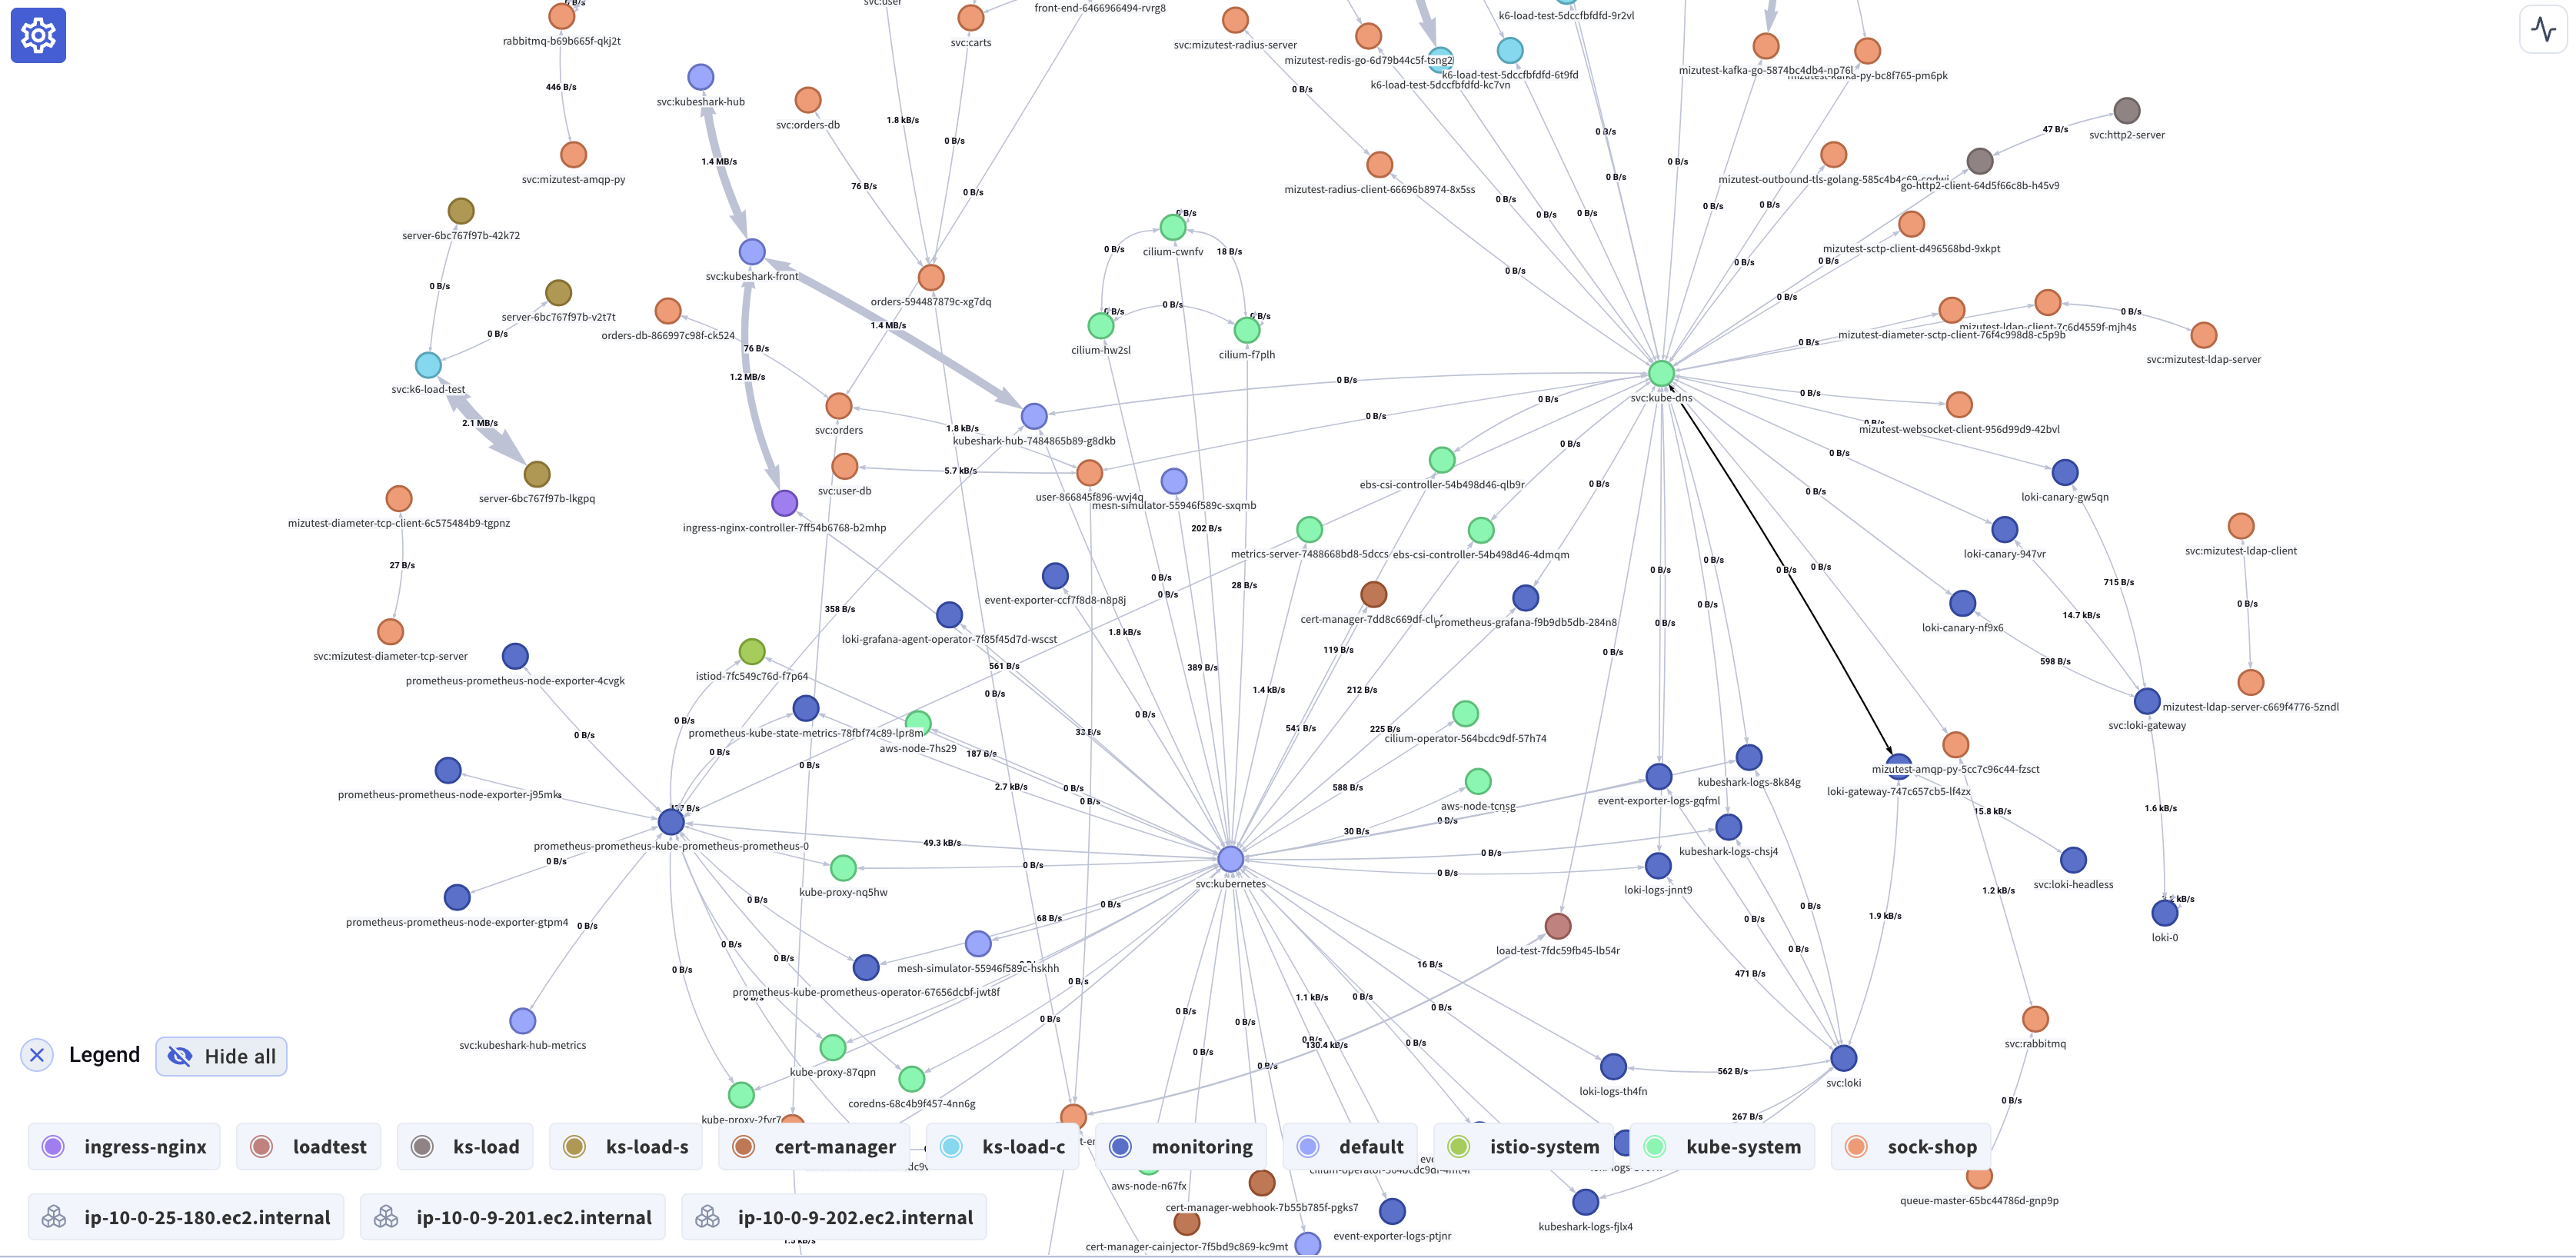
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…

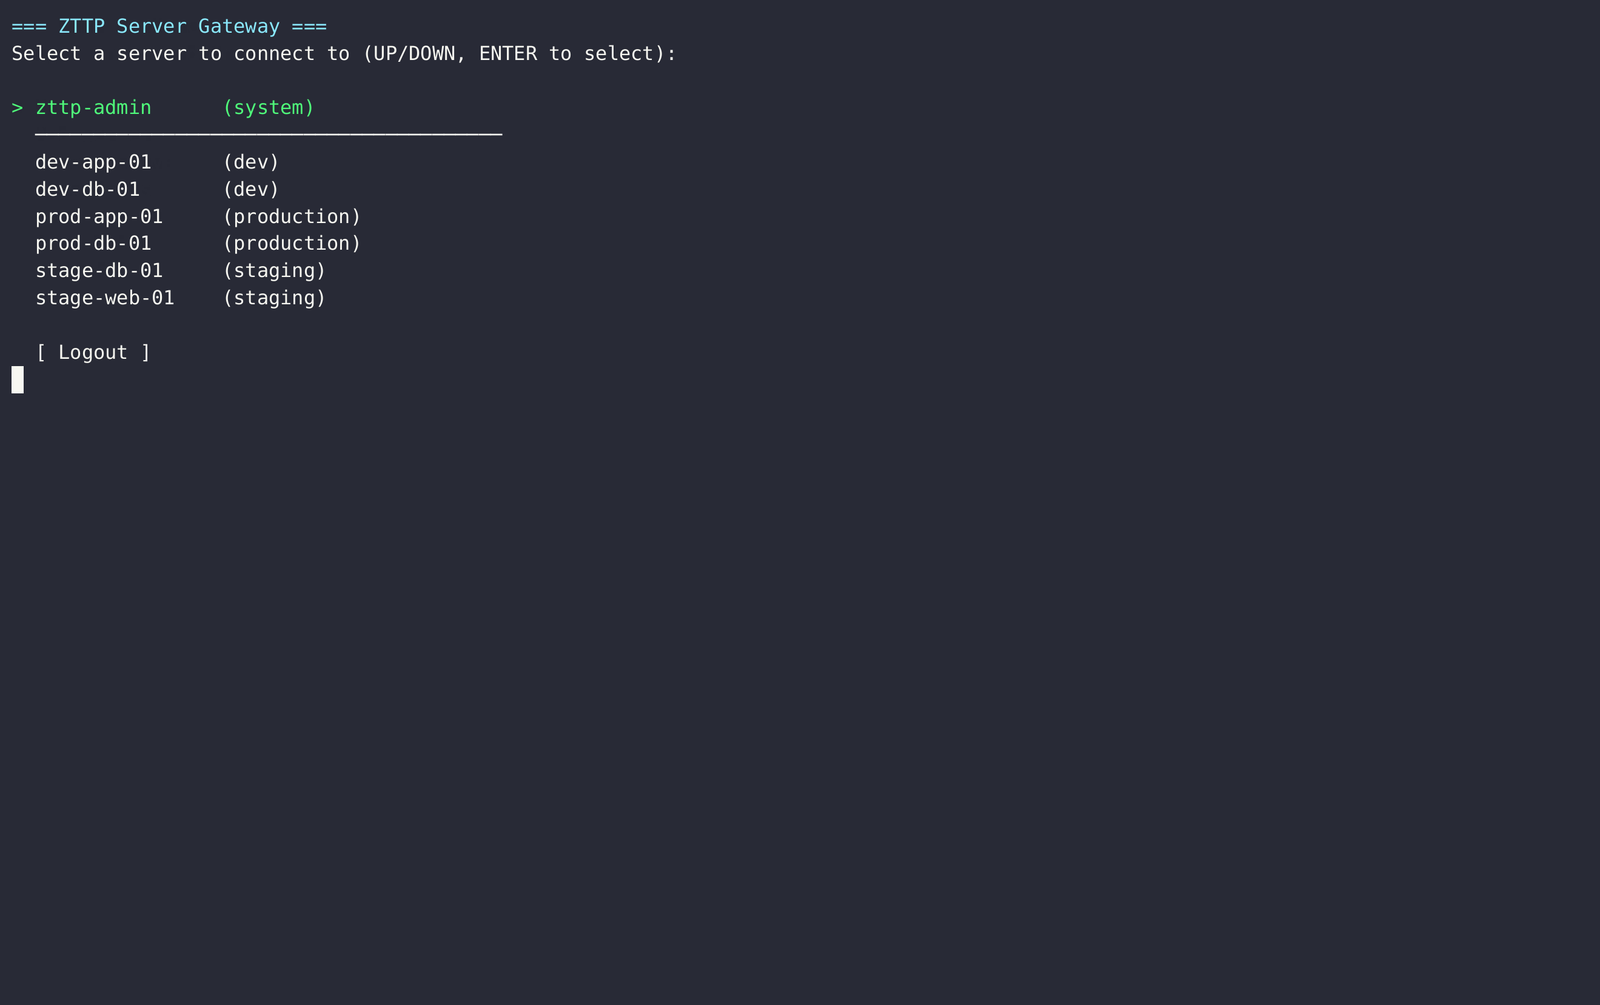
Zero-trust SSH bastion proxy with Vault-backed key management, RBAC policy enforcement, full session recording, and admin TUI for auditable access to…

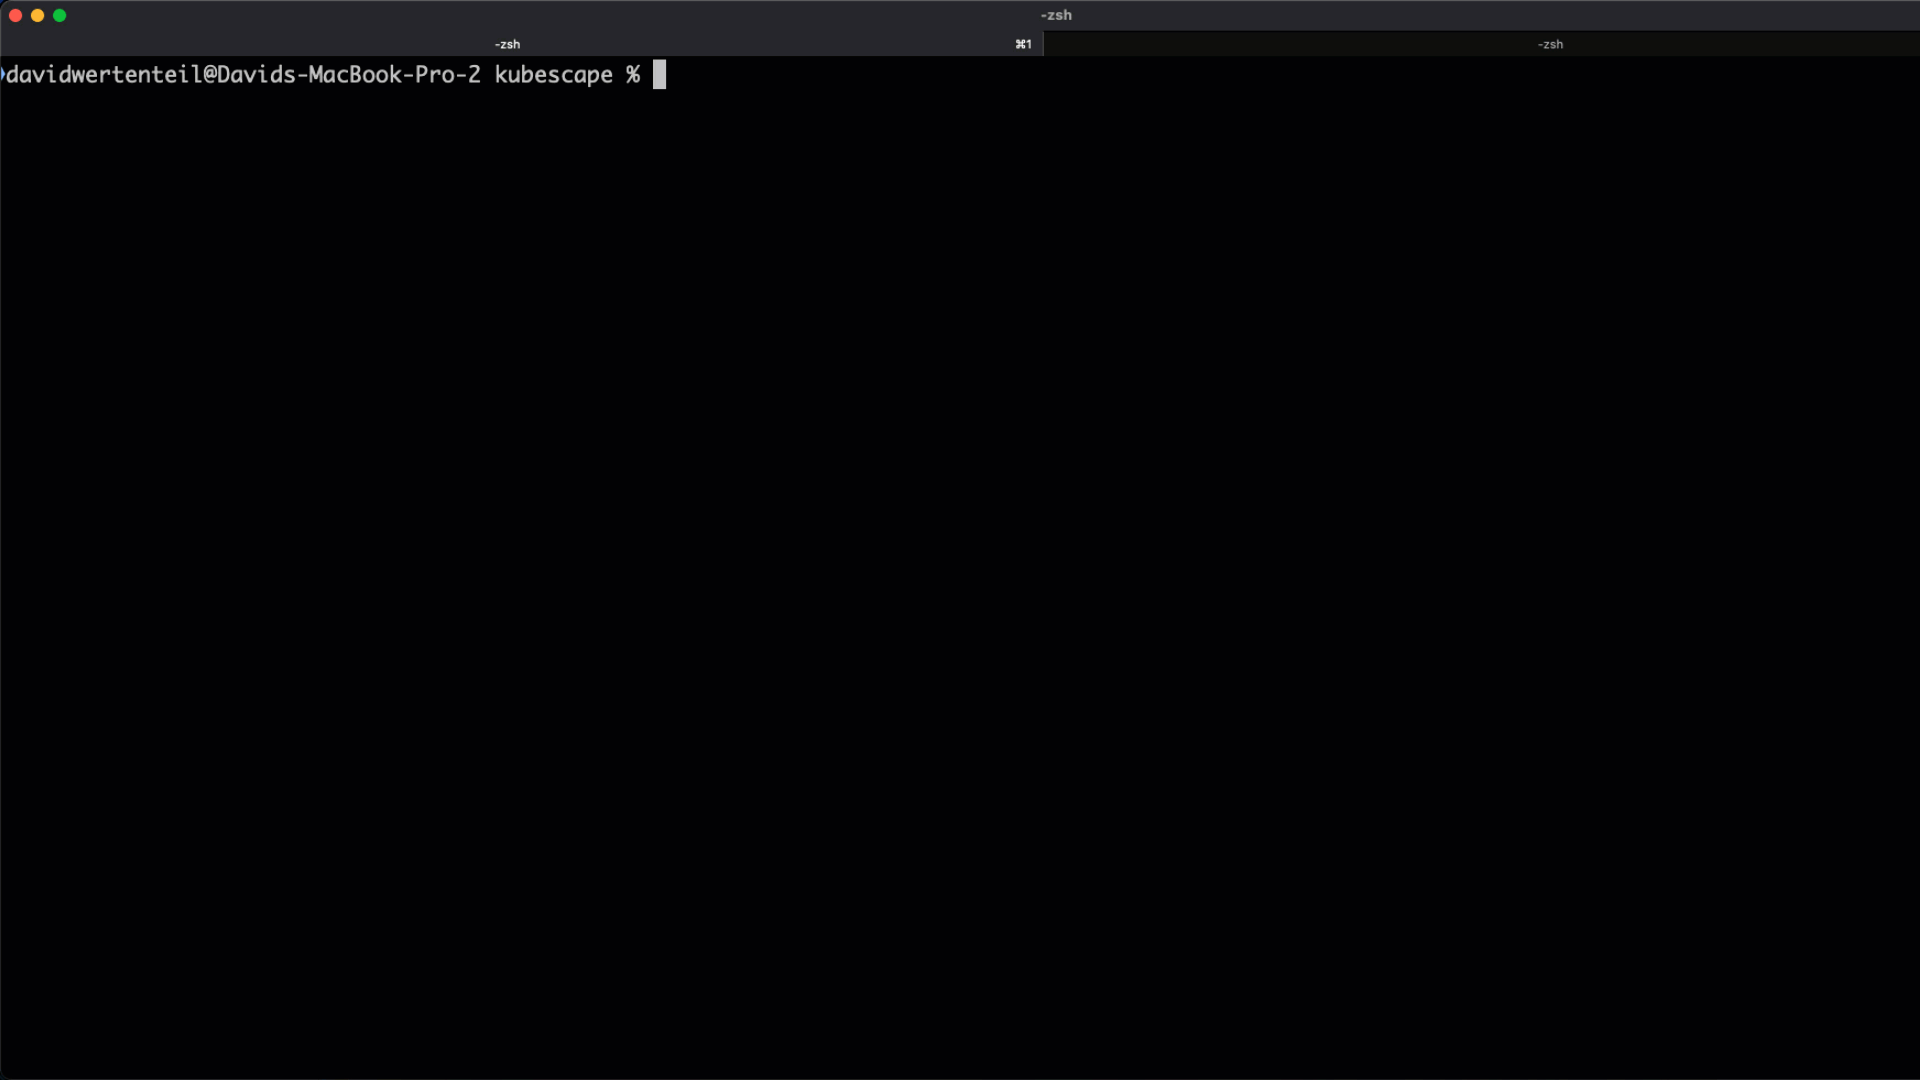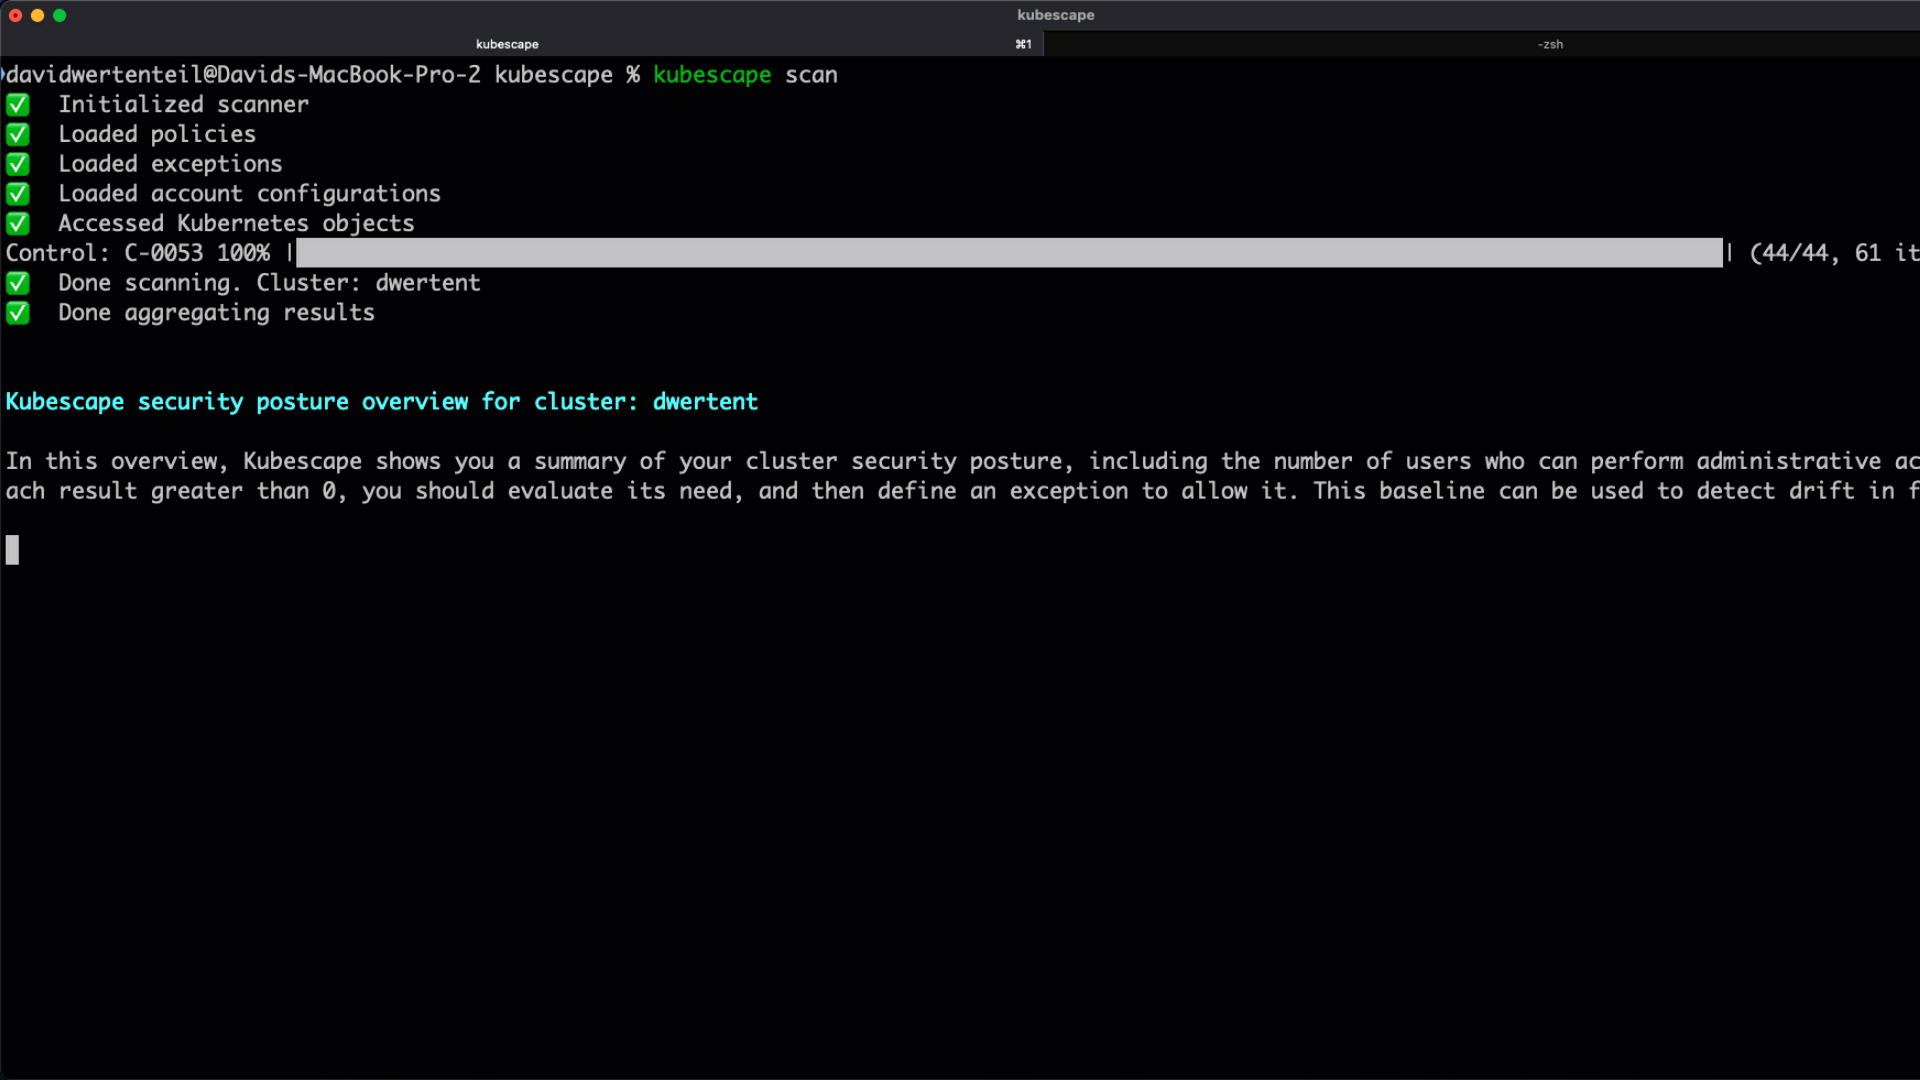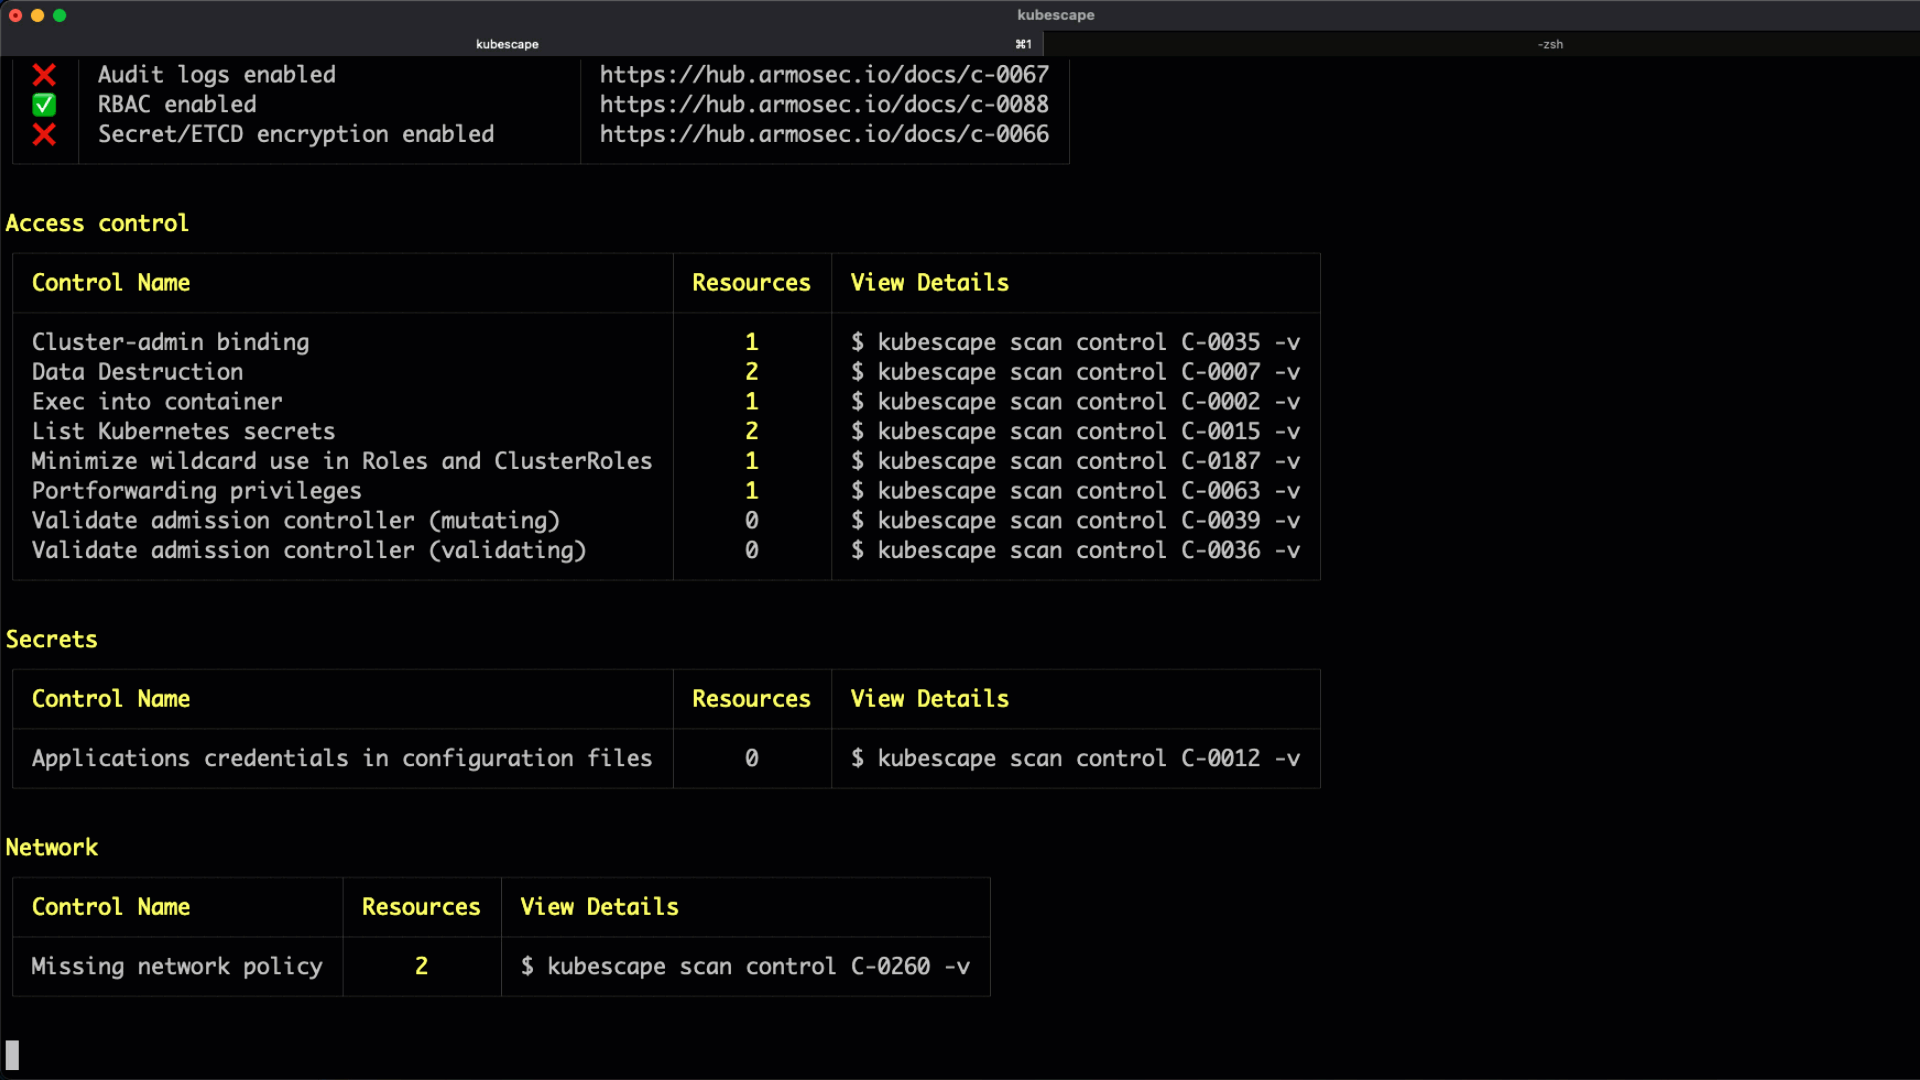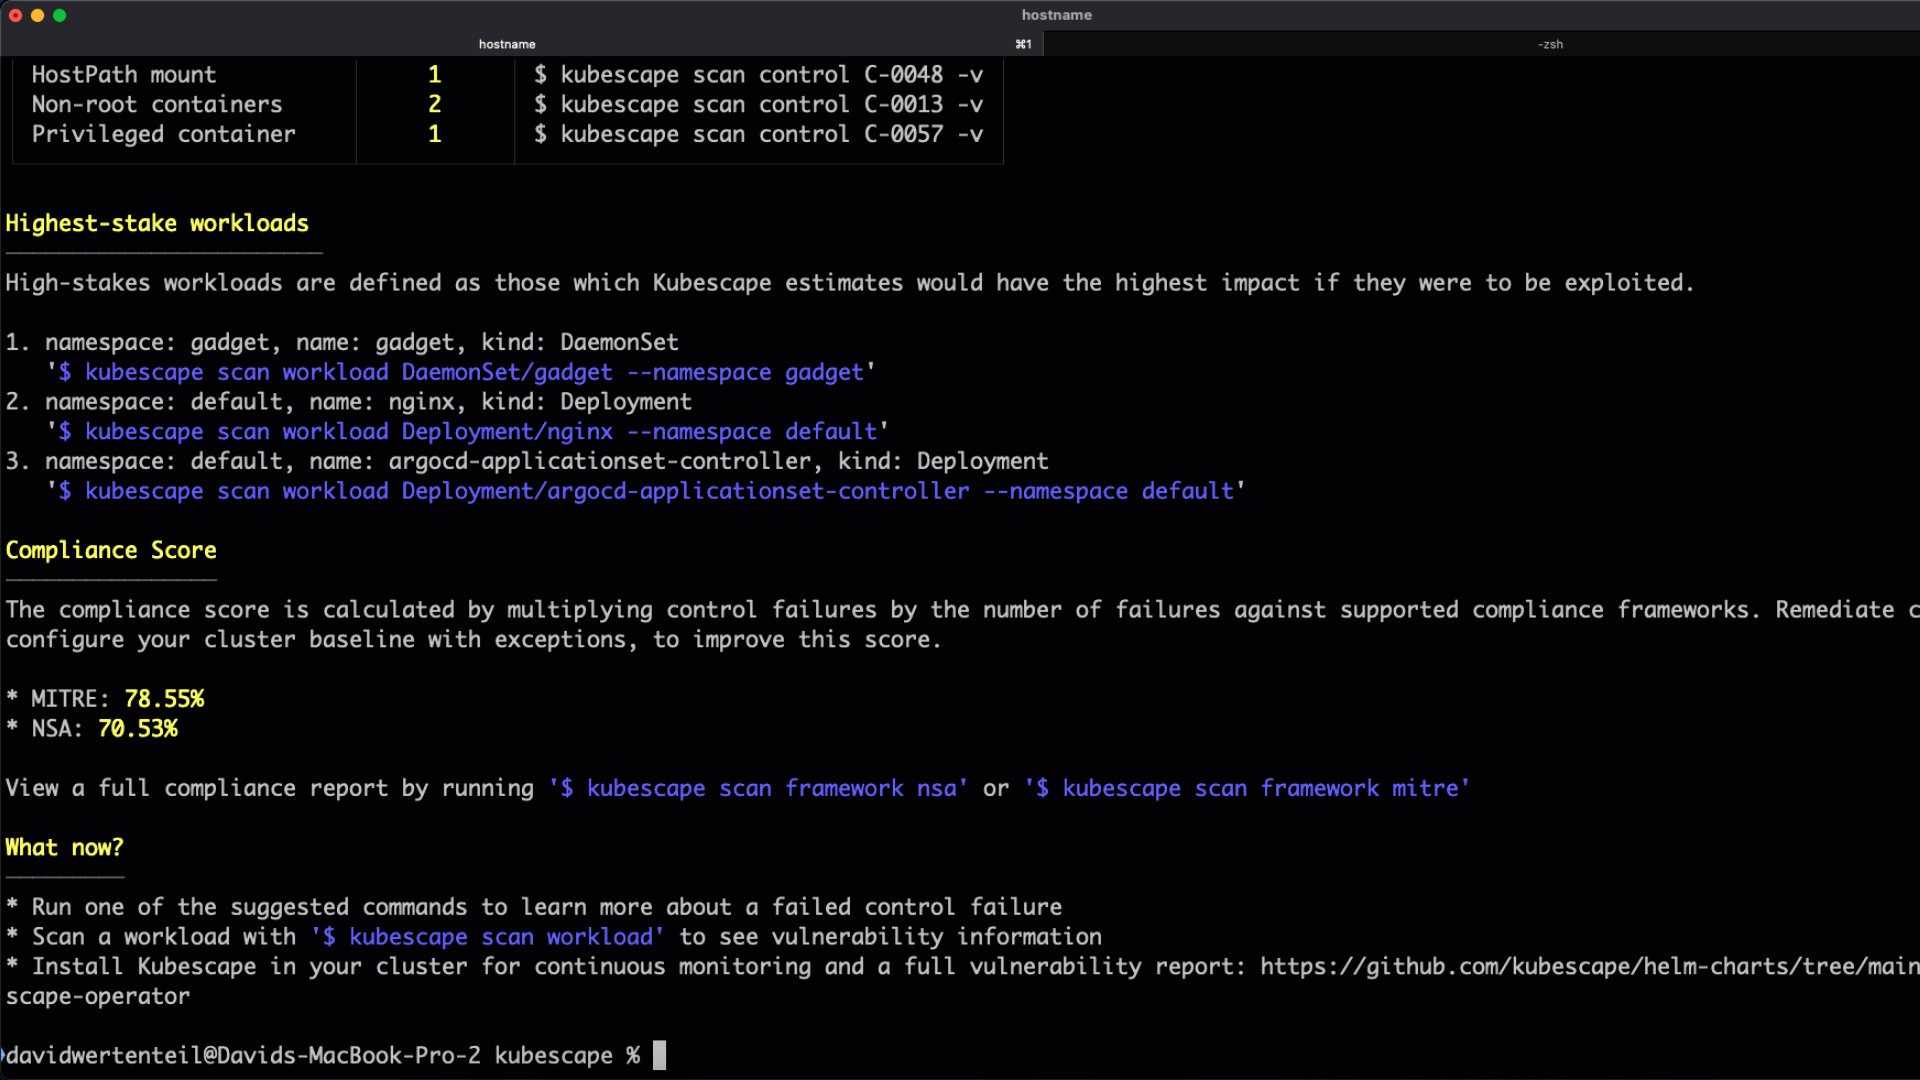
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…

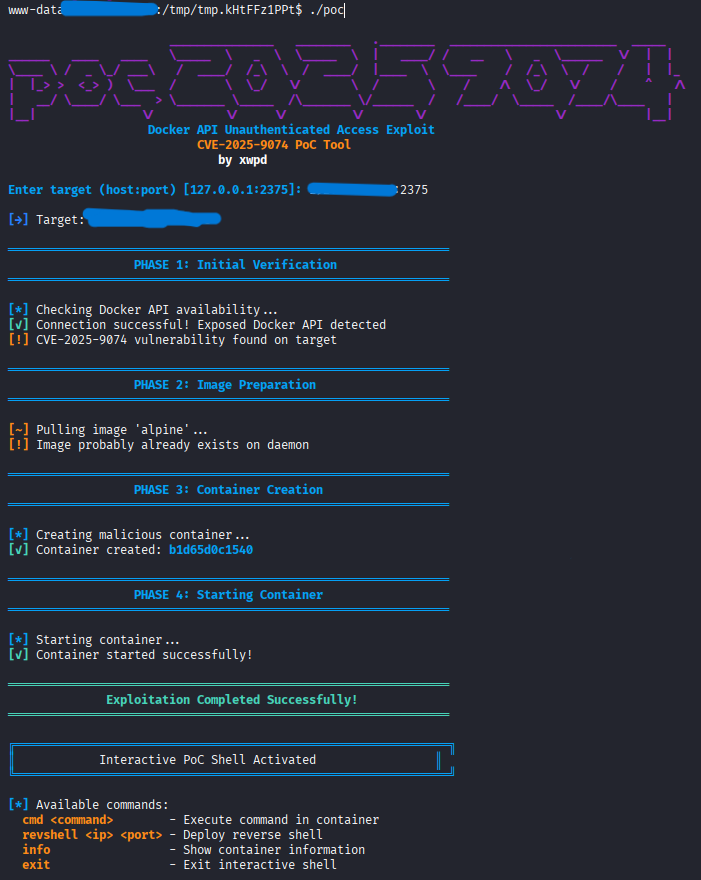
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…

AWSGoat : A Damn Vulnerable AWS Infrastructure

A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …

🔐 Lightweight CLI utility designed to synchronize SSH public keys from remote URLs into local authorized_keys files

Ansible playbook to automate mitigation of CVE-2023-46747 (BIG-IP unauthenticated RCE) by applying F5's official script across multiple devices.

CLI framework for deploying and managing serverless applications on AWS Lambda with YAML infrastructure, local development, and multi-language…

Secure and fast microVMs for serverless computing.

Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…

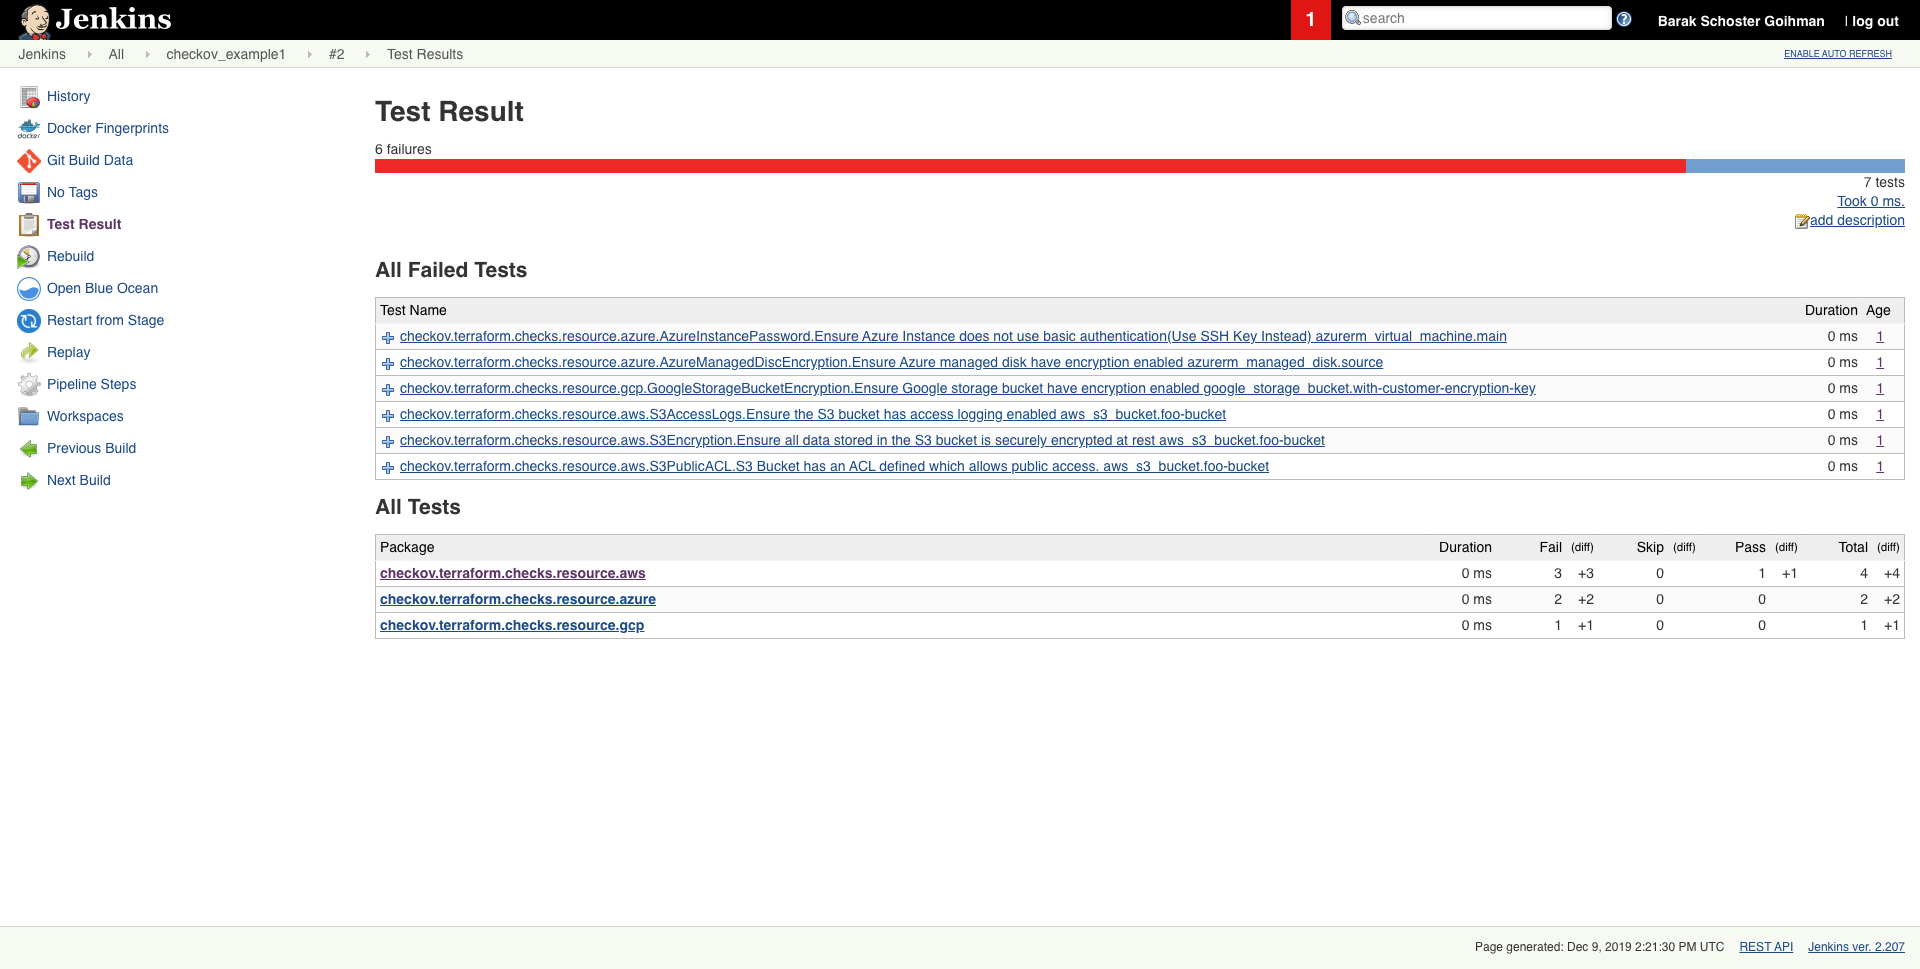
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…

Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…

Rules engine for cloud security, cost optimization, and governance, DSL in yaml for policies to query, filter, and take actions on resources