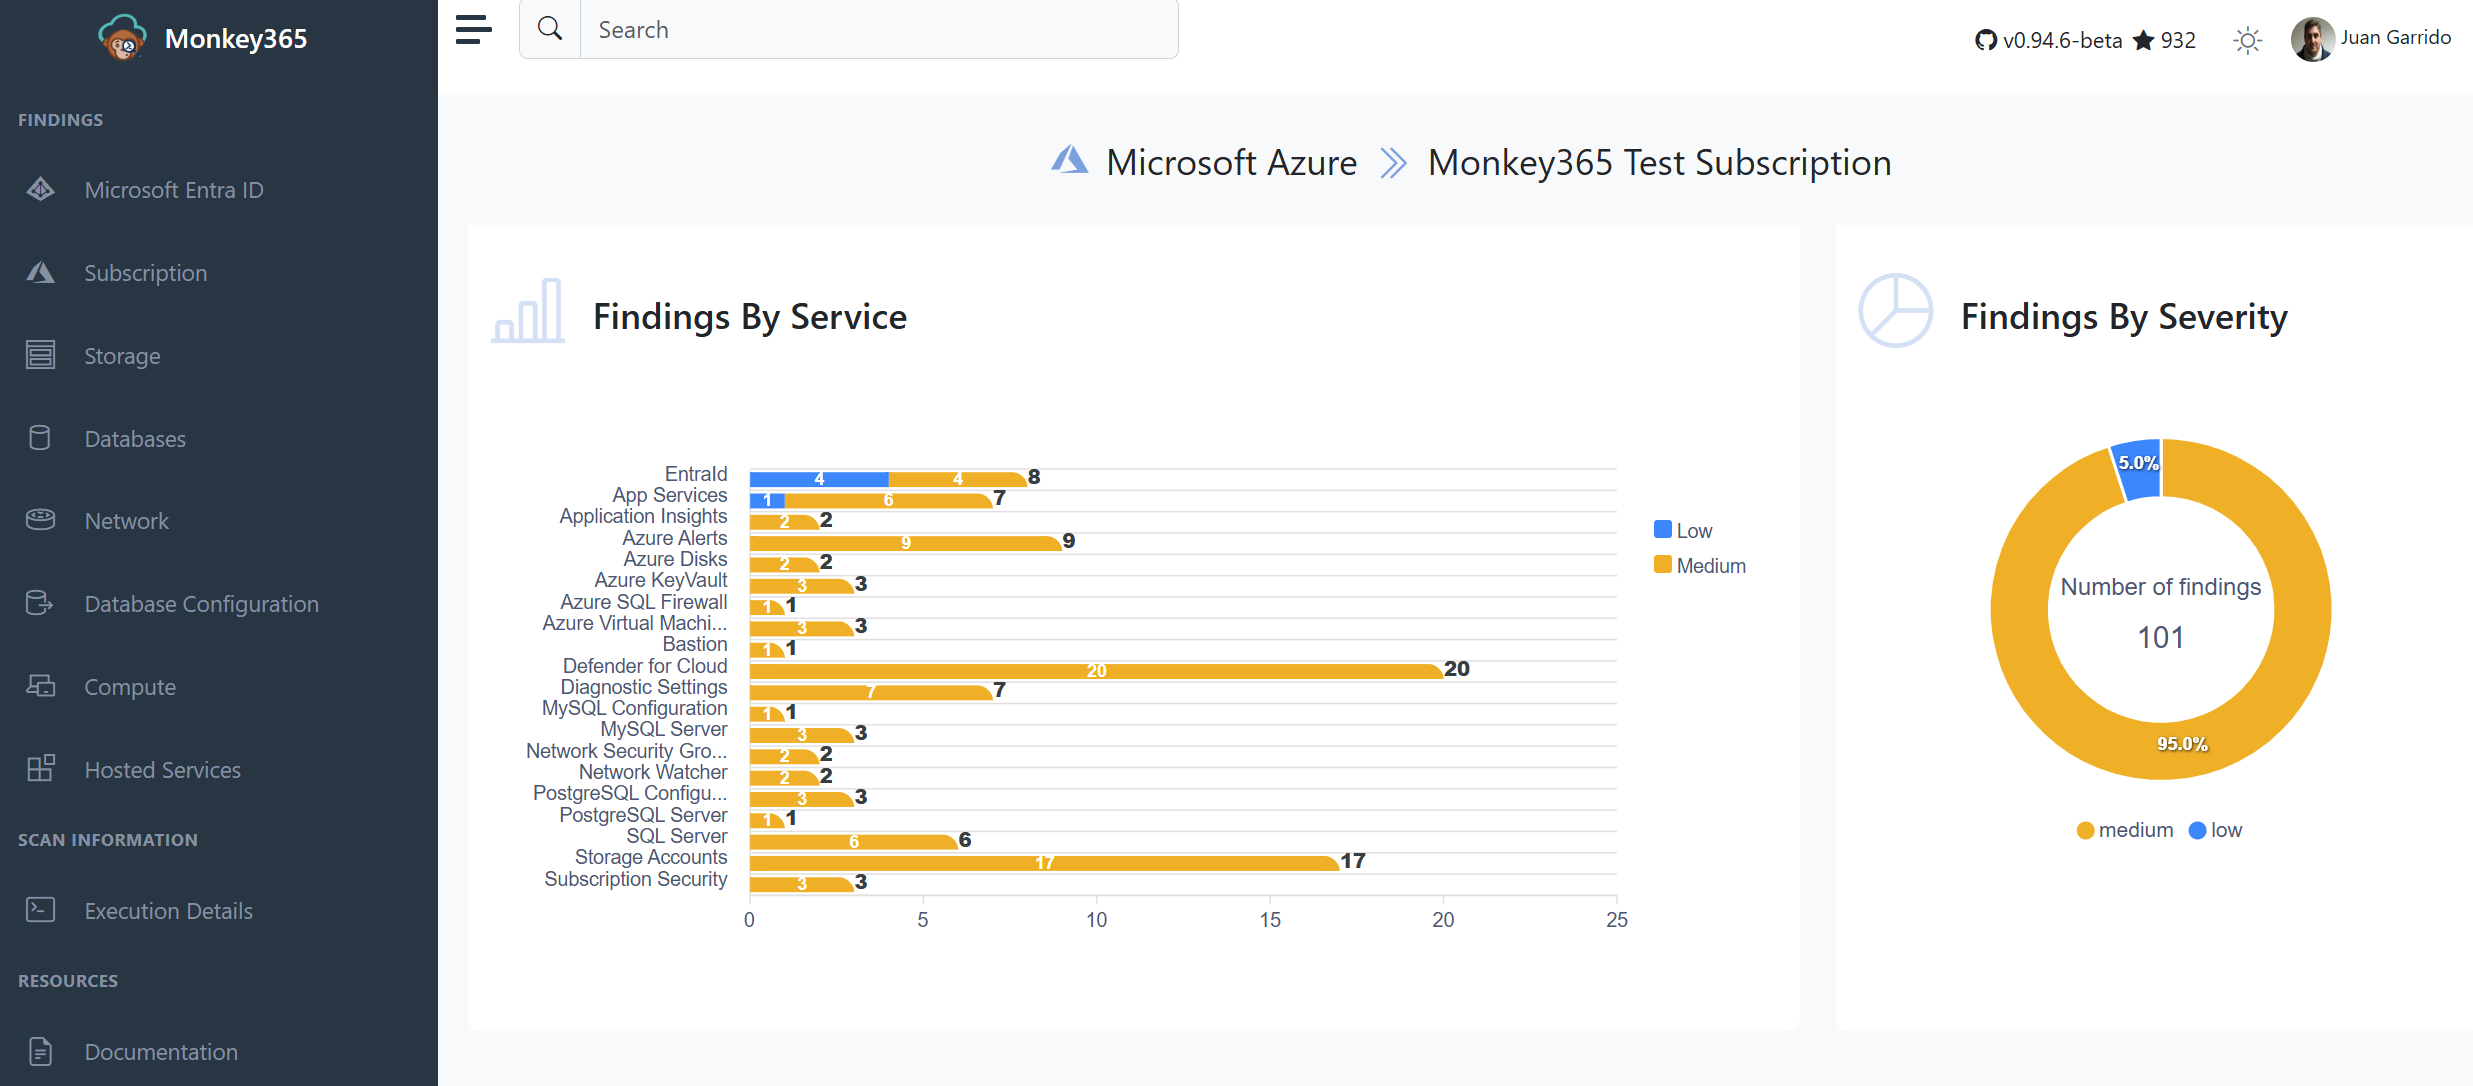

monkey365
PowerShell-based security assessment framework for Microsoft 365, Azure, and Entra ID. Scans for misconfigurations, CIS benchmark compliance, and…

PowerShell-based security assessment framework for Microsoft 365, Azure, and Entra ID. Scans for misconfigurations, CIS benchmark compliance, and…

A little tool to play with Azure Identity - Azure and Entra ID lab creation tool. Blog: https://medium.com/@iknowjason/sentinel-for-purple-teaming-1…

Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…

Terraform module to manage AWS Security Groups. Currently, the ingress and egress rules support IPv4, IPv6, and Security Group ID inputs.

Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…

Read-only audit tooling for CVE-2026-0300 (PAN-OS User-ID Authentication Portal exposure)

Microsoft Entra ID (Azure AD) Unauthenticated Enumeration

Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)

S3 Account Search

DaemonSet с реализацией временной меры для митигации уязвимости Copy Fail (CVE-2026-31431)