
serverless
 serverless/serverless
CLI framework for deploying and managing serverless applications on AWS Lambda with YAML infrastructure, local development, and multi-language…
authenticationcloud-infrastructure-securitydevsecops+4
46.9k
serverless/serverlessCLI framework for deploying and managing serverless applications on AWS Lambda with YAML infrastructure, local development, and multi-language…
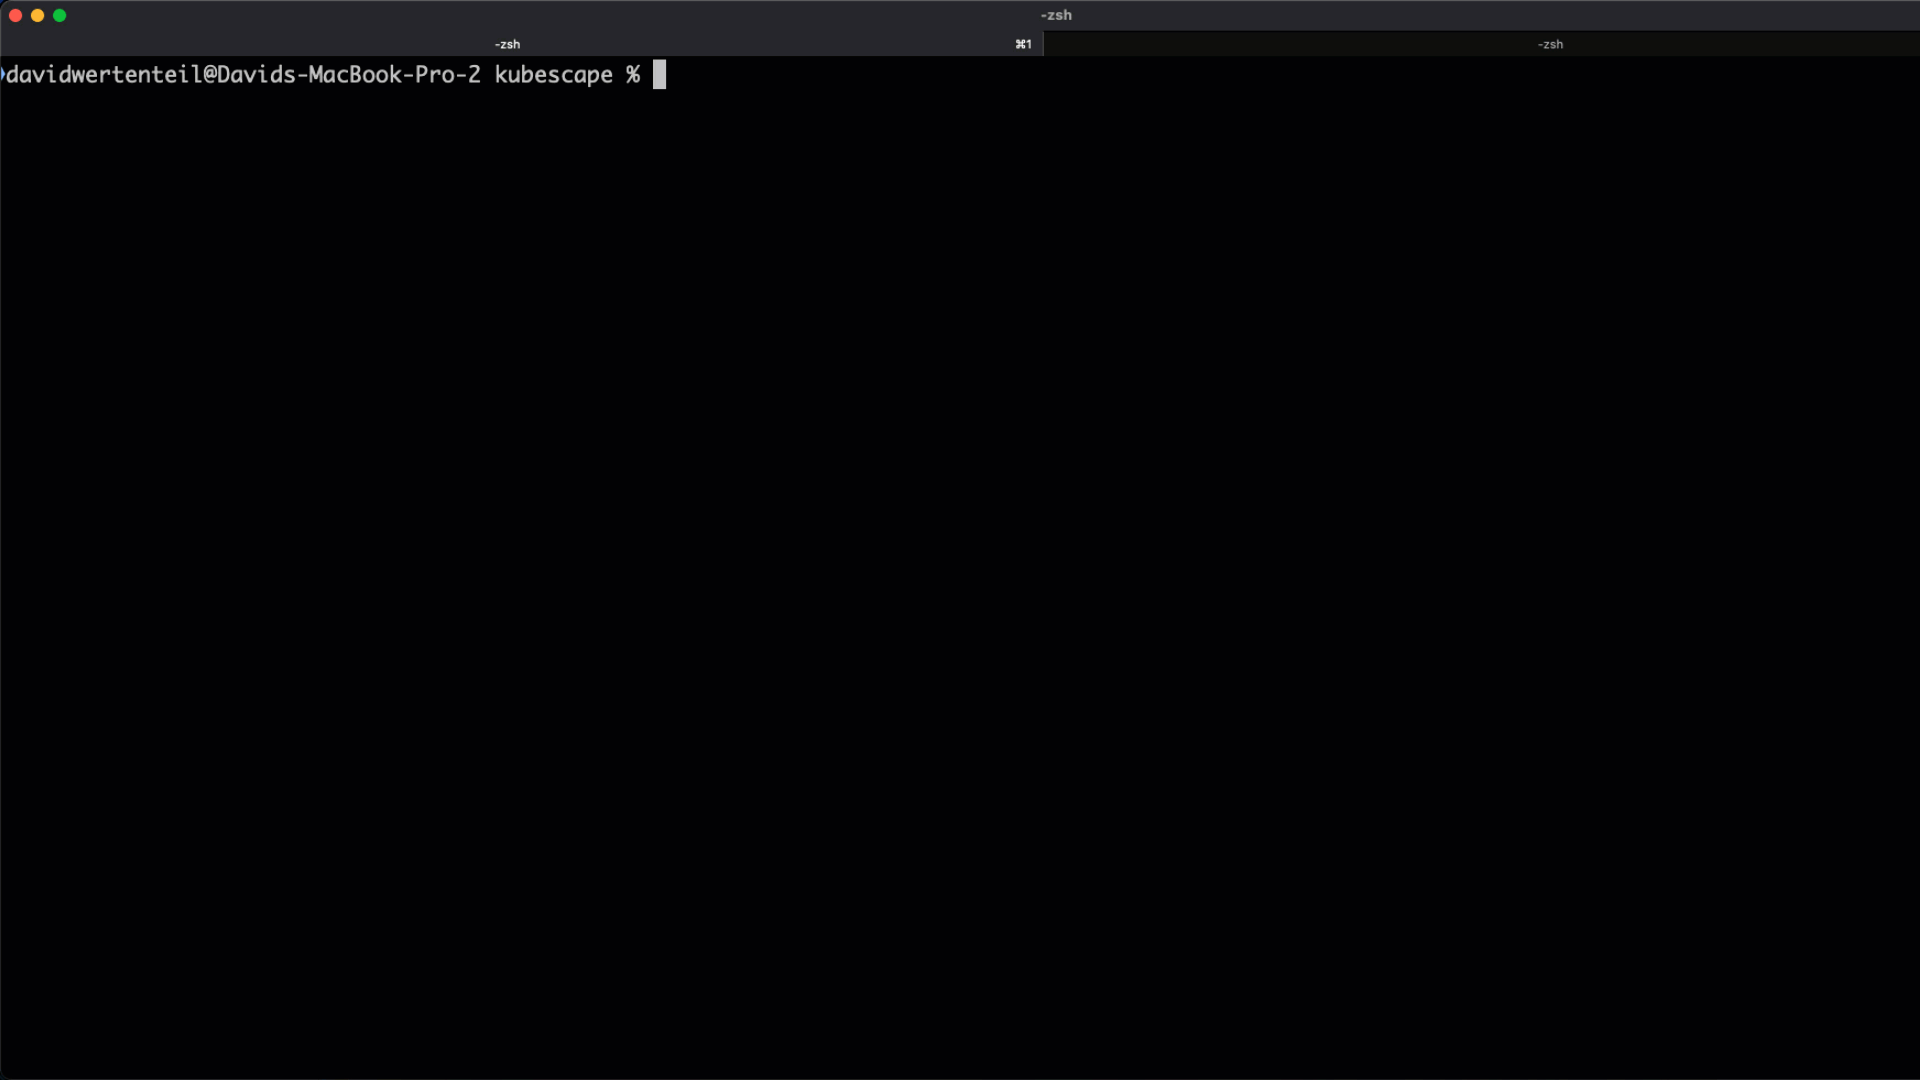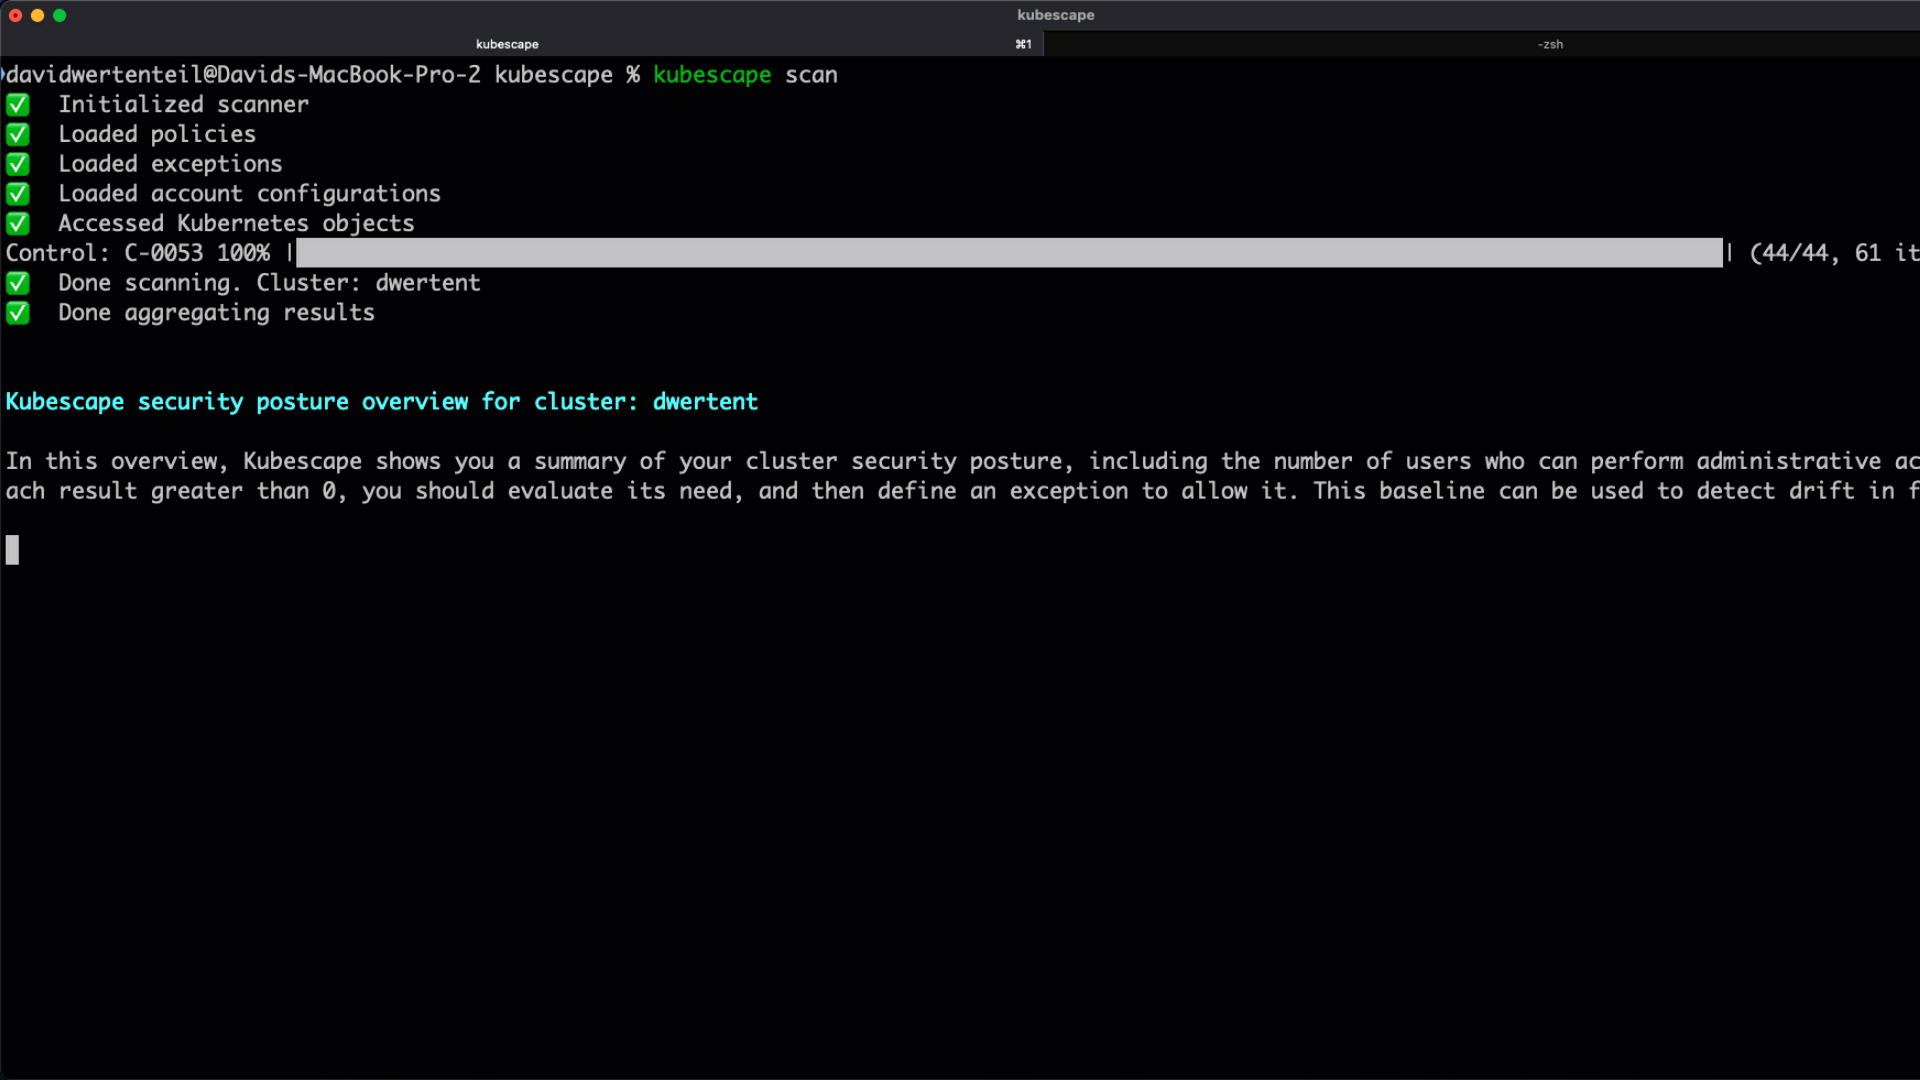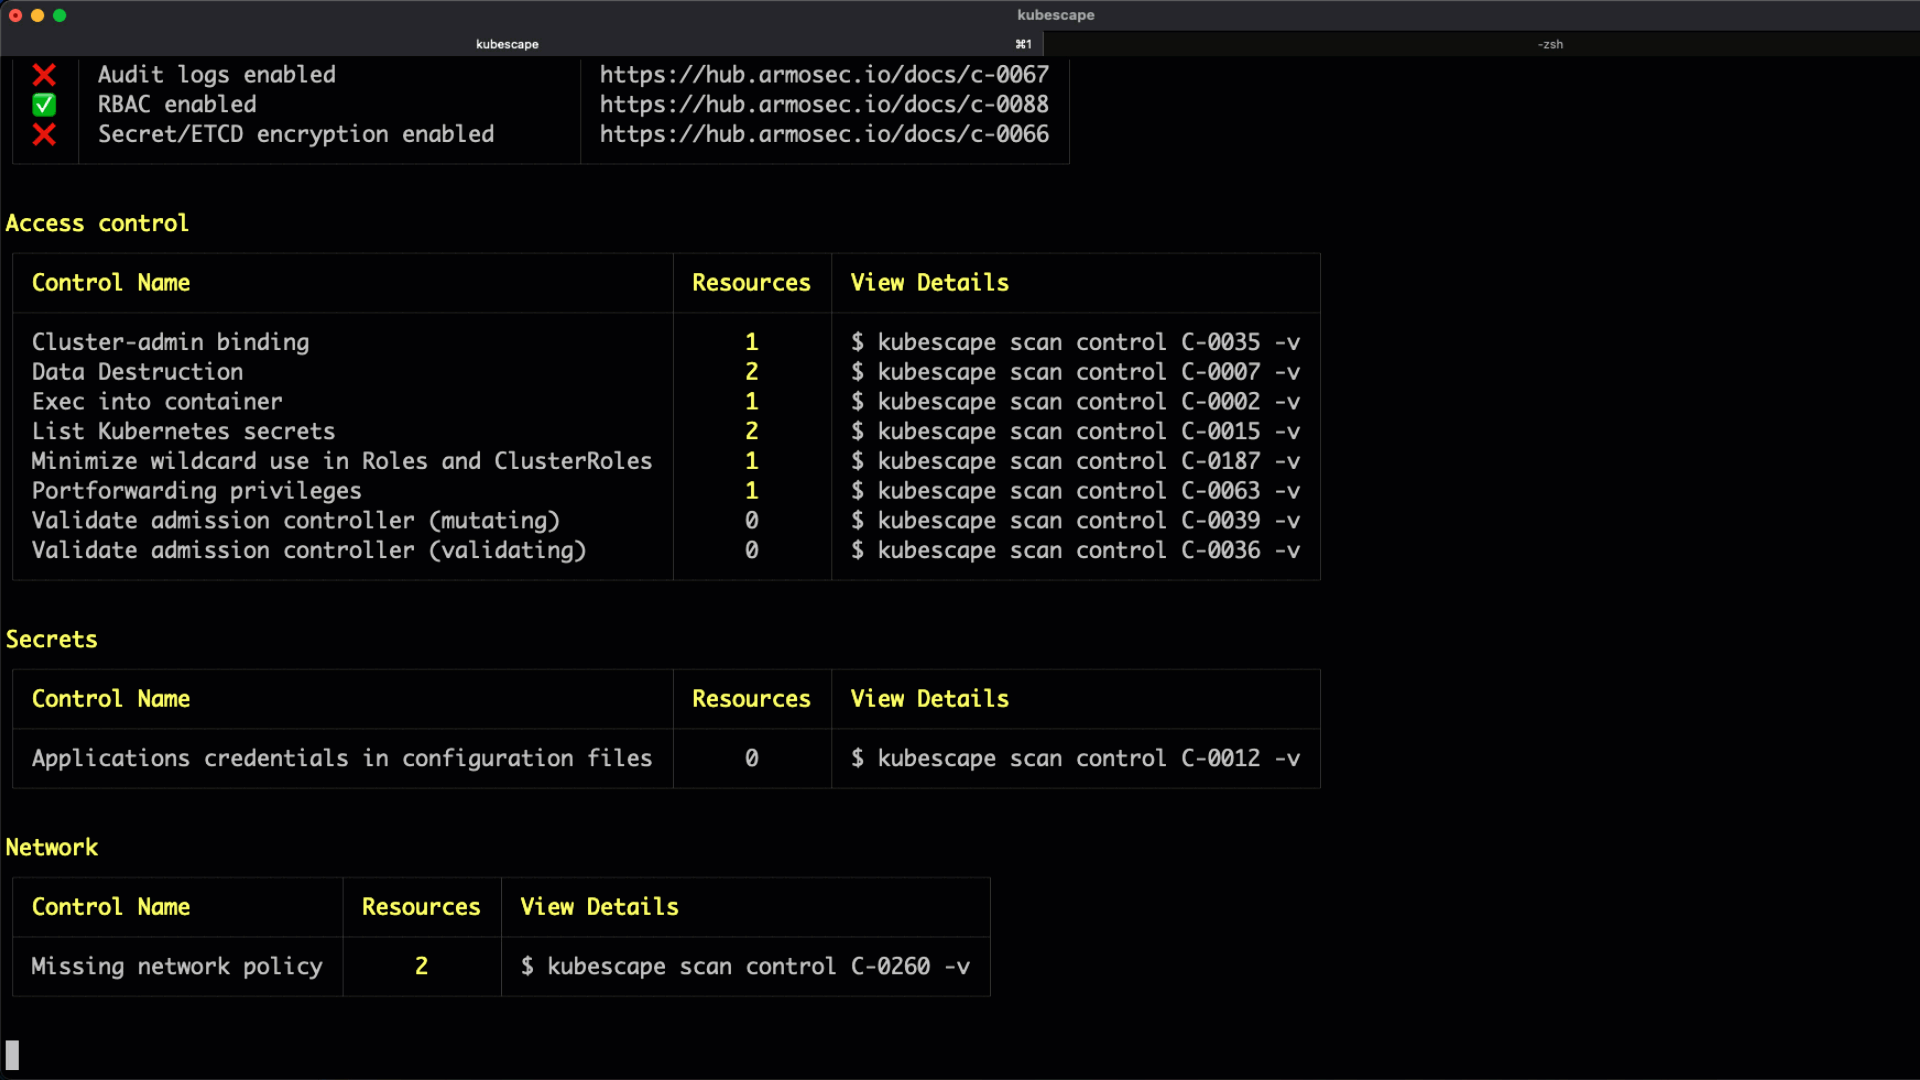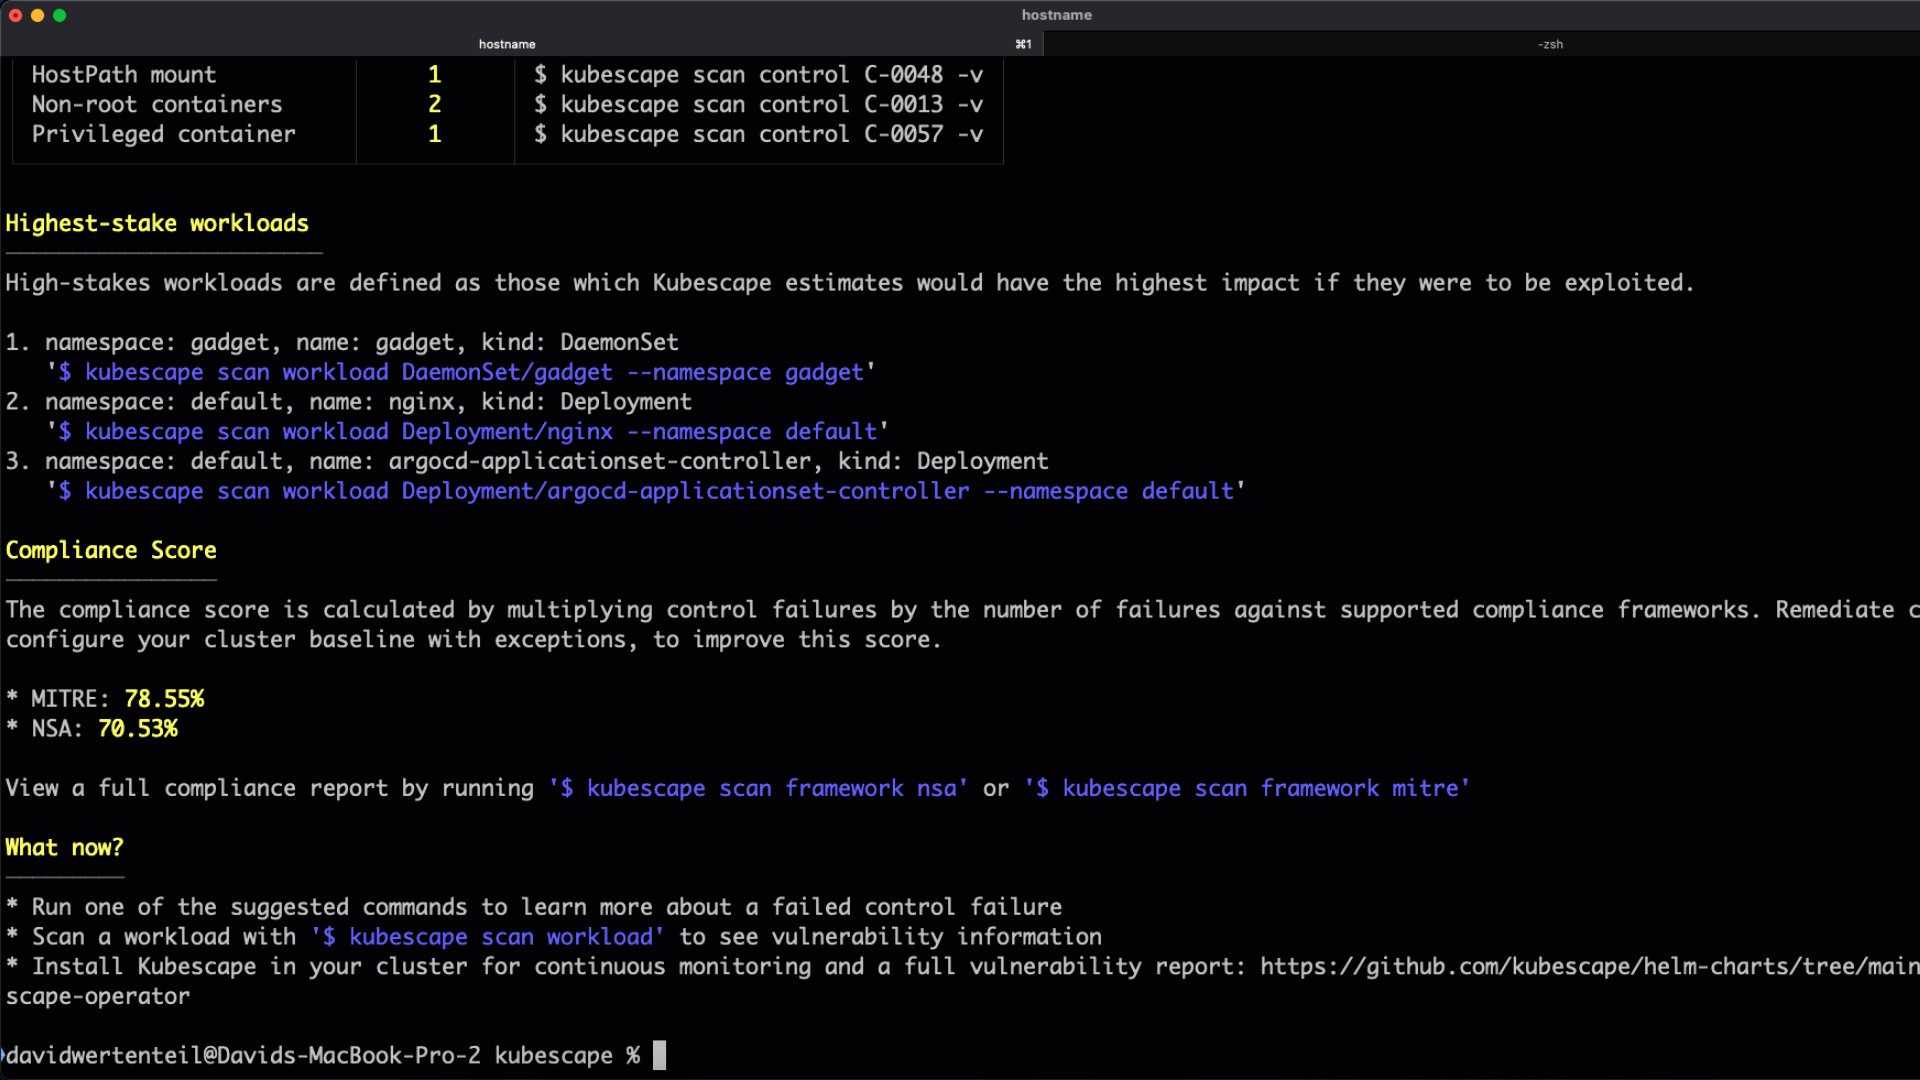 kubescape/kubescape
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…
 dirkjanm/roadtools
A collection of Azure AD/Entra tools for offensive and defensive security purposes
 eilonh/s3crets_scanner
Automated scanner that hunts for secrets (API keys, credentials) accidentally uploaded to public S3 buckets, using truffleHog3 for detection and…
 getkern/kern
Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
 summitroute/aws_exposable_resources
Curated catalog of AWS resource types that can be publicly exposed, with CLI commands for creating and auditing public access configurations across…
 expl0itabl3/check_mdi
Python script to enumerate valid Microsoft 365 domains, retrieve tenant name, and check for an MDI instance.
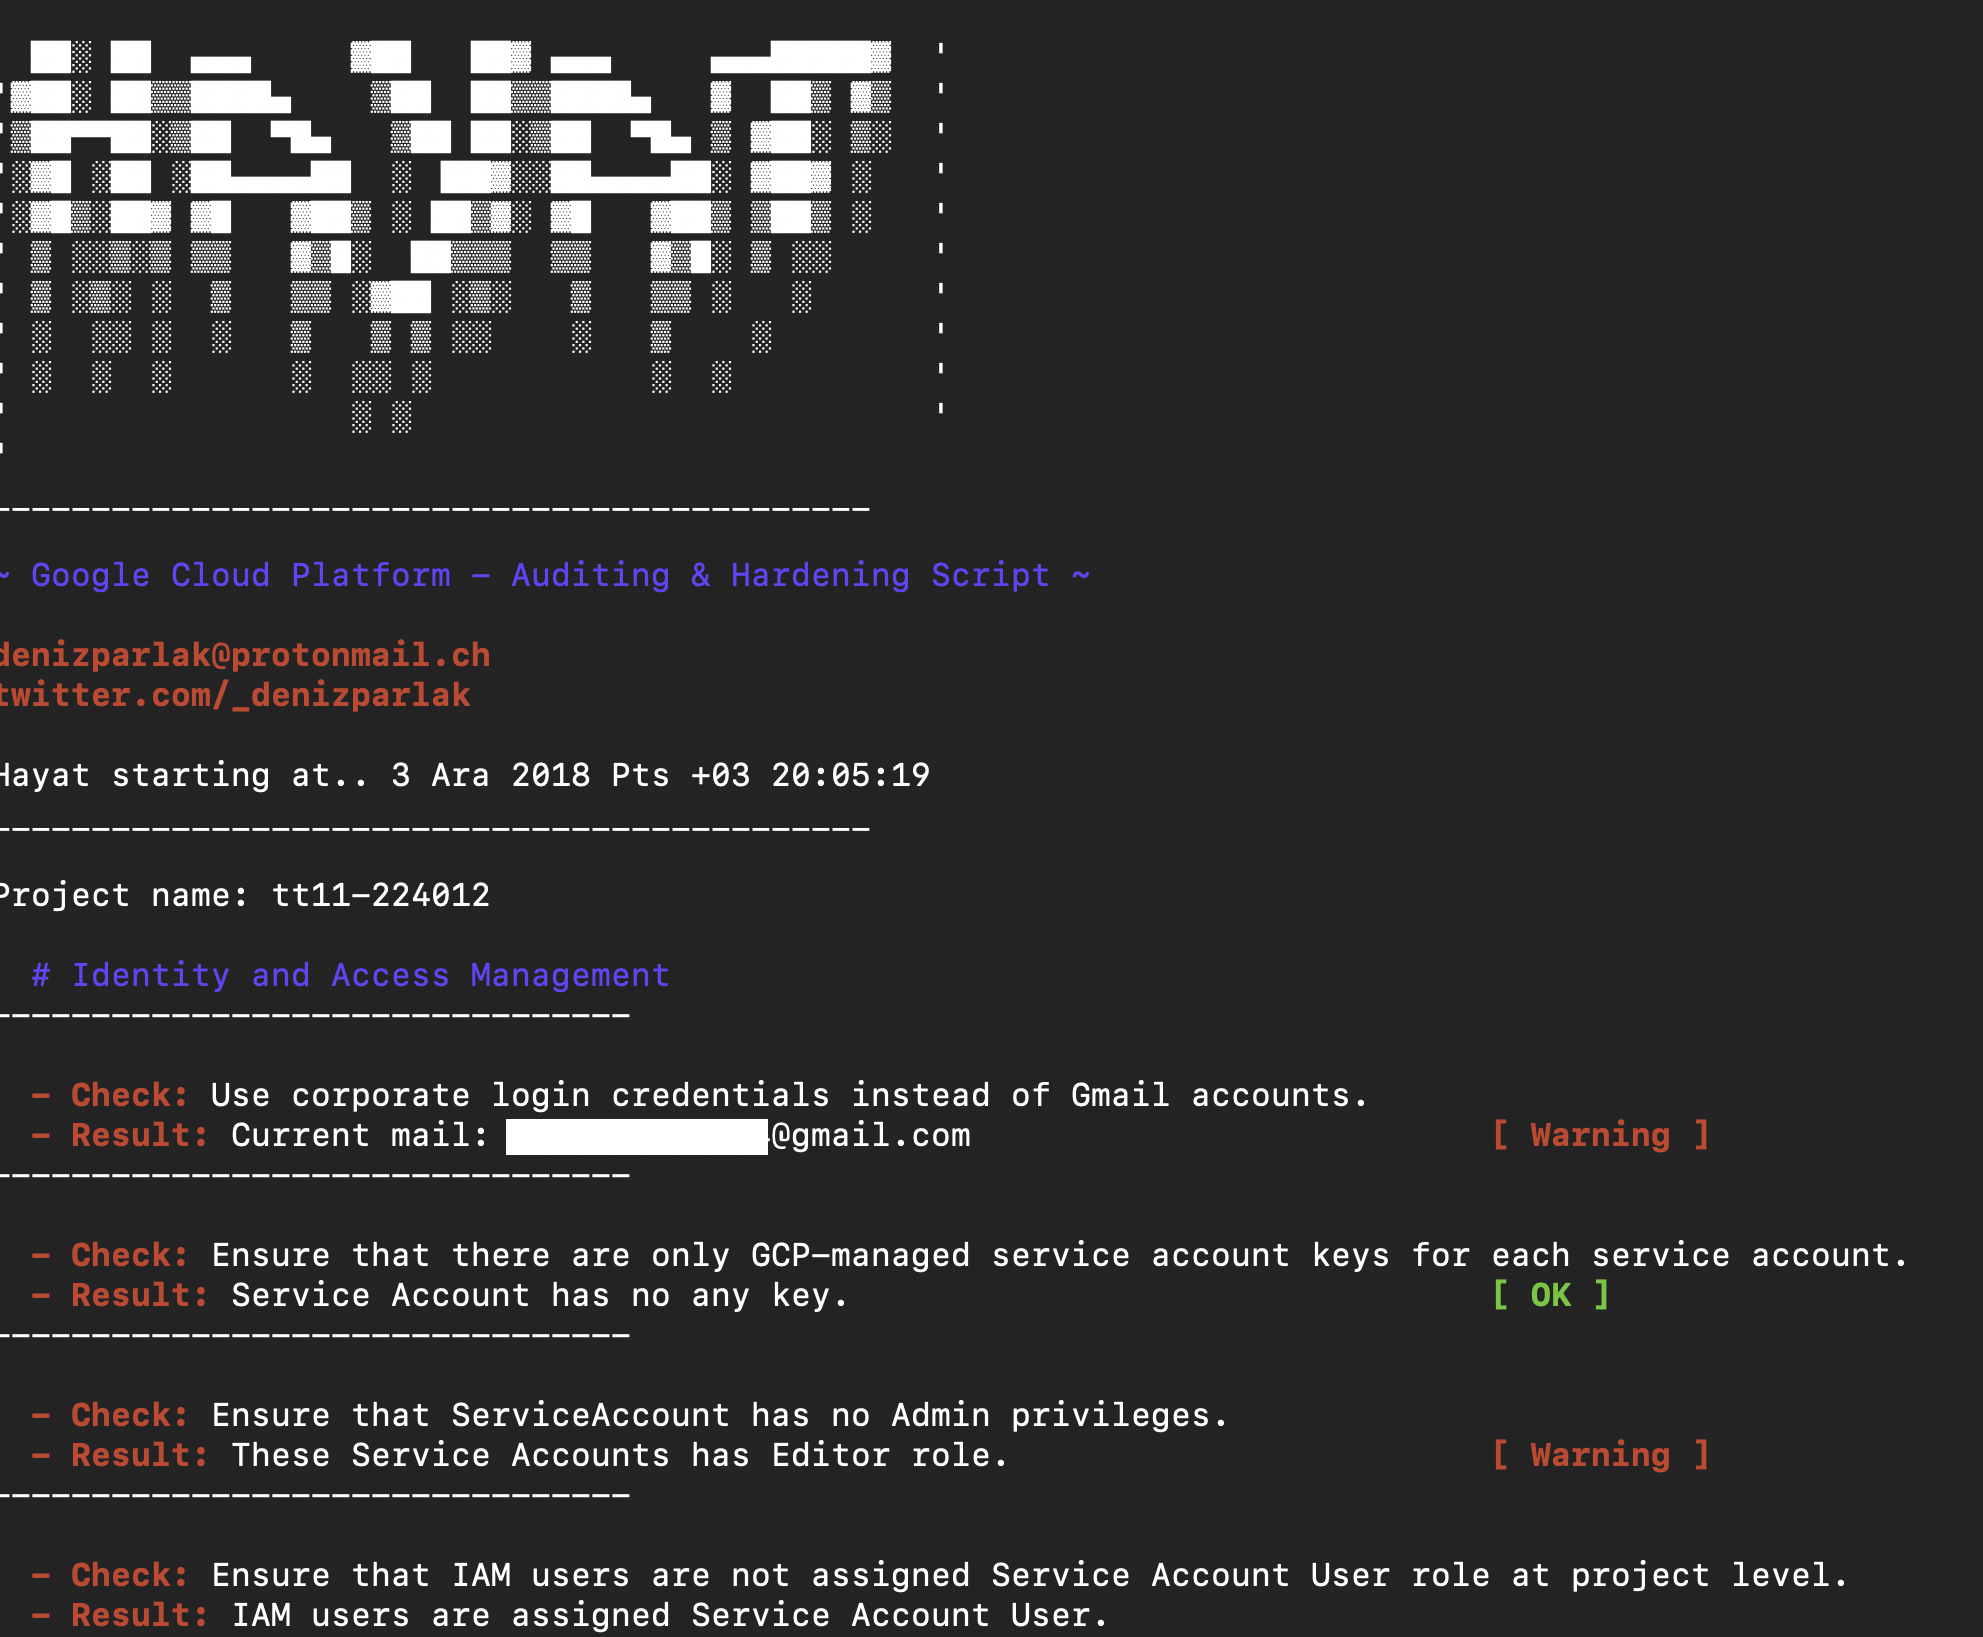 denizparlak/hayat
Hayat is a script for report and analyze Google Cloud Platform resources.
 aquasecurity/trivy-plugin-aqua
Plugin for integrating Trivy with Aqua Security platform to scan IaC, pipelines, and dependencies for vulnerabilities and misconfigurations.
 shahidmallaofficial/cpanel-cve-2026-41940-fix
One-shot detection and remediation for cPanel/WHM servers compromised via CVE-2026-41940, including IOC checks, malware cleanup, C2 blocking, and…
 isagoakira/ghes-cve-scanner
Scans GitHub Enterprise Server instances for CVE-2026-3854 and CVE-2026-4821, providing version-based detection with batch scanning and multiple…
 omerati/almalinux-fix-cve-2026-31431
Automates kernel patching for CVE-2026-31431 and Dirty Frag, sets secure kernel as default in GRUB, and disables testing repo for production safety.
 hodgeluke/ai-agent-security-research
Open security research on AI coding agent infrastructure. Agent-executable remediation manifests for CVE-2026-22812 and CVE-2026-22813.
 netflix/security_monkey
Security Monkey monitors AWS, GCP, OpenStack, and GitHub orgs for assets and their changes over time.
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 microsoft/azurelinux
Hardened, Azure-optimized Linux distribution built from Fedora sources with RPM packaging, supply chain security, and declarative configuration for…
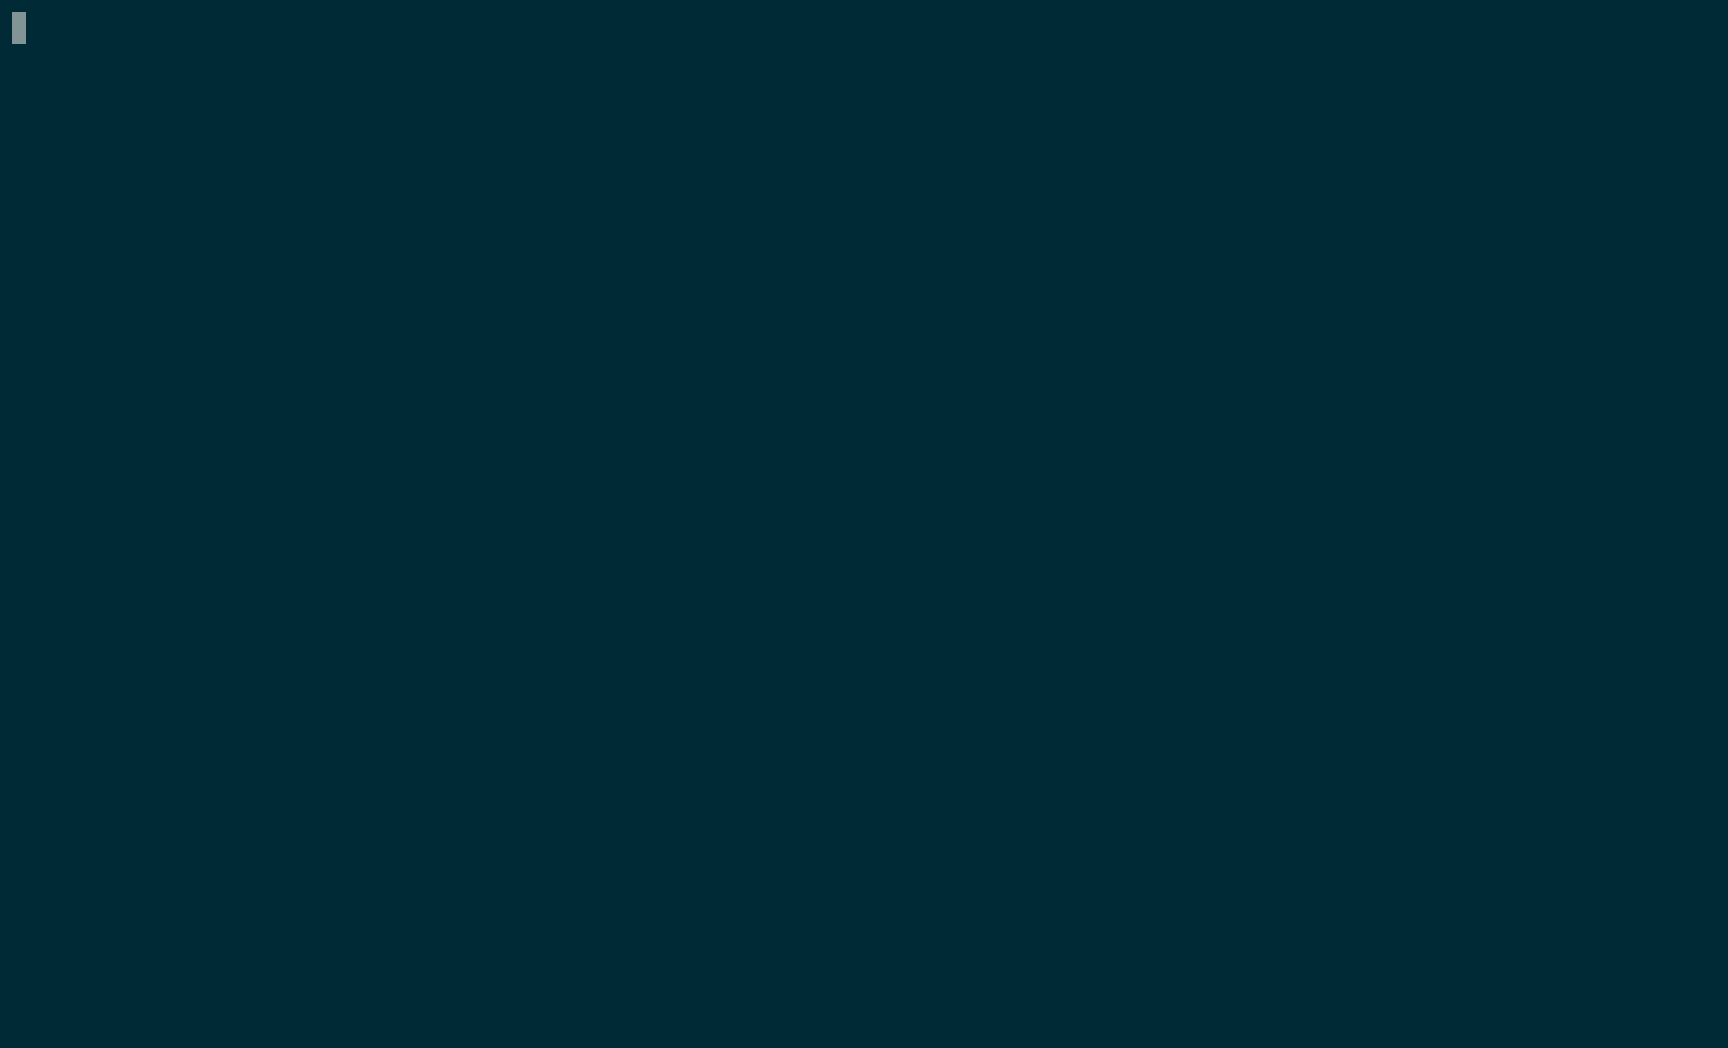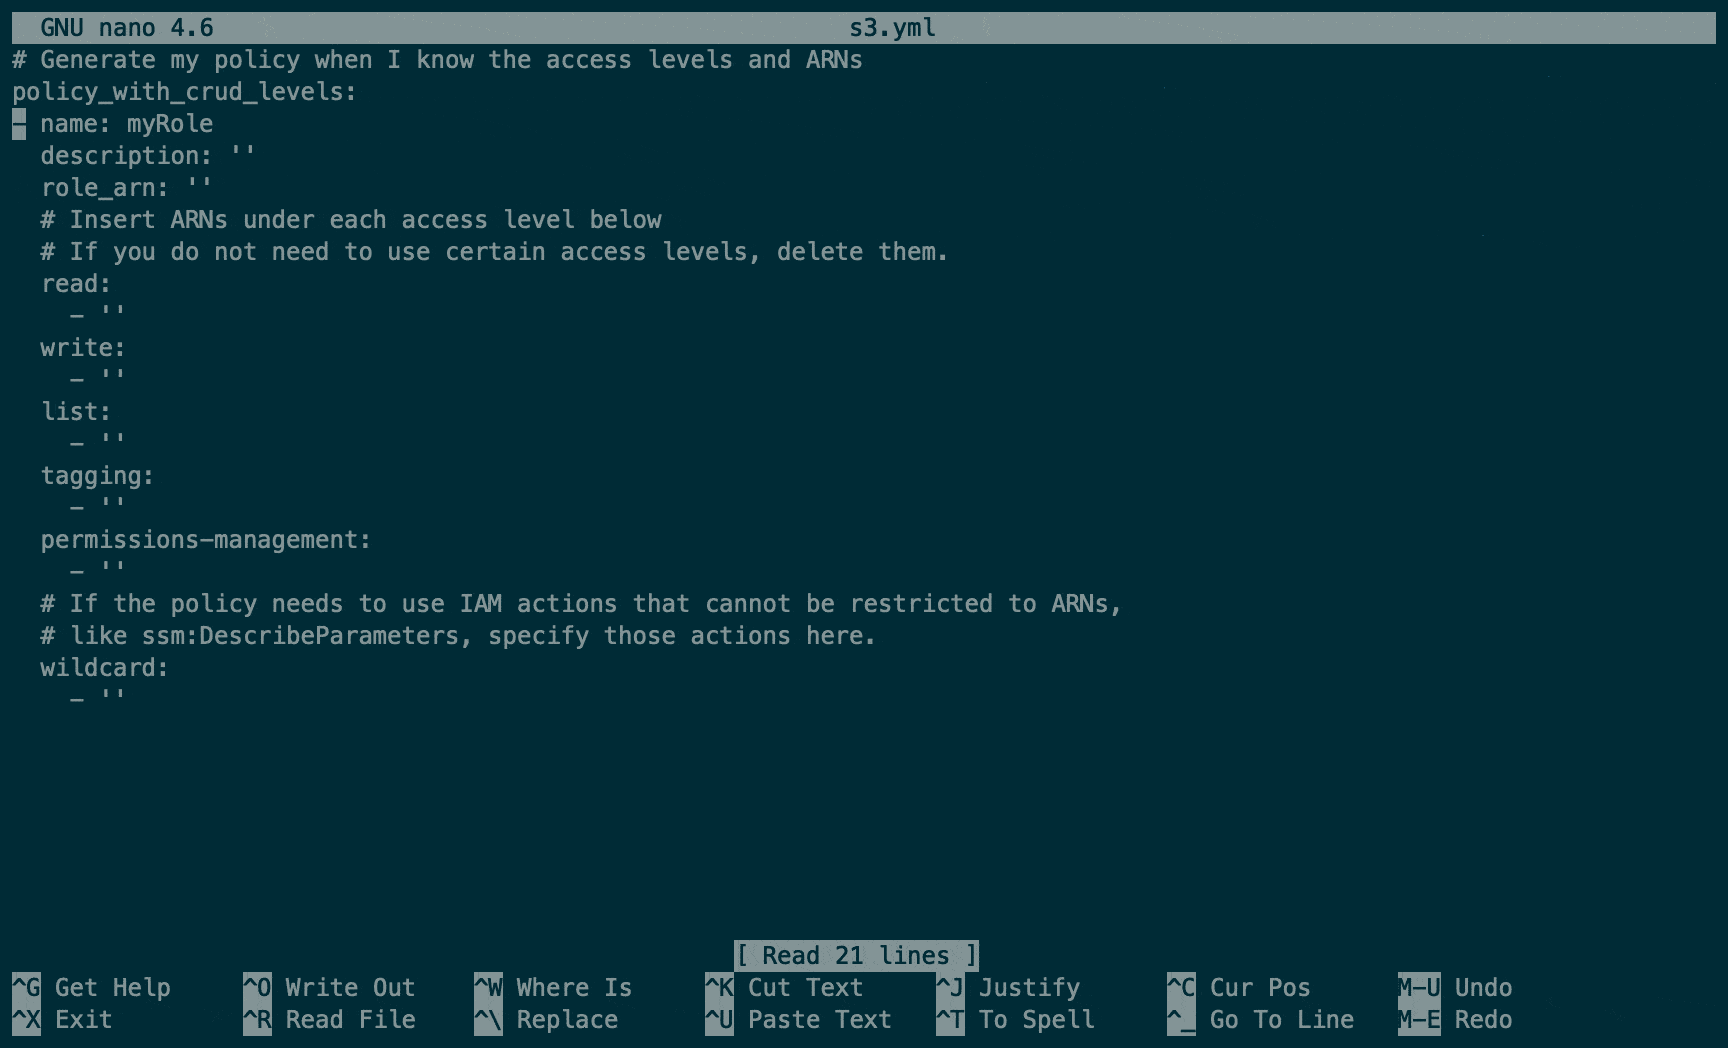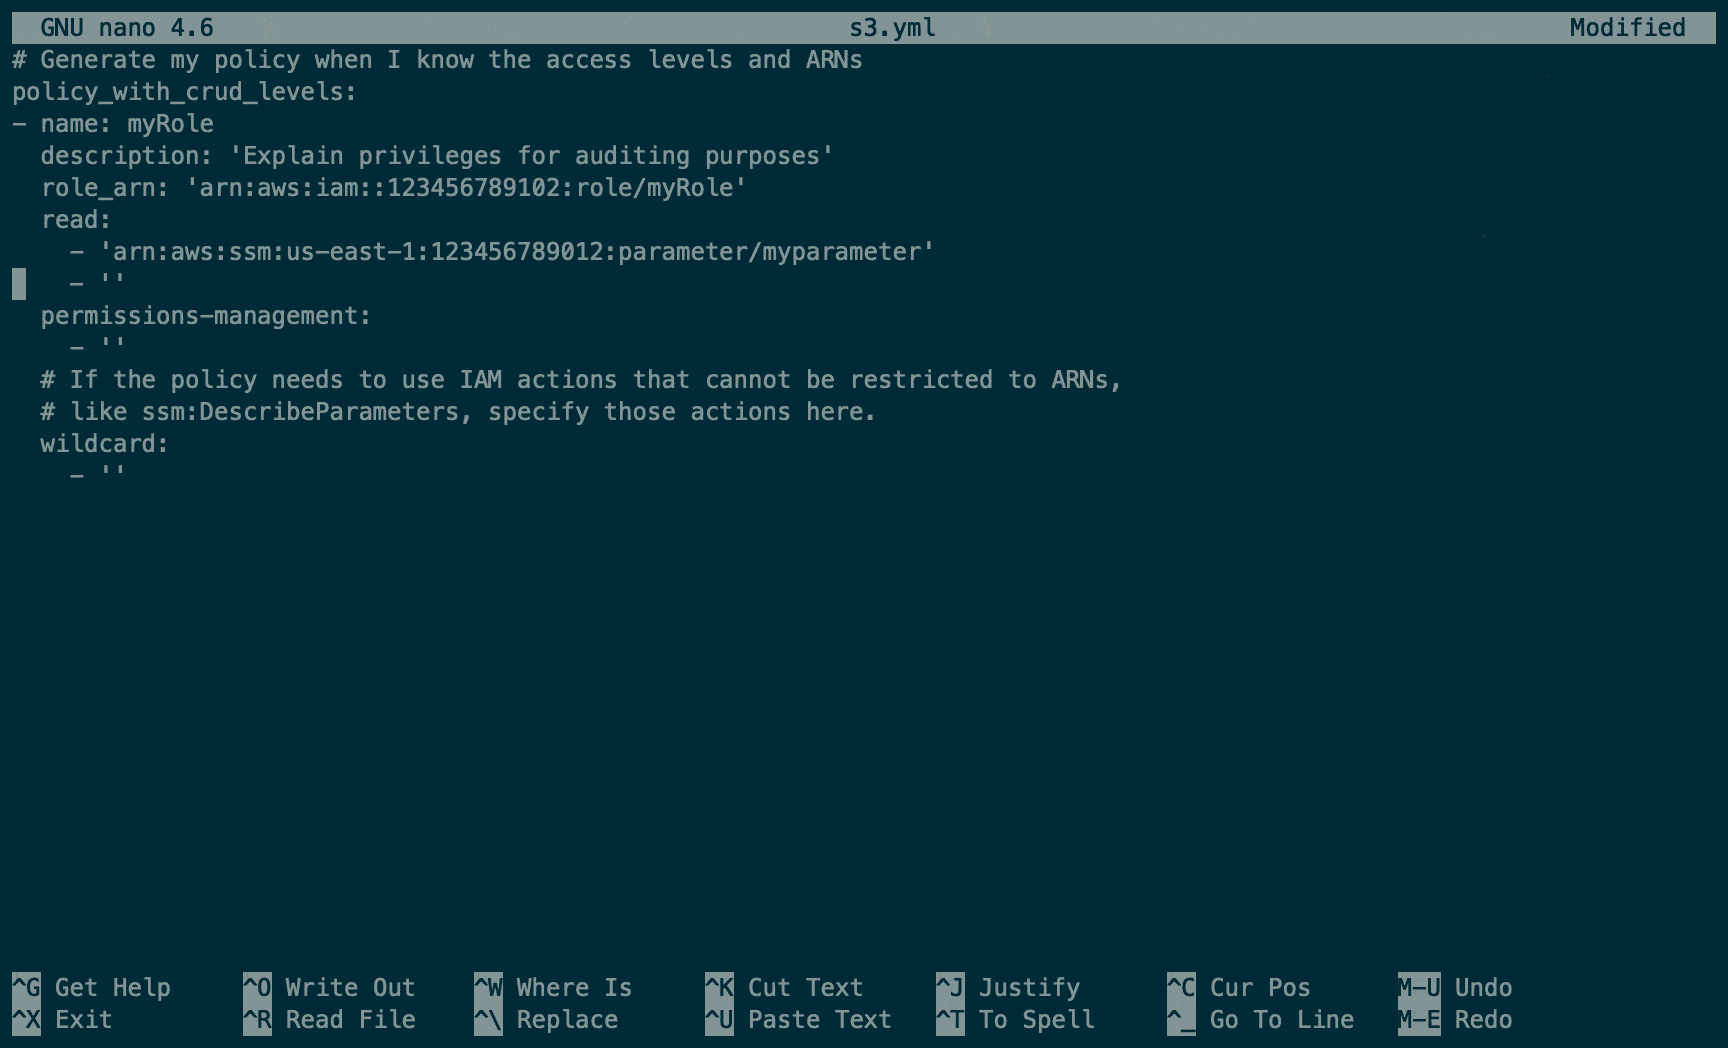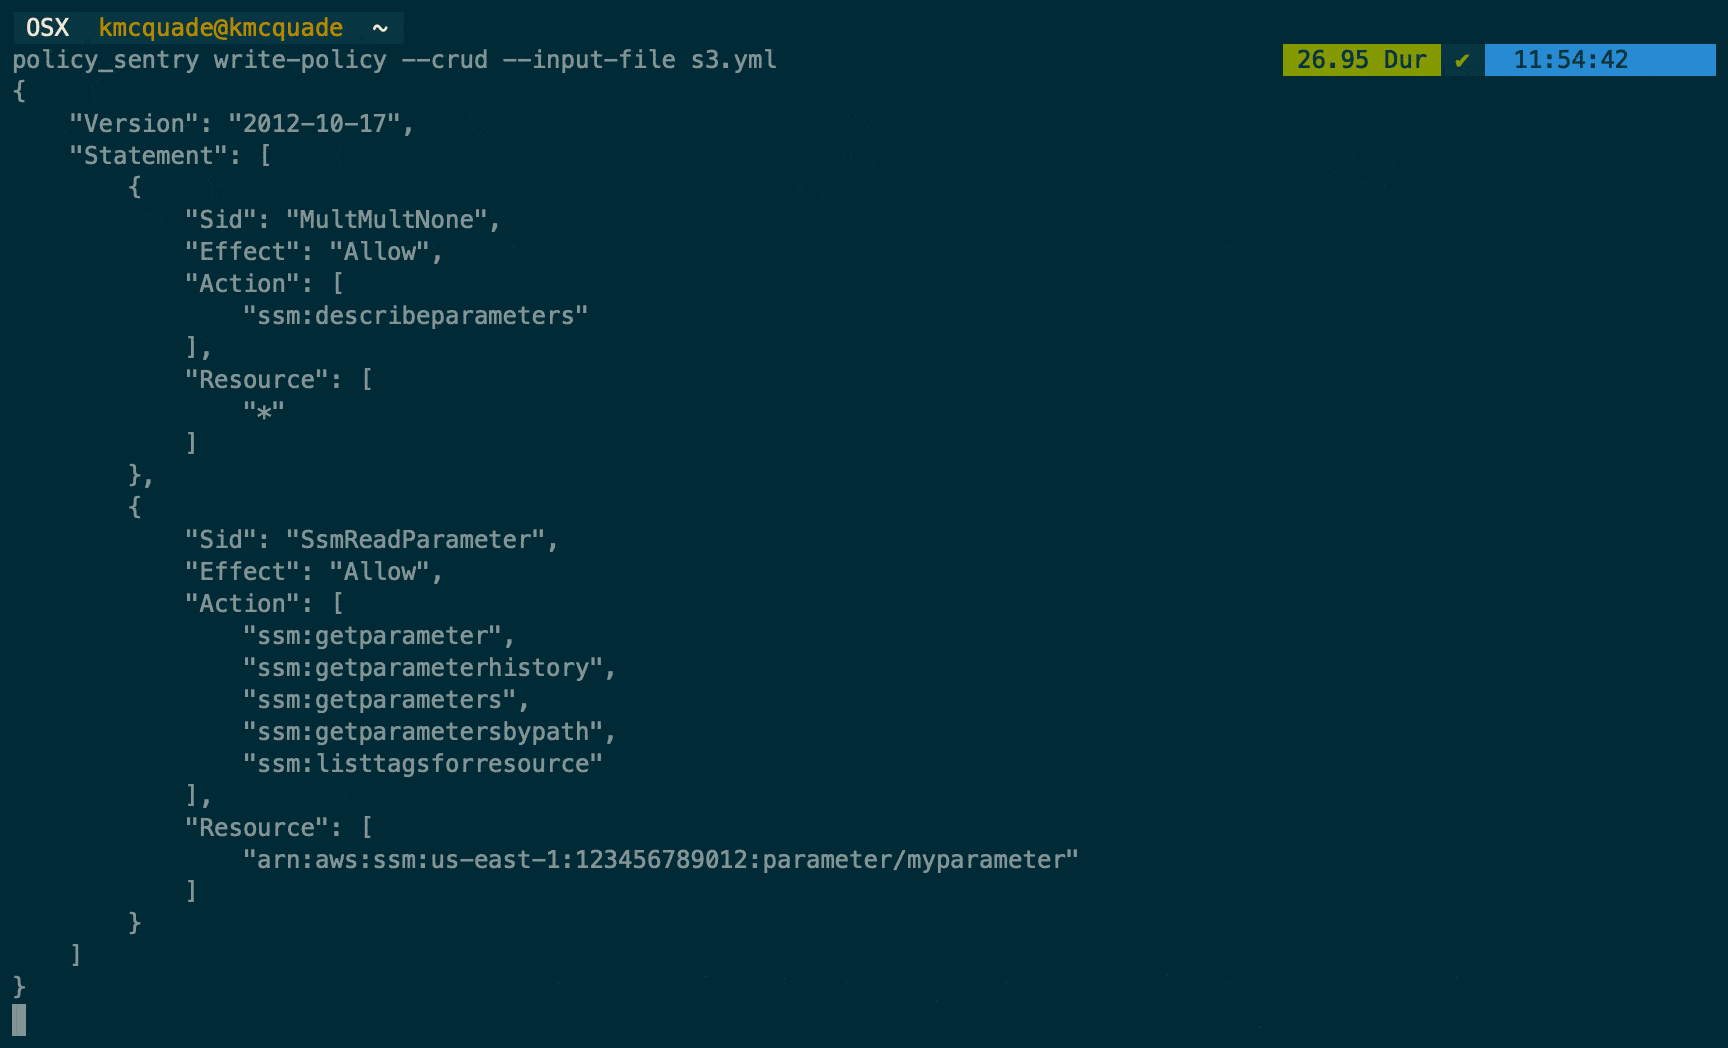 salesforce/policy_sentry
Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.
 tellerops/teller
Cloud native secrets management for developers - never leave your command line for secrets.