
aws-perimeter
 thirukguru/aws-perimeter
A terminal-based AWS Security Scanner with 102+ security checks across VPC, IAM, S3, CloudTrail, containers (ECS/EKS), and AI attack detection.…
ai-securitycloud-infrastructure-securitycloud-security+9
3
thirukguru/aws-perimeterA terminal-based AWS Security Scanner with 102+ security checks across VPC, IAM, S3, CloudTrail, containers (ECS/EKS), and AI attack detection.…
 hacktricks-wiki/hacktricks-cloud
Community-driven knowledge base for pentesting cloud environments and CI/CD pipelines: attack techniques, enumeration, privilege escalation, and…
 mandiant/azure_workshop
Terraform-deployable vulnerable-by-design Azure lab with realistic attack paths and common misconfigurations for practicing red teaming and security…
 nccgroup/scoutsuite
Multi-cloud security auditing tool that leverages cloud provider APIs to gather configuration data, assess security posture, and generate HTML…
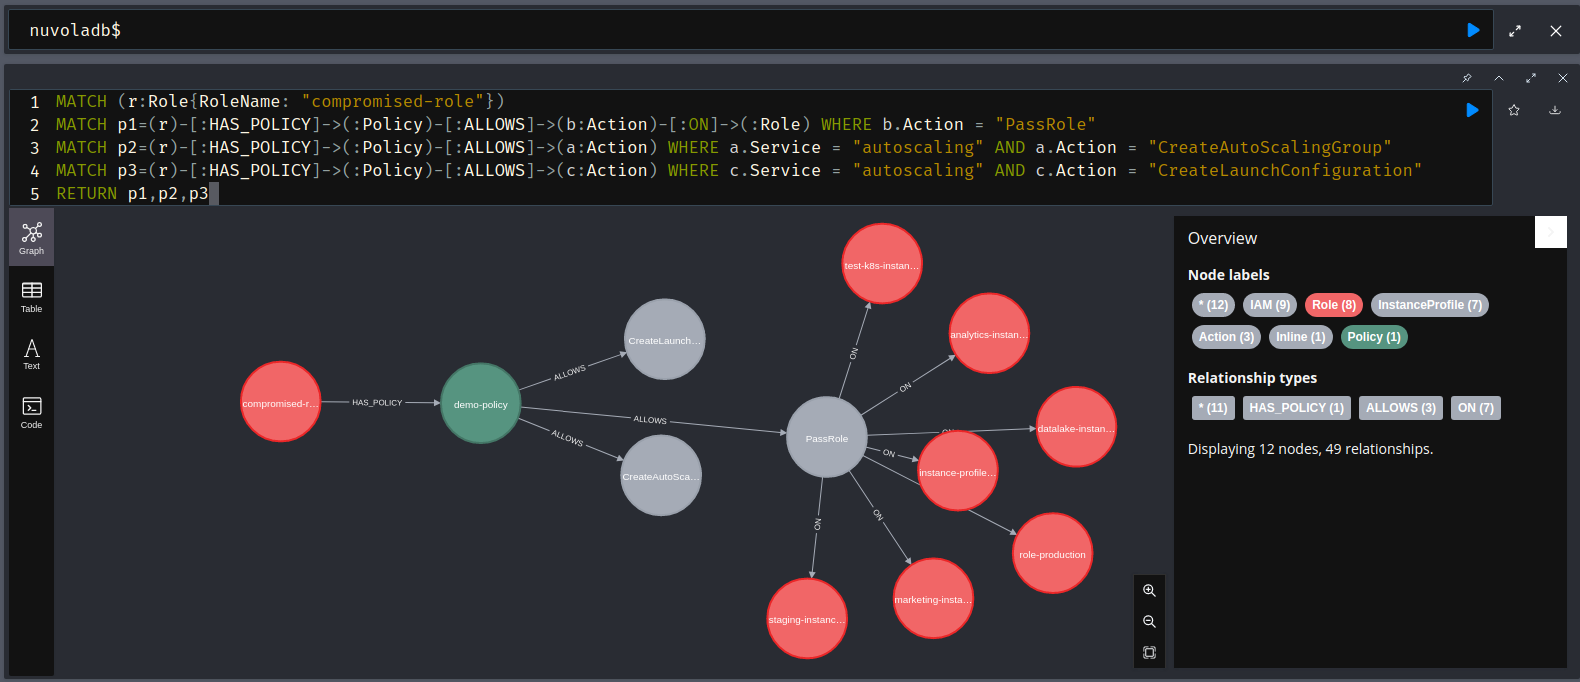 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
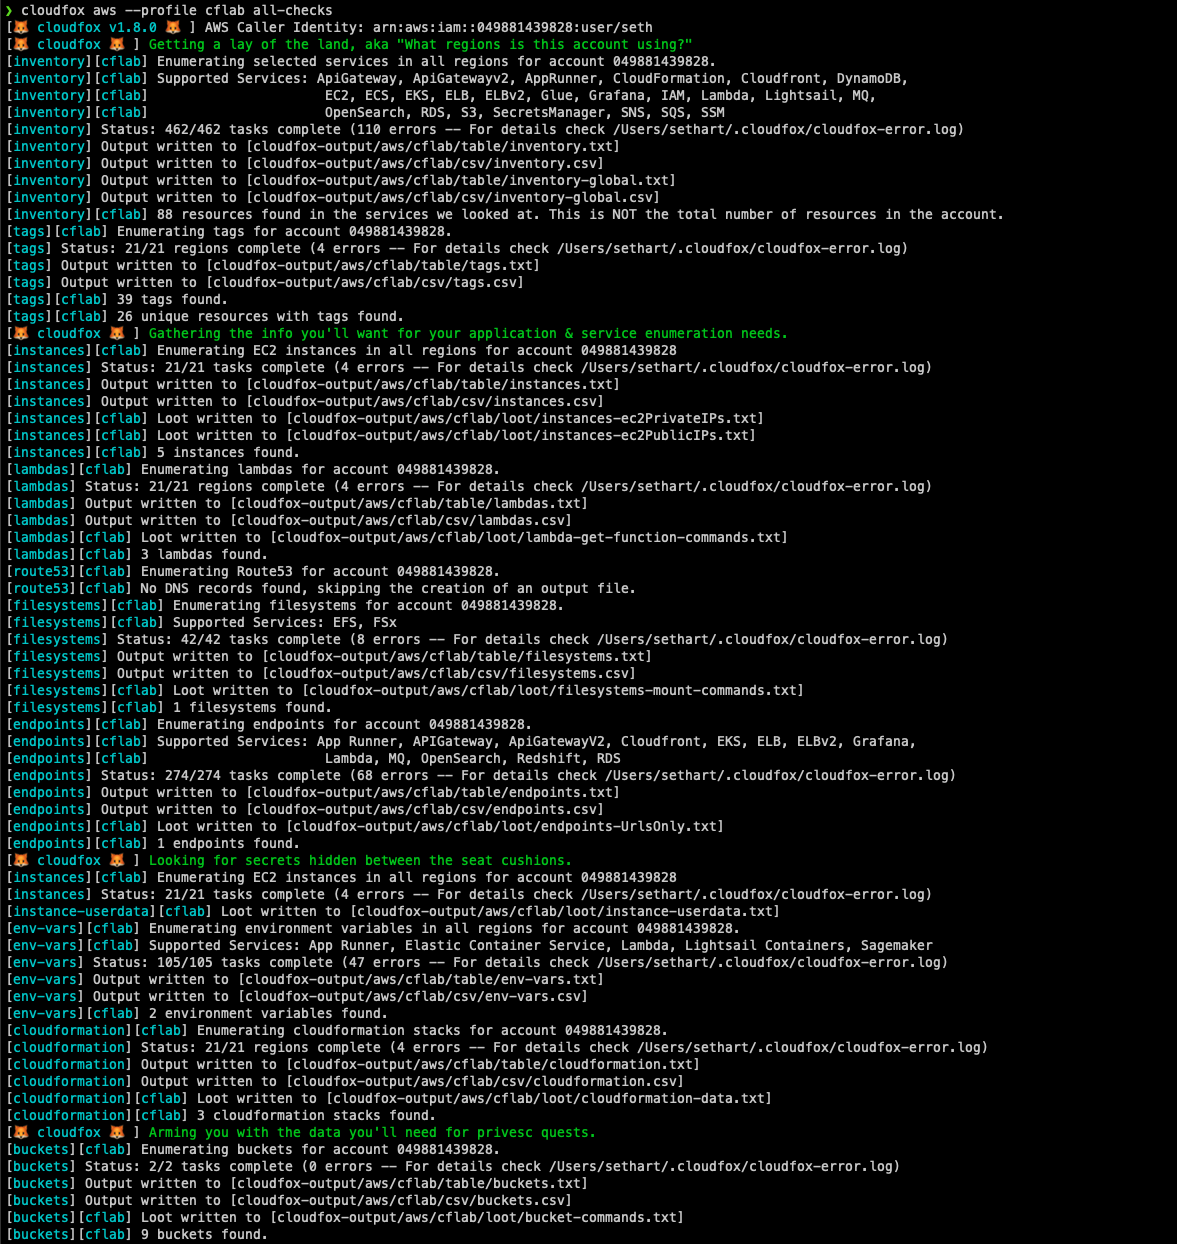 bishopfox/cloudfox
Automating situational awareness for cloud penetration tests.
 george0papasotiriou/cve-2026-5556-kubernetes-admission-controller-bypass-via-case-sensitivity
Exploit PoC and vulnerable admission webhook for CVE-2026-5556, demonstrating Kubernetes admission controller bypass via case-sensitive pod name…
 datadog/stratus-red-team
:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud
 c0axx/canaryhunter
Canary Hunter aims to be a quick PowerShell script to check for Common Canaries in various formats generated for free on canarytokens.org
 h4wkst3r/dop2mop
OpenGraph collector for BloodHound that maps attack paths from DevOps to MLOps infrastructure, collecting CI/CD pipeline, service principal, and ML…
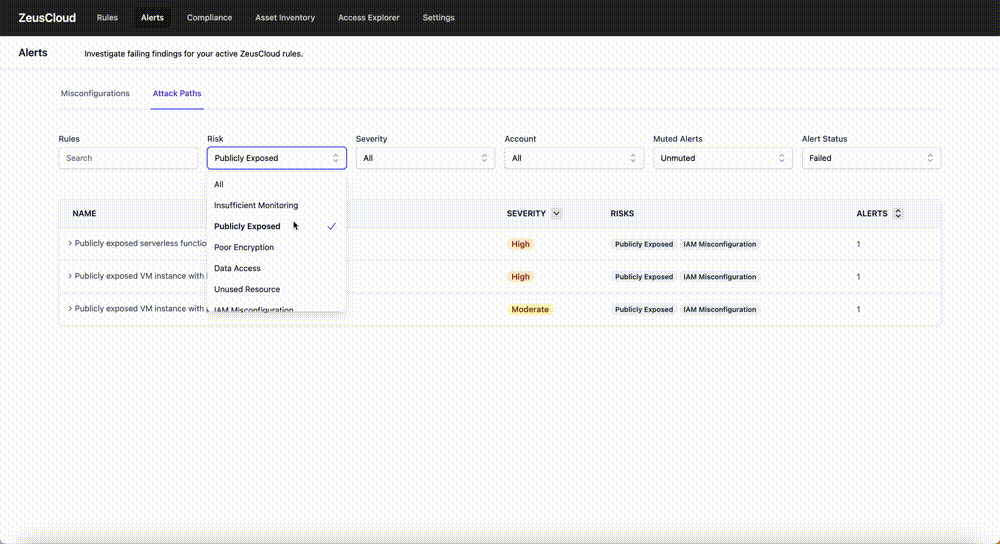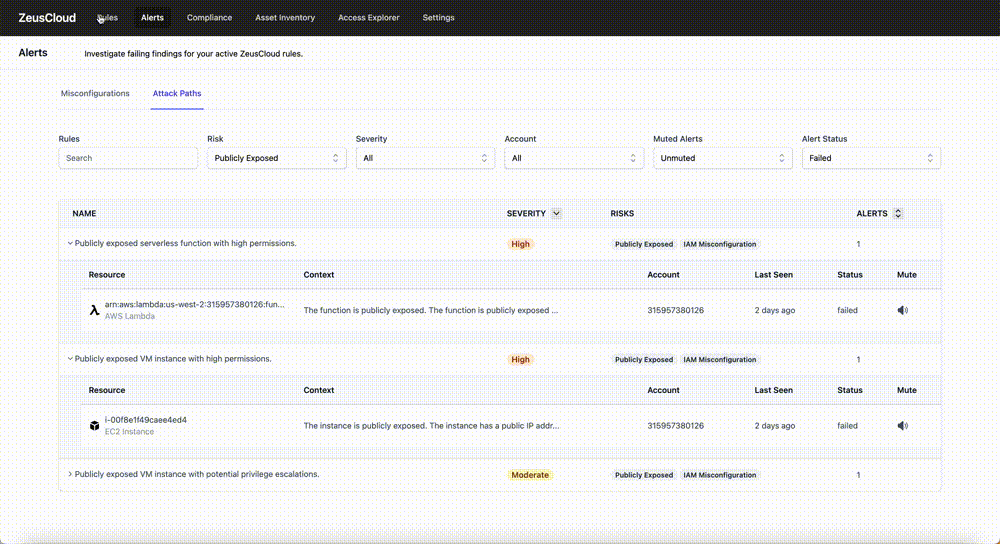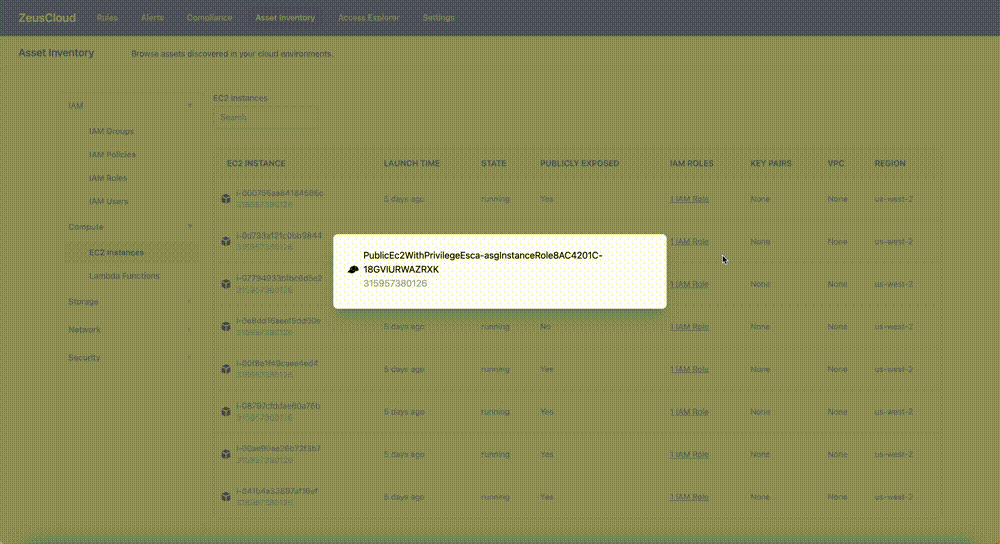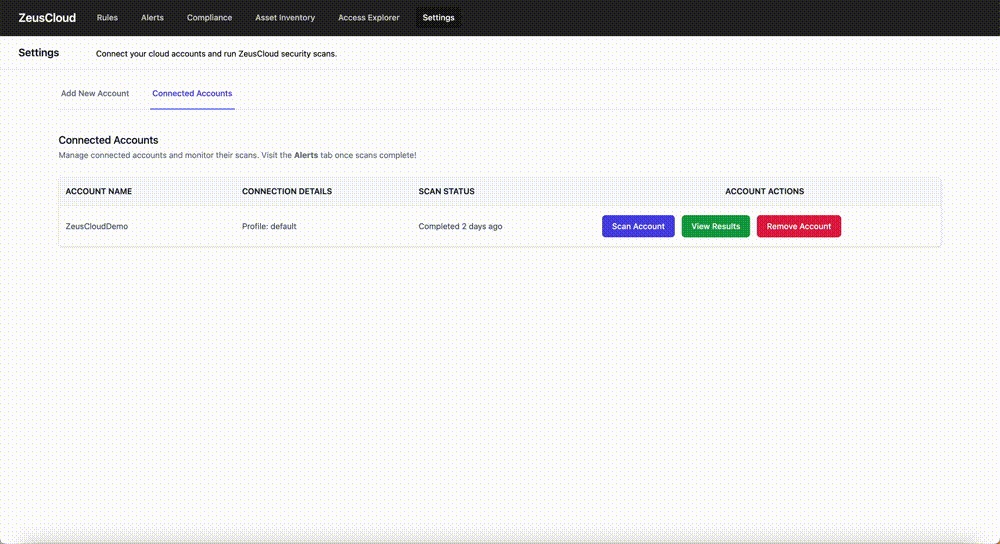 zeus-labs/zeuscloud
Open-source cloud security platform that discovers attack paths, identifies misconfigurations, visualizes IAM access, and provides step-by-step…
 natlas/natlas
Attack Surface Management since before Attack Surface Management was a thing
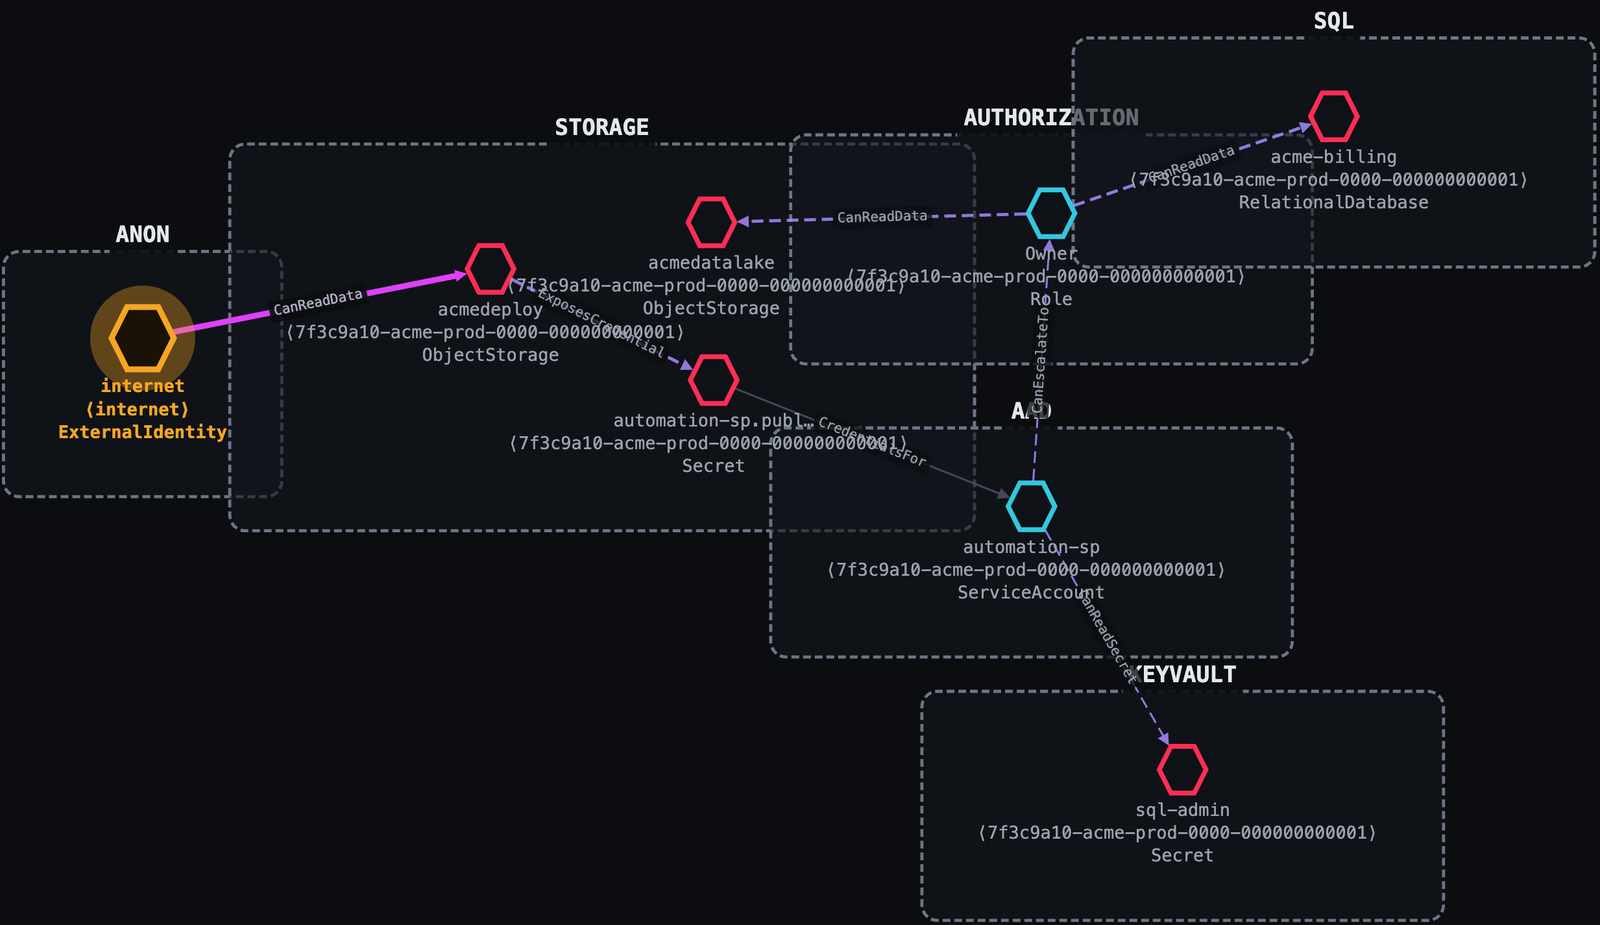 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 kozmer/aad-bofs
Cobalt Strike BOF collection for attacking Azure AD during red team operations, covering authentication, enumeration, and post-exploitation vectors.
 george0papasotiriou/cve-2026-21019-kubernetes-cronjob-suspended-execution-via-time-manipulation
Reproduces CVE-2026-21019 by manipulating node clock to force early Kubernetes CronJob execution; includes vulnerable YAML manifest and Python…
 disqualifier/psa-2026-00043-recovery
Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)
 npm/ansible-bashpocalypse
Patch for CVE-2014-6271