
laforge
 gen0cide/laforge
Competition Infrastructure Management
cloud-infrastructure-securityctfeducation+1
gen0cide/laforgeCompetition Infrastructure Management
 rhinosecuritylabs/iamactionhunter
An AWS IAM policy statement parser and query tool.
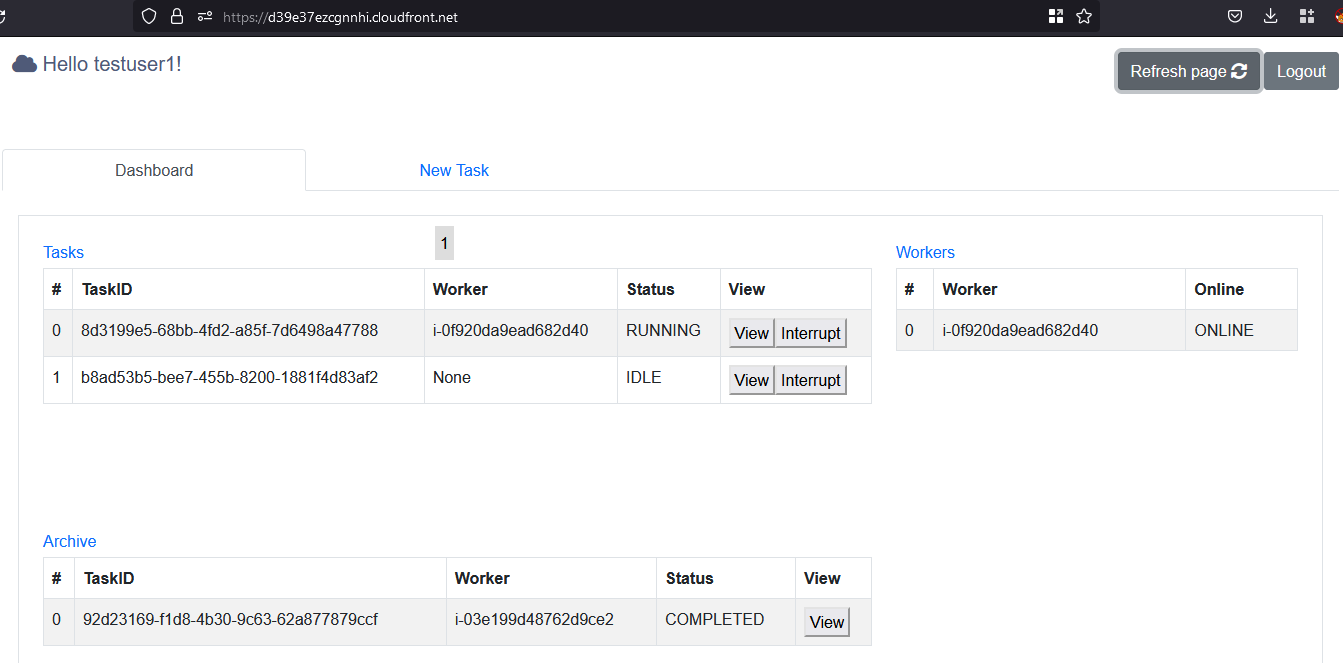 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
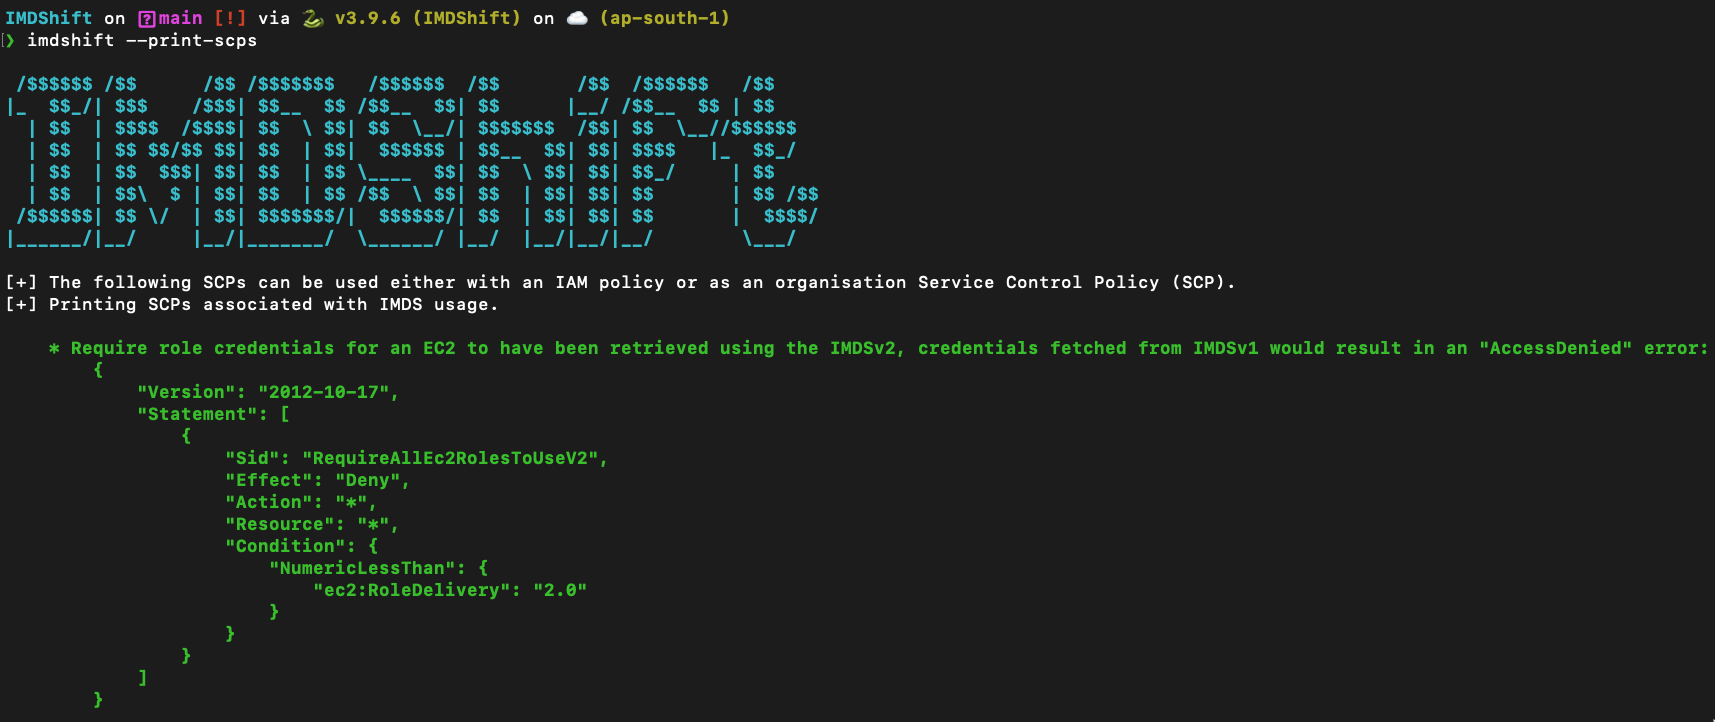 ayushpriya10/imdshift
Automates migration of AWS workloads from IMDSv1 to IMDSv2 to mitigate SSRF attacks. Detects IMDSv1 usage across EC2, ECS, EKS, Lightsail, and more,…
 contrastsecurity/contrast
SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
 akhld/spark-exploit
Arbitary Code Execution in Unsecured Apache Spark Cluster
 mandiant/vcsa-hardening-tool
Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)
 shahidmallaofficial/cpanel-cve-2026-41940-fix
One-shot detection and remediation for cPanel/WHM servers compromised via CVE-2026-41940, including IOC checks, malware cleanup, C2 blocking, and…
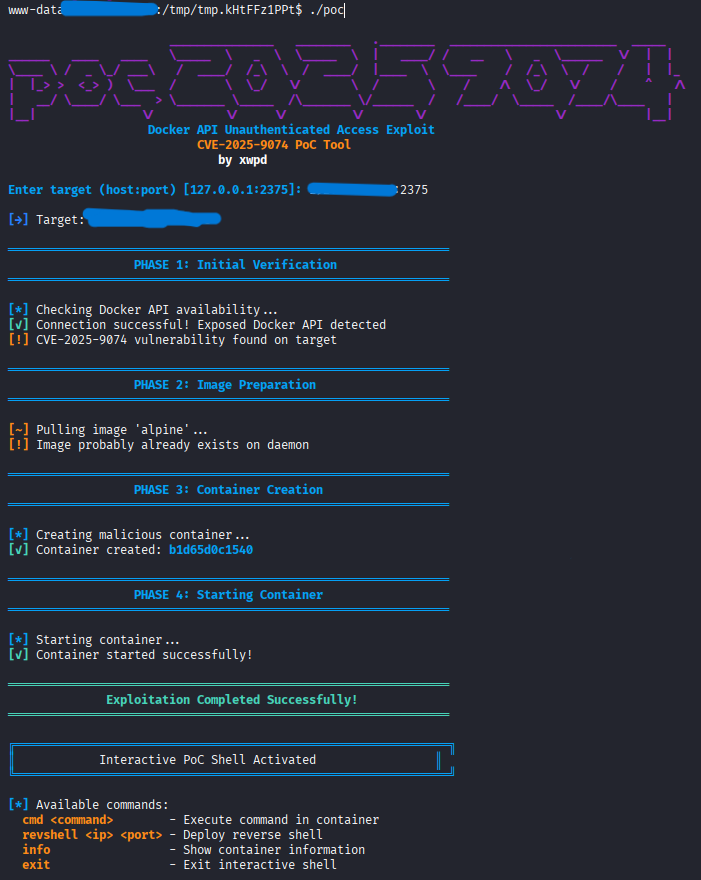 xwpdx0/poc-2025-9074
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…
 aestechno/cve-2026-31431-ansible
Ansible playbook to detect and apply kernel cmdline mitigation for CVE-2026-31431 (Copy Fail) across Debian/Ubuntu/RHEL fleets, with read-only…
 jithinkrishnanrs/cve-2026-67401-cpanel-emailtrack-sqli
Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…
 0xblackash/cve-2026-64531
Reference analysis of a Linux kernel Open vSwitch memory-corruption vulnerability, covering root cause, impact, detection commands, and mitigation…
 bishopfox/cve-2026-58073-check
Safely detect Veeam Service Provider Console auth bypass CVE-2026-58073
 dumbmachine/cloud-doctor
One command grades your whole cloud account — misconfigurations, missing observability, and security posture.
 fazmin/vcenter-server-workaround-script-cve-2021-44228
Script - Workaround instructions to address CVE-2021-44228 in vCenter Server
 boliu83/cve-2026-31431-algif-aead-remediator
Kubernetes DaemonSet to detect and remediate CVE-2026-31431 (GHSA-2274-3hgr-wxv6) — algif_aead LPE via modprobe blacklist
 dawnsmithcyber/azure-vulnerability-remediation-project
End-to-end vulnerability management lifecycle on Azure Windows Server 2025. Features OS patching and network-level compensating controls (NSG) to…
 teresh1/cve-2025-12748
Proof of concept for CVE-2025-12748, a denial-of-service vulnerability in libvirt XML processing that bypasses ACL checks, allowing resource…