aws_exposable_resources

Curated catalog of AWS resource types that can be publicly exposed, with CLI commands for creating and auditing public access configurations across…

Curated catalog of AWS resource types that can be publicly exposed, with CLI commands for creating and auditing public access configurations across…

BucketLoot is an automated S3-compatible bucket inspector that can help users extract assets, flag secret exposures and even search for custom…

Event-driven AWS security misconfiguration detection framework that monitors multiple accounts in real-time, triggering alerts via Lambda for IAM,…

Service that scans your Infrastructure as Code for common vulnerabilities

Exploit for CVE-2019-5736: runc container escape that overwrites host docker-runc binary with a payload, triggered via docker exec.

we are providing DevOps and security teams script to identify cloud workloads that may be vulnerable to the Log4j vulnerability(CVE-2021-44228) in…

Aurea is an open-source, AI-powered platform that secures infrastructure-as-code (IaC) across Terraform, Kubernetes, Docker, and Ansible. It…

OpenGraph collector for BloodHound that maps attack paths from DevOps to MLOps infrastructure, collecting CI/CD pipeline, service principal, and ML…

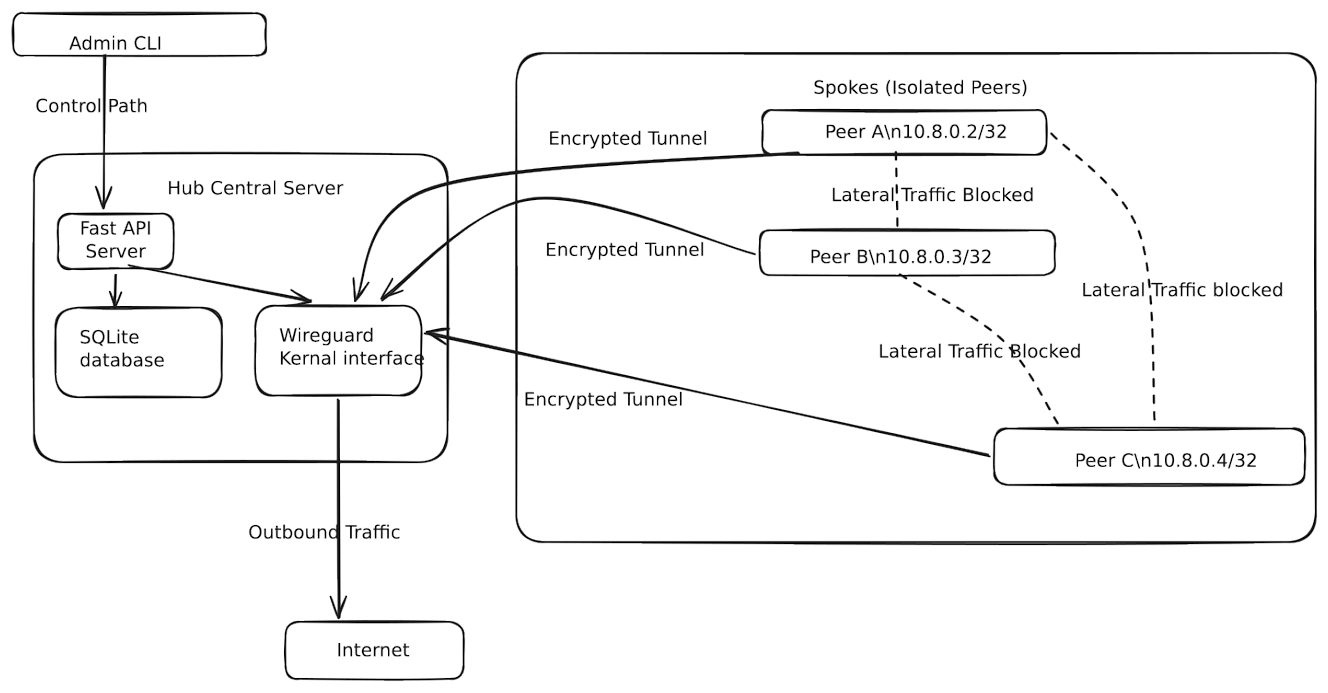
A lightweight, policy-driven framework that brings Zero-Trust micro-segmentation to SOHO networks using WireGuard.

This repository contains BigFix Content that I created for identifying the AlmaLinux systems that require patching to remediate CVE-2026-31431

A Kroxylicious filter plugin that provides transparent post-quantum (ML-KEM + AES-256-GCM) record-level encryption for Apache Kafka, requiring zero…

Proof of concept for CVE-2025-12748, a denial-of-service vulnerability in libvirt XML processing that bypasses ACL checks, allowing resource…

CVE-2025-54914 exposes a critical flaw in Azure Networking that allows attackers to escalate privileges and control routing across subnets. The…

OPA Gatekeeper constraint policy that detects and prevents Kubernetes clusters from being vulnerable to CVE-2020-8554, enforcing secure configuration.

OpenID Connect (OIDC) identity and OAuth 2.0 provider with pluggable connectors

Checks whether Kubernetes is deployed according to security best practices as defined in the CIS Kubernetes Benchmark

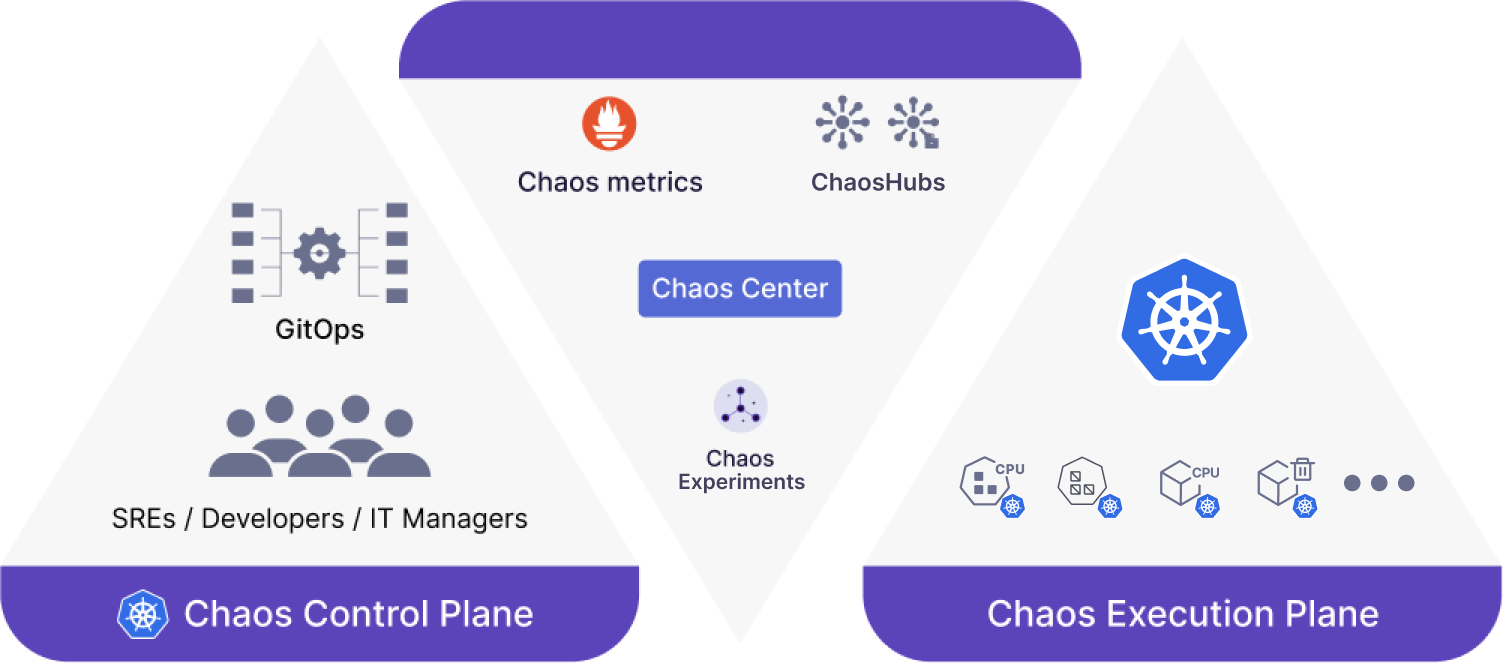
Cloud-native chaos engineering platform for Kubernetes with fault injection, workflow orchestration, and steady-state validation to surface system…

Infrastructure as code for DNS!