
CVE-2020-8554
Proof-of-concept exploit for CVE-2020-8554, demonstrating Kubernetes service externalIP manipulation to achieve man-in-the-middle attacks on cluster…

Proof-of-concept exploit for CVE-2020-8554, demonstrating Kubernetes service externalIP manipulation to achieve man-in-the-middle attacks on cluster…

Terraform-deployed red team operator lab on AWS: Mythic, Sliver, and Adaptix C2 behind a production-style Apache redirector, with Kali/Windows hosts…

Multi-threaded AWS inventory collection tool with a focus on security-relevant resources and metadata.

Prevent SSRF attacks on AWS EC2 via automated upgrades to the more secure Instance Metadata Service v2 (IMDSv2).

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …

Meaningful control of data in distributed systems.

An open source, cloud-native security to protect everything from build to runtime

A little tool to play with Azure Identity - Azure and Entra ID lab creation tool. Blog: https://medium.com/@iknowjason/sentinel-for-purple-teaming-1…

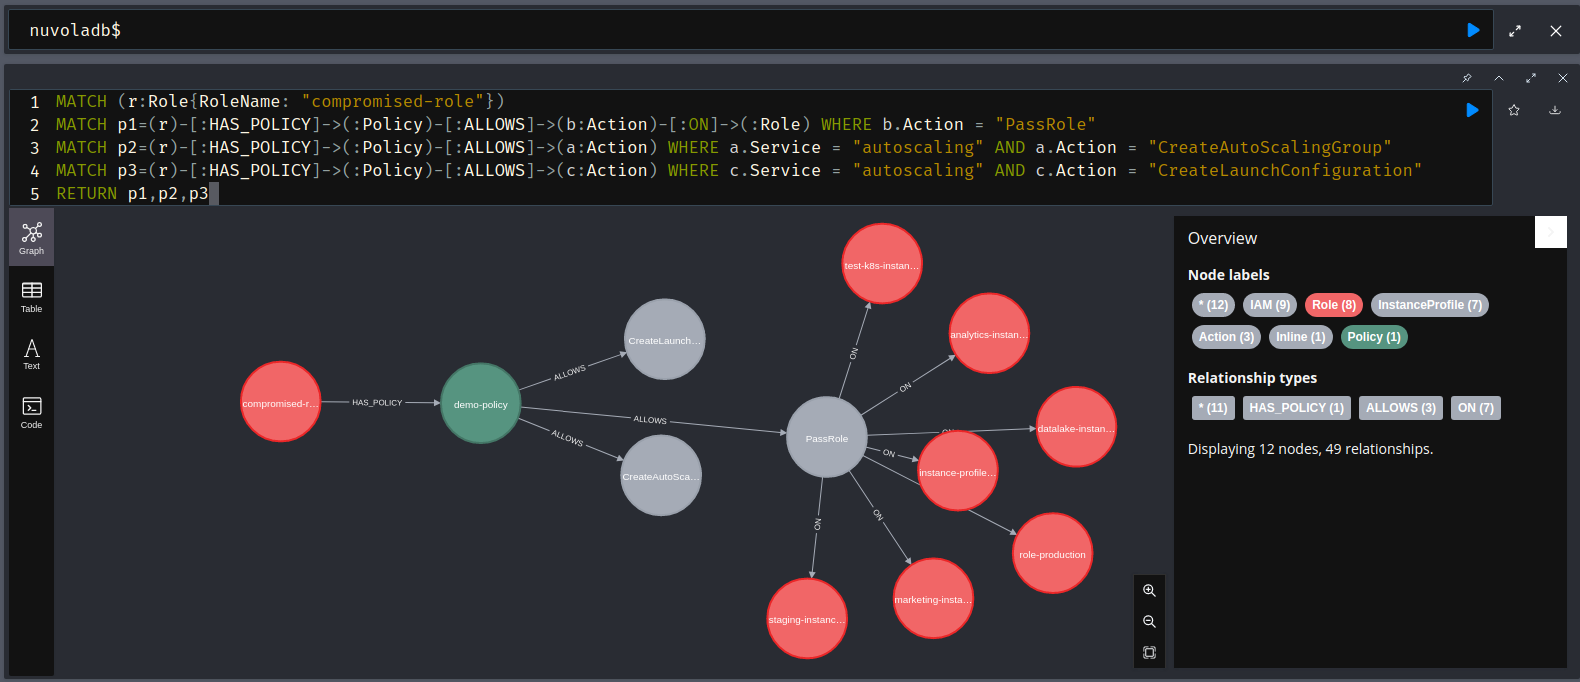
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…

Powershell module for VMWare vSphere forensics

Event-driven AWS security misconfiguration detection framework that monitors multiple accounts in real-time, triggering alerts via Lambda for IAM,…

Like Envoy xDS, but for eBPF filters

Clean accounts over permissions in GCP infra at scale

Automates migration of AWS workloads from IMDSv1 to IMDSv2 to mitigate SSRF attacks. Detects IMDSv1 usage across EC2, ECS, EKS, Lightsail, and more,…

Exploit for Linux kernel CVE-2026-31431 causing page cache corruption via authencesn AEAD manipulation, targeting privilege escalation in containers…

On-prem API gateway for AI coding agents with per-engineer cost attribution, hard budgets, egress governance (secrets/entity scanning), context-rot…

Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…