
cve_2026_frag_family_fix
 first-john/cve_2026_frag_family_fix
CVE-2026-46300 / CVE-2026-43500 / CVE-2026-31431 / CVE-2026-43284 golang hotfix
cloud-infrastructure-securitycloud-securityconfiguration-auditing+4
first-john/cve_2026_frag_family_fixCVE-2026-46300 / CVE-2026-43500 / CVE-2026-31431 / CVE-2026-43284 golang hotfix
 rjt-gupta/cve-2021-33104
CVE-2021-33104 - Improper access control in the Intel(R) OFU software
 chusiang/cve-2016-3714.ansible.role
Fix ImageMagick Command Injection (CVE-2016-3714) with Ansible.
 fazmin/vcenter-server-workaround-script-cve-2021-44228
Script - Workaround instructions to address CVE-2021-44228 in vCenter Server
 m0nk3ygod/cve-2026-34040-poc
Lab reproduction of CVE-2026-34040: bypasses Docker/Moby AuthZ plugins using oversized (>1MB) request bodies to create privileged containers with…
 selectel/mks-copy-fail-mitigation
DaemonSet с реализацией временной меры для митигации уязвимости Copy Fail (CVE-2026-31431)
 jshdevs/cve_kernellinux_jsh
Framework modular Bash para auditar CVE-2026-31431 (CopyFail) y CVEs relacionados del kernel Linux en distros RPM-based (AlmaLinux, Rocky, CentOS…
 jbiniek/copy.fail-mitigation-mlm
Salt state to deploy a mitigation of the copy.fail vulnerability (CVE-2026-31431)
 mrmtwoj/ubuntu-cve-2026-31431-mitigation
دستورالعملهای کاهش ریسک و بهروزرسانی برای CVE-2026-31431 در سیستمهای اوبونتو، شامل مراحل ارتقاء کرنل و kmod.
 jdmulloy/meltdown-aws-scanner
Naive shell script to verify Meltdown (CVE-2017-5754) patch status of EC2 instances
 radzarr/wsusresponder
Module PowerShell de réponse à l'incident CVE-2025-59287 — WSUS Remote Code Execution (RCE)
 arnaudluti/ps-cve-2021-44228
Static detection of vulnerable log4j librairies on Windows servers, members of an AD domain.
 ziadsaleemi/polkit_cve-2021-4034
Ansible role to patch RHSB-2022-001 Polkit Privilege Escalation - (CVE-2021-4034)
 daniel-odrinski/cve-2024-6387-mitigation-ansible-playbook
An Ansible Playbook to mitigate the risk of RCE (CVE-2024-6387) until platforms update OpenSSH to a non-vulnerable version.
 atilacastro/update-apt-package
Playbook update APT package because CVE-2019-3462
 project-oak/oak
Meaningful control of data in distributed systems.
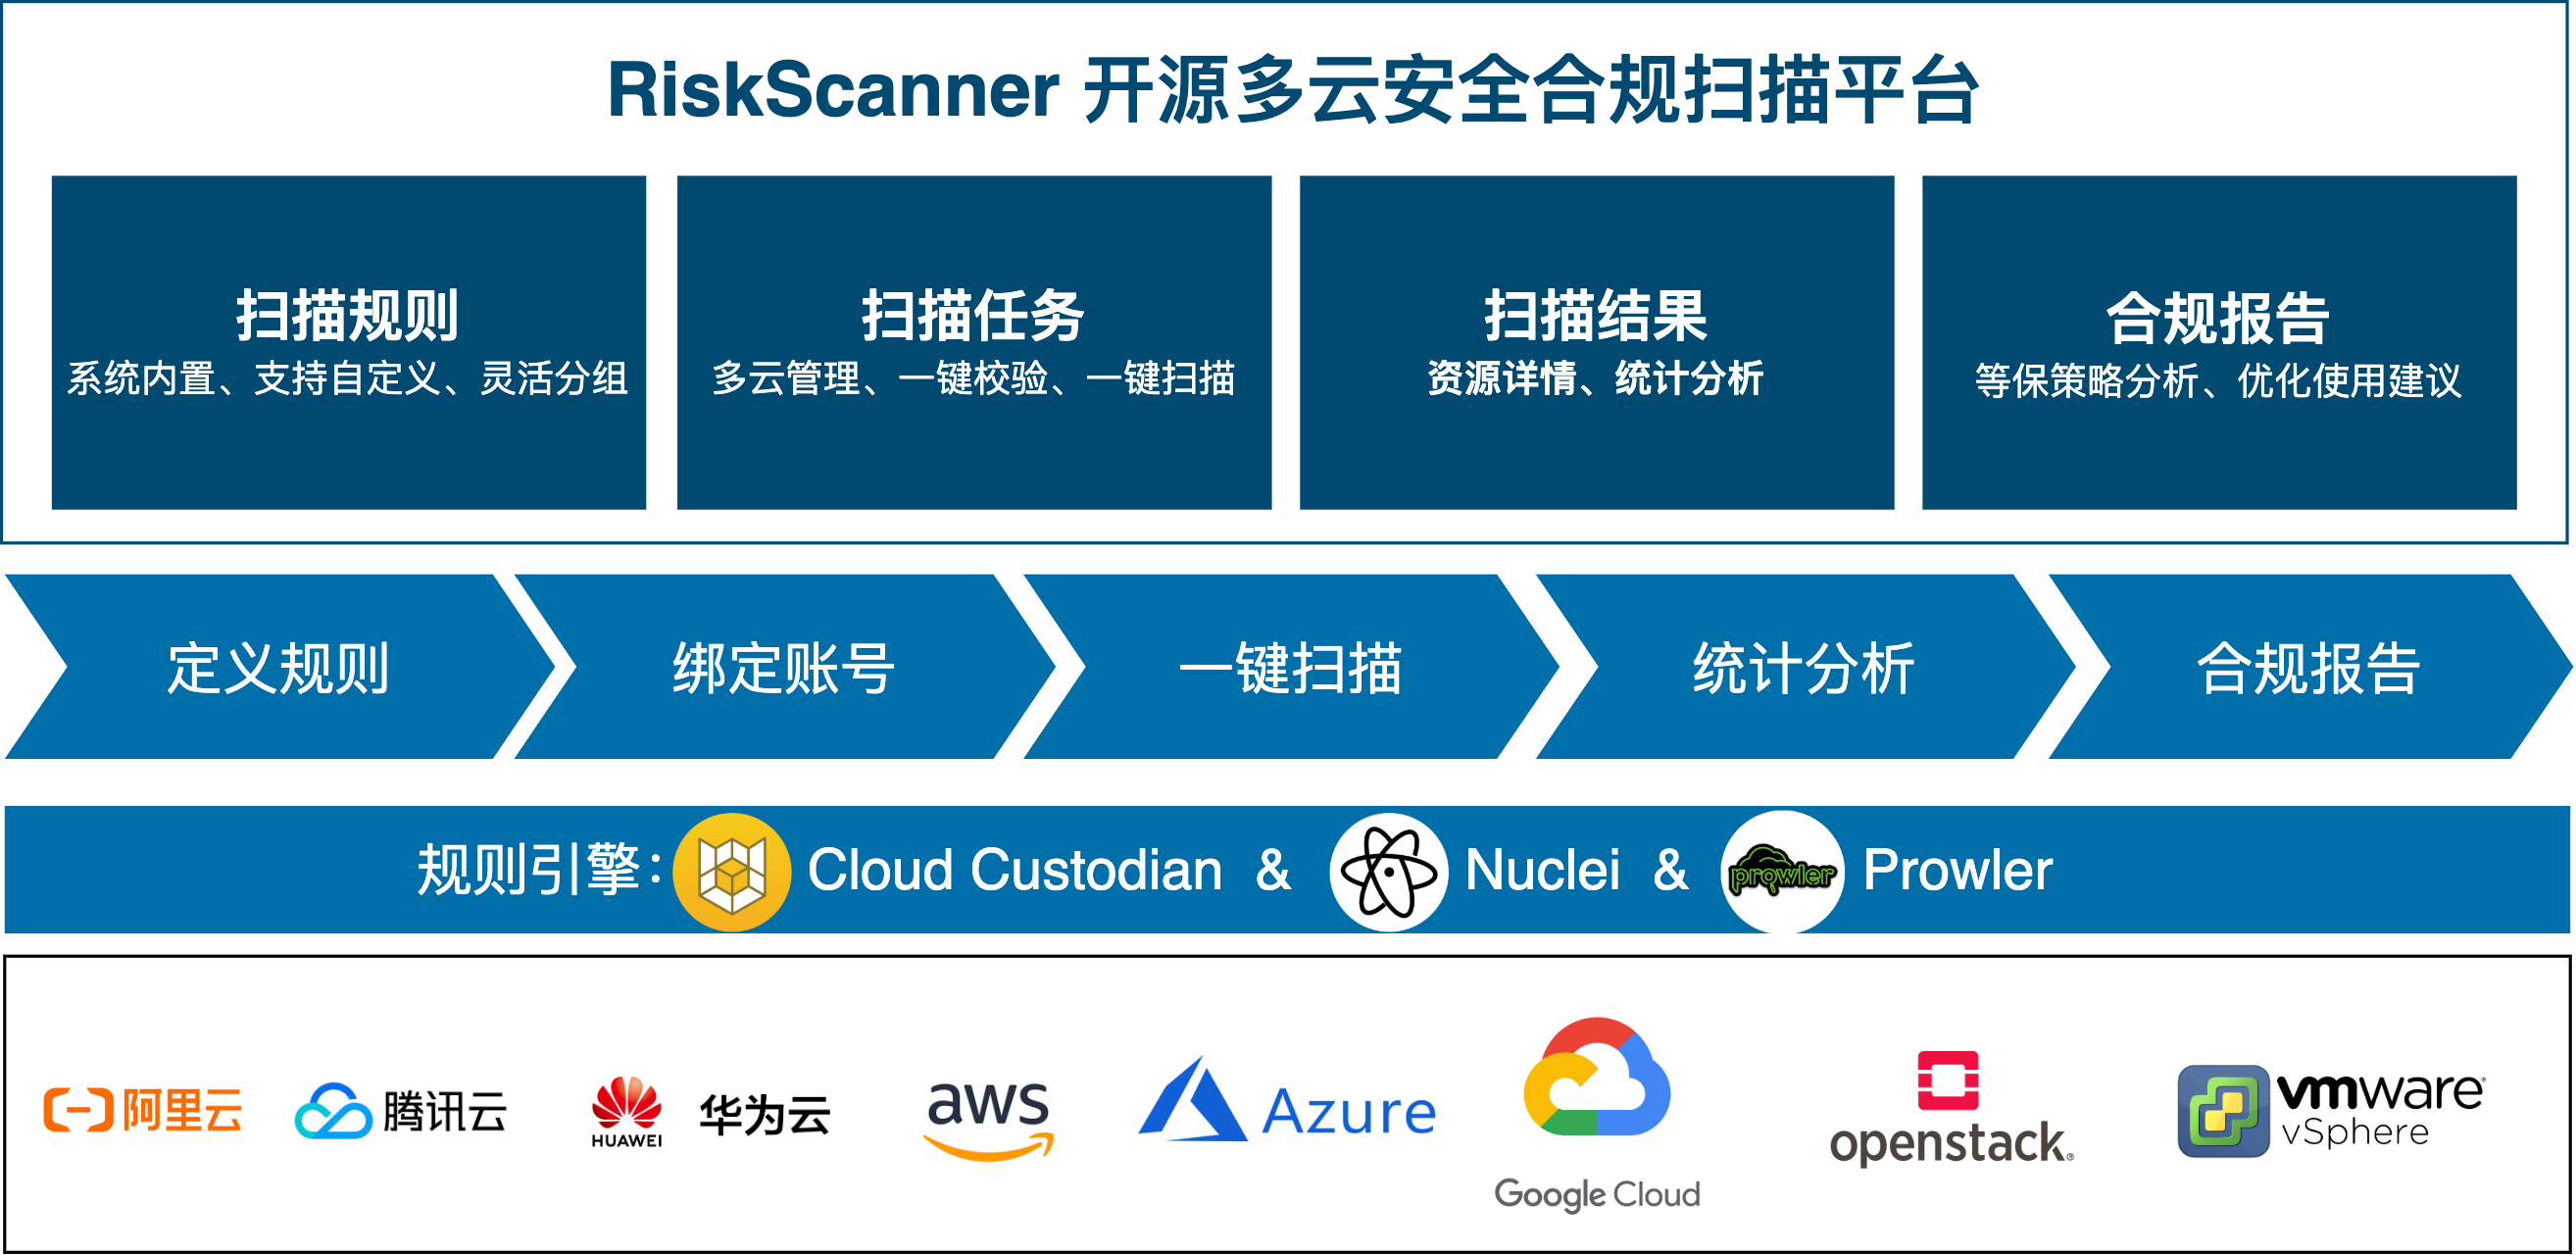 fit2cloud/riskscanner
RiskScanner 是开源的多云安全合规扫描平台,基于 Cloud Custodian 和 Nuclei 引擎,实现对主流公(私)有云资源的安全合规扫描和漏洞扫描。
 skyscanner/lambdaguard
AWS Serverless Security