
ingress-nightmare
 tuladhar/ingress-nightmare
IngressNightmare (CVE-2025-1974)
cloud-infrastructure-securitycloud-securityconfiguration-auditing+3
tuladhar/ingress-nightmareIngressNightmare (CVE-2025-1974)
 alebedev87/gatekeeper-cve-2020-8554
OPA Gatekeeper constraint policy that detects and prevents Kubernetes clusters from being vulnerable to CVE-2020-8554, enforcing secure configuration.
 ziadsaleemi/polkit_cve-2021-4034
Ansible role to patch RHSB-2022-001 Polkit Privilege Escalation - (CVE-2021-4034)
 daniel-odrinski/cve-2024-6387-mitigation-ansible-playbook
An Ansible Playbook to mitigate the risk of RCE (CVE-2024-6387) until platforms update OpenSSH to a non-vulnerable version.
 git-rep-src/cved
A tool to manage vulnerable docker containers
 shanika04/cloudfoundry_uaa
CVE-2016-4468
 atilacastro/update-apt-package
Playbook update APT package because CVE-2019-3462
 dev-sec/ansible-ssh-hardening
This Ansible role provides numerous security-related ssh configurations, providing all-round base protection.
 puppetlabs-toy-chest/puppetlabs-cve20113872
Puppet Module to help fix and migrate a Puppet deployment (CVE-2011-3872)
 joshlarsen/aws-recon
Multi-threaded AWS inventory collection tool with a focus on security-relevant resources and metadata.
 skyscanner/lambdaguard
AWS Serverless Security
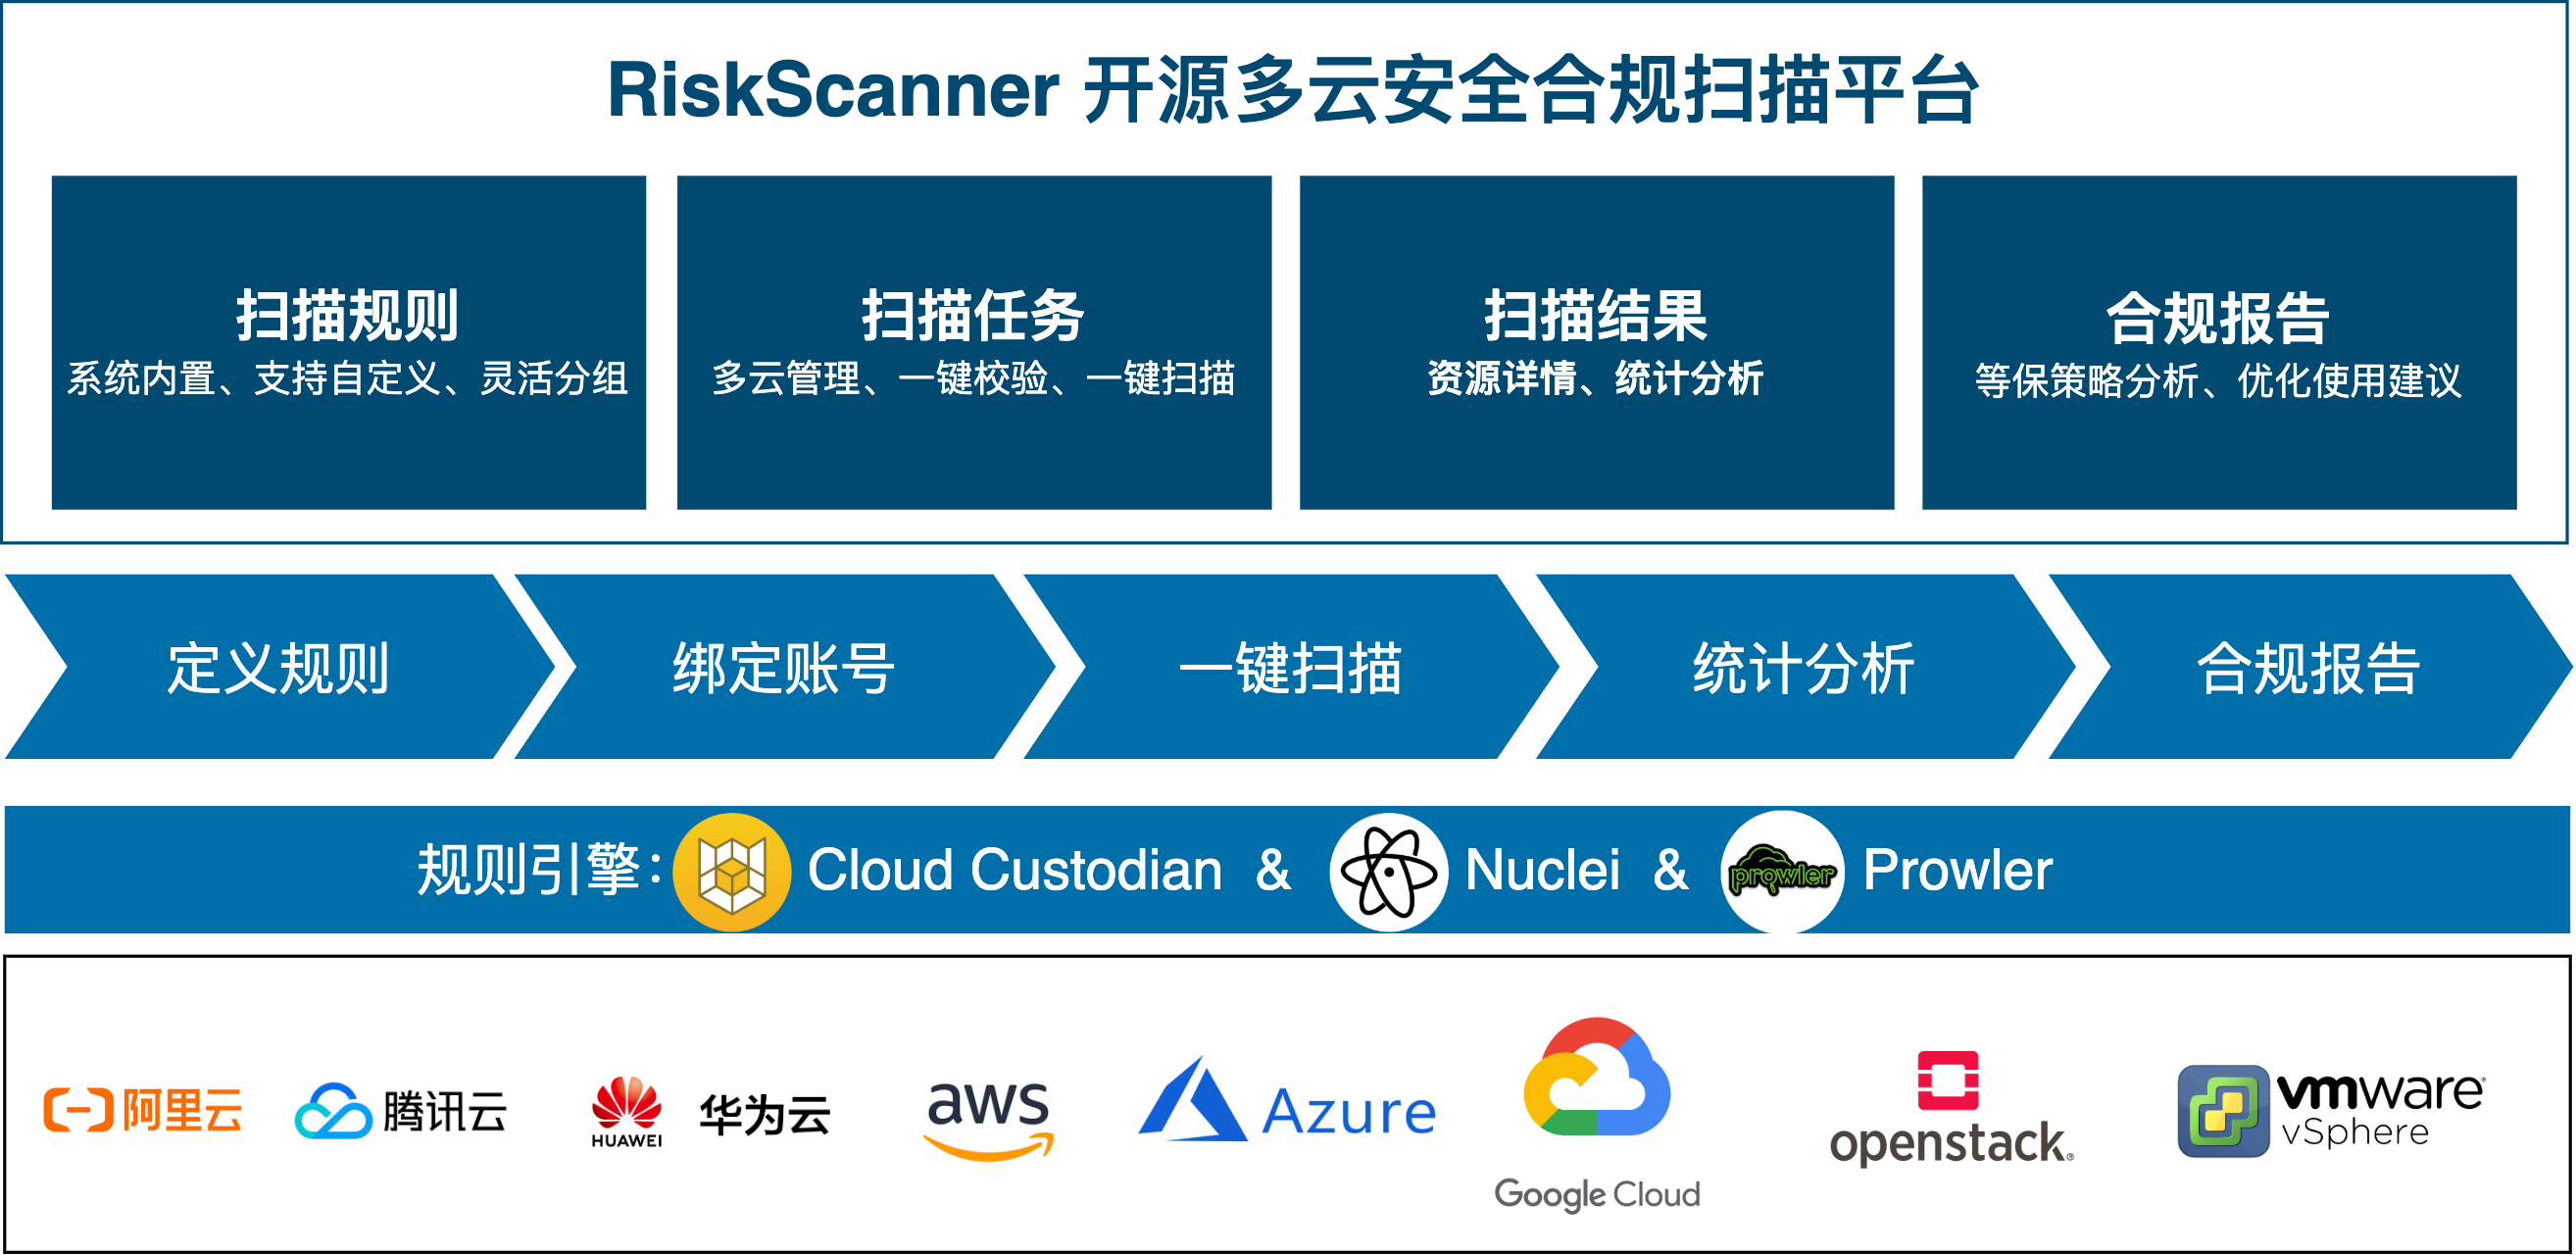 fit2cloud/riskscanner
RiskScanner 是开源的多云安全合规扫描平台,基于 Cloud Custodian 和 Nuclei 引擎,实现对主流公(私)有云资源的安全合规扫描和漏洞扫描。
 wavestone-cdt/abaddon
Red team operations management platform automating infrastructure deployment, C2 setup, phishing campaigns, and reconnaissance with integrated tool…
 octarinesec/kube-scan
kube-scan: Octarine k8s cluster risk assessment tool
 azuread/azure-ad-incident-response-powershell-module
The Azure Active Directory Incident Response PowerShell module provides a number of tools, developed by the Azure Active Directory Product Group in…
 salesforce/metabadger
Prevent SSRF attacks on AWS EC2 via automated upgrades to the more secure Instance Metadata Service v2 (IMDSv2).