
vcsa-hardening-tool
 mandiant/vcsa-hardening-tool
Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)
authenticationcloud-infrastructure-securityconfiguration-auditing+9
14
mandiant/vcsa-hardening-toolAutomated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)
 leitwacht/leitwacht
Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration
 fer1035_terraform/modules/terraform-aws-security-group
Terraform module to manage AWS Security Groups. Currently, the ingress and egress rules support IPv4, IPv6, and Security Group ID inputs.
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 firecracker-microvm/firecracker
Secure and fast microVMs for serverless computing.
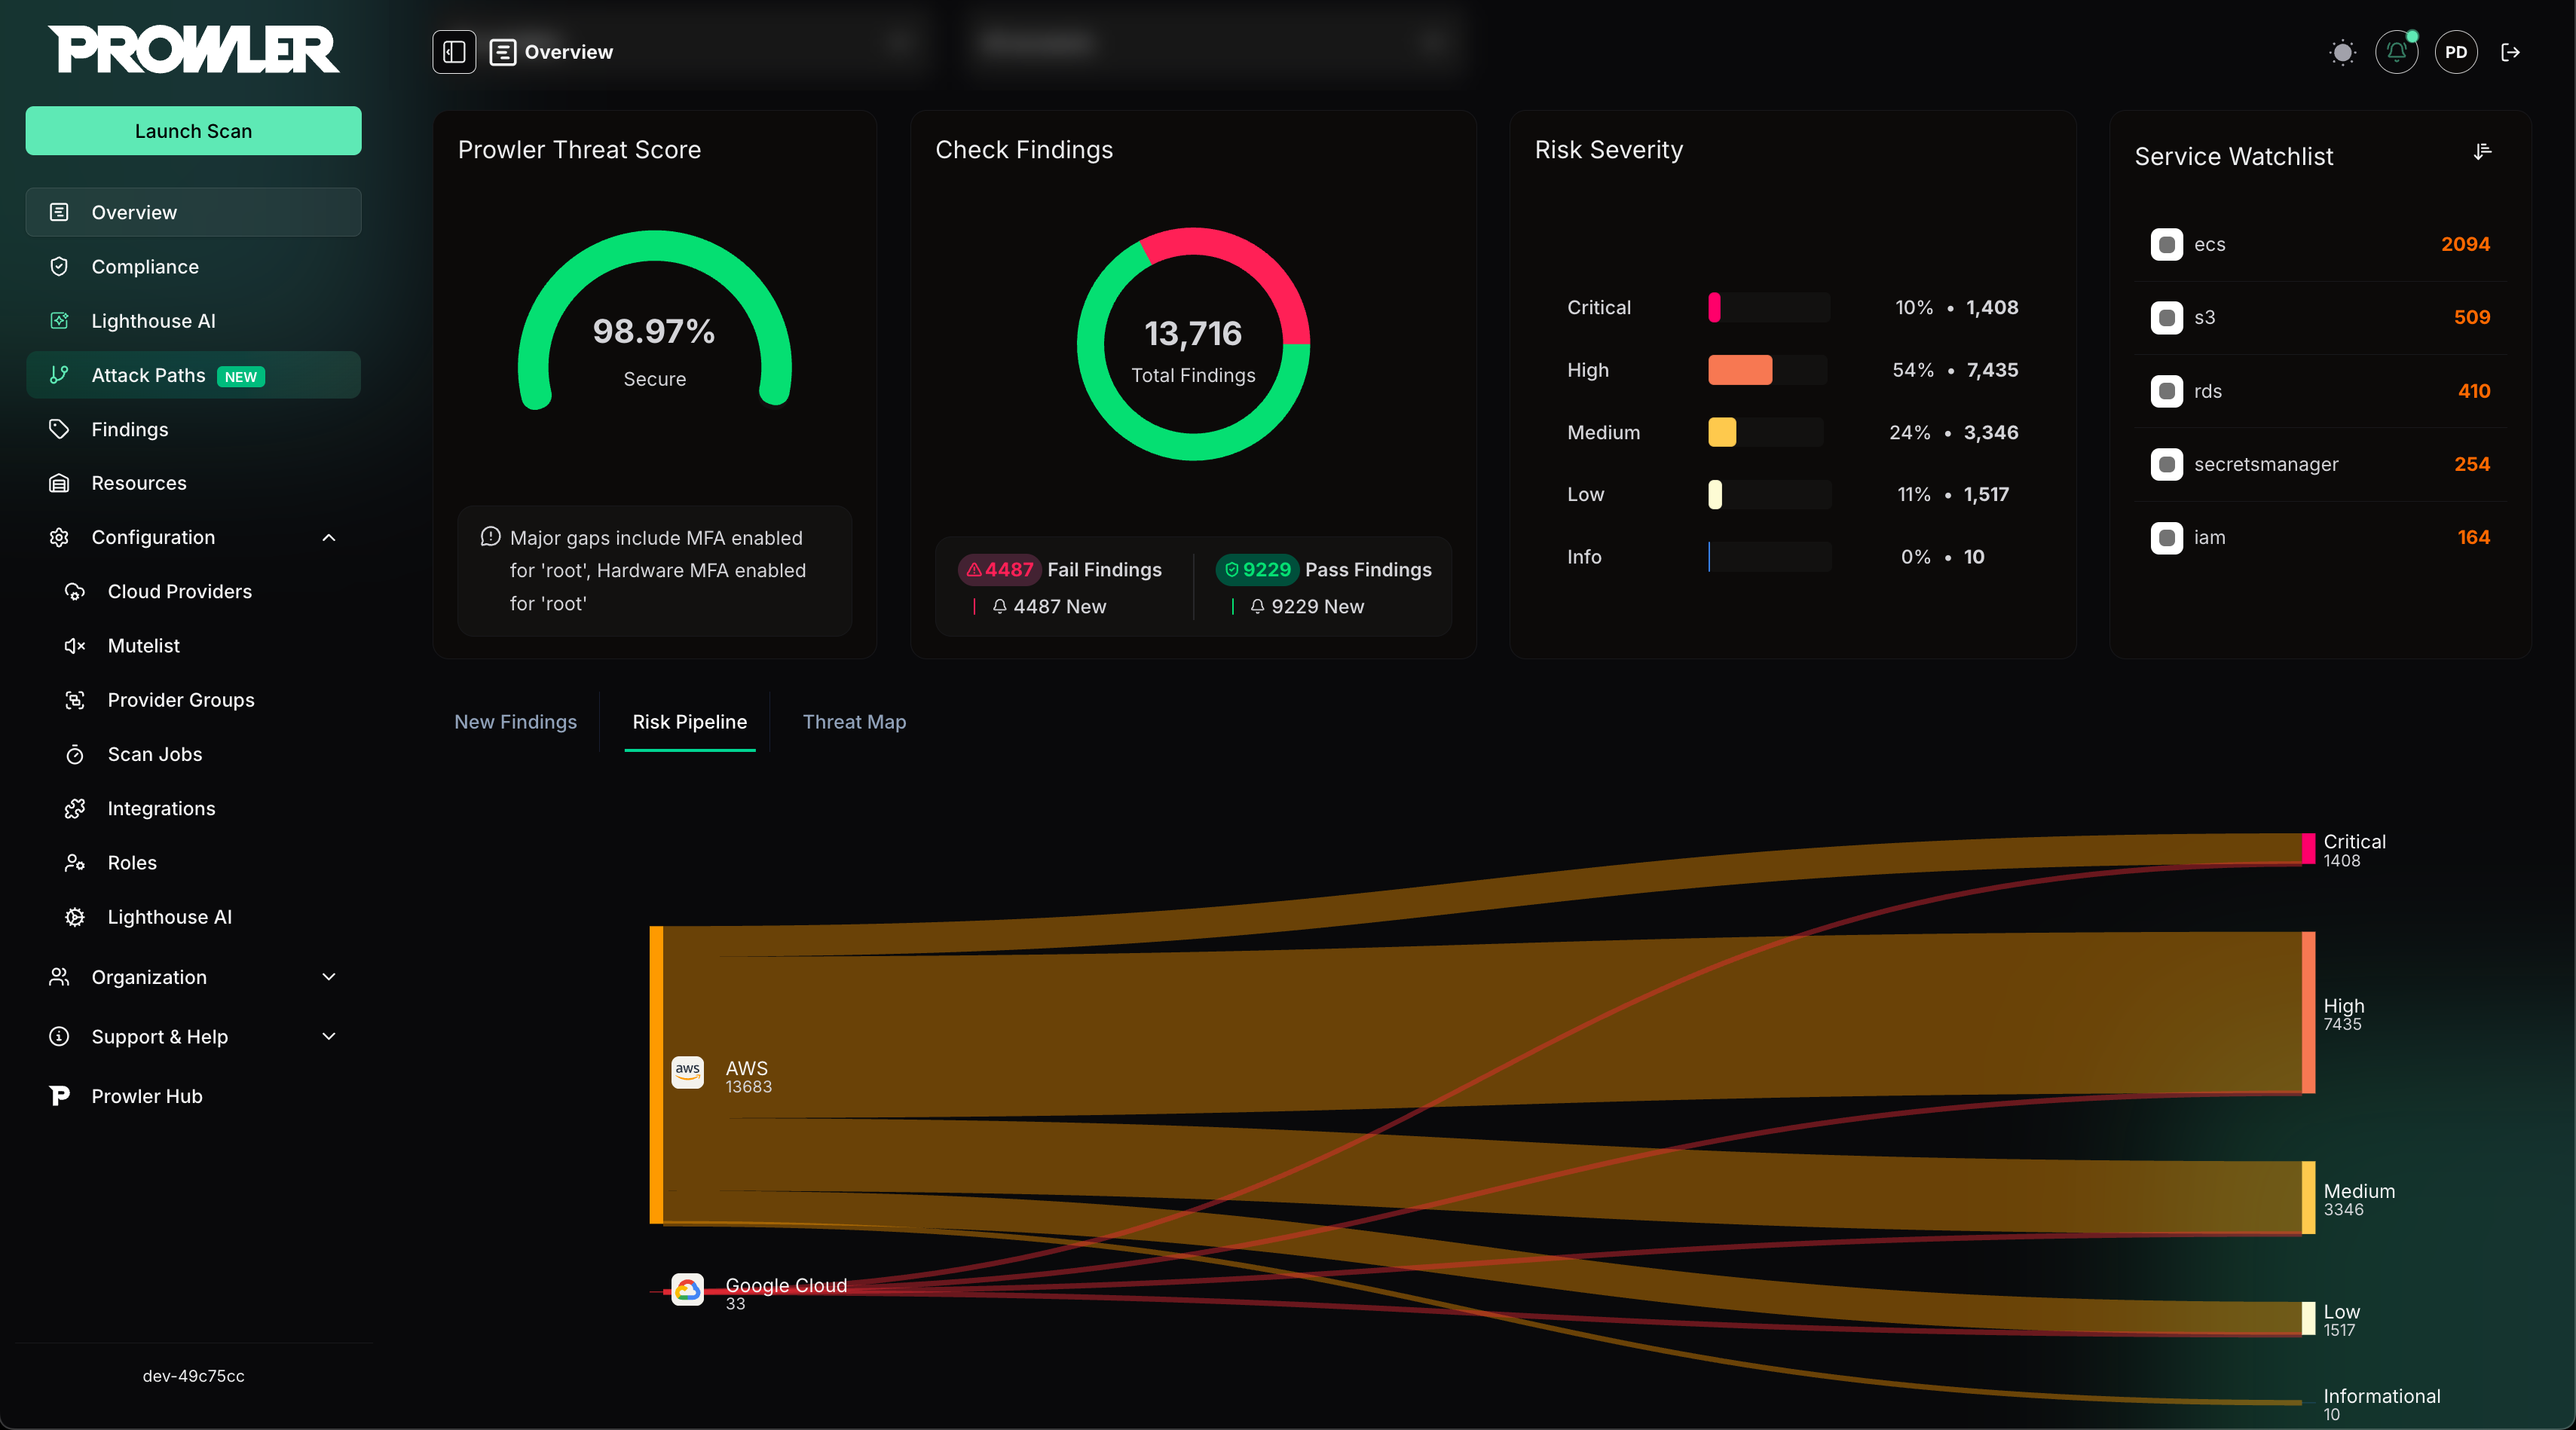 prowler-cloud/prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…
 dexidp/dex
OpenID Connect (OIDC) identity and OAuth 2.0 provider with pluggable connectors
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 chaos-mesh/chaos-mesh
A Chaos Engineering Platform for Kubernetes.
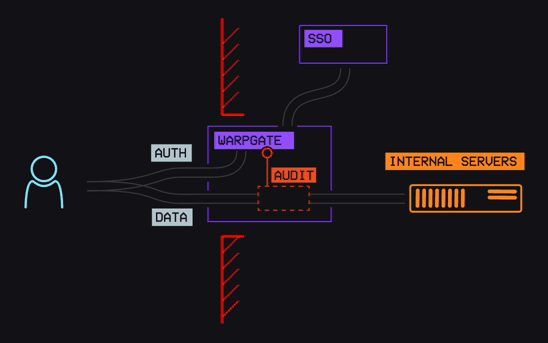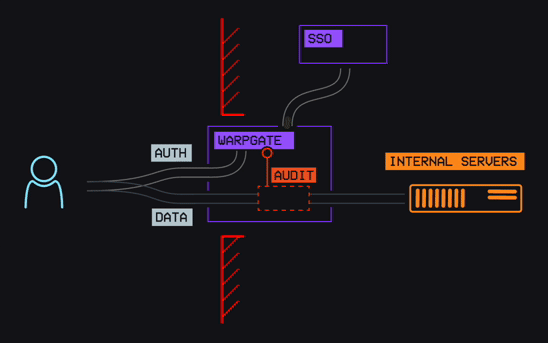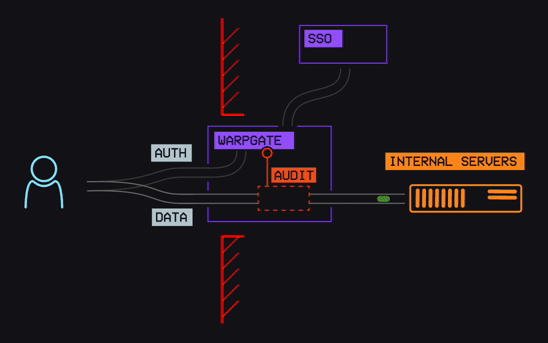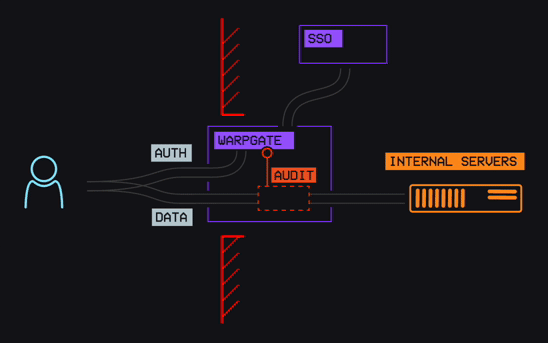 warp-tech/warpgate
Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software
 hashicorp/boundary
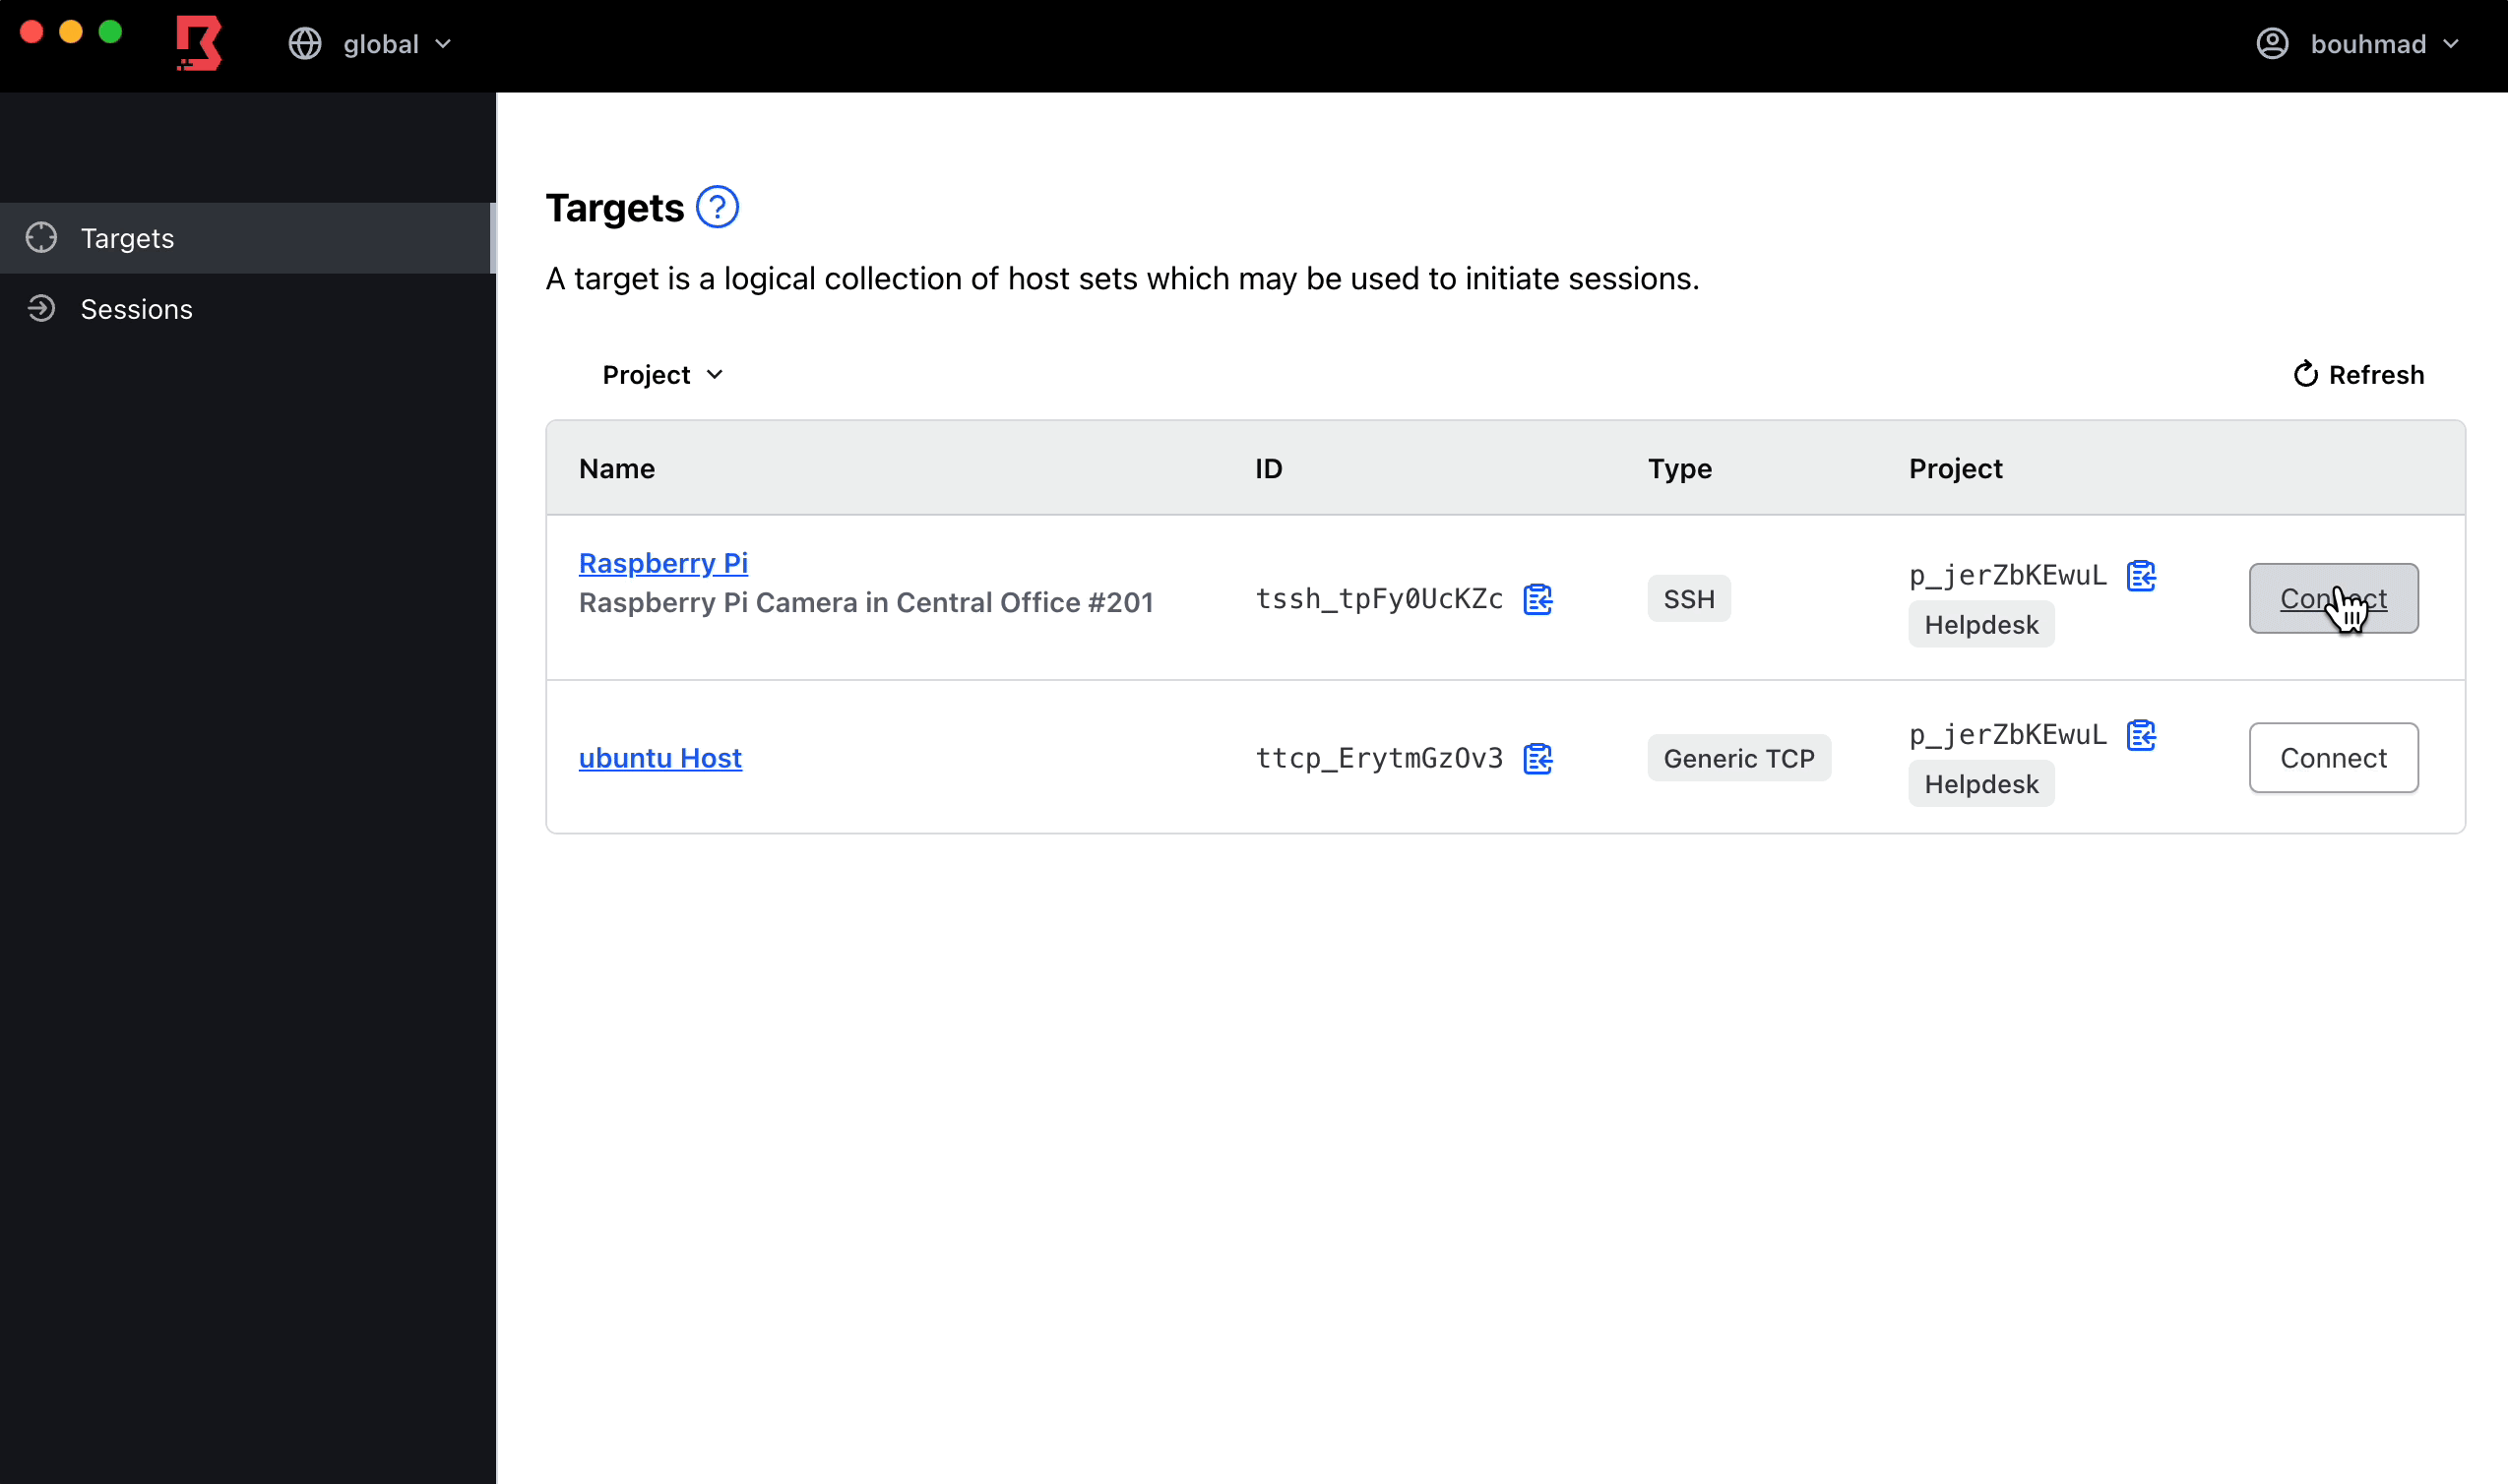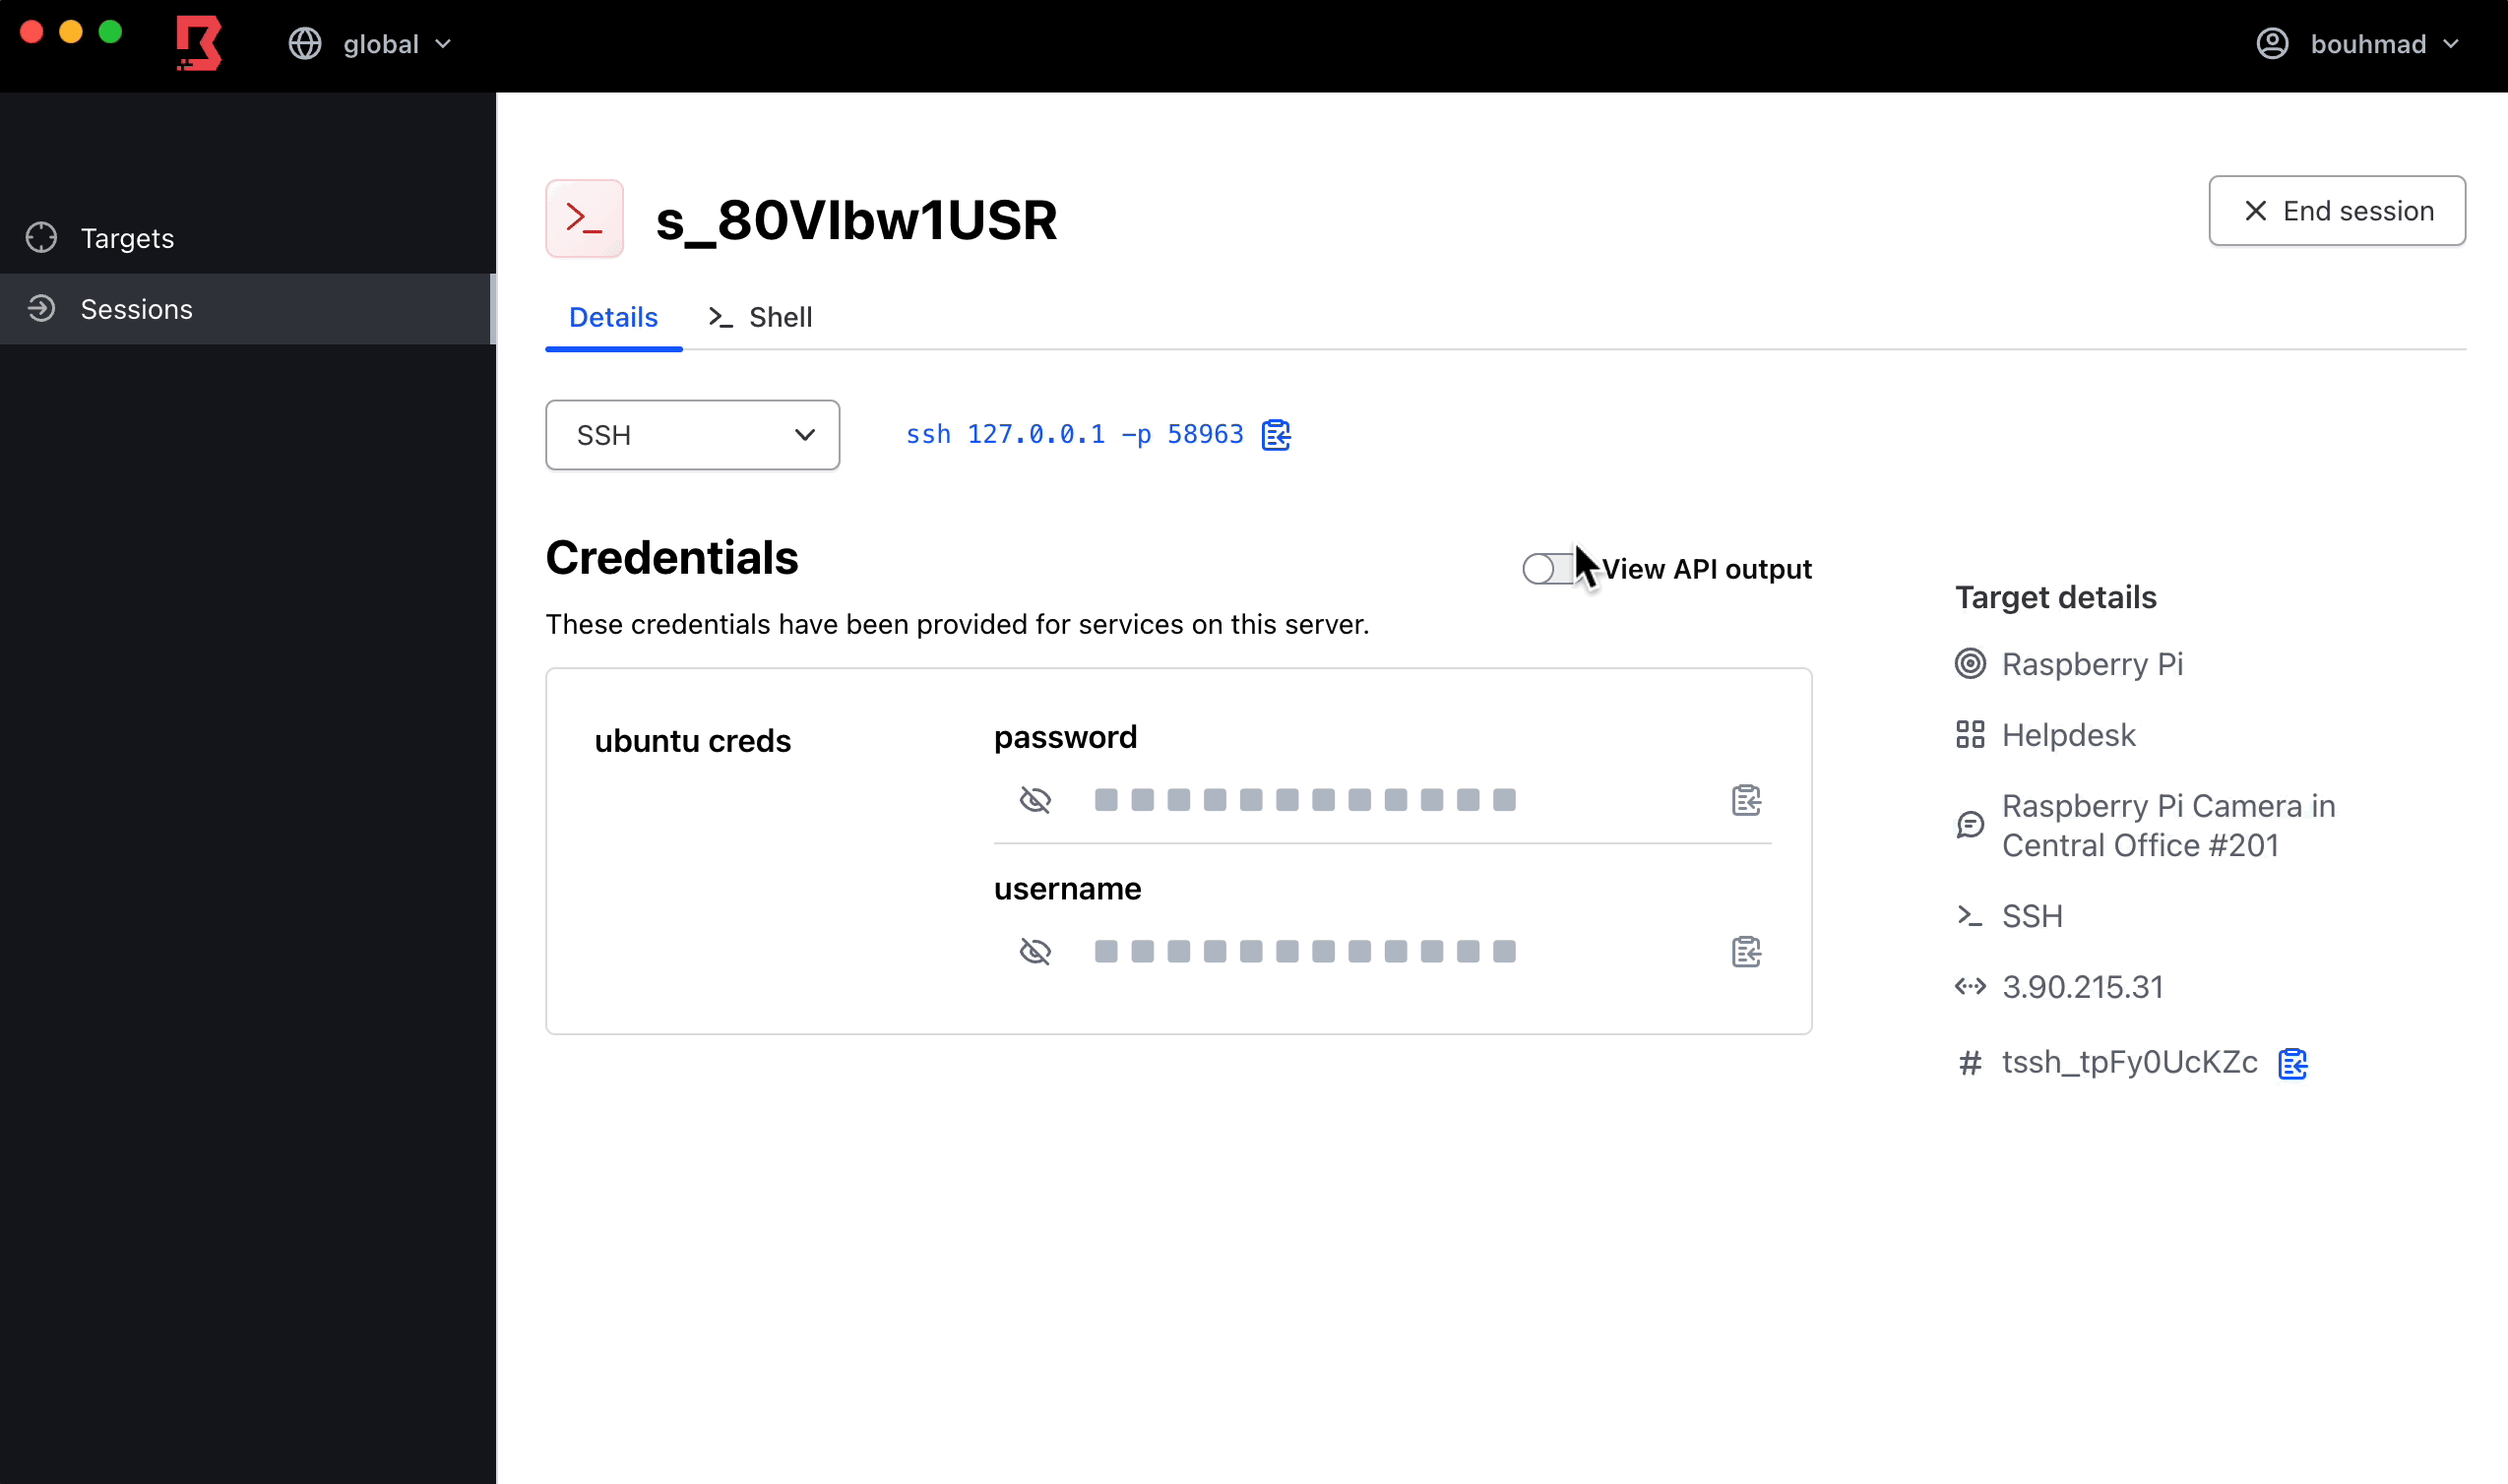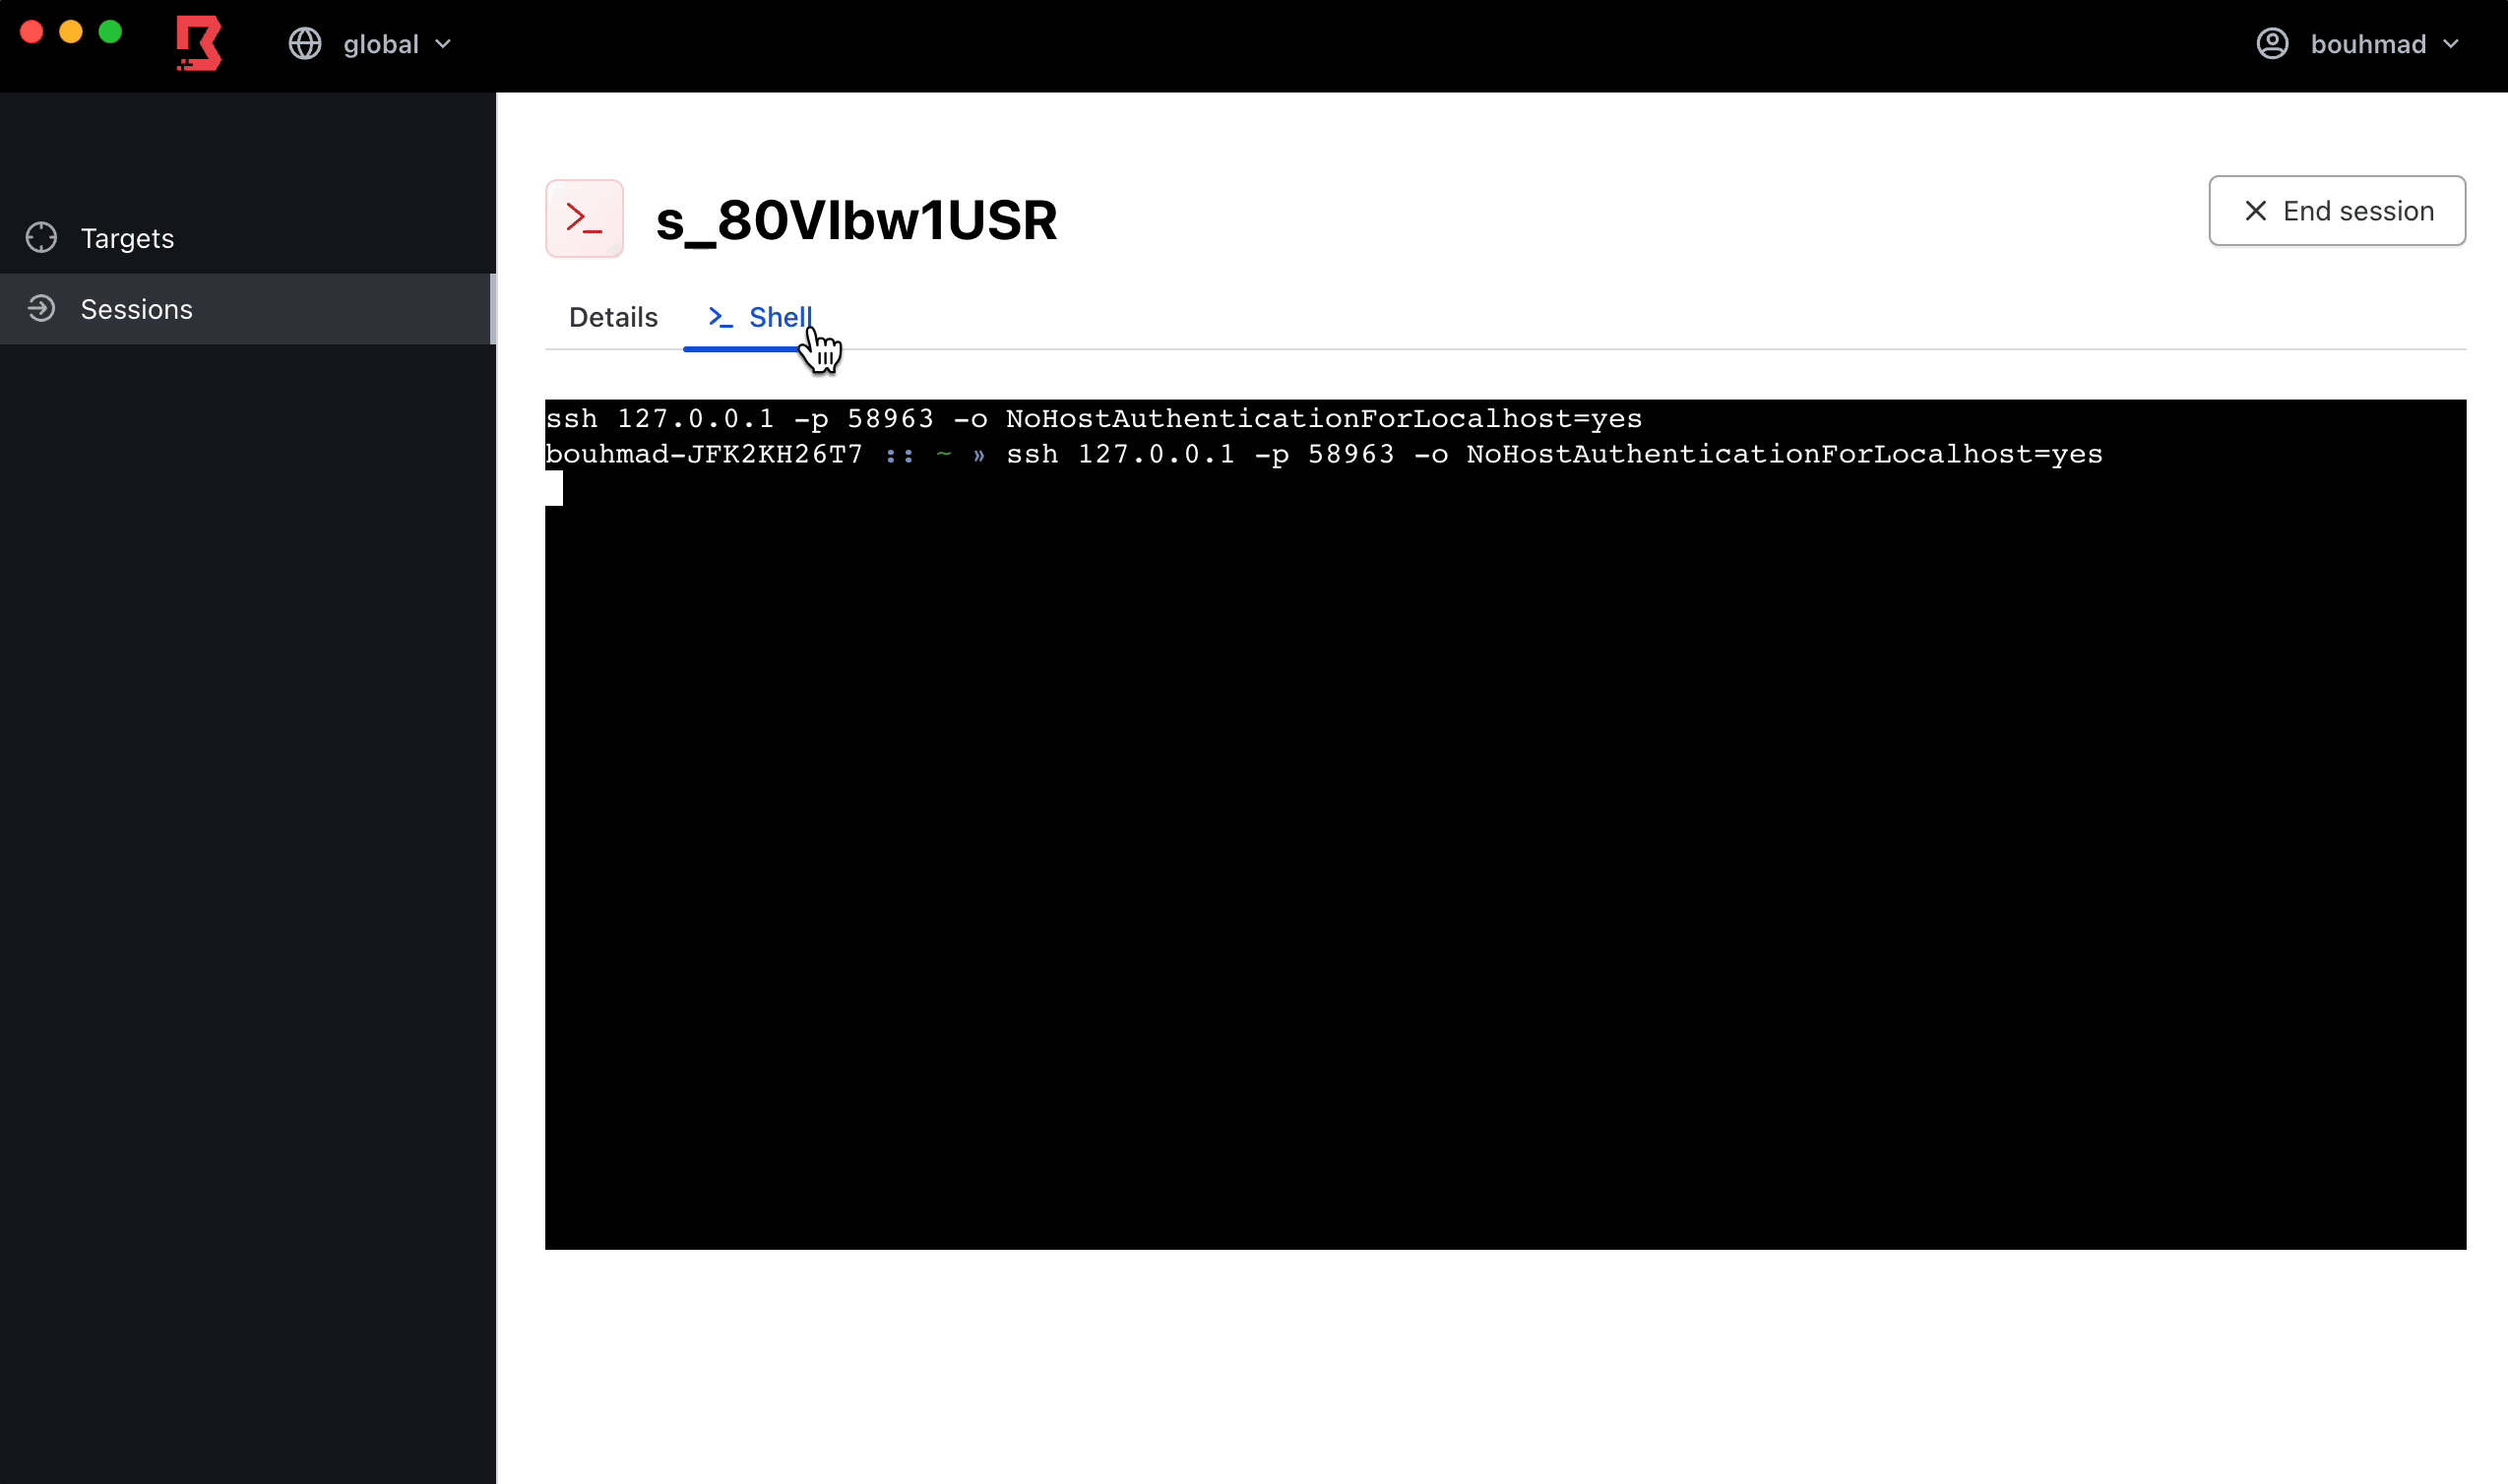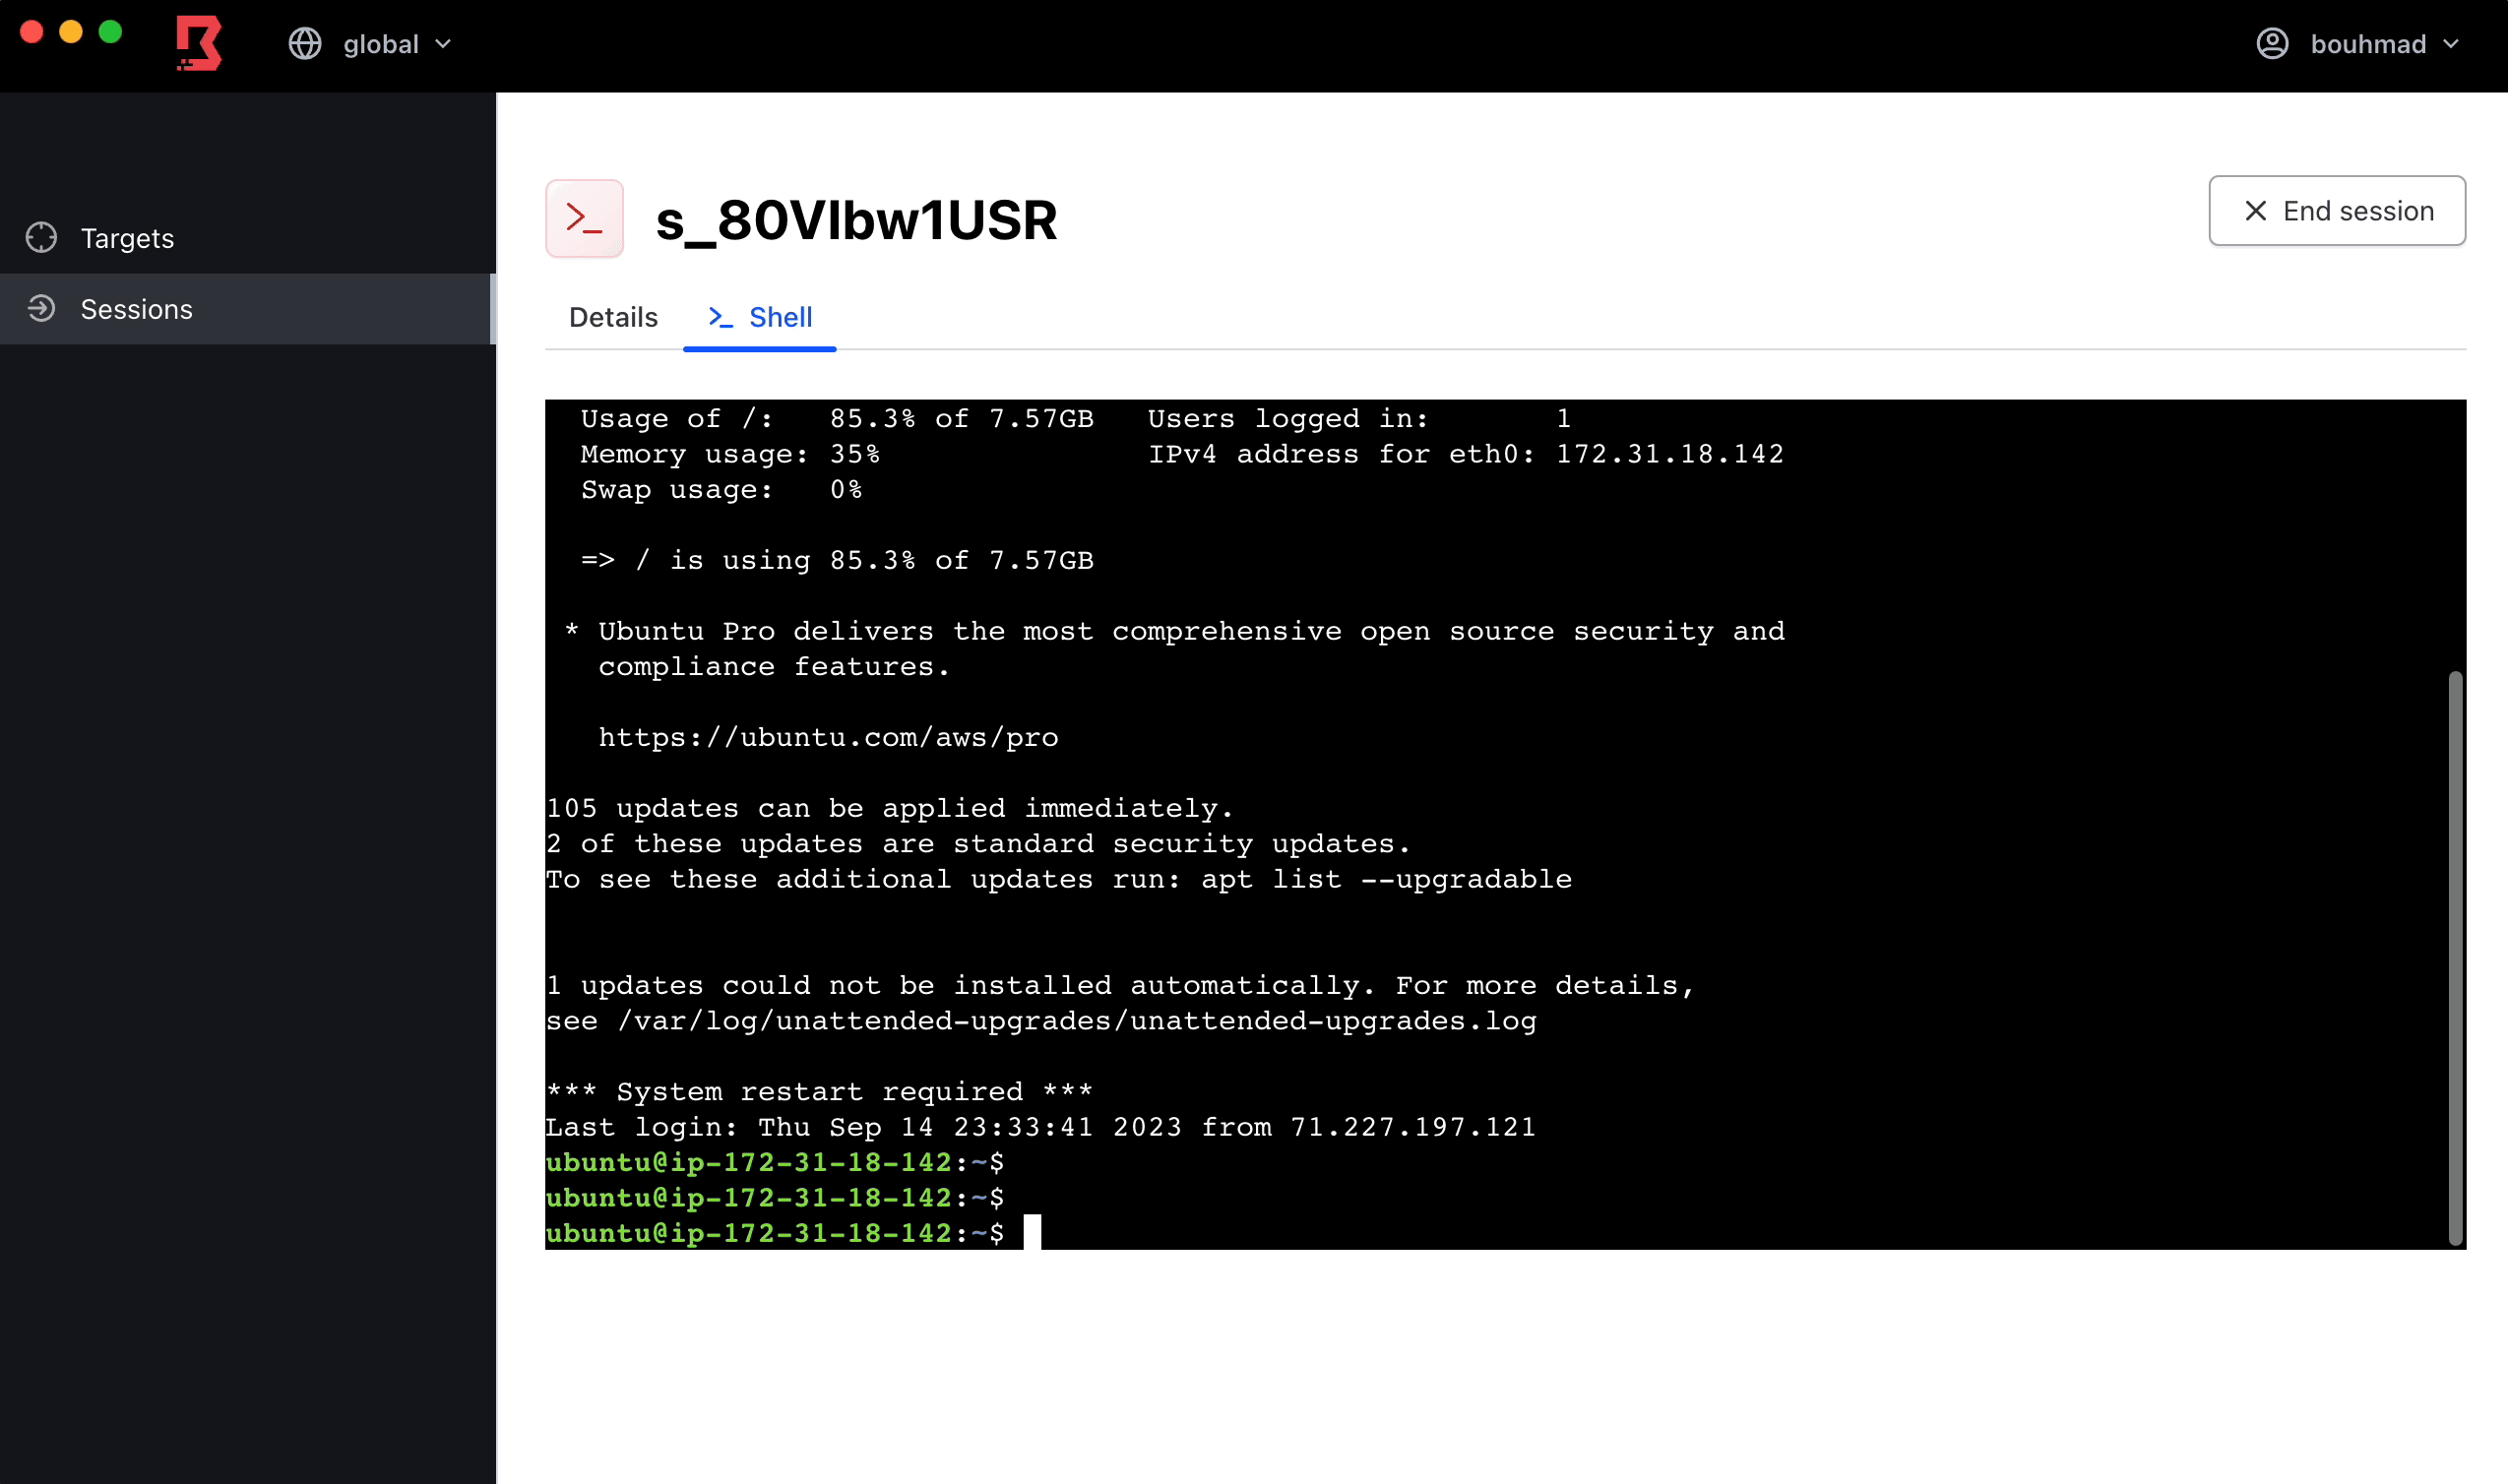
Boundary enables identity-based access management for dynamic infrastructure.
 bluscreenofjeff/red-team-infrastructure-wiki
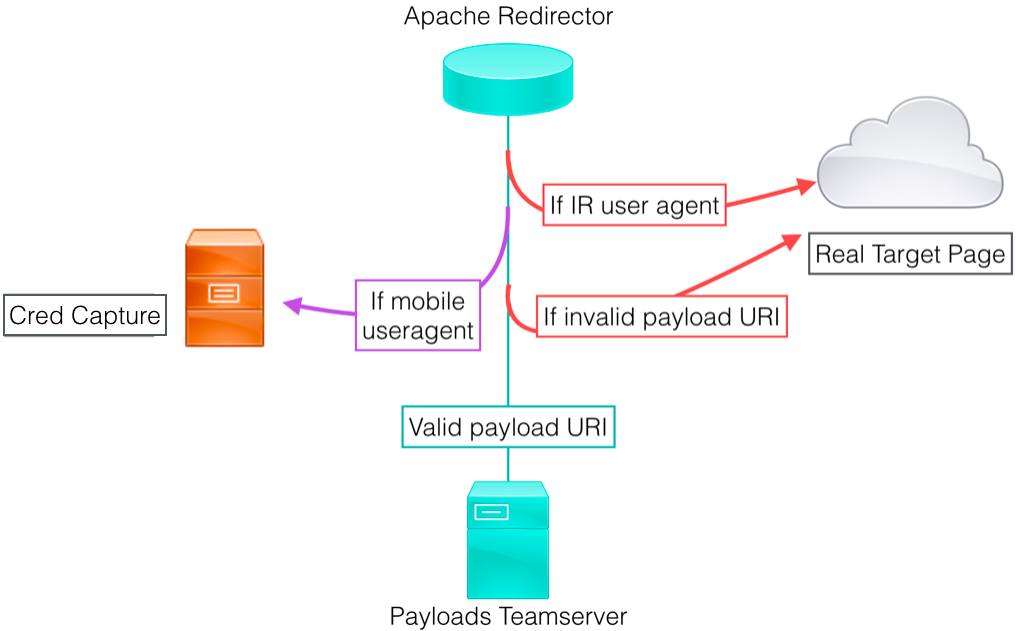
Wiki to collect Red Team infrastructure hardening resources
 dirkjanm/roadtools
A collection of Azure AD/Entra tools for offensive and defensive security purposes
 spiffe/spire
Workload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters