
copy.fail-mitigation-MLM
 jbiniek/copy.fail-mitigation-mlm
Salt state to deploy a mitigation of the copy.fail vulnerability (CVE-2026-31431)
cloud-infrastructure-securityconfiguration-auditingdevsecops+1
jbiniek/copy.fail-mitigation-mlmSalt state to deploy a mitigation of the copy.fail vulnerability (CVE-2026-31431)
 mrmtwoj/ubuntu-cve-2026-31431-mitigation
دستورالعملهای کاهش ریسک و بهروزرسانی برای CVE-2026-31431 در سیستمهای اوبونتو، شامل مراحل ارتقاء کرنل و kmod.
 first-john/cve_2026_frag_family_fix
CVE-2026-46300 / CVE-2026-43500 / CVE-2026-31431 / CVE-2026-43284 golang hotfix
 deadrabbit92/mitigate-copy-fail.yml
Mitigates CVE-2026-31431 (Copy Fail) by unloading and blacklisting algif_aead kernel module if it is loadable and has no active references.
 jdmulloy/meltdown-aws-scanner
Naive shell script to verify Meltdown (CVE-2017-5754) patch status of EC2 instances
 radzarr/wsusresponder
Module PowerShell de réponse à l'incident CVE-2025-59287 — WSUS Remote Code Execution (RCE)
 mrk336/cve-2024-10220-kubernetes-gitrepo-volume-vulnerability
CVE-2024-10220 reveals a critical flaw in Kubernetes’ deprecated gitRepo volume type, allowing attackers to execute arbitrary commands via malicious…
 arnaudluti/ps-cve-2021-44228
Static detection of vulnerable log4j librairies on Windows servers, members of an AD domain.
 randomrobbiebf/bucket-brute
Aws S3 Tko Tool
 ifulxploit/minio-security-vulnerability-checker
Program ini adalah alat (tool) yang dibuat untuk memeriksa keamanan sistem Minio terkait dengan kerentanan CVE-2022-35919
 jblaine/cookbook-bash-cve-2014-6271
Chef cookbook that will fail if bash vulnerability found per CVE-2014-6271
 tuladhar/ingress-nightmare
IngressNightmare (CVE-2025-1974)
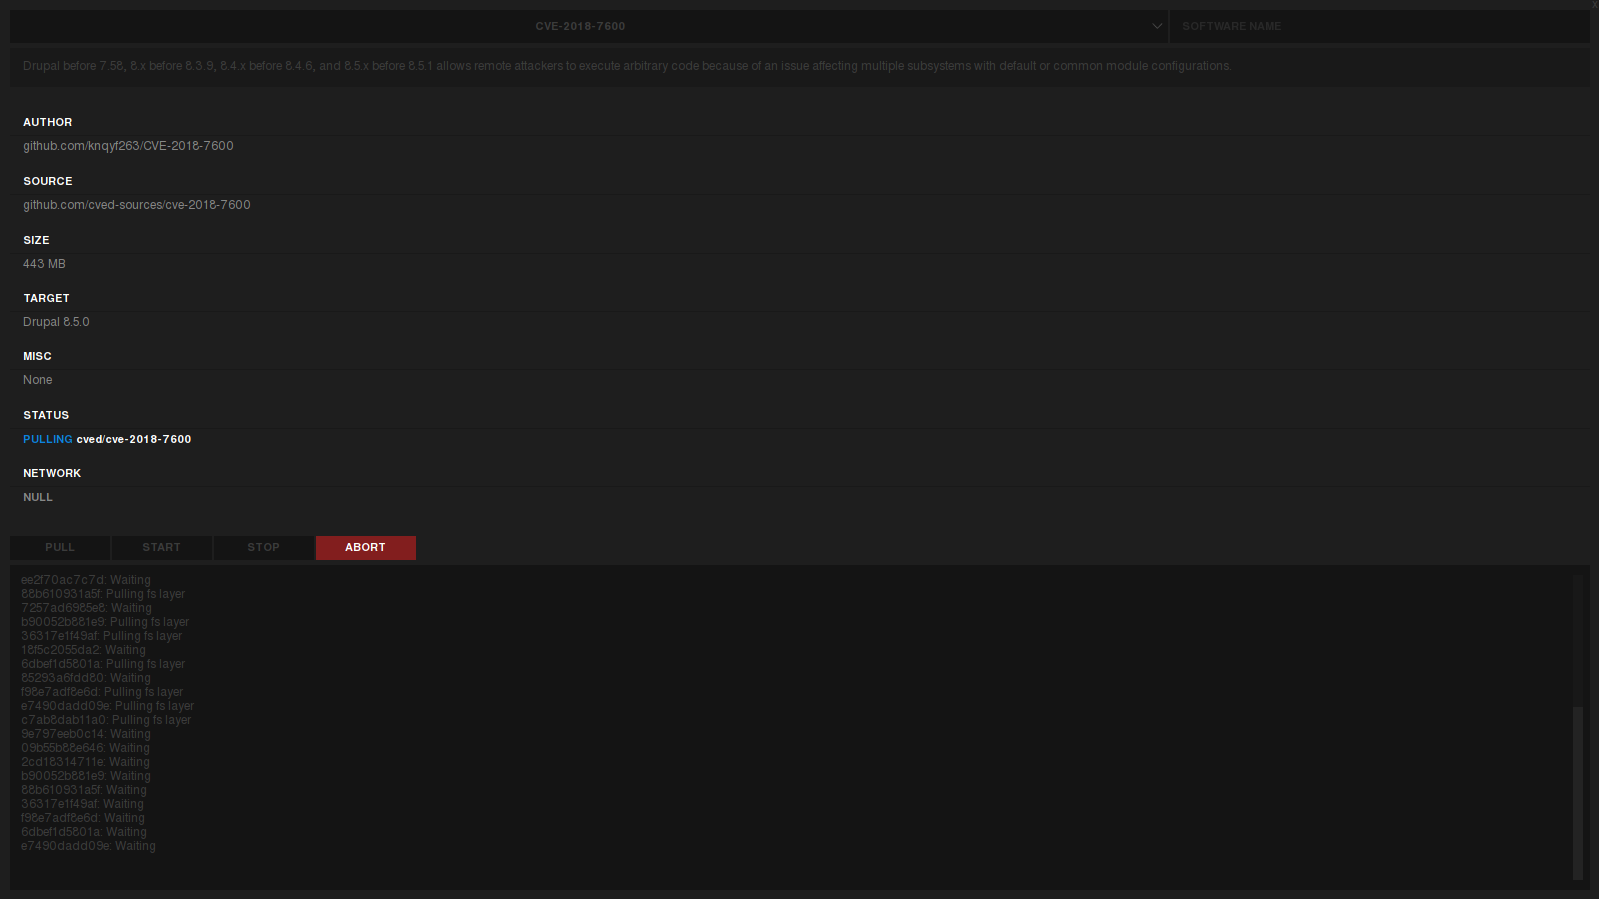 git-rep-src/cved
A tool to manage vulnerable docker containers
 daniel-odrinski/cve-2024-6387-mitigation-ansible-playbook
An Ansible Playbook to mitigate the risk of RCE (CVE-2024-6387) until platforms update OpenSSH to a non-vulnerable version.
 alebedev87/gatekeeper-cve-2020-8554
OPA Gatekeeper constraint policy that detects and prevents Kubernetes clusters from being vulnerable to CVE-2020-8554, enforcing secure configuration.
 ziadsaleemi/polkit_cve-2021-4034
Ansible role to patch RHSB-2022-001 Polkit Privilege Escalation - (CVE-2021-4034)
 atilacastro/update-apt-package
Playbook update APT package because CVE-2019-3462
 dev-sec/ansible-ssh-hardening
This Ansible role provides numerous security-related ssh configurations, providing all-round base protection.