

ingress-nightmare
 tuladhar/ingress-nightmare
IngressNightmare (CVE-2025-1974)
cloud-infrastructure-securitycloud-securityconfiguration-auditing+3
tuladhar/ingress-nightmareIngressNightmare (CVE-2025-1974)
 alebedev87/gatekeeper-cve-2020-8554
OPA Gatekeeper constraint policy that detects and prevents Kubernetes clusters from being vulnerable to CVE-2020-8554, enforcing secure configuration.
 simplifi-ed/cve-2024-3094-patcher
Ansible playbook for patching CVE-2024-3094
 daniel-odrinski/cve-2024-6387-mitigation-ansible-playbook
An Ansible Playbook to mitigate the risk of RCE (CVE-2024-6387) until platforms update OpenSSH to a non-vulnerable version.
 git-rep-src/cved
A tool to manage vulnerable docker containers
 malindarathnayake/intel-cve-2018-3639-mitigation_registryupdate
PowerShell script to apply Windows registry mitigation for CVE-2018-3639 (Speculative Store Bypass), enabling automated security hardening against…
 shoucheng3/kubernetes-client__java_cve-2020-8570_client-java-parent-9_0_2_fixed
Java client library for the Kubernetes API, enabling programmatic management of clusters, pods, deployments, and other resources with support for…
 atilacastro/update-apt-package
Playbook update APT package because CVE-2019-3462
 dev-sec/ansible-ssh-hardening
This Ansible role provides numerous security-related ssh configurations, providing all-round base protection.
 netwrix/pingcastlecloud
Audit program for AzureAD
 puppetlabs-toy-chest/puppetlabs-cve20113872
Puppet Module to help fix and migrate a Puppet deployment (CVE-2011-3872)
 shopify/kubeaudit
kubeaudit helps you audit your Kubernetes clusters against common security controls
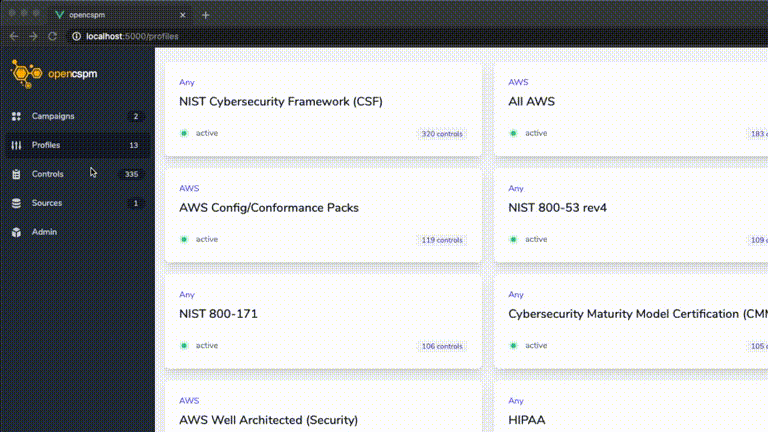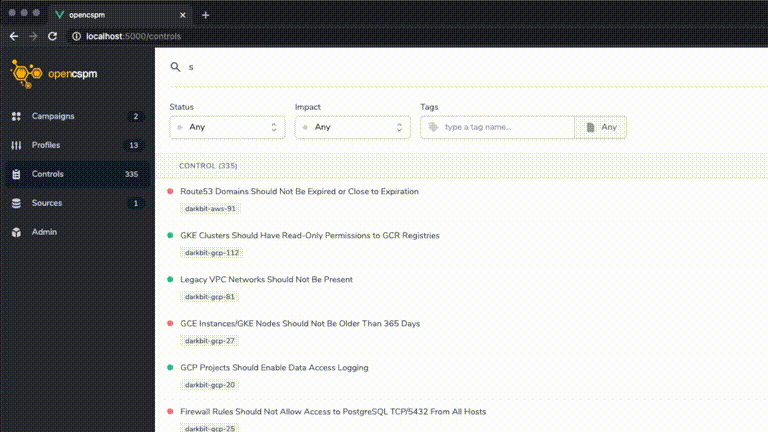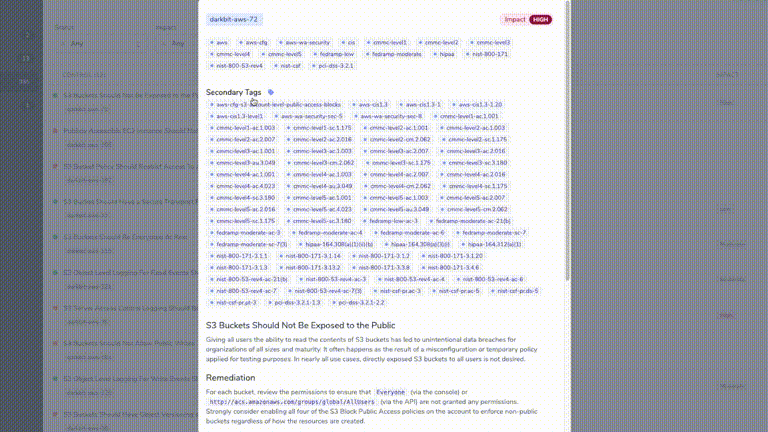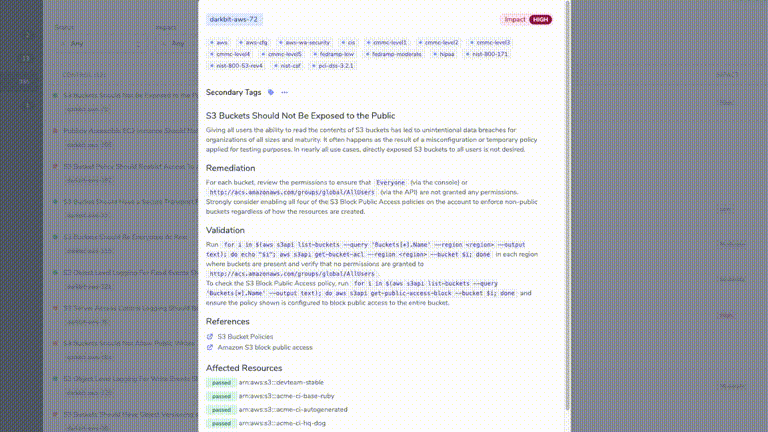 opencspm/opencspm
Open Cloud Security Posture Management Engine
 npm/ansible-bashpocalypse
Patch for CVE-2014-6271
 kubernetes/ingress-nginx
Ingress NGINX Controller for Kubernetes
 nccgroup/scout2
Security auditing tool for AWS environments
 rossengeorgiev/salt-security-backports
Salt security backports for CVE-2020-11651 & CVE-2020-11652
 skyscanner/lambdaguard
AWS Serverless Security