
nixos-config
 xddxdd/nixos-config
Lan Tian's NixOS Configuration
cloud-infrastructure-securityconfiguration-auditingcryptography+6
1307h 53m ago
xddxdd/nixos-configLan Tian's NixOS Configuration
 mondoohq/cnspec
An open source, cloud-native security to protect everything from build to runtime
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 cloudquery/cloudquery
Data pipelines for cloud config and security data. Build cloud asset inventory, CSPM, FinOps, and vulnerability management solutions. Extract from…
 tencentcloud/cubesandbox
Instant, Concurrent, Secure & Lightweight Sandbox for AI Agents.
 spiffe/spire
Workload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
 cachethq/cachet
🚦 Cachet, the open source, self-hosted status page system.
 stackrox/stackrox
The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…
 hacktricks-wiki/hacktricks-cloud
Community-driven knowledge base for pentesting cloud environments and CI/CD pipelines: attack techniques, enumeration, privilege escalation, and…
 microsoft/mxc
Policy-driven, layered isolation and containment
 aws/serverless-application-model
Transforms SAM templates into CloudFormation resources, generating Lambda functions, IAM roles, and policies with built-in serverless best practices.
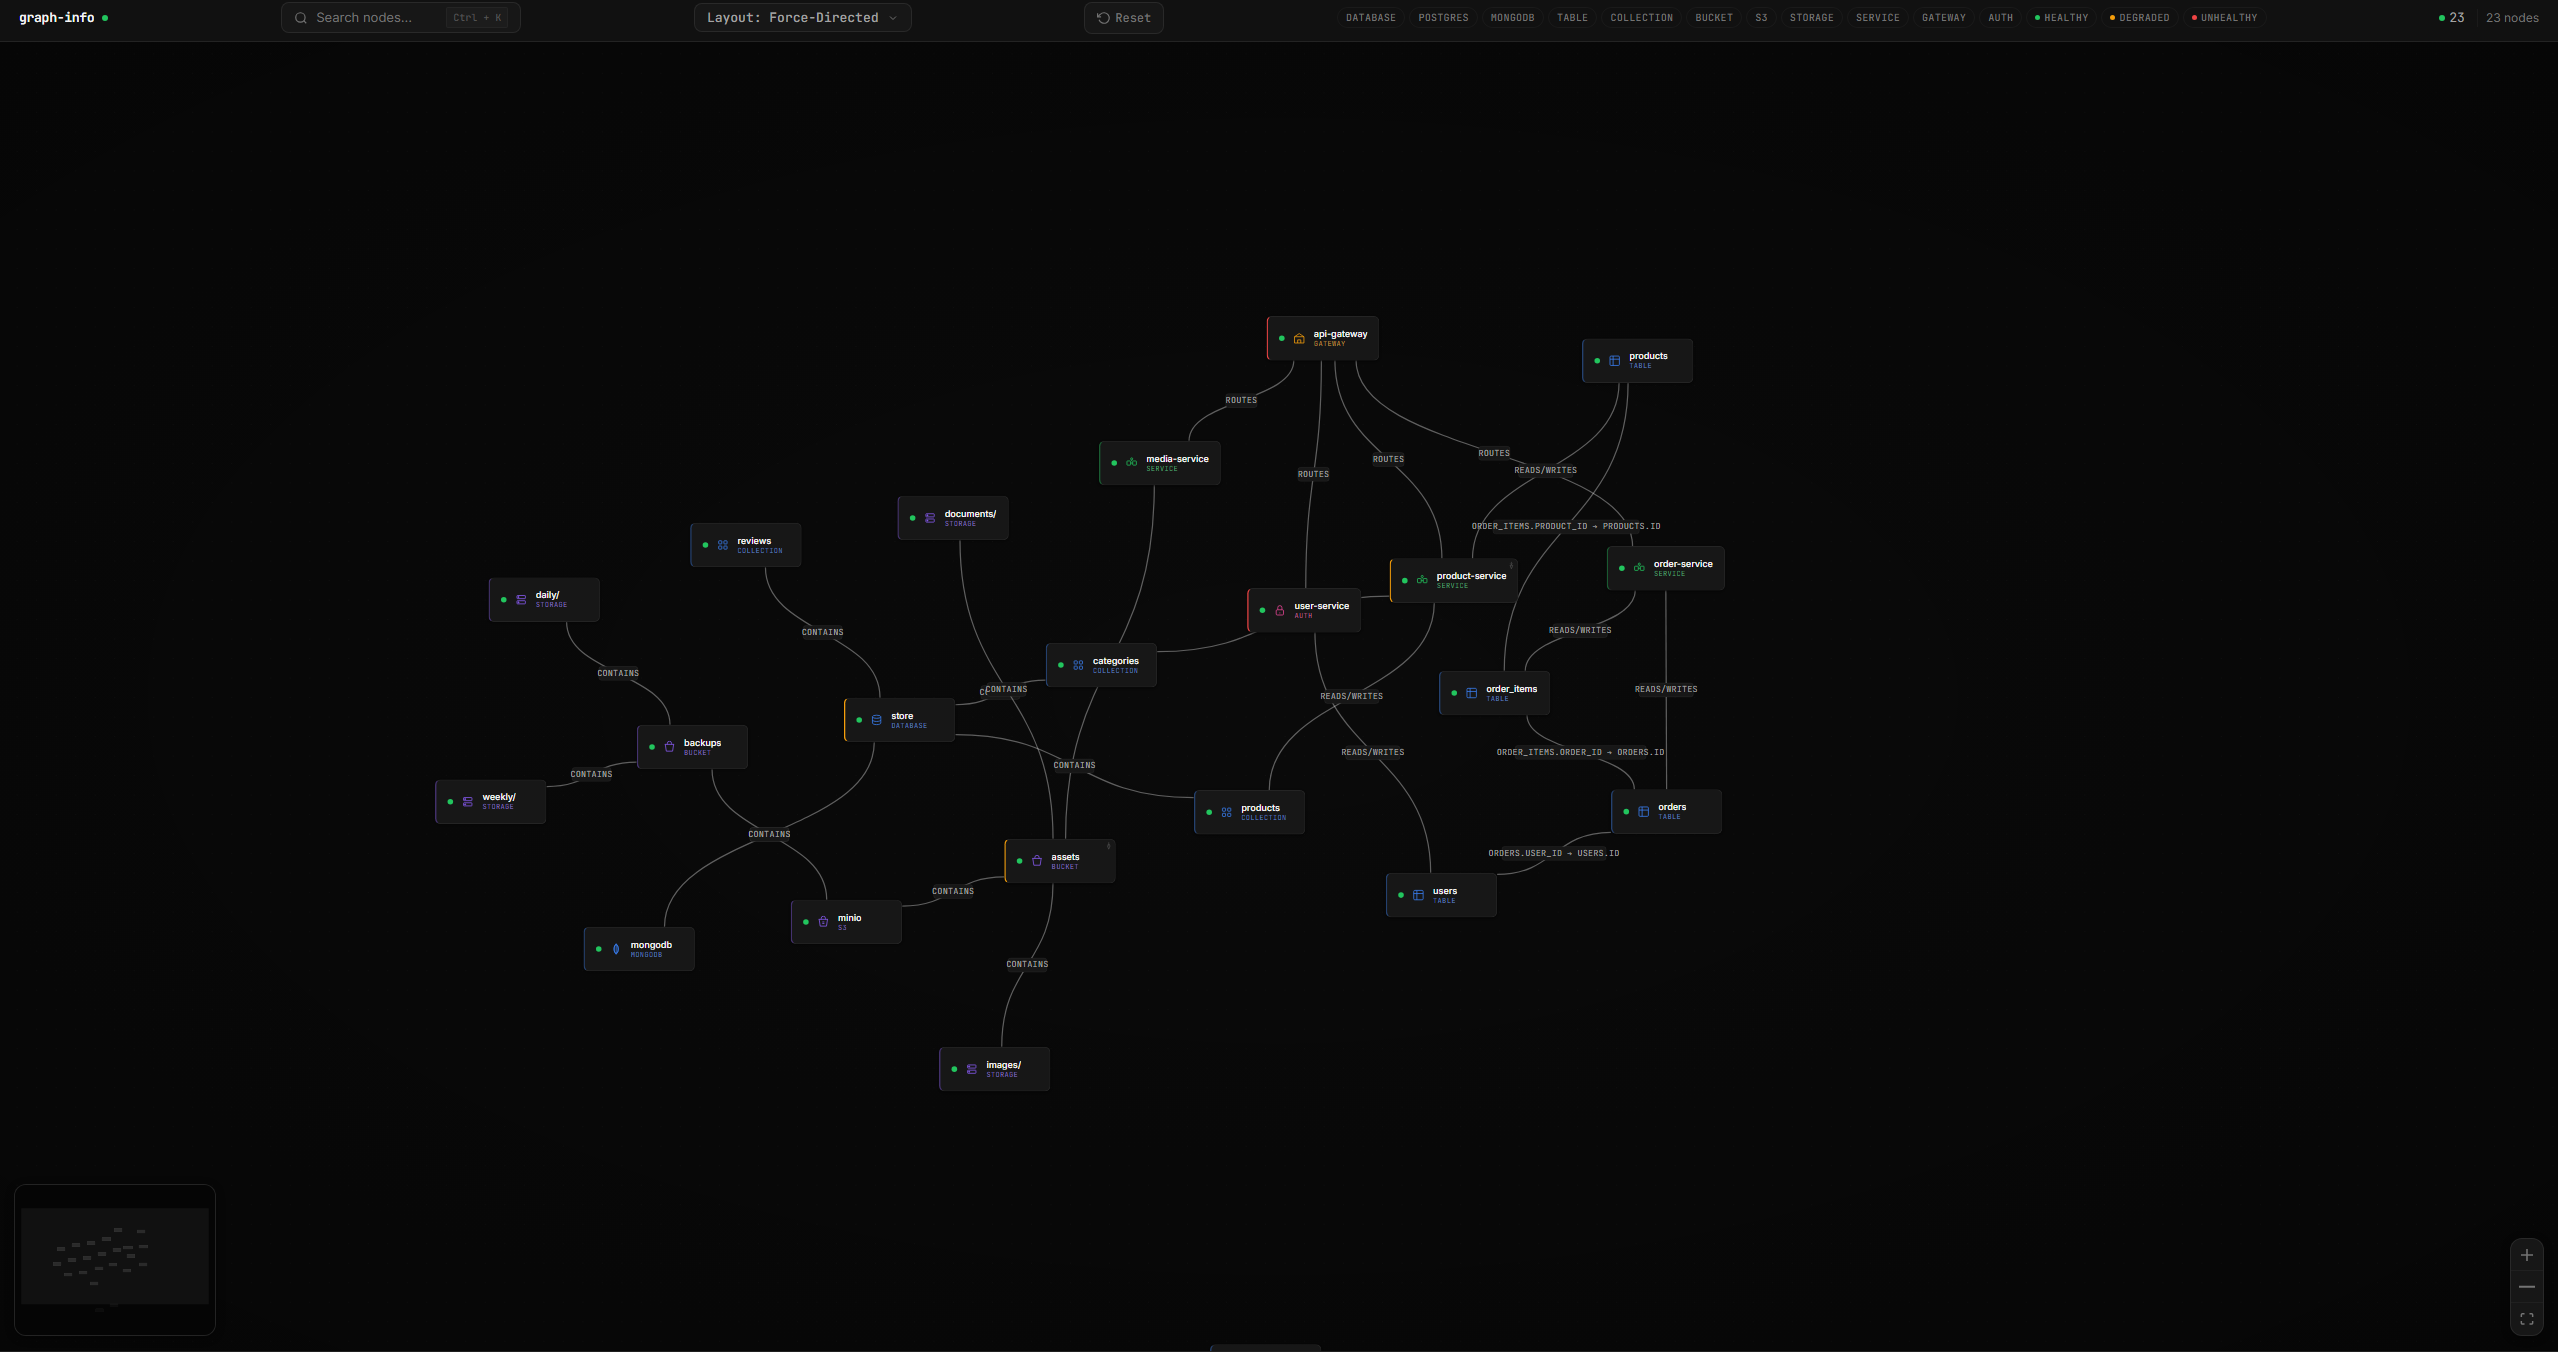 guilherme-grimm/graph-go
simply nodes and graphs
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
 bishopfox/cloudfox
Automating situational awareness for cloud penetration tests.
 cloudflare/cloudflared
Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
 juanfont/headscale
An open source, self-hosted implementation of the Tailscale control server