
cloudquery
Data pipelines for cloud config and security data. Build cloud asset inventory, CSPM, FinOps, and vulnerability management solutions. Extract from…

Data pipelines for cloud config and security data. Build cloud asset inventory, CSPM, FinOps, and vulnerability management solutions. Extract from…

Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more

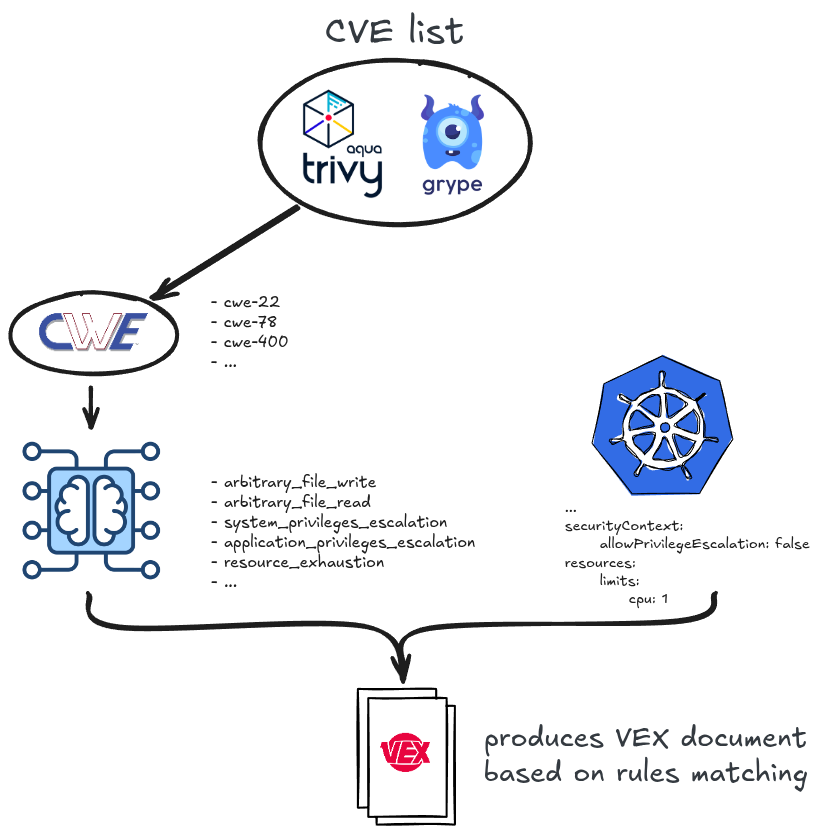
Suppress vulnerabilities applying Kubernetes context to scans

Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…

Complete fix collection for the CVE-2026-53359 guest-to-host escape vulnerability in the KVM/x86 shadow MMU. From zero-downtime livepatch to kernel…

Apache Hadoop YARN ResourceManager - Unauthenticated RCE PoC

Automated deployment of OWASP Juice Shop on Kubernetes using kubeadm and Terraform, with integrated Trivy vulnerability scanning for DevSecOps…

Simple Ansible Playbook to mitigate against CopyFail (CVE-2026-31431) and DirtyFrag (CVE-2026-43284) vulnerabilities.

Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…

Passive, read-only vulnerability scanner for detecting CVE-2026-41940 in cPanel & WHM. Performs version-based fingerprinting, generates…

Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…

An Ansible Playbook to mitigate the vulnerability CVE-2026-31431 on RHEL-based and Debian-based OSes.

Ansible playbooks to audit and mitigate CVE-2026-31431 ("Copy Fail"), a local privilege escalation vulnerability in the Linux kernel's `algif_aead`…

Kubernetes DaemonSet to detect and remediate CVE-2026-31431 (GHSA-2274-3hgr-wxv6) — algif_aead LPE via modprobe blacklist

Salt state to deploy a mitigation of the copy.fail vulnerability (CVE-2026-31431)

End-to-end vulnerability management lifecycle on Azure Windows Server 2025. Features OS patching and network-level compensating controls (NSG) to…

Docker base image with backported Host header validation fix for CVE-2025-12543 in Undertow 1.4.x, enabling secure deployment of WildFly 11…

Automated mitigation tool for CVE-2026-32746, providing atomic rollback, multi-firewall support (UFW, firewalld, nftables, iptables), and…