
redStackPRO
A canvas for red team infrastructure and cyber ranges. Compose a topology, export runnable Terraform and Ansible, and deploy it yourself. Your cloud…

A canvas for red team infrastructure and cyber ranges. Compose a topology, export runnable Terraform and Ansible, and deploy it yourself. Your cloud…

:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud

Automating situational awareness for cloud penetration tests.

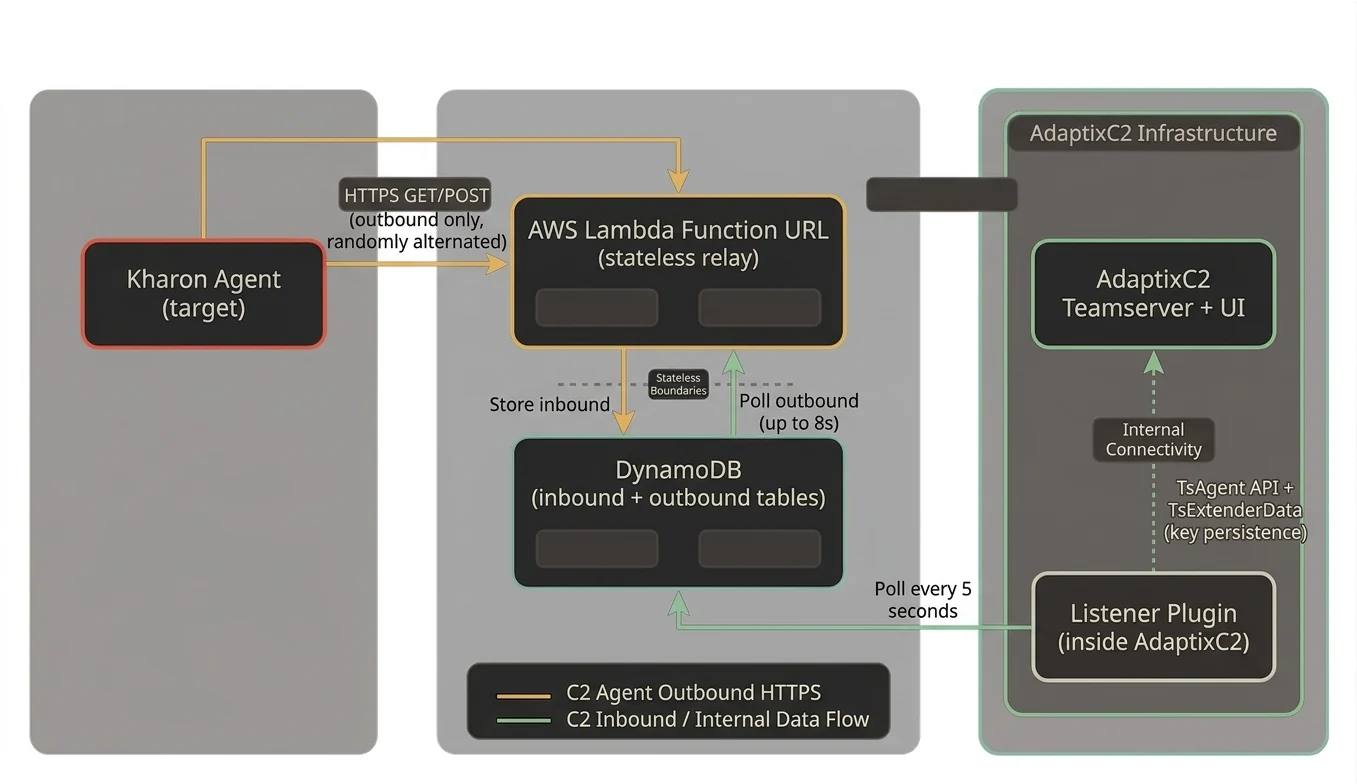
Serverless C2 transport plugin for AdaptixC2 v1.2 using AWS Lambda + DynamoDB as the relay infrastructure.

Terraform-deployed red team operator lab on AWS: Mythic, Sliver, and Adaptix C2 behind a production-style Apache redirector, with Kali/Windows hosts…

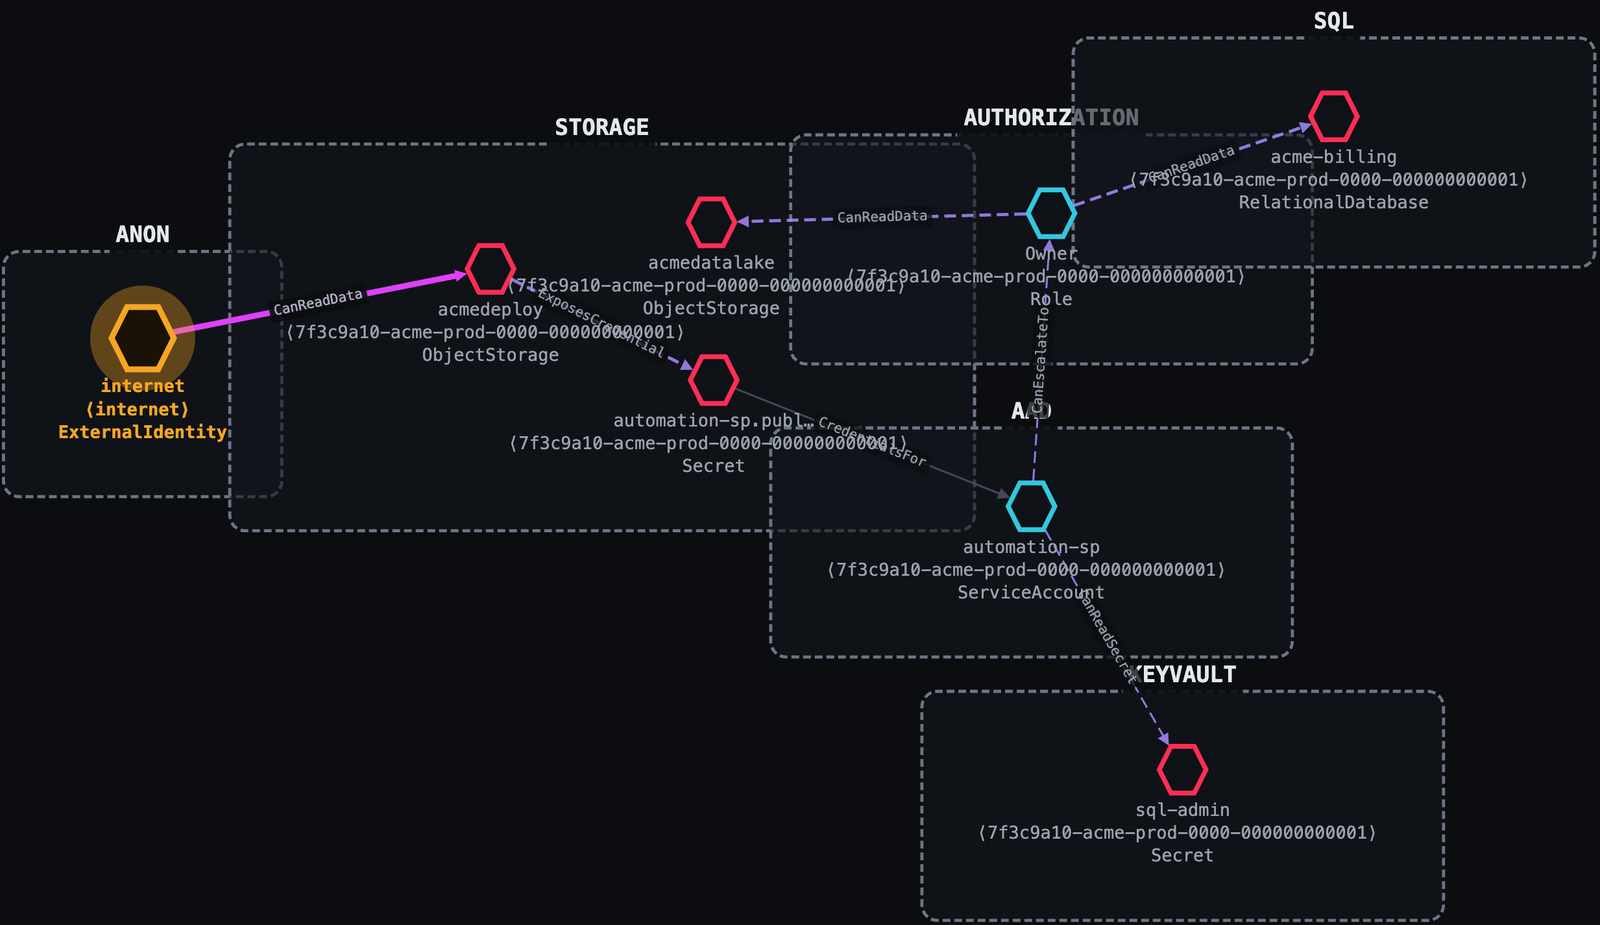
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…

Exploit KVM/x86 guest-to-host escape CVE-2026-64561 with Zapscape, a proof-of-concept demonstrating hypervisor vulnerability.

Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…

Proof-of-concept exploit for Kubernetes service-account token disclosure via hostPath mounts; includes vulnerable pod YAML and Python token-theft…

Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…

A collection of scripts for assessing Microsoft Azure security

AI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.

OpenClarity is an open source platform built to enhance security and observability of cloud native applications and infrastructure

DaemonSet с реализацией временной меры для митигации уязвимости Copy Fail (CVE-2026-31431)

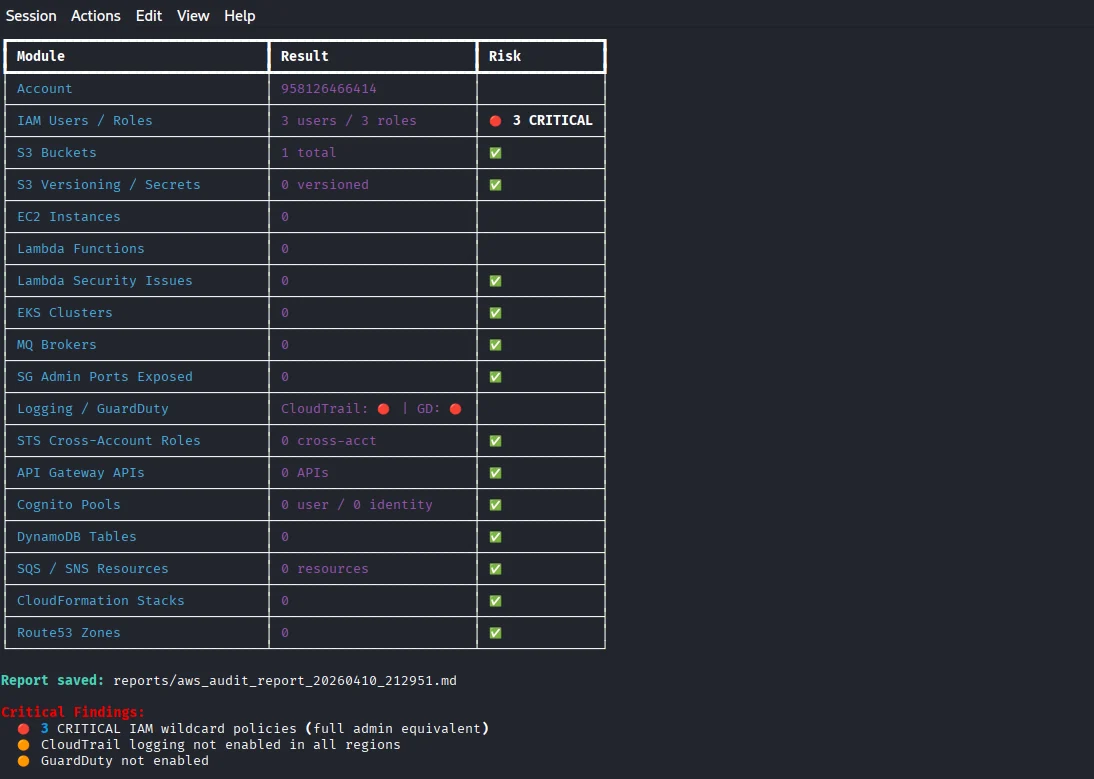
Automated AWS security assessment CLI with 30 modules covering IAM privilege escalation, S3 exposure, compute, network, logging and misconfiguration…

Exploit for Linux kernel CVE-2026-31431 causing page cache corruption via authencesn AEAD manipulation, targeting privilege escalation in containers…

Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)

The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.