

opa
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
api-securityauthenticationauthentication-authorization+10
12.4k
open-policy-agent/opaDeclarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 stillbigjosh/adaptix-serverless-c2
Serverless C2 transport plugin for AdaptixC2 v1.2 using AWS Lambda + DynamoDB as the relay infrastructure.
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 open-policy-agent/conftest
Write tests against structured configuration data using the Open Policy Agent Rego query language
 chaosblade-io/chaosblade
An easy to use and powerful chaos engineering experiment toolkit.(阿里巴巴开源的一款简单易用、功能强大的混沌实验注入工具)
 zeroecco/holos
Declarative KVM/QEMU VM orchestration tool using YAML compose files. Manages multi-VM stacks with cloud-init, SSH, PCI passthrough, and image…
 oseguera12/cowrie-honeypot-digitalocean
Medium-interaction SSH/Telnet honeypot built with Cowrie, Loki, Promtail, and Grafana - provisioned on DigitalOcean via Terraform with a GitLab CI…
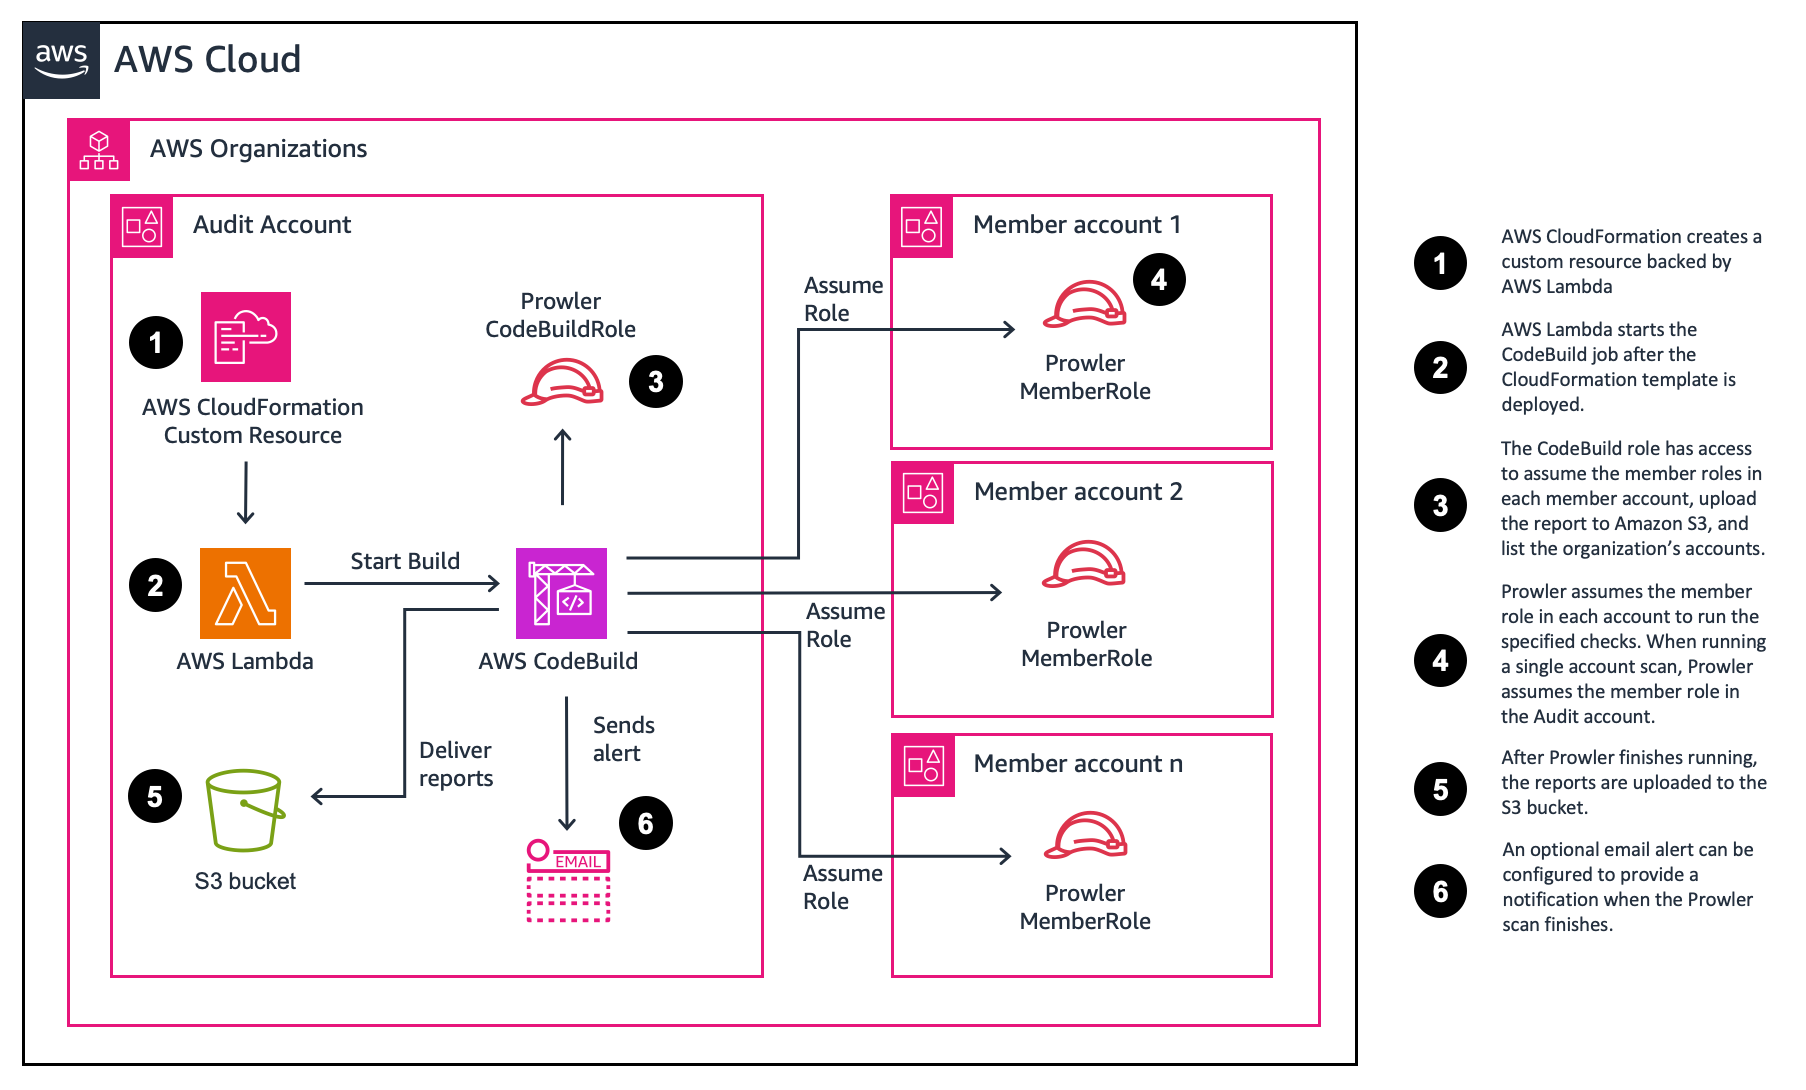 awslabs/aws-security-assessment-solution
An AWS tool to help you create a point in time assessment of your AWS account using Prowler.
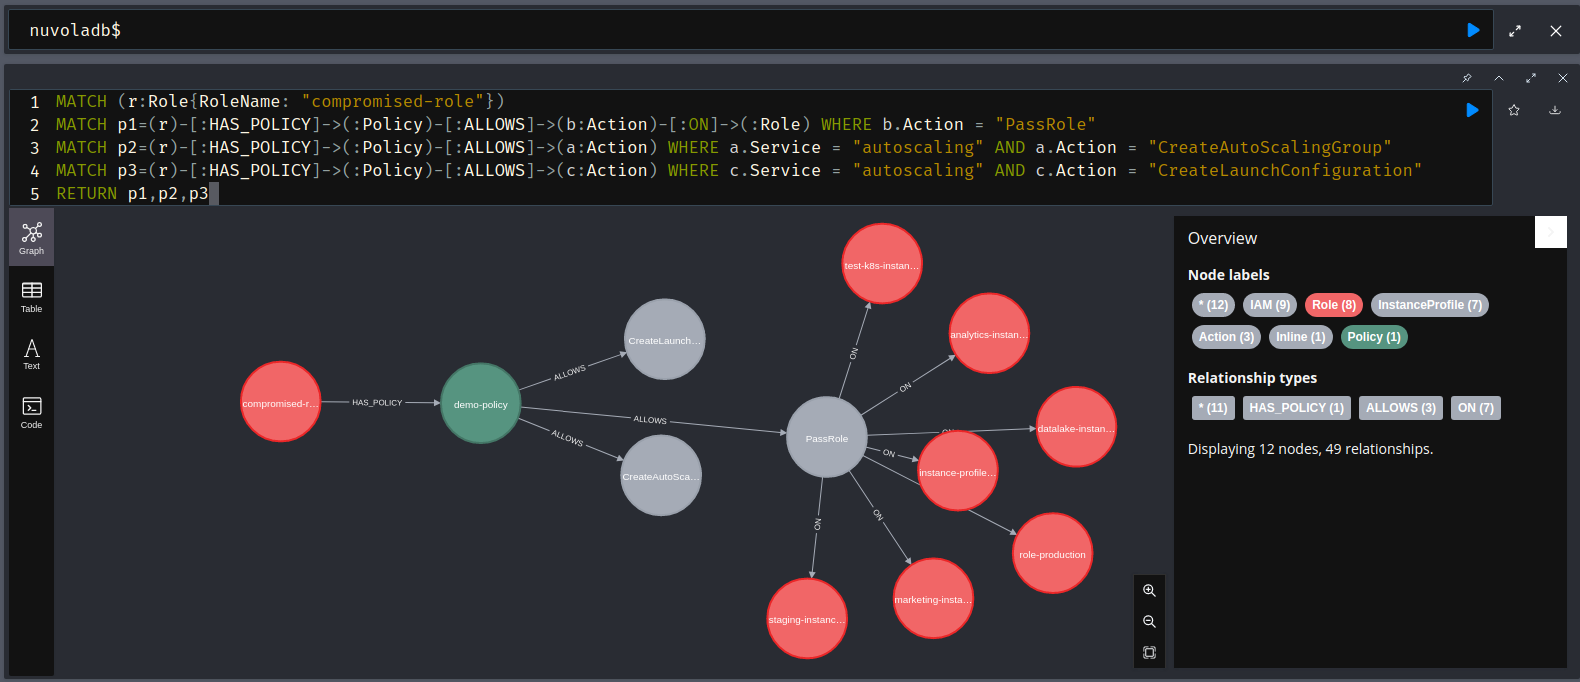 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
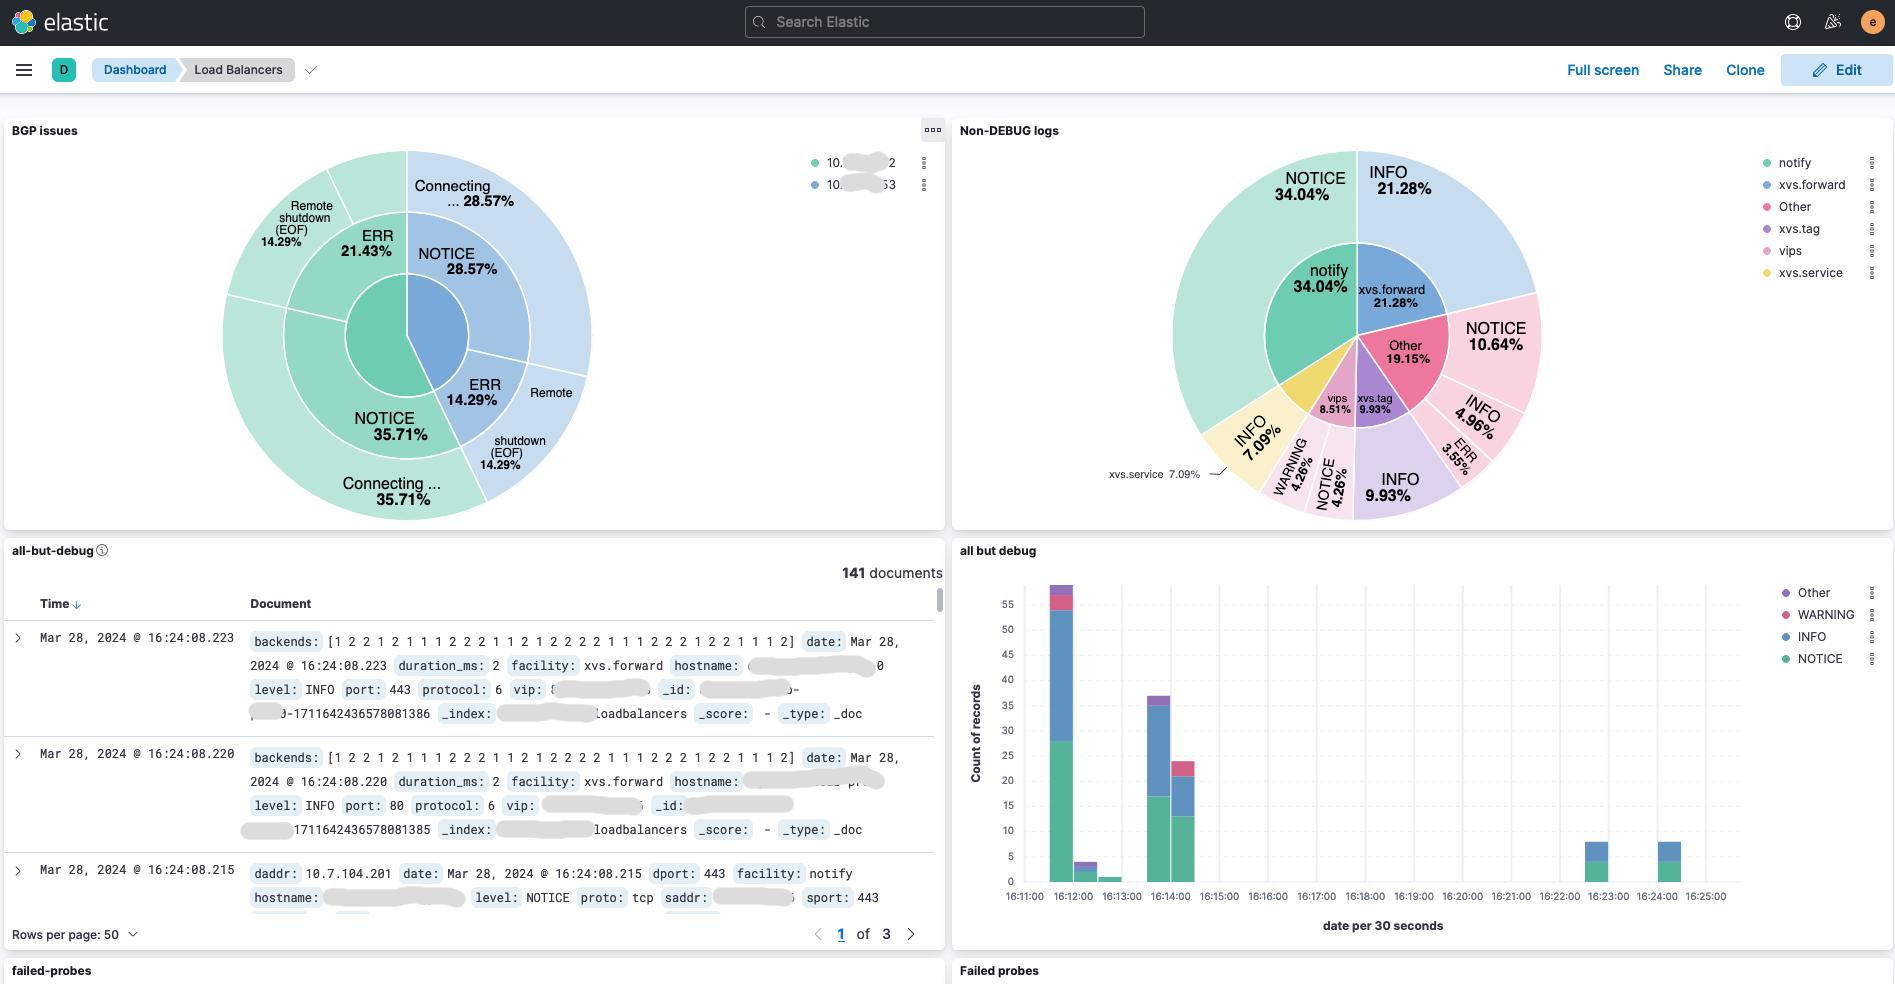 davidcoles/vc5
A horizontally scalable Direct Server Return layer 4 load balancer for Linux using XDP/eBPF
 barun121/cve-2024-9264-in-grafana-11.x
Vulnerability Exploitation using tools Penetration Testing, Grafana, Docker, Kali Linux.
 qmadev/tf-mythic-azure
Automatically deploying Mythic C2 in Azure using Terraform
 zzugab/juice-shop-with-kubeadm-and-tf
Automated deployment of OWASP Juice Shop on Kubernetes using kubeadm and Terraform, with integrated Trivy vulnerability scanning for DevSecOps…
 m0nk3ygod/cve-2026-34040-poc
Lab reproduction of CVE-2026-34040: bypasses Docker/Moby AuthZ plugins using oversized (>1MB) request bodies to create privileged containers with…
 infiniroot/ansible-mitigate-copyfail-dirtyfrag
Simple Ansible Playbook to mitigate against CopyFail (CVE-2026-31431) and DirtyFrag (CVE-2026-43284) vulnerabilities.
 aestechno/cve-2026-31431-ansible
Ansible playbook to detect and apply kernel cmdline mitigation for CVE-2026-31431 (Copy Fail) across Debian/Ubuntu/RHEL fleets, with read-only…
 jbiniek/copy.fail-mitigation-mlm
Salt state to deploy a mitigation of the copy.fail vulnerability (CVE-2026-31431)
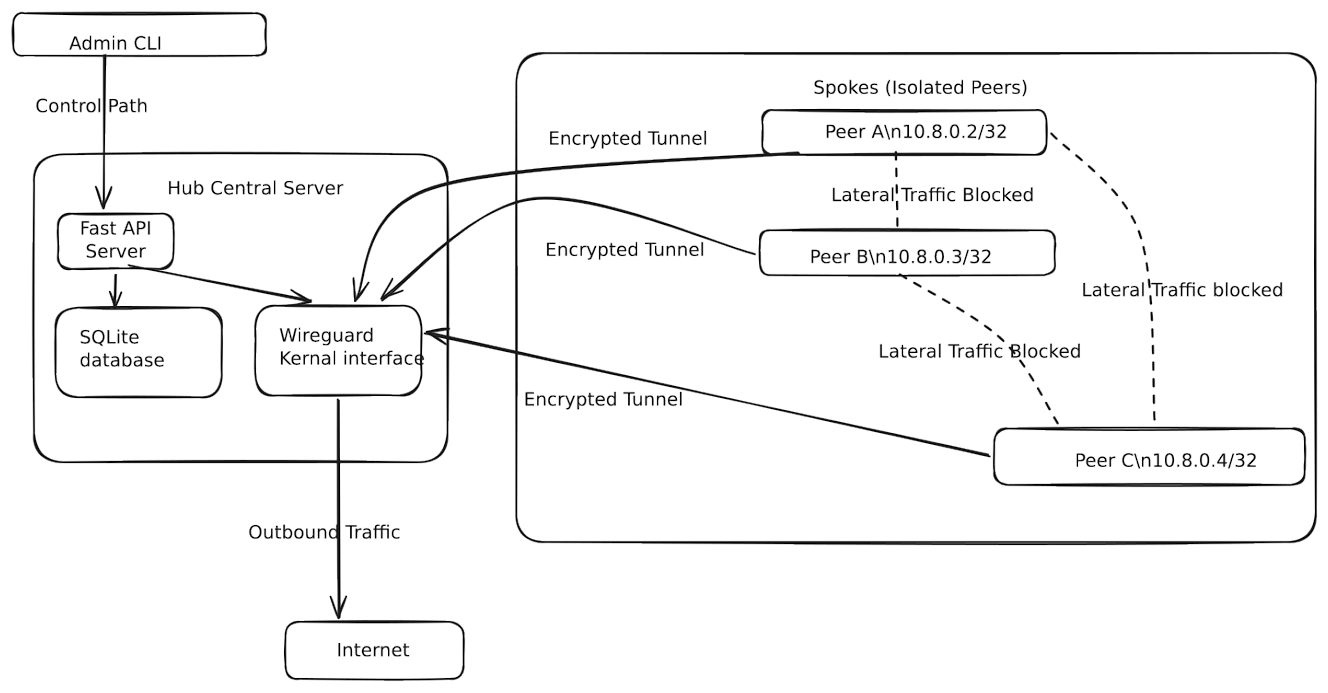 alvin-alvo/safenet-soho-security-framework
A lightweight, policy-driven framework that brings Zero-Trust micro-segmentation to SOHO networks using WireGuard.