
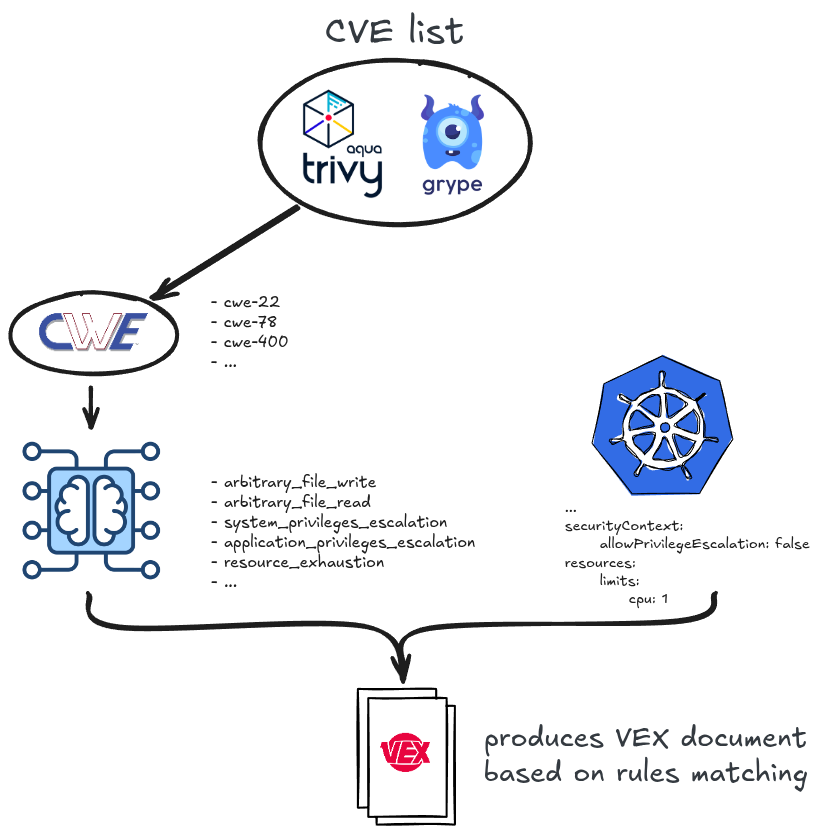
vex8s
 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
cloud-infrastructure-securitycloud-securityconfiguration-auditing+7
388 days ago
alegrey91/vex8sSuppress vulnerabilities applying Kubernetes context to scans
 barun121/cve-2024-9264-in-grafana-11.x
Vulnerability Exploitation using tools Penetration Testing, Grafana, Docker, Kali Linux.
 aarif450/aarif450.github.io
Exploit KVM/x86 guest-to-host escape CVE-2026-64561 with Zapscape, a proof-of-concept demonstrating hypervisor vulnerability.
 chuzhongyun/cve-2026-64561-kernel-fix
Linux 内核升级指南 - 修复 CVE-2026-64561
 0xblackash/cve-2026-64531
Reference analysis of a Linux kernel Open vSwitch memory-corruption vulnerability, covering root cause, impact, detection commands, and mitigation…
 chuzhongyun/cve-2026-53359-kernel-fix
Linux 内核升级指南 - 修复 CVE-2026-53359
 aoripus-ltd/januscape-hotfix
Complete fix collection for the CVE-2026-53359 guest-to-host escape vulnerability in the KVM/x86 shadow MMU. From zero-downtime livepatch to kernel…
 infiniroot/ansible-mitigate-copyfail-dirtyfrag
Simple Ansible Playbook to mitigate against CopyFail (CVE-2026-31431) and DirtyFrag (CVE-2026-43284) vulnerabilities.
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
 linko-iheb/cve-2026-41940-scanner
Passive, read-only vulnerability scanner for detecting CVE-2026-41940 in cPanel & WHM. Performs version-based fingerprinting, generates…
 mahdi13830510/cve-2026-31431-mitigation-suite
Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…
 mlazzarotto/copy-fail-cve-2026-31431-mitigation-ansible-playbook
An Ansible Playbook to mitigate the vulnerability CVE-2026-31431 on RHEL-based and Debian-based OSes.
 mahradbt/copyfail-mitigation
Ansible playbooks to audit and mitigate CVE-2026-31431 ("Copy Fail"), a local privilege escalation vulnerability in the Linux kernel's `algif_aead`…
 boliu83/cve-2026-31431-algif-aead-remediator
Kubernetes DaemonSet to detect and remediate CVE-2026-31431 (GHSA-2274-3hgr-wxv6) — algif_aead LPE via modprobe blacklist
 jbiniek/copy.fail-mitigation-mlm
Salt state to deploy a mitigation of the copy.fail vulnerability (CVE-2026-31431)
 dawnsmithcyber/azure-vulnerability-remediation-project
End-to-end vulnerability management lifecycle on Azure Windows Server 2025. Features OS patching and network-level compensating controls (NSG) to…
 kavin71725/cve-2025-12543-fix-for-wildfly
Docker base image with backported Host header validation fix for CVE-2025-12543 in Undertow 1.4.x, enabling secure deployment of WildFly 11…
 hodgeluke/ai-agent-security-research
Open security research on AI coding agent infrastructure. Agent-executable remediation manifests for CVE-2026-22812 and CVE-2026-22813.