
CloudGarrison
Offline browser-based multi-cloud posture workbench that simulates attack paths, audits IaC compliance, analyzes identity graphs, and maps audit logs…

Offline browser-based multi-cloud posture workbench that simulates attack paths, audits IaC compliance, analyzes identity graphs, and maps audit logs…

Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…

Acquires the EBS disks of an AWS AMI you can launch, streaming snapshots via EBS direct APIs to a private S3 bucket with sha256 manifests and…

Cross-cloud S3-compatible object storage CLI to list, export, and download buckets across AWS, Aliyun, Tencent, Huawei and more, with anonymous…

Scans public cloud object-storage endpoints across Yandex, VK, Selectel, Sber, Alibaba, Tencent, Huawei, and Baidu to find listable buckets and…

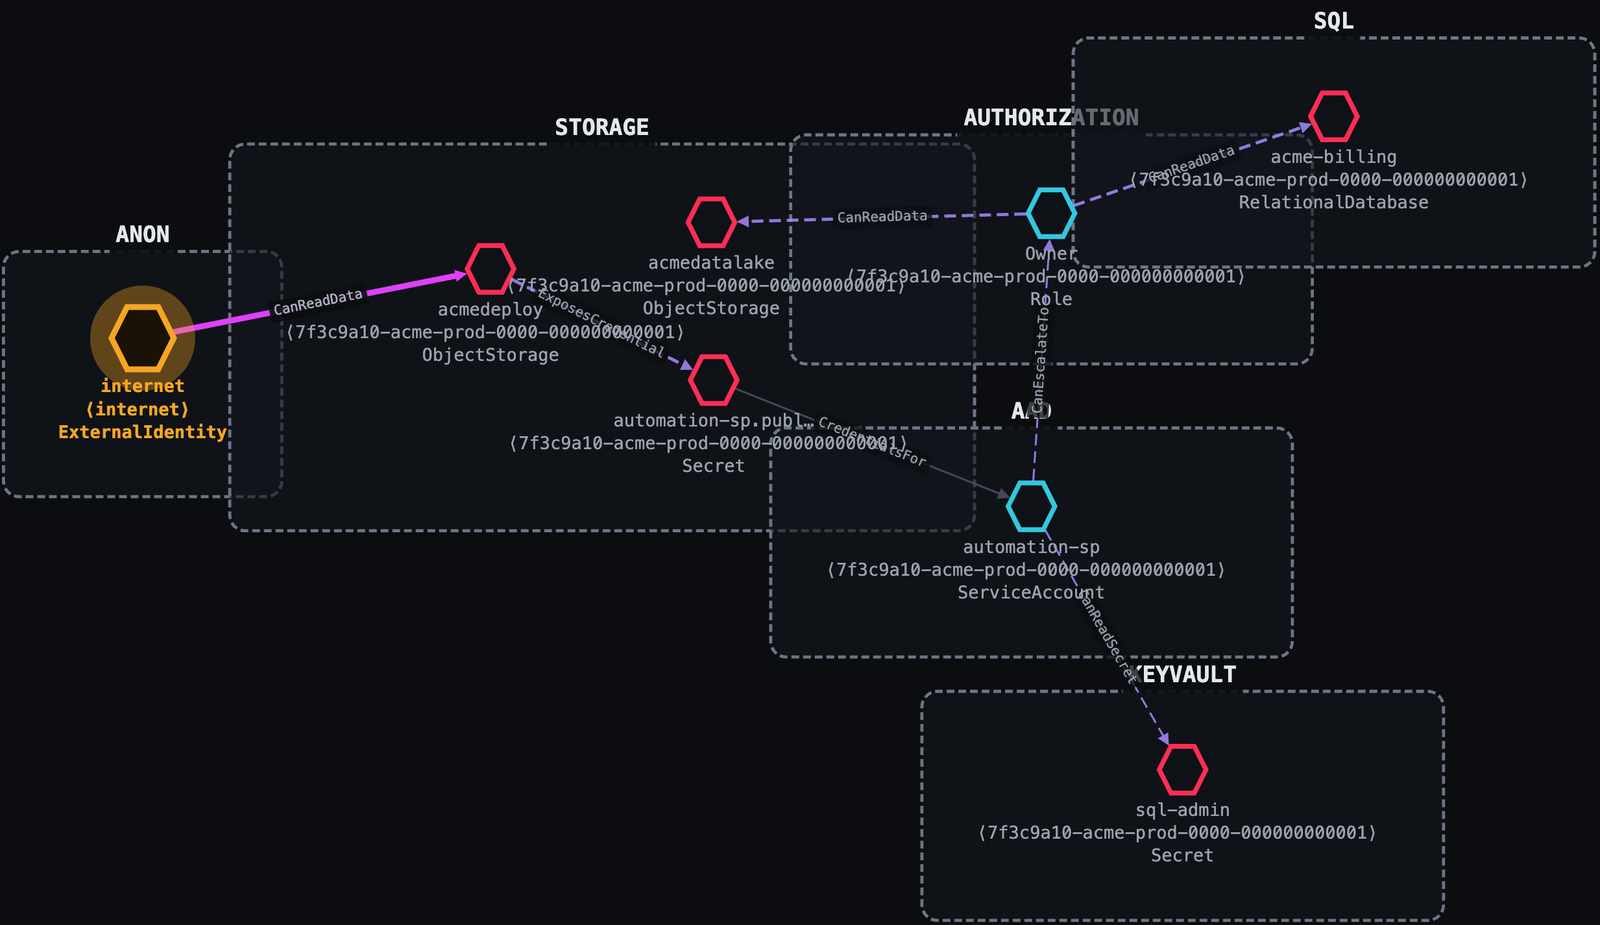
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…

Policy-driven, layered isolation and containment

This puppet module provides numerous security-related configurations, providing all-round base protection.

This chef cookbook provides secure ssh-client and ssh-server configurations.

This puppet module provides secure ssh-client and ssh-server configurations.

JetBrains TeamCity On-Premises CVE-2026-63077 Emergency Hardening & Patch Runbook Package

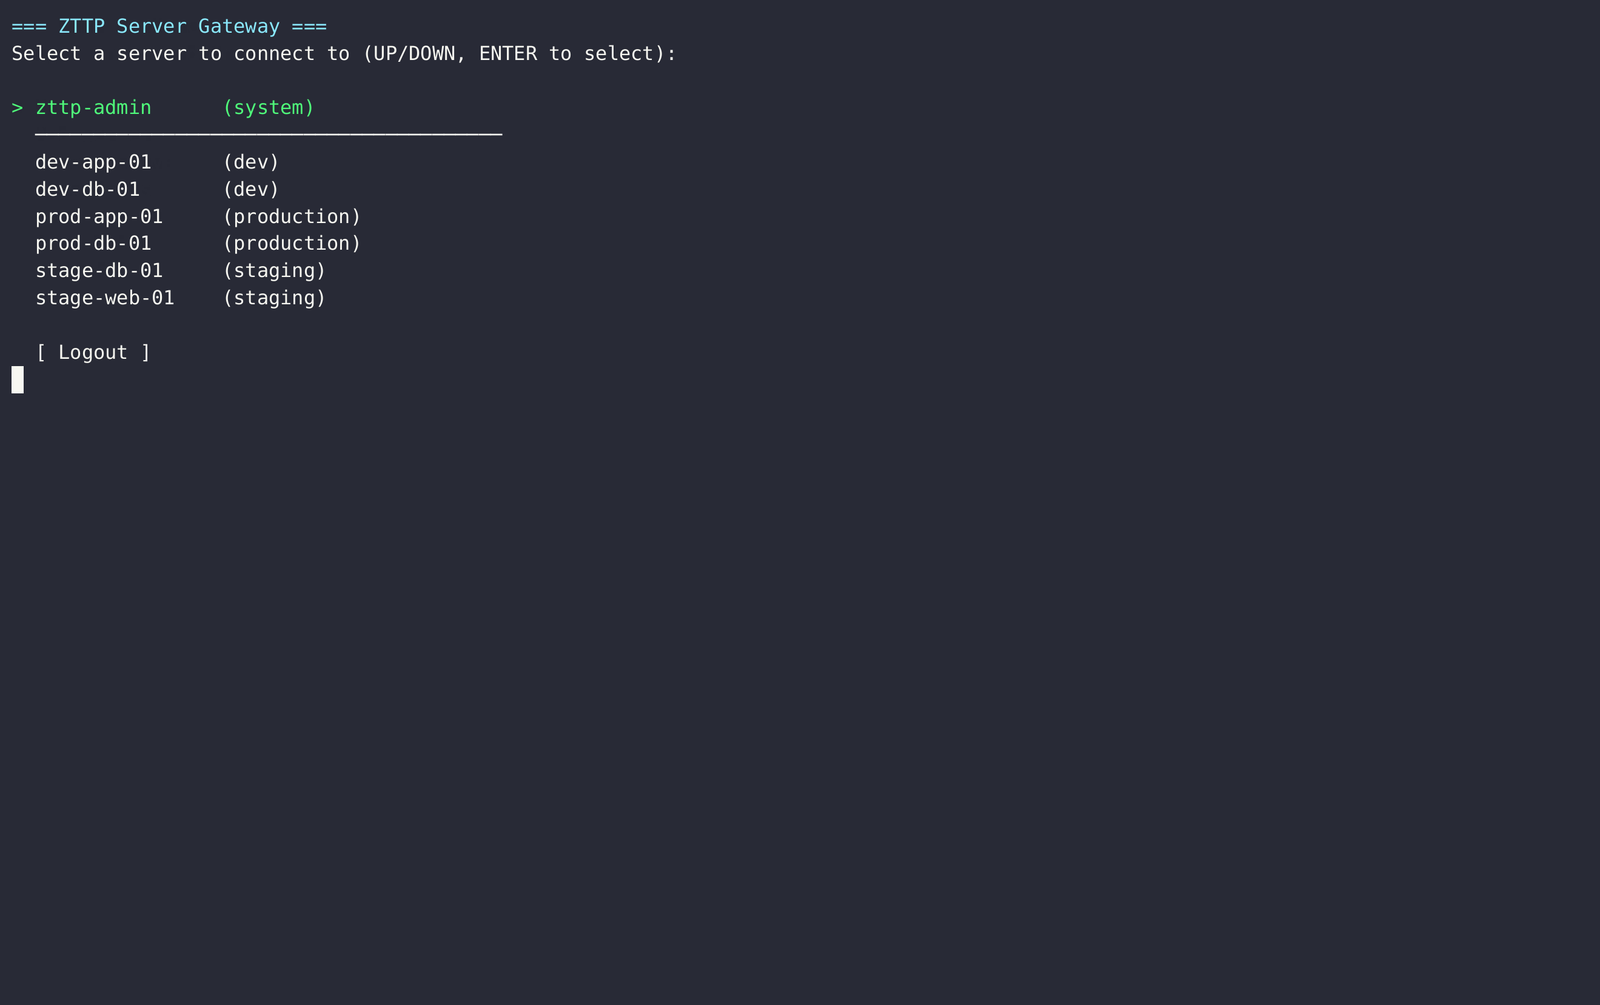
Zero-trust SSH bastion proxy with Vault-backed key management, RBAC policy enforcement, full session recording, and admin TUI for auditable access to…

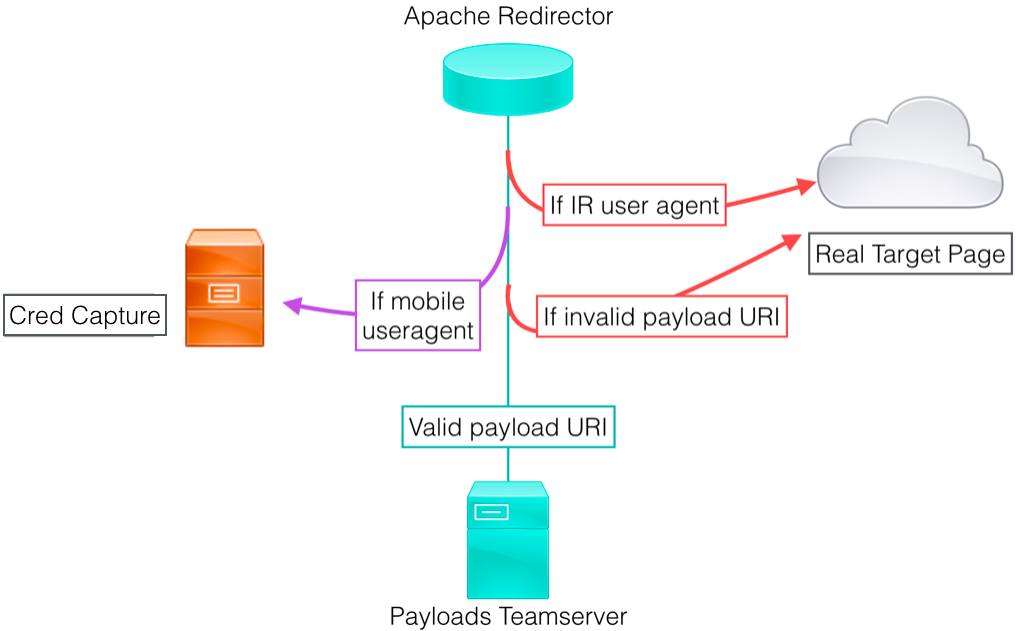
Wiki to collect Red Team infrastructure hardening resources

Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…

Scans GitHub Enterprise Server instances for CVE-2026-3854 and CVE-2026-4821, providing version-based detection with batch scanning and multiple…

Read-only audit tooling for CVE-2026-0300 (PAN-OS User-ID Authentication Portal exposure)

Safely detect Veeam Service Provider Console auth bypass CVE-2026-58073

One-shot detection and remediation for cPanel/WHM servers compromised via CVE-2026-41940, including IOC checks, malware cleanup, C2 blocking, and…