

trivy
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
cloud-infrastructure-securitycloud-securitycode-analysis+14
37.4k
aquasecurity/trivyFind vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 cloudquery/cloudquery
Data pipelines for cloud config and security data. Build cloud asset inventory, CSPM, FinOps, and vulnerability management solutions. Extract from…
 puppetlabs-toy-chest/puppetlabs-cve20113872
Puppet Module to help fix and migrate a Puppet deployment (CVE-2011-3872)
 blake-fm/vcenter-log4j
Script to apply official workaround for VMware vCenter log4j vulnerability CVE-2021-44228
 danindiana/cve-2026-32746-mitigation
Automated mitigation tool for CVE-2026-32746, providing atomic rollback, multi-firewall support (UFW, firewalld, nftables, iptables), and…
 boliu83/cve-2026-31431-algif-aead-remediator
Kubernetes DaemonSet to detect and remediate CVE-2026-31431 (GHSA-2274-3hgr-wxv6) — algif_aead LPE via modprobe blacklist
 mahdi13830510/cve-2026-31431-mitigation-suite
Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…
 abrahamsurf/sdwan-scanner-cve-2026-20127
Cisco SD-WAN Exposure & Potential Vulnerability Scanner (Passive Fingerprinting) 2026
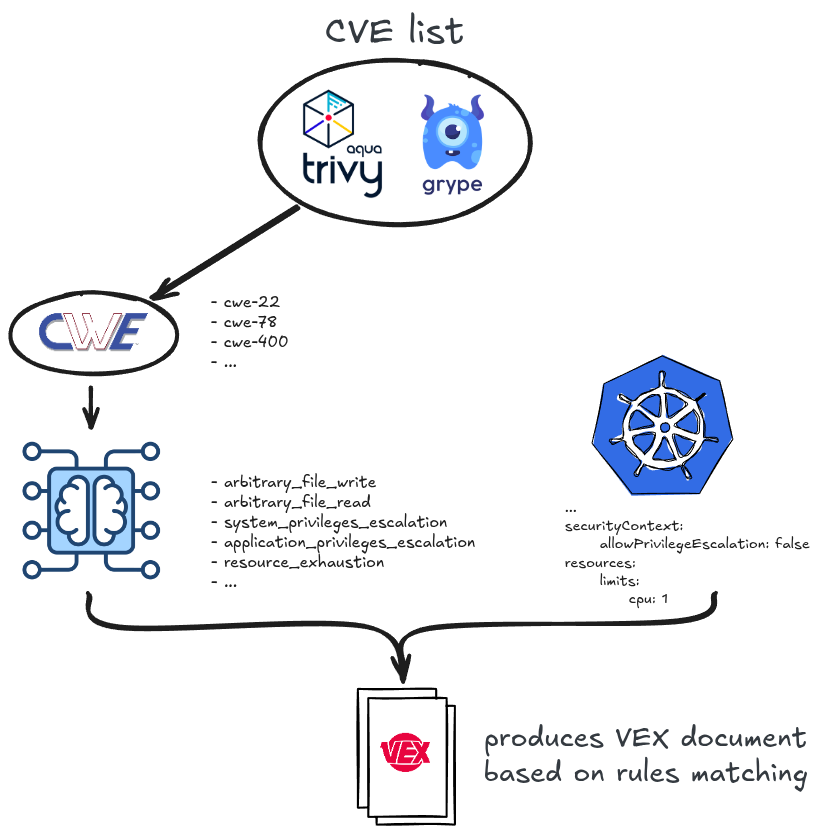 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
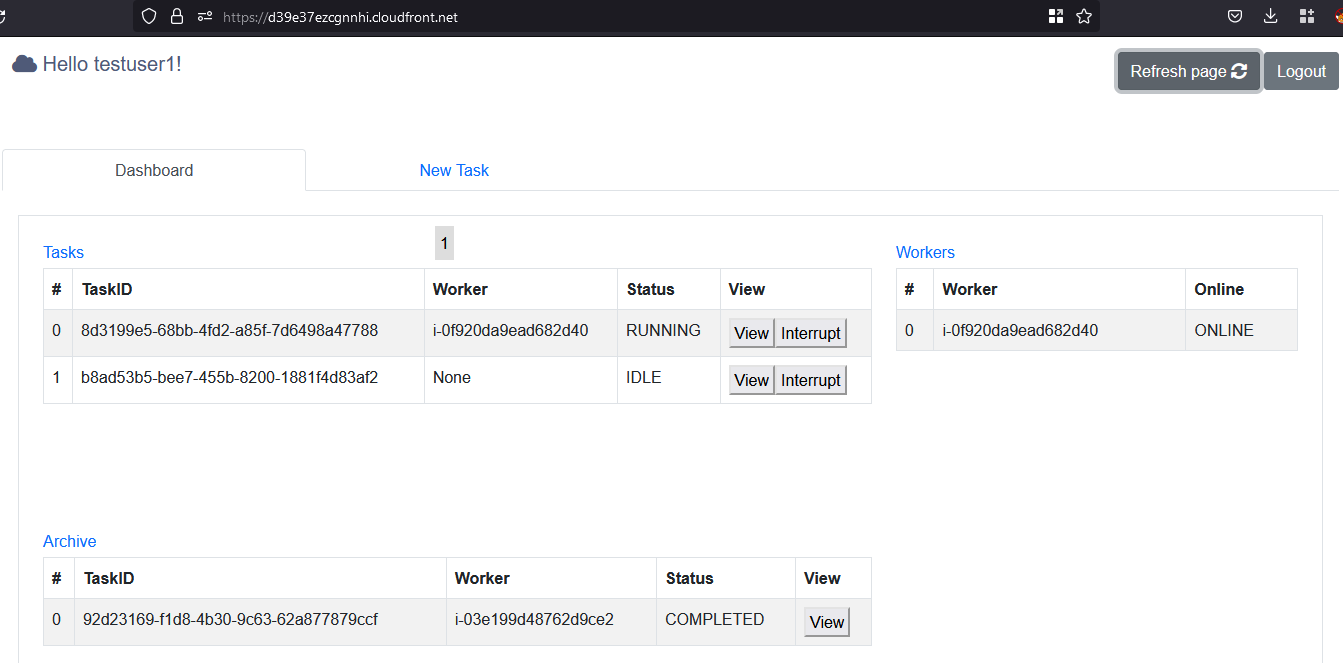 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
 linko-iheb/cve-2026-41940-scanner
Passive, read-only vulnerability scanner for detecting CVE-2026-41940 in cPanel & WHM. Performs version-based fingerprinting, generates…
 mlazzarotto/copy-fail-cve-2026-31431-mitigation-ansible-playbook
An Ansible Playbook to mitigate the vulnerability CVE-2026-31431 on RHEL-based and Debian-based OSes.
 xlab-si/iac-scan-runner
Service that scans your Infrastructure as Code for common vulnerabilities
 mahradbt/copyfail-mitigation
Ansible playbooks to audit and mitigate CVE-2026-31431 ("Copy Fail"), a local privilege escalation vulnerability in the Linux kernel's `algif_aead`…
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 zzugab/juice-shop-with-kubeadm-and-tf
Automated deployment of OWASP Juice Shop on Kubernetes using kubeadm and Terraform, with integrated Trivy vulnerability scanning for DevSecOps…
 aoripus-ltd/januscape-hotfix
Complete fix collection for the CVE-2026-53359 guest-to-host escape vulnerability in the KVM/x86 shadow MMU. From zero-downtime livepatch to kernel…