
AzureADEnumeration
 logisek/azureadenumeration
Microsoft Entra ID (Azure AD) Unauthenticated Enumeration
cloud-infrastructure-securitycloud-securitydns-analysis+6
79
logisek/azureadenumerationMicrosoft Entra ID (Azure AD) Unauthenticated Enumeration
 netspi/microburst
A collection of scripts for assessing Microsoft Azure security
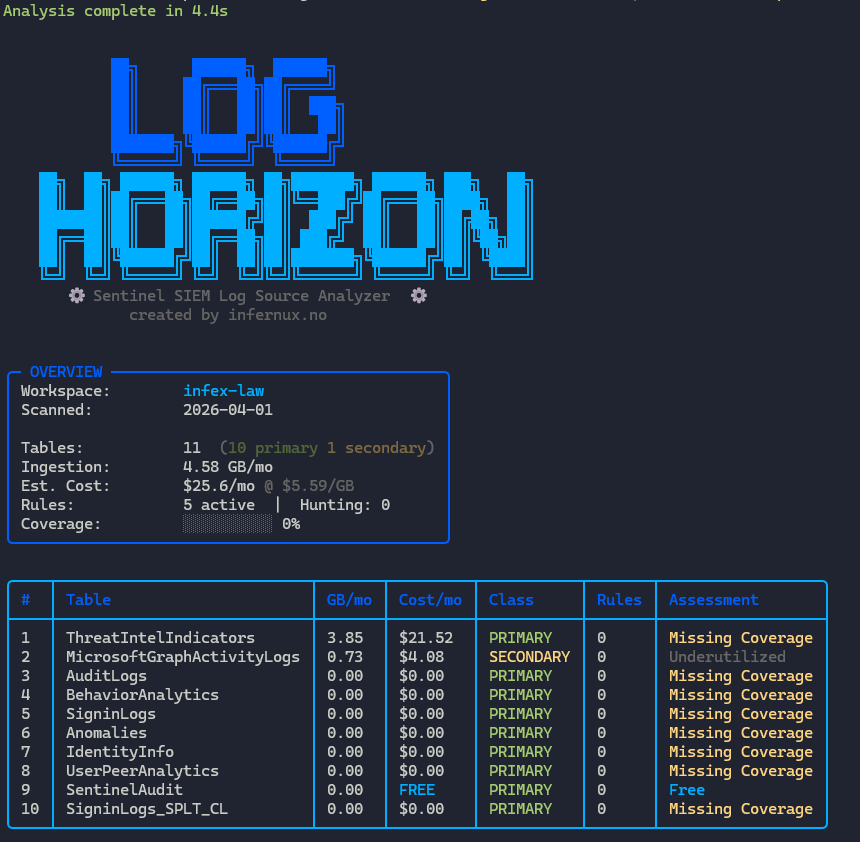 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…
 azuread/azureadassessment
Tooling for assessing an Azure AD tenant state and configuration
 neelkotnis/azure-security-auditor
CLI tool to audit Azure security posture, RBAC, NSGs, storage, identity, and encryption
 azuread/azure-ad-incident-response-powershell-module
The Azure Active Directory Incident Response PowerShell module provides a number of tools, developed by the Azure Active Directory Product Group in…
 expl0itabl3/check_mdi
Python script to enumerate valid Microsoft 365 domains, retrieve tenant name, and check for an MDI instance.