
CVE-2023-2002
 lrh2000/cve-2023-2002
Linux Bluetooth - Run arbitrary management commands as an unprivileged user
binary-exploitationbluetooth-securityeducation+3
853 years ago
lrh2000/cve-2023-2002Linux Bluetooth - Run arbitrary management commands as an unprivileged user
 zalexdev/wpair-app
WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
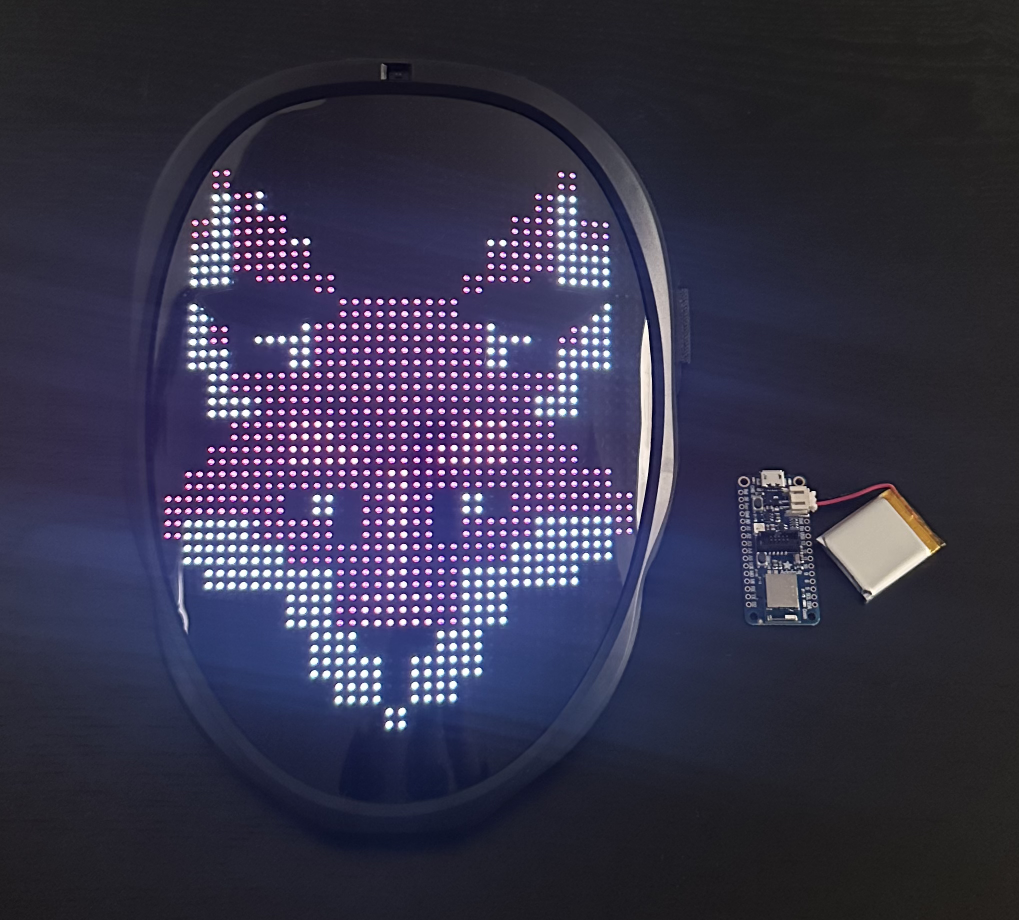 bishopfox/shining-mask
BLE-based tool that automatically discovers and exploits Shining LED Masks by uploading a custom image without user interaction, proving security…
 sergeb250/blueducky
BlueDucky exploits a Bluetooth vulnerability, specifically CVE-2023-45866, which allows an attacker to inject keystrokes into a target device. The…
 nccgroup/blesuite
BLESuite is a Python package that provides an easier way to test Bluetooth Low Energy (BLE) device
 anssi-fr/ultrablue
User-friendly Lightweight TPM Remote Attestation over Bluetooth
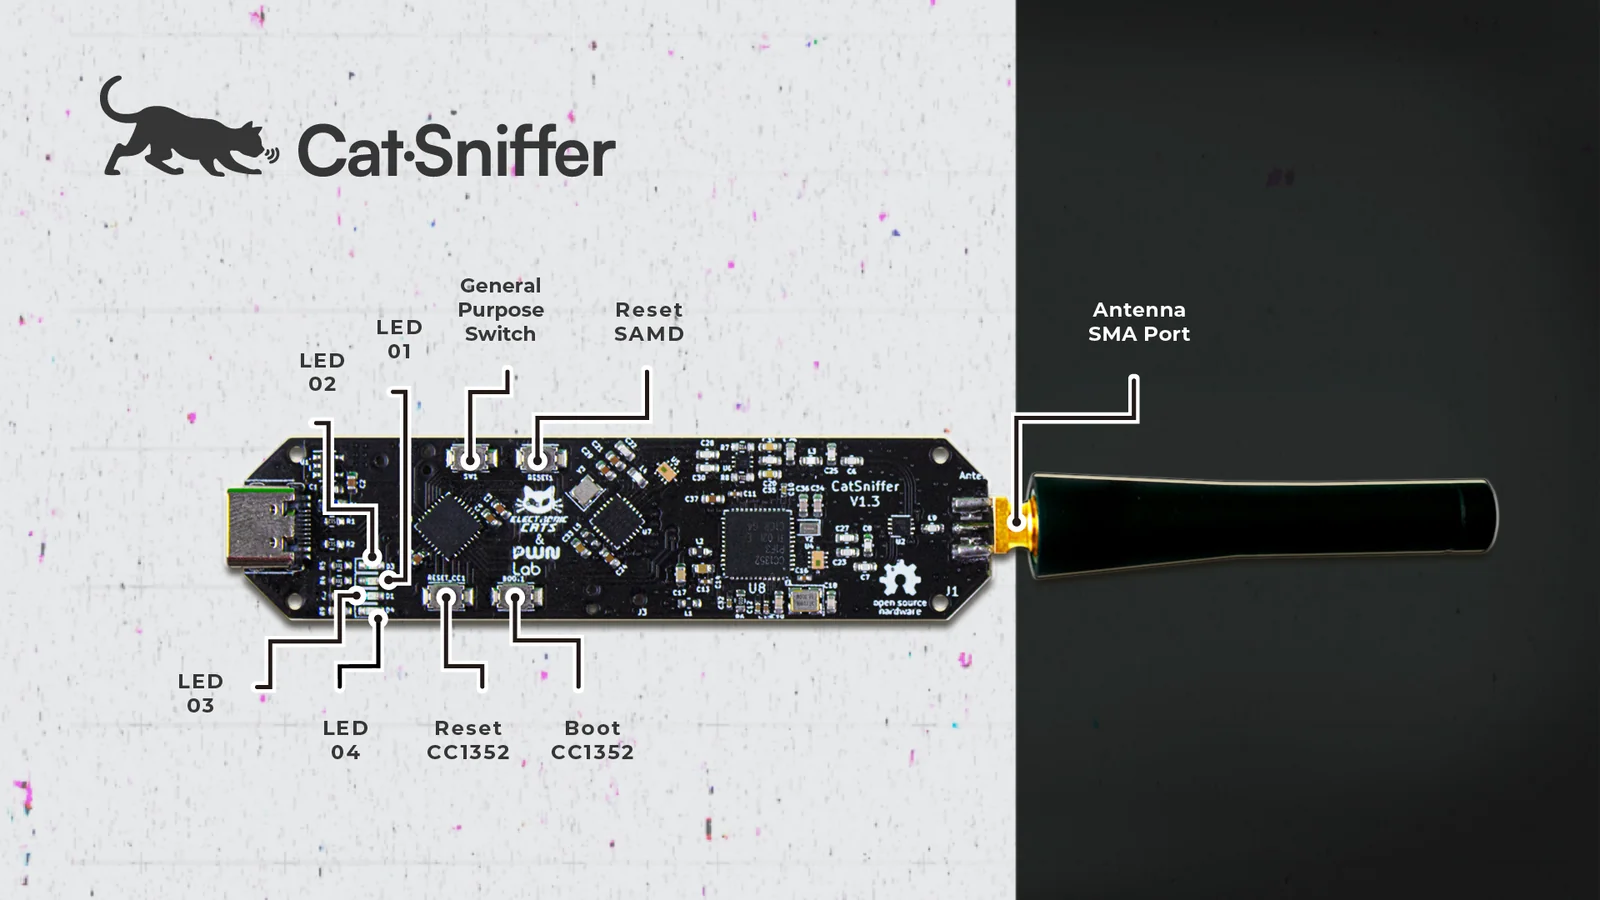 electroniccats/catsniffer-firmware
Firmware repository for CatSniffer, a multi-protocol IoT security research board supporting BLE, Zigbee, Sub-1 GHz, and more, with version-specific…