

KITT
 cisc0-gif/kitt
Python-Based Pentesting Framework
bluetooth-securityexploit-frameworkshardware-hacking+9
cisc0-gif/kittPython-Based Pentesting Framework
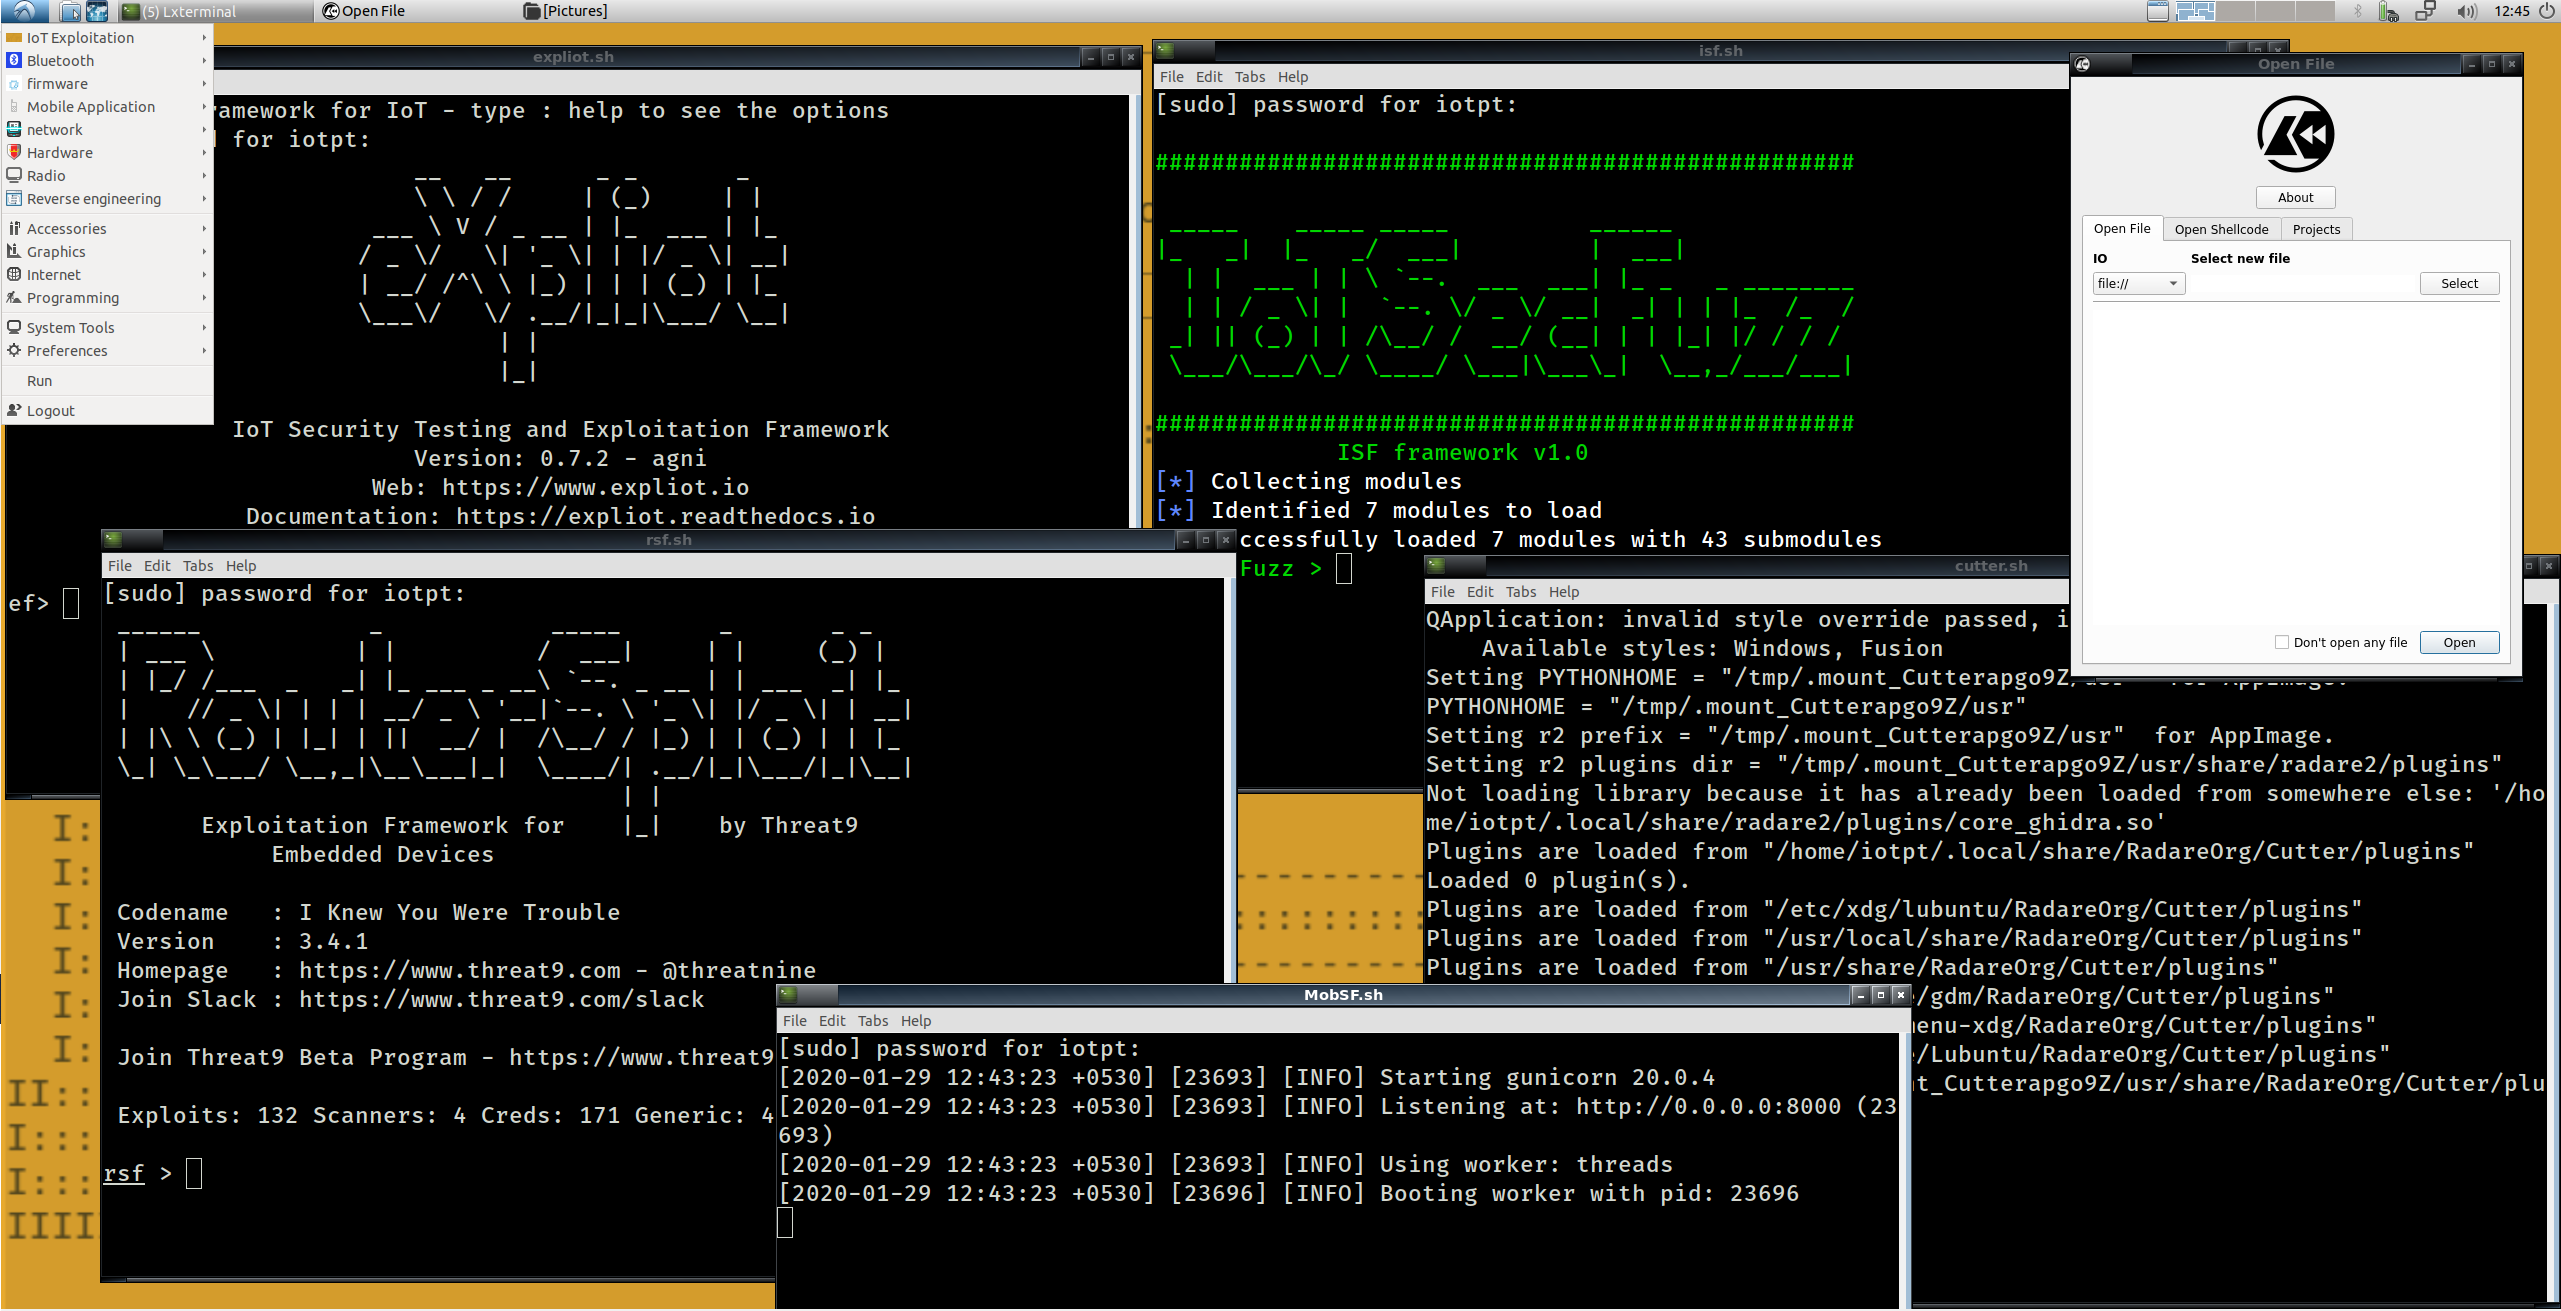 iot-ptv/iot-pt-v1
A Virtual environment for Pentesting IoT Devices
 rogandawes/p4wnp1_aloa
P4wnP1 A.L.O.A. by MaMe82 is a framework which turns a Rapsberry Pi Zero W into a flexible, low-cost platform for pentesting, red teaming and…
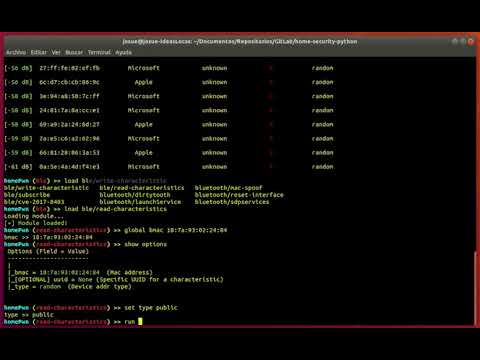 telefonica/homepwn
HomePwn - Swiss Army Knife for Pentesting of IoT Devices
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
 sgxgsx/bluetoolkit
Modular Bluetooth Classic (BR/EDR) vulnerability testing framework with reconnaissance, exploit modules for 43 public attacks/CVEs, and structured…
 fo-000/bluing
An intelligence gathering tool for hacking Bluetooth
 cosmic-zip/witchcraft
WITCHCRAFT is a cyberdeck toolkit built for runners who dive deep into the mesh. It’s your all-in-one rig for data-ghosting, ICE-breaking, and…
 penthertz/cve-2025-36911-exploit
Exploit of the CVE-2025-36911 vulnerability in Python for testing our own equipment
 ojasookert/cve-2017-0785
Blueborne CVE-2017-0785 Android information leak vulnerability
 zalexdev/wpair-app
WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…
 alwentiu/covidsafe-cve-2020-12856
A bluetooth-related vulnerability in some contact tracing apps
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025
 mjancek/bluebornedetection
Simple detection tool for Blueborne vulnerability found on Android devices --- CVE-2017-0781.
 ravss/bluetooth-crash-cve-2017-0785
Exploit script for CVE-2017-0785 that crashes the Bluetooth module on Android 4.0+ devices by sending crafted SDP search requests, causing…
 aymankhalfatni/cve-2017-0785
CVE-2017-0785: BlueBorne PoC
 cipher-attack/chimera
Payload injector and HID emulator for Android like Hak5 and rubber ducky
 librepods-org/librepods
AirPods liberated from Apple's ecosystem.