
AndroidAuto
 mretallack/androidauto
Open-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…
android-securitybluetooth-securityeducation+4
1
mretallack/androidautoOpen-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…
 antoinet/obike
Reverse engineering of the oBike protocol communication (BLE and HTTP)
 adrihd/shiningappmask-reverseengineering
Reverse Engineering of the Shining App Mask
 librepods-org/librepods
AirPods liberated from Apple's ecosystem.
 permissionlesstech/bitchat-android
Decentralized, encrypted peer-to-peer messaging app over Bluetooth mesh networks. No internet, servers, or phone numbers required. Features X25519 +…
 yjeanrenaud/yj_nearbyglasses
attempting to detect smart glasses nearby and warn you
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 fo-000/bluing
An intelligence gathering tool for hacking Bluetooth
 ojasookert/cve-2017-0785
Blueborne CVE-2017-0785 Android information leak vulnerability
 zalexdev/wpair-app
WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…
 sysnets/atfuzzer
Grammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…
 ojasookert/cve-2017-0781
Blueborne CVE-2017-0781 Android heap overflow vulnerability
 leommxj/cve-2020-0022
Proof-of-concept exploit for CVE-2020-0022, targeting Android Bluetooth stack to trigger a buffer overflow via crafted L2CAP packets, causing denial…
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…
 k3vinlusec/bluefrag_cve-2020-0022
This is a RCE bluetooth vulnerability on Android 8.0 and 9.0
 alwentiu/covidsafe-cve-2020-12856
A bluetooth-related vulnerability in some contact tracing apps
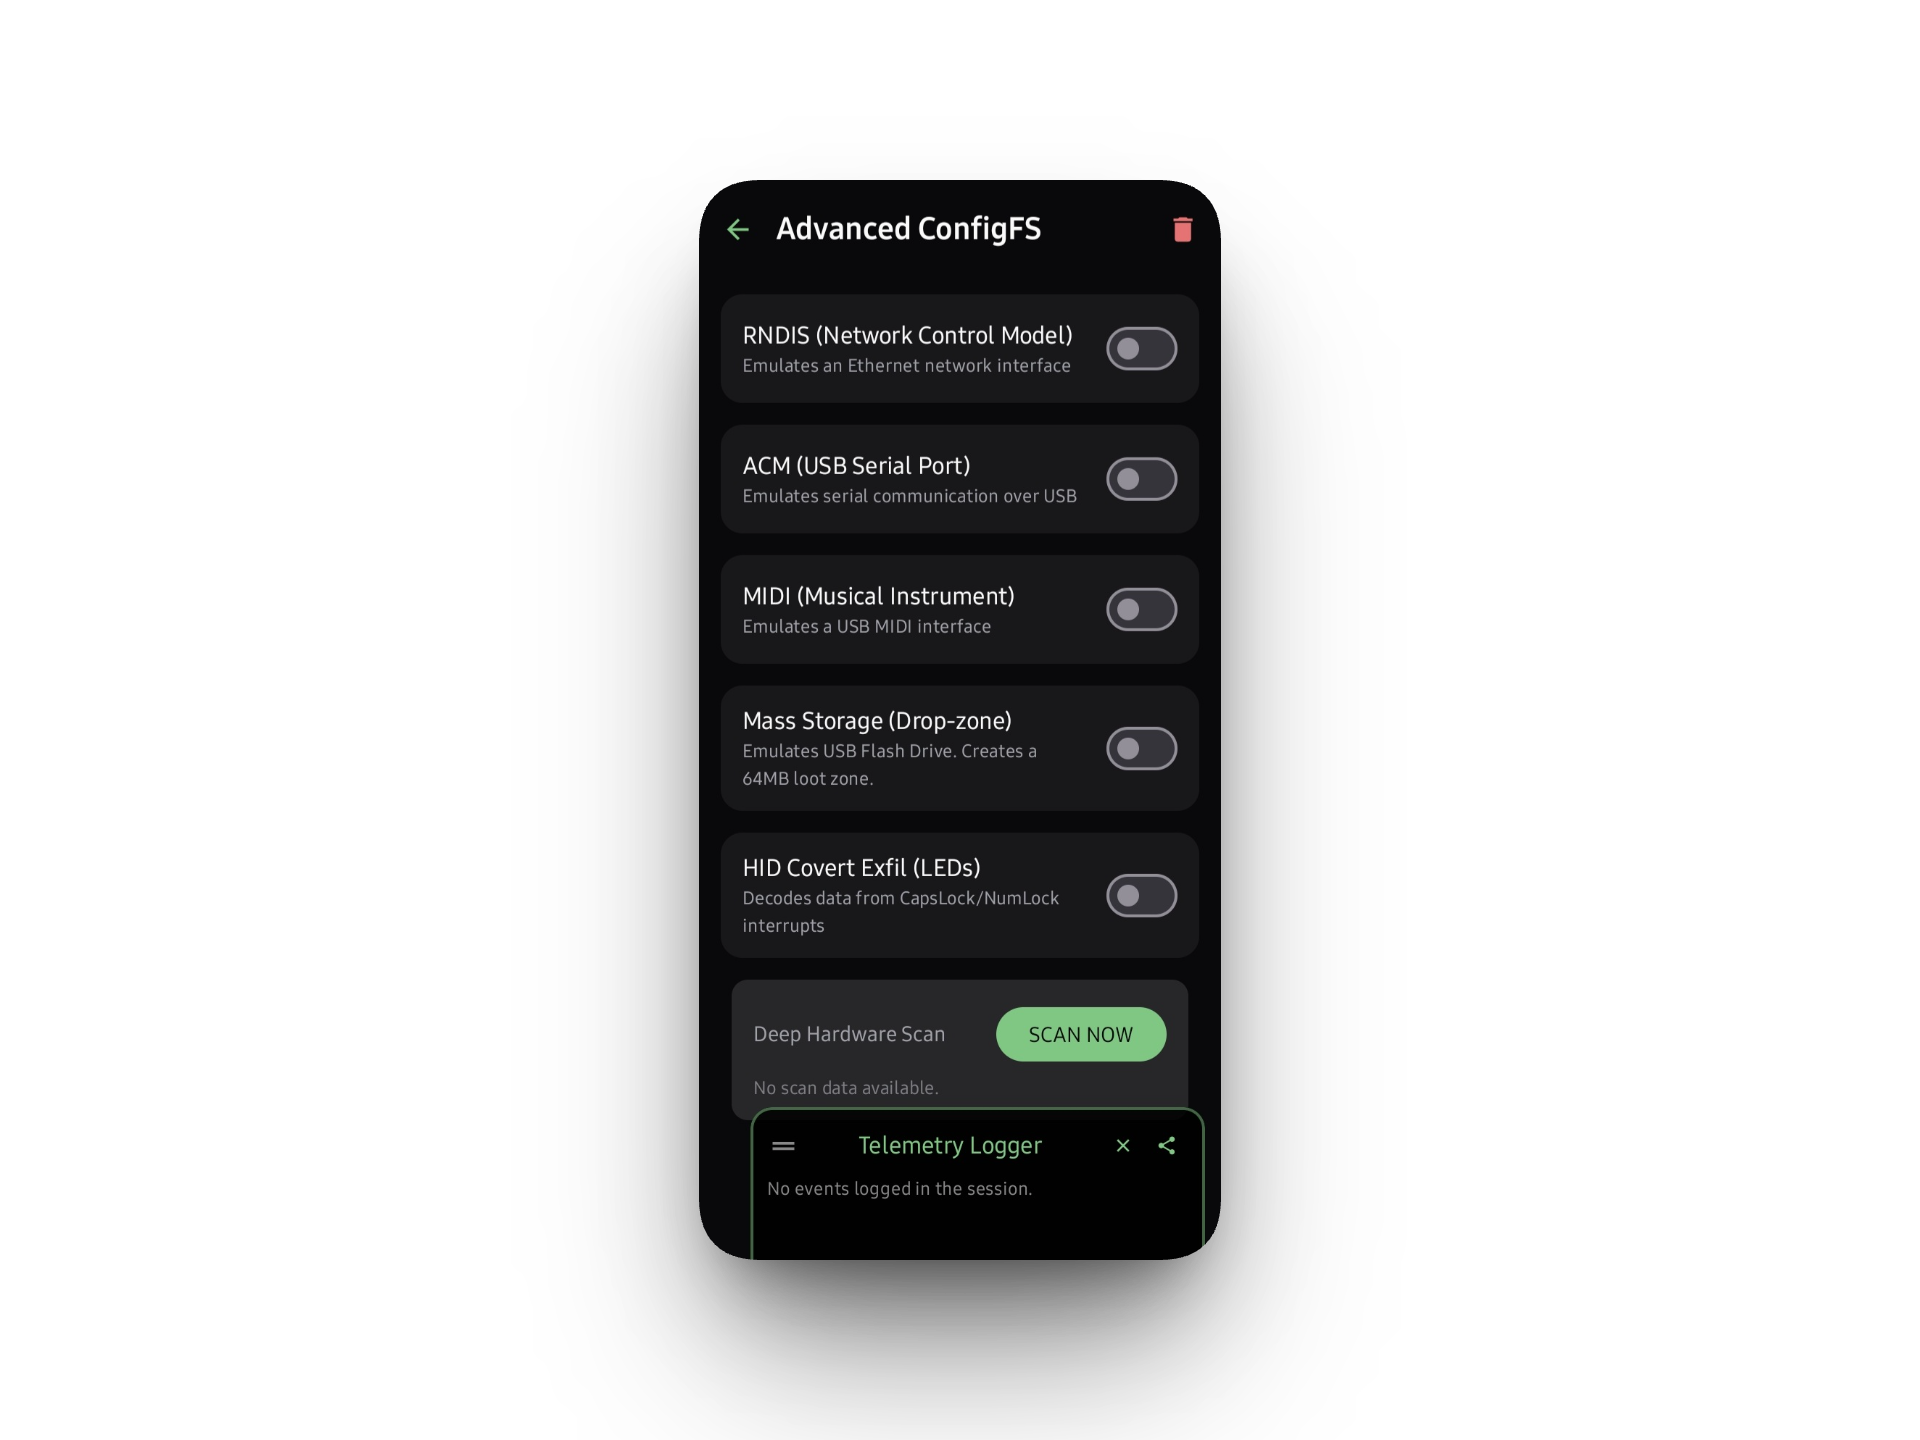 cipher-attack/chimera
Payload injector and HID emulator for Android like Hak5 and rubber ducky