
DLPwn
 gryfman/dlpwn
Red Team tool for covert file exfiltration via Bluetooth audio transmission, encoding binary data into FLAC signals to bypass EDR, XDR, and DLP…
bluetooth-securitycommand-and-controldata-exfiltration+5
25
gryfman/dlpwnRed Team tool for covert file exfiltration via Bluetooth audio transmission, encoding binary data into FLAC signals to bypass EDR, XDR, and DLP…
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
 lrh2000/cve-2023-2002
Linux Bluetooth - Run arbitrary management commands as an unprivileged user
 kevinmitchell-oswp-cissp/cve-2023-52709-poc
PoC for 2023-52709 - TI Bluetooth stack can fail to generate a resolvable Random Private Address (RPA) leading to DoS for already bonded peer devices.
 own2pwn/blueborne-cve-2017-1000251-poc
Proof-of-concept exploit for BlueBorne vulnerability CVE-2017-1000251 targeting Bluetooth stack. Demonstrates remote code execution possibility. For…
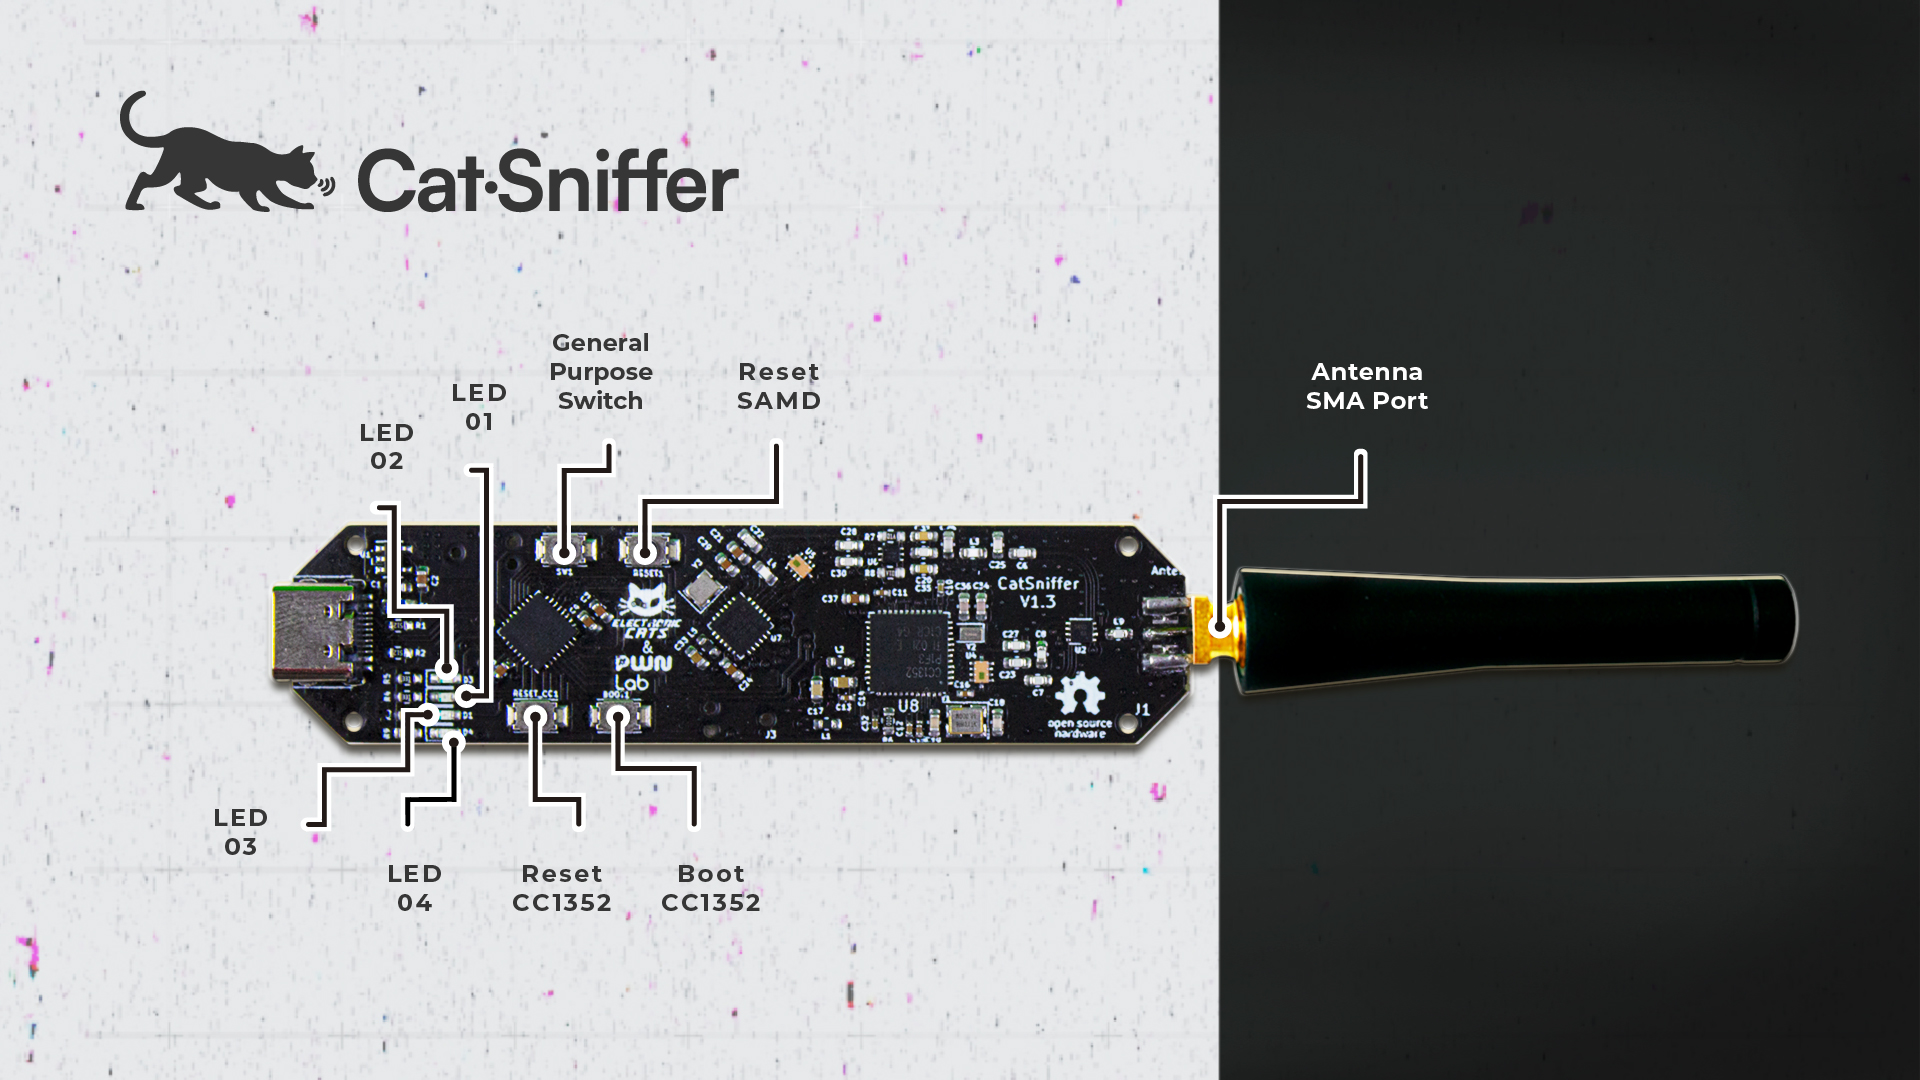 electroniccats/catsniffer
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
 pentestfunctions/blueducky
🚨 CVE-2023-45866 - BlueDucky Implementation (Using DuckyScript) 🔓 Unauthenticated Peering Leading to Code Execution (Using HID Keyboard)
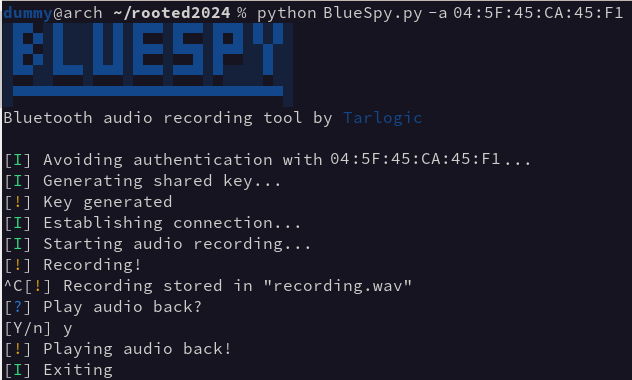 tarlogicsecurity/bluespy
PoC to record audio from a Bluetooth device
 insecurityofthings/jackit
Exploit tool for MouseJack vulnerability enabling keystroke injection and mouse hijacking over nRF24L01 wireless dongles. Supports multiple Microsoft…
 securing/gattacker
A Node.js package for BLE (Bluetooth Low Energy) security assessment using Man-in-the-Middle and other attacks
 telefonica/homepwn
HomePwn - Swiss Army Knife for Pentesting of IoT Devices
 francozappa/bluffs
Toolkit for testing Bluetooth session establishment against forward and future secrecy attacks, using firmware patching, PCAP analysis, and automated…
 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
 elevenpaths/dirtytooth-raspberrypi
Exploit the hack for IOS 11.1.2 and earlier to collect leaked information.
 scramblr/rf-chaos
RF CHAOS is an Android App That Is Designed To Cause Chaos via All RF Adapters Possible - Enjoy!
 hayzamjs/blueborne-cve-2017-1000251
Proof-of-concept exploit for Blueborne CVE-2017-1000251 enabling Bluetooth denial-of-service attacks on Linux machines via crafted L2CAP packets.
 penthertz/cve-2025-36911-exploit
Exploit of the CVE-2025-36911 vulnerability in Python for testing our own equipment
 securelayer7/pwnfb50
:unlock: transfer ownership of any FB50 smart lock to yourself (CVE-2019-13143)