
trackem
 veteranop/trackem
Passive Device Tracker (Android)TrackEm Mobile is a real-time, passive Wi-Fi + Bluetooth LE probe-request scanner designed for OSINT, red-team ops,…
bluetooth-securityinformation-gatheringiot-security+6
4
veteranop/trackemPassive Device Tracker (Android)TrackEm Mobile is a real-time, passive Wi-Fi + Bluetooth LE probe-request scanner designed for OSINT, red-team ops,…
 djsime1/awesome-flipperzero
🐬 A collection of awesome resources for the Flipper Zero device.
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 justcallmekoko/esp32marauder
A suite of WiFi/Bluetooth offensive and defensive tools for the ESP32
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 eonraider/violent-python3
Source code for the book "Violent Python" by TJ O'Connor. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…
 telefonica/homepwn
HomePwn - Swiss Army Knife for Pentesting of IoT Devices
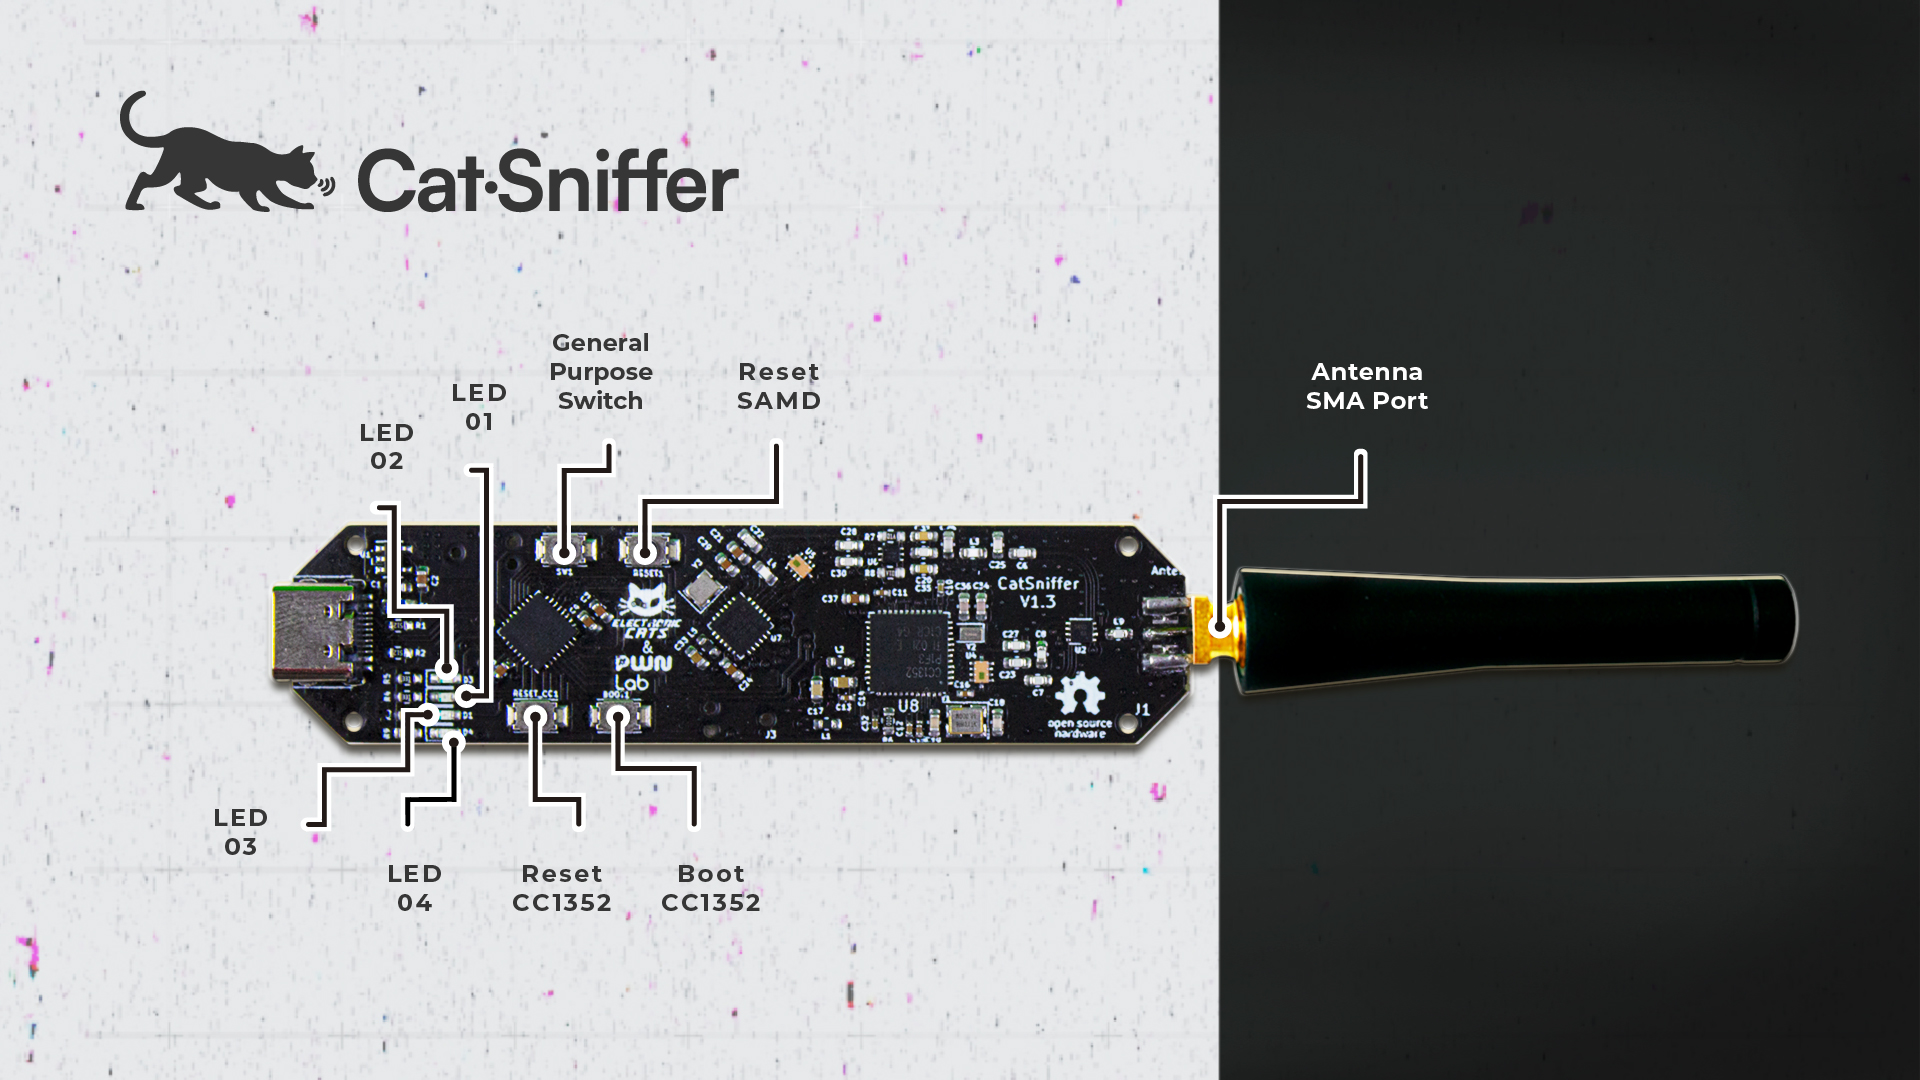 electroniccats/catsniffer
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
 zalexdev/wpair-app
WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…
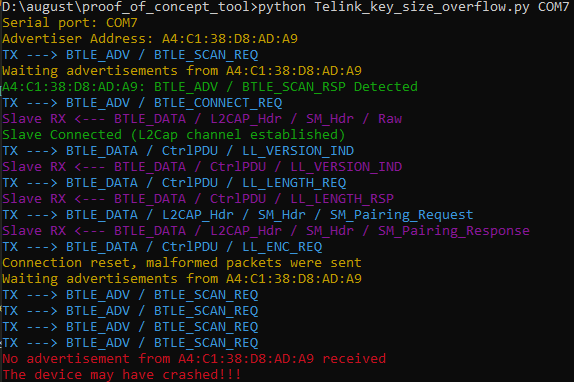 matheus-garbelini/sweyntooth_bluetooth_low_energy_attacks
Proof of Concept of Sweyntooth Bluetooth Low Energy (BLE) vulnerabilities.
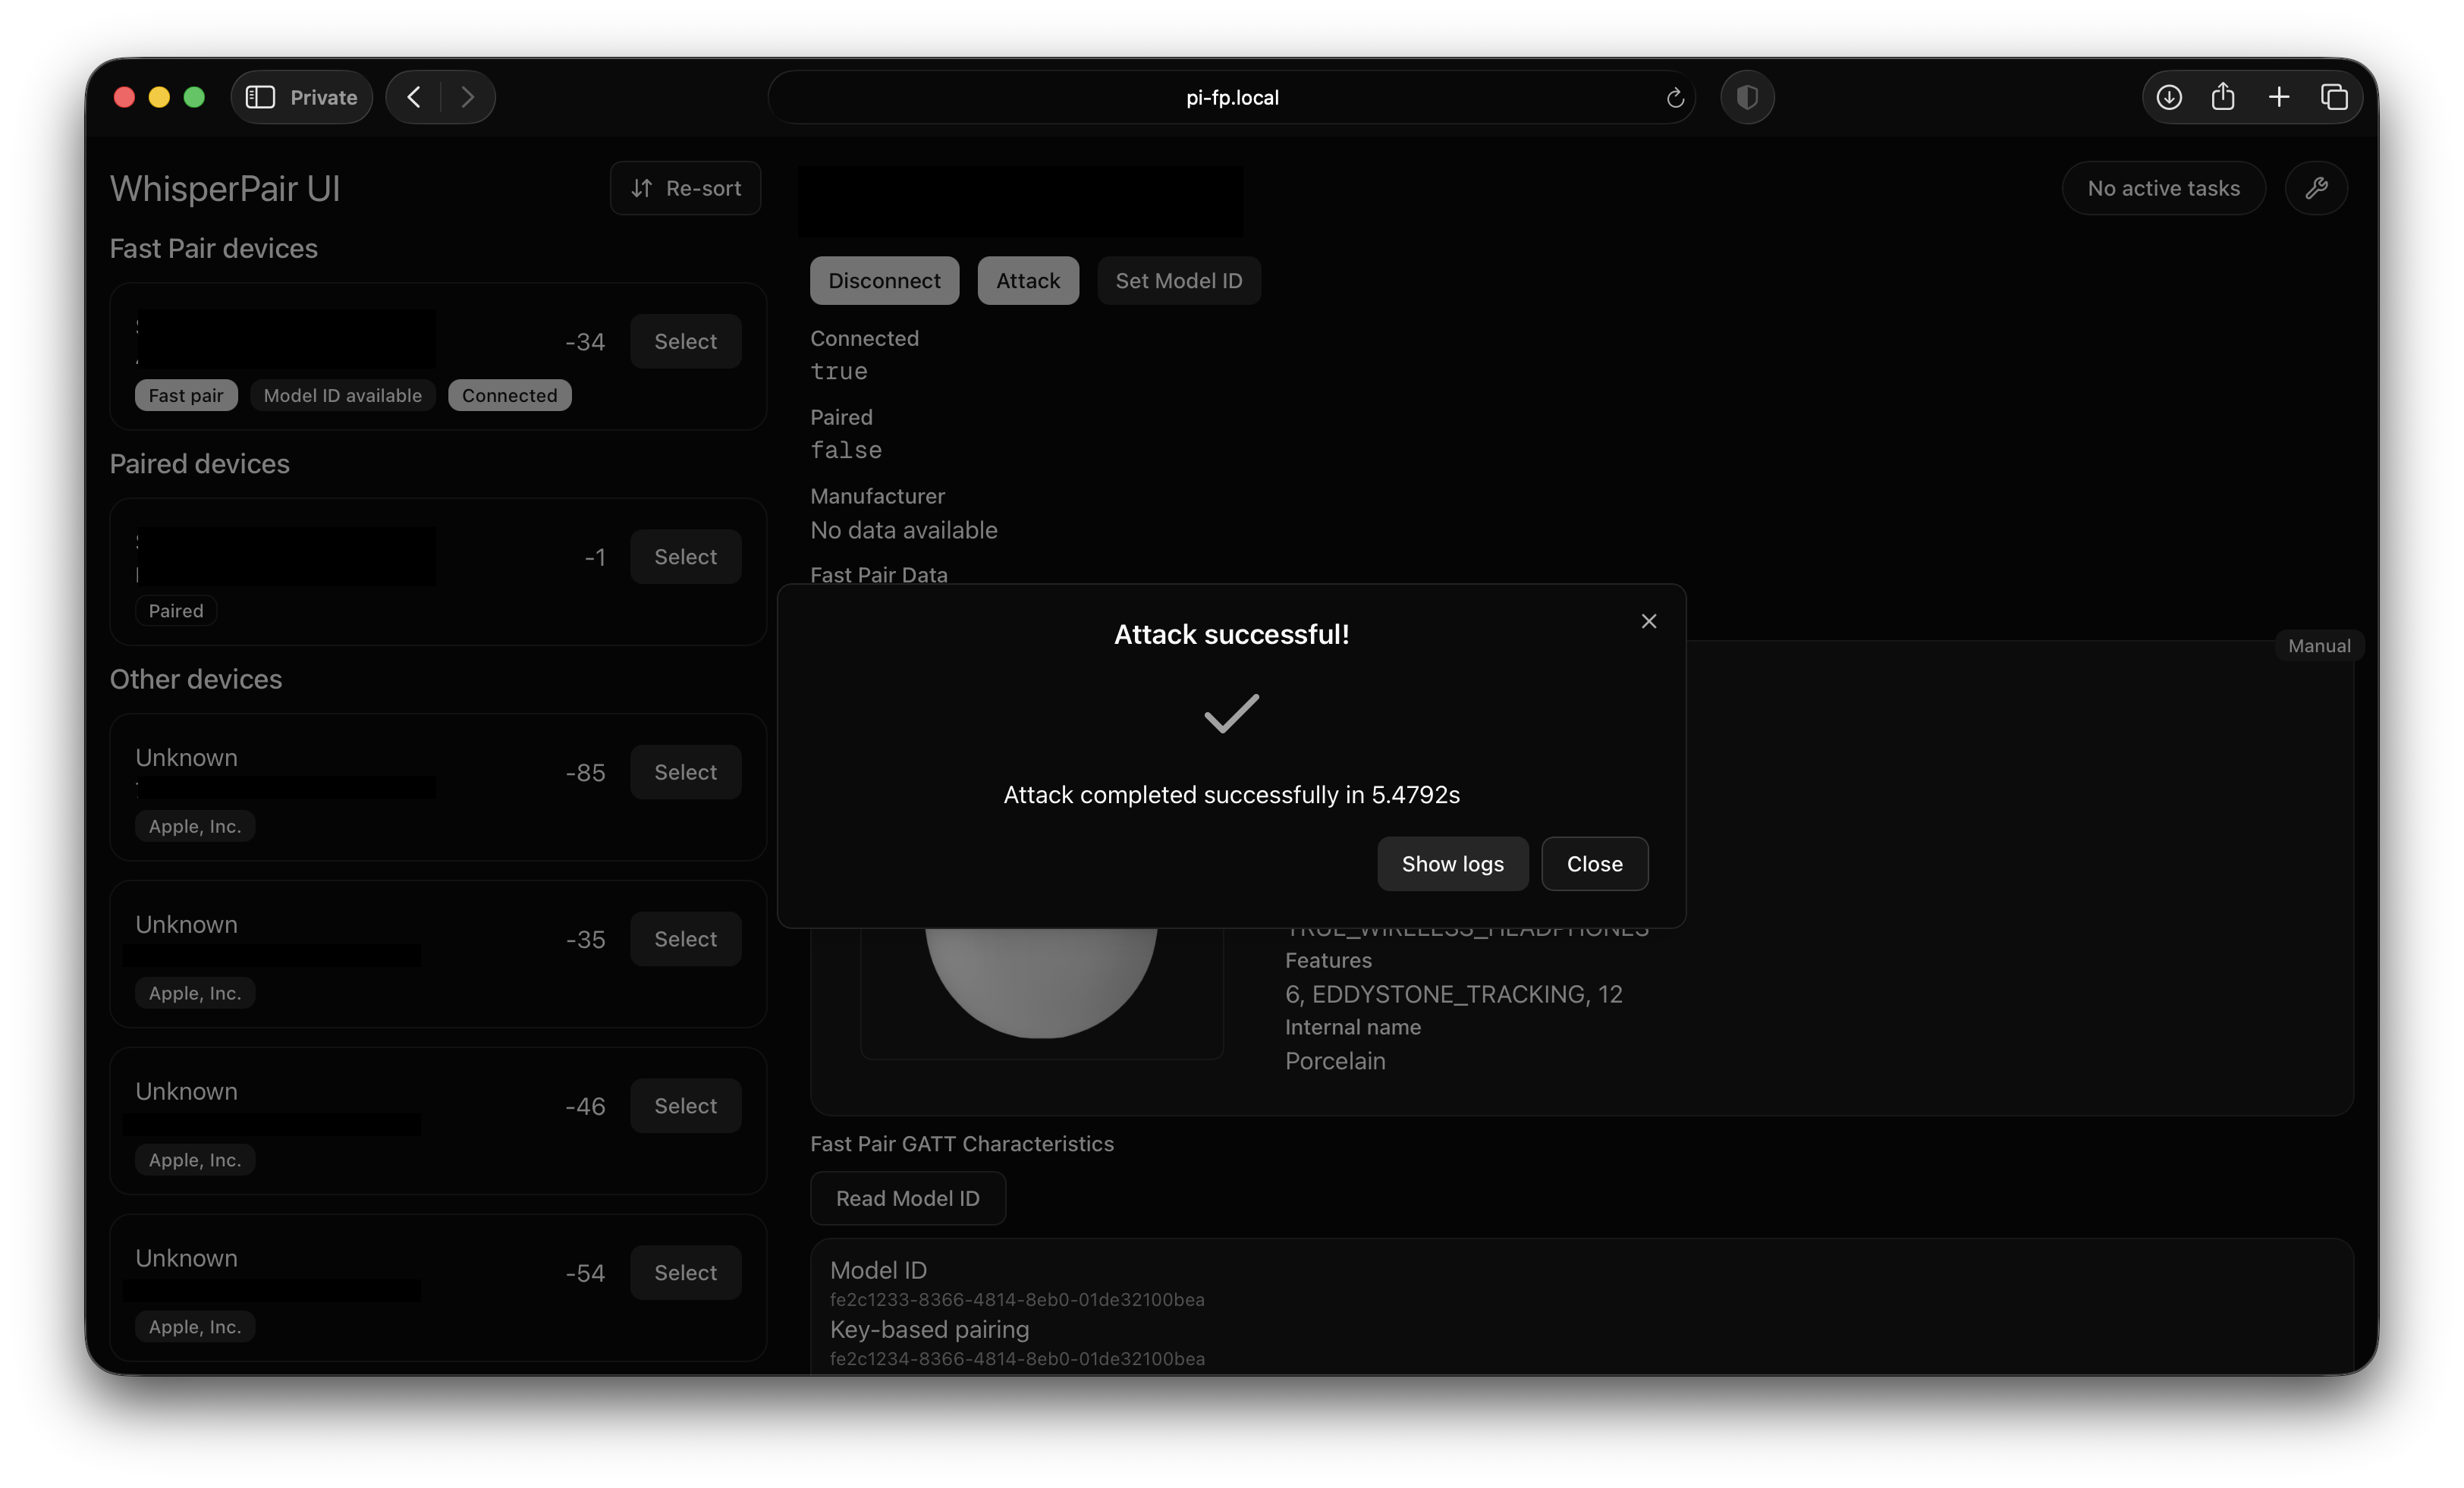 kuleuven-cosic/whisperpair
The official reference implementation & vulnerability verification of our attack WhisperPair (CVE-2025-36911) which affects Google's Fast Pair…
 francozappa/knob
Key Negotiation Of Bluetooth (KNOB) attacks on Bluetooth BR/EDR and BLE [CVE-2019-9506]
 sysnets/atfuzzer
Grammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…
 leommxj/cve-2020-0022
Proof-of-concept exploit for CVE-2020-0022, targeting Android Bluetooth stack to trigger a buffer overflow via crafted L2CAP packets, causing denial…
 antoinet/obike
Reverse engineering of the oBike protocol communication (BLE and HTTP)
 helgesverre/sony-vp-extract
Decrypt and extract voice guidance MP3 prompts from Sony WH-1000XM4 encrypted voice packs. AES key extracted via Bluetooth firmware dump of the…
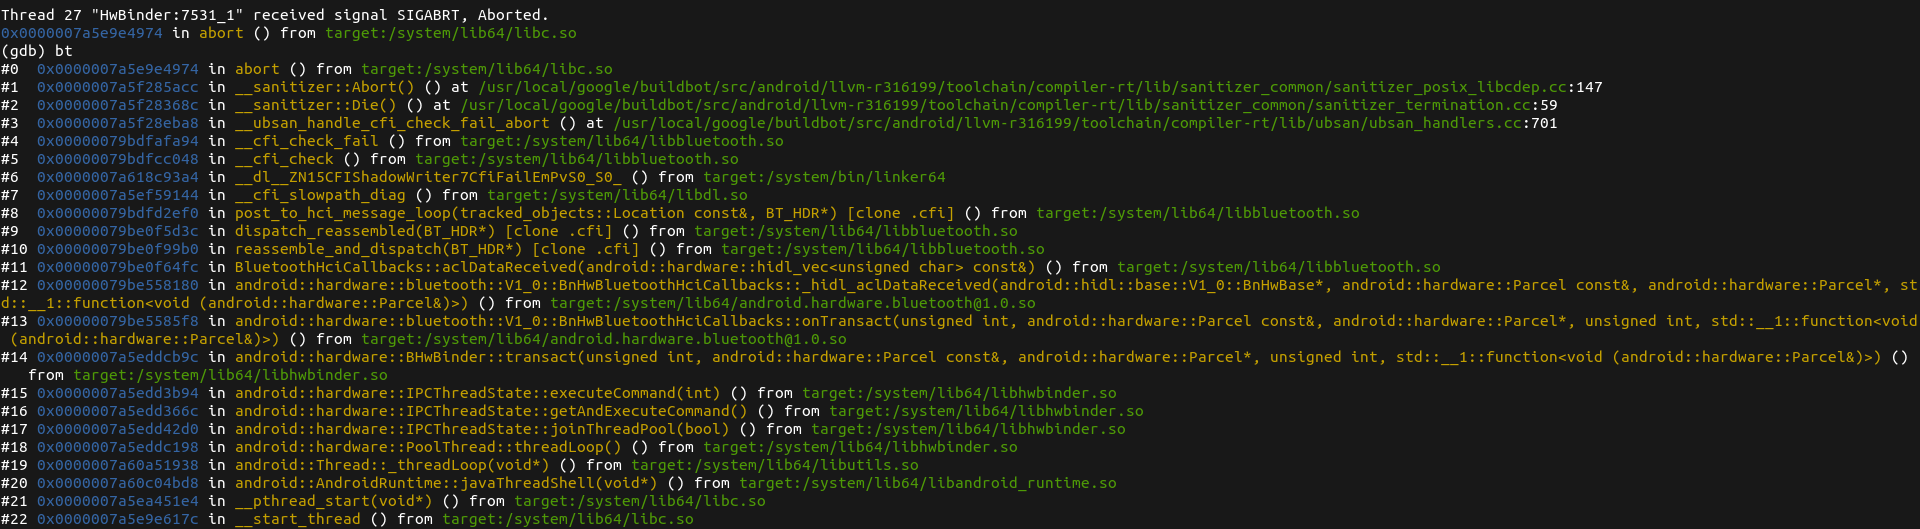 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
 penthertz/cve-2025-36911-exploit
Exploit of the CVE-2025-36911 vulnerability in Python for testing our own equipment