
BluetoothDucky
 eason-zz/bluetoothducky
Exploit implementation for CVE-2023-45866 enabling unauthenticated Bluetooth keyboard injection using DuckyScript payloads on Raspberry Pi.
bluetooth-securityexploitationhardware-iot-security+4
16
eason-zz/bluetoothduckyExploit implementation for CVE-2023-45866 enabling unauthenticated Bluetooth keyboard injection using DuckyScript payloads on Raspberry Pi.
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025
 phuchaudeveloper/badblue
CVE-2024-21306 BadBlue implementation (Using DuckyScript)
 xen0bit/fwbt
Proof of Concept code for interaction with Firewalla via Bluetooth Low-Energy and exploitation of CVE-2024-40892 / CVE-2024-40893
 m4rm0k/cve-2020-10135-bias
CVE 2020-10135 a.k.a BIAS (Bluetooth Impersonation Attack)
 zalexdev/wpair-app
WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…
 spectrixdev/diy_whisperpair
Hijacking Bluetooth Accessories Using Google Fast Pair: WhisperPair CVE-2025-36911 Reference Implementation & Vulnerability Verification Toolkit
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 zhuowei/blueshrimp
Proof-of-concept for CVE-2025-48593
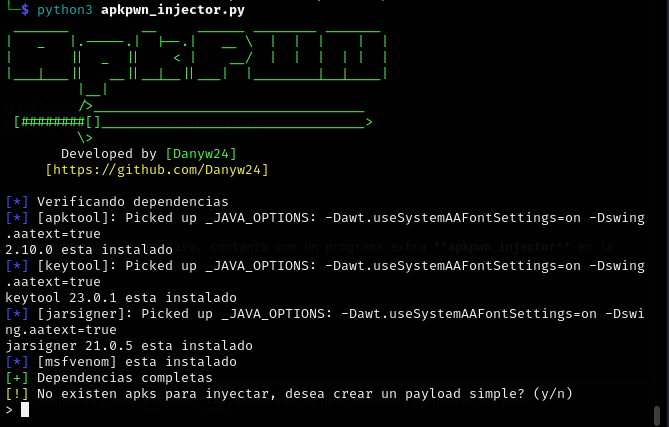 danyw24/bluexploit
Exploit basado en vulnerabilidades criticas Bluetooth (CVE-2023-45866, CVE-2024-21306)
 penthertz/cve-2025-36911-exploit
Exploit of the CVE-2025-36911 vulnerability in Python for testing our own equipment
 pivotchip/frostedfastpair
WhisperPair (CVE-2025-36911) POC for ESP32 device
 olivierlaflamme/unibleed
Unitree G1 RCE PoC & Scripts (CVE-2026-76639 / CVE-2026-76640) technical details at boschko.ca/g1-ble-rce/
 ynwarcs/cve-2023-23388
poc for CVE-2023-23388 (LPE in Windows 10/11 bthserv service)
 keldnorman/cve-2024-0230-blue
Helper script to POC of CVE-2024-0230 Bluetooth
 davidrxchester/smart-sketcher-upload
Exploits Bluetooth authentication bypass on smART Sketcher 2.0 toy projector, allowing unauthenticated connection and image upload via Python scripts.
 naren-jayram/linux-heap-based-type-confusion-in-l2cap
CVE-2020-12351
 nicholas-howland/cve-2026-6992-poc
Vulnerability proof of concept reworked from https://github.com/utmost3/cve/issues/2 I take no credit for discovering the vulnerability. This is for…