
-CVE-2017-0785-BlueBorne-PoC
 alfa100001/-cve-2017-0785-blueborne-poc
CVE-2017-0785 BlueBorne PoC
bluetooth-securityexploitationinformation-gathering+4
40
alfa100001/-cve-2017-0785-blueborne-pocCVE-2017-0785 BlueBorne PoC
 saimanish1/logitech-ipc-protocol
Reverse-engineered Logi Options+ agent IPC protocol. Switch Logitech multi-host devices programmatically via Unix socket (macOS) or named pipe…
 ynwarcs/cve-2023-23388
poc for CVE-2023-23388 (LPE in Windows 10/11 bthserv service)
 gmh5225/cve-2023-21739
Windows Bluetooth Driver Elevation of Privilege Vulnerability. CVE project by @Sn0wAlice
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 wh00hw/pyflipper
Flipper Zero Python CLI Wrapper
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 cisc0-gif/kitt
Python-Based Pentesting Framework
 flipperdevices/flipperzero-firmware
Flipper Zero firmware source code
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 earlephilhower/arduino-pico
Raspberry Pi Pico Arduino core, for all RP2040 and RP2350 boards
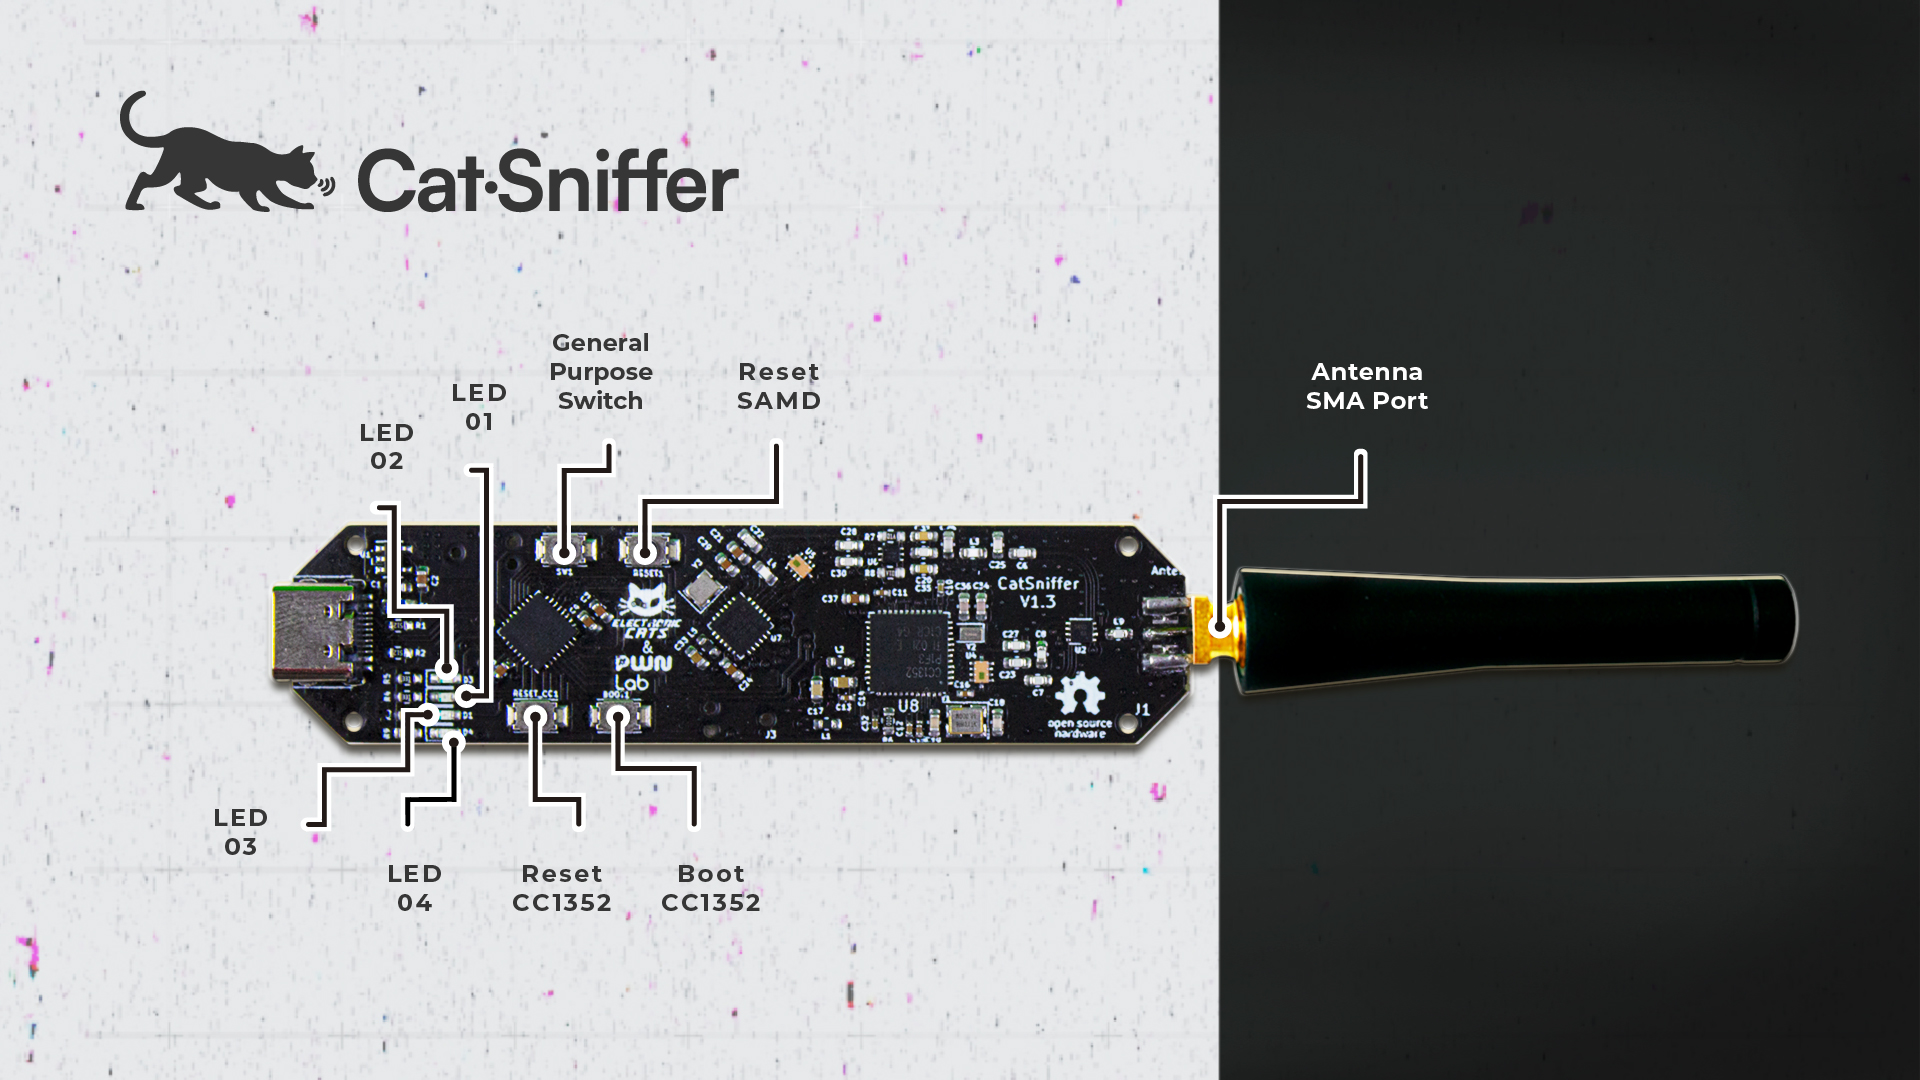 electroniccats/catsniffer
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
 0ct0sec/m5porkchop
ON NO! Someone put an RPG in a packet sniffer
 hackingdave/btrpa-scan
Bluetooth Low Energy (BLE) scanner with Resolvable Private Address (RPA) resolution using Identity Resolving Keys (IRKs)
 4shadoww/hakkuframework
Hakku Framework penetration testing
 phuchaudeveloper/badblue
CVE-2024-21306 BadBlue implementation (Using DuckyScript)