
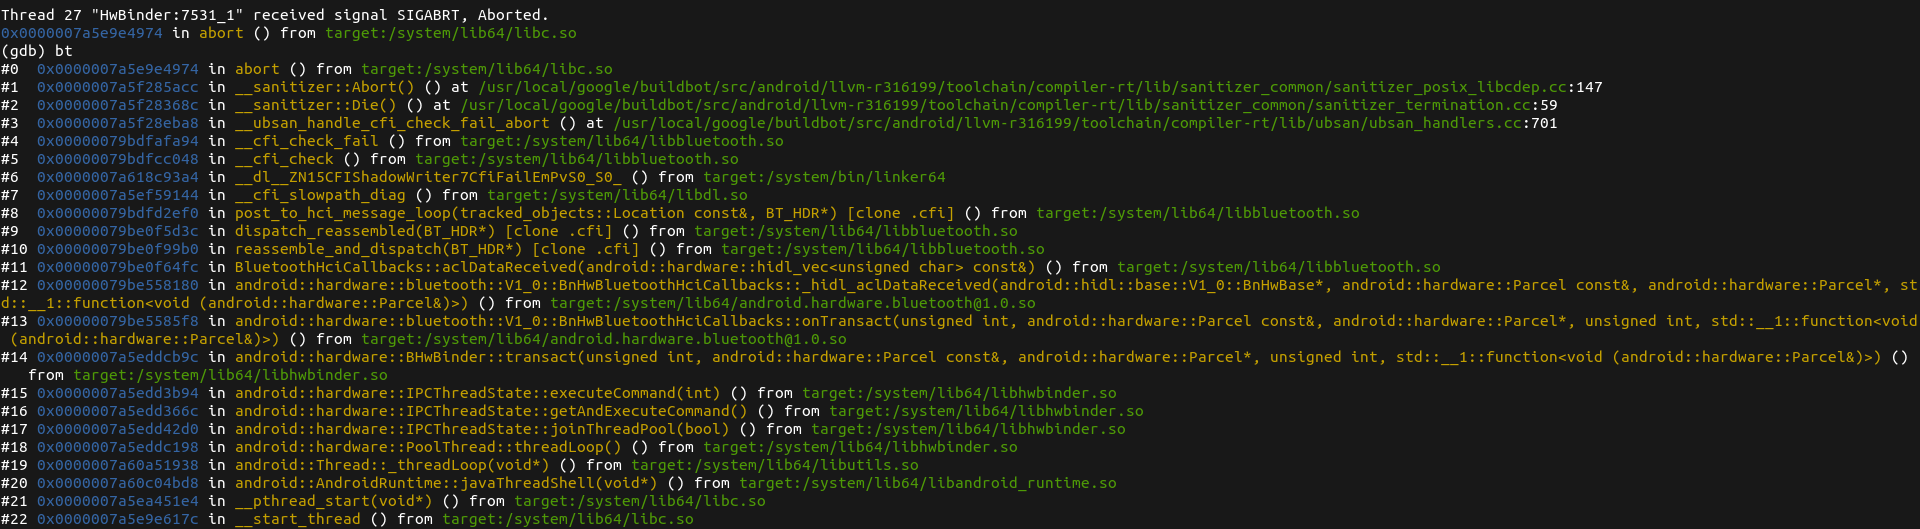
CVE-2020-0022
 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
android-securitybinary-exploitationbluetooth-security+7
22
themmokhtar/cve-2020-0022A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
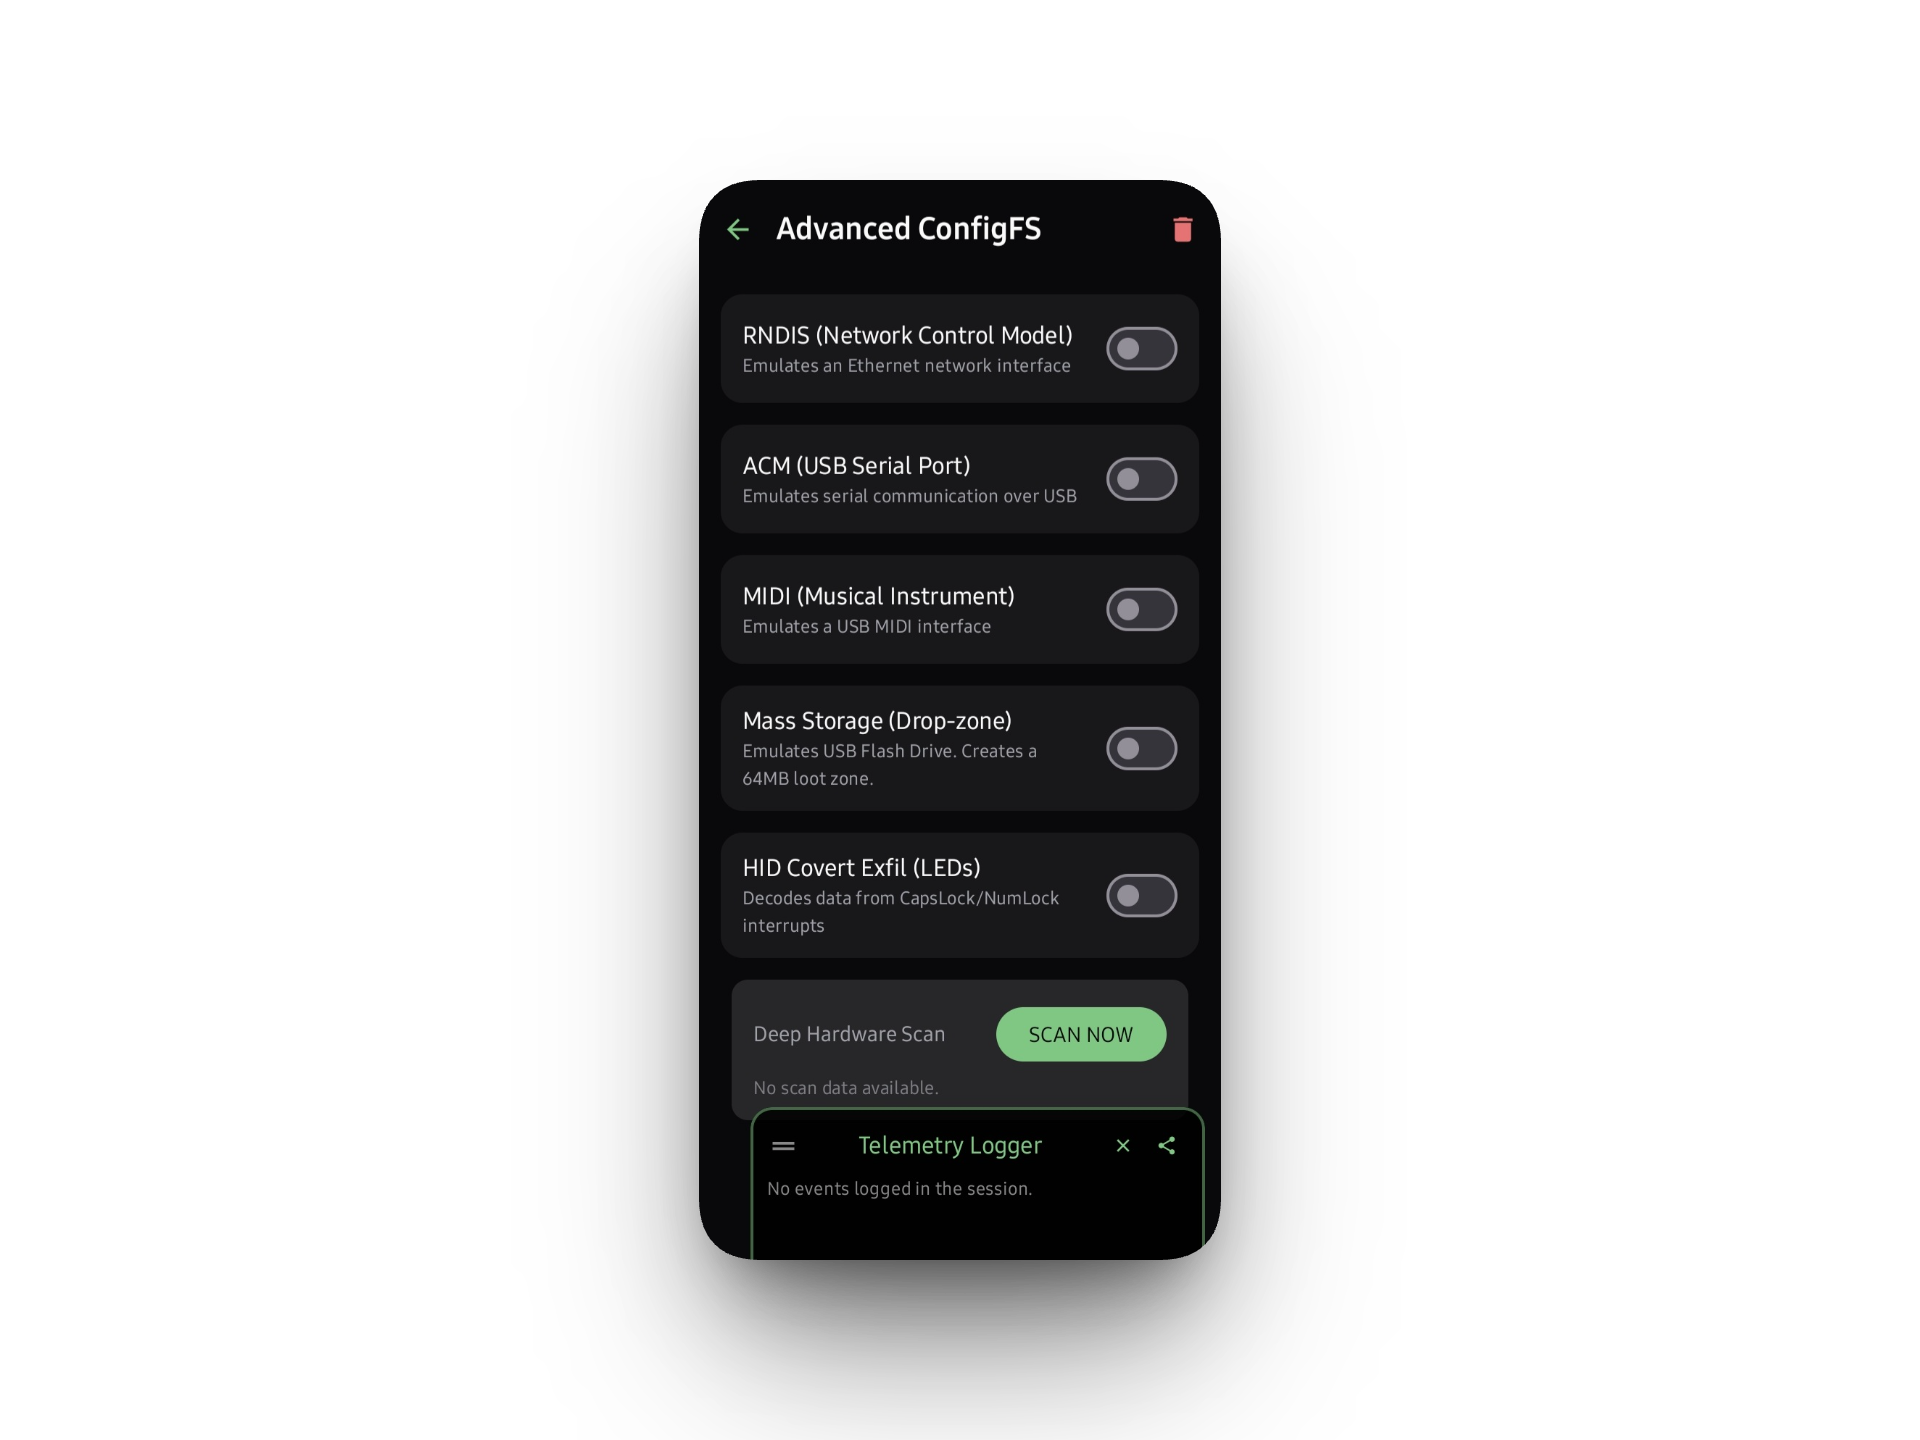 cipher-attack/chimera
Payload injector and HID emulator for Android like Hak5 and rubber ducky
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 ojasookert/cve-2017-0785
Blueborne CVE-2017-0785 Android information leak vulnerability
 sysnets/atfuzzer
Grammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…
 ojasookert/cve-2017-0781
Blueborne CVE-2017-0781 Android heap overflow vulnerability
 leommxj/cve-2020-0022
Proof-of-concept exploit for CVE-2020-0022, targeting Android Bluetooth stack to trigger a buffer overflow via crafted L2CAP packets, causing denial…
 k3vinlusec/bluefrag_cve-2020-0022
This is a RCE bluetooth vulnerability on Android 8.0 and 9.0
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 mretallack/androidauto
Open-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025
 x3ero0/android712-blueborne
Android Blueborne RCE CVE-2017-0781
 bloodcode-spasov/ble-cve2025-attack-new-version
# android-ble-cve-2025-4866 🔐 **PoC za CVE-2025-4866 — Android BLE ranjivost (javna verzija)** 📡 Iskorišćavanje slabosti u BLE autorizaciji na…
 trinadh465/packages_apps_bluetooth_aosp10_r33_cve-2022-20126
Android Bluetooth package with a patch for CVE-2022-20126, addressing a security vulnerability in AOSP 10.
 shaikusaf/system_bt_aosp10_r33_cve-2022-20229
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2022-20229, providing a vulnerable version for security research and exploit…
 satheesh575555/system_bt_aosp_10_r33_cve-2021-0316
Patched Bluetooth stack for Android 10 (AOSP r33) fixing buffer overflow vulnerability CVE-2021-0316.
 shaikusaf/packages_apps_bluetooth_aosp10_r33_cve-2021-0329
Android Bluetooth package with modifications addressing CVE-2021-0329, a critical remote code execution vulnerability in Bluetooth. Provides patched…
 mjancek/bluebornedetection
Simple detection tool for Blueborne vulnerability found on Android devices --- CVE-2017-0781.