
Learn.BlueJam
 damiansuess/learn.bluejam
Learn what is BlueJam CVE-2017-0781
bluetooth-securityctfeducation+3
damiansuess/learn.bluejamLearn what is BlueJam CVE-2017-0781
 satheesh575555/system_bt_aosp10_r33_cve-2020-0413
Android Bluetooth stack (Fluoride) source code for AOSP 10, modified for CVE-2020-0413 analysis and patching.
 nanopathi/system_bt_aosp10_r33_cve-2021-0476
Android Bluetooth stack (AOSP 10 r33) containing CVE-2021-0476 for vulnerability analysis, exploitation testing, and security research.
 nanopathi/system_bt_aosp10_r33_cve-2020-0463
Android Bluetooth stack (Fluoride) with a fix for CVE-2020-0463, enabling security analysis and exploitation testing of Bluetooth vulnerabilities on…
 shaikusaf/system_bt_aosp10_r33_cve-2020-0380
AOSP Bluetooth stack (Fluoride) with a patch for CVE-2020-0380, enabling analysis and testing of Bluetooth vulnerabilities on Android 10.
 shaikusaf/system_bt_aosp10_r33_cve-2021-0431
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0431, enabling analysis and testing of Bluetooth vulnerabilities in AOSP 10.
 satheesh575555/system_bt_aosp10_r33_cve-2020-0377
Android Bluetooth stack (Fluoride) with a patch for CVE-2020-0377, addressing a Bluetooth vulnerability in AOSP 10.
 trinadh465/system_bt_aosp10_r33_cve-2021-0589
Patched Android Bluetooth stack (AOSP10) addressing CVE-2021-0589, with build instructions for AOSP and Linux.
 devdanqtuan/poc-for-cve-2020-0022
cve-2020-0022
 nanopathi/packages_apps_bluetooth_aosp10_r33_cve-2020-0183
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 djsime1/awesome-flipperzero
🐬 A collection of awesome resources for the Flipper Zero device.
 justcallmekoko/esp32marauder
A suite of WiFi/Bluetooth offensive and defensive tools for the ESP32
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 eonraider/violent-python3
Source code for the book "Violent Python" by TJ O'Connor. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
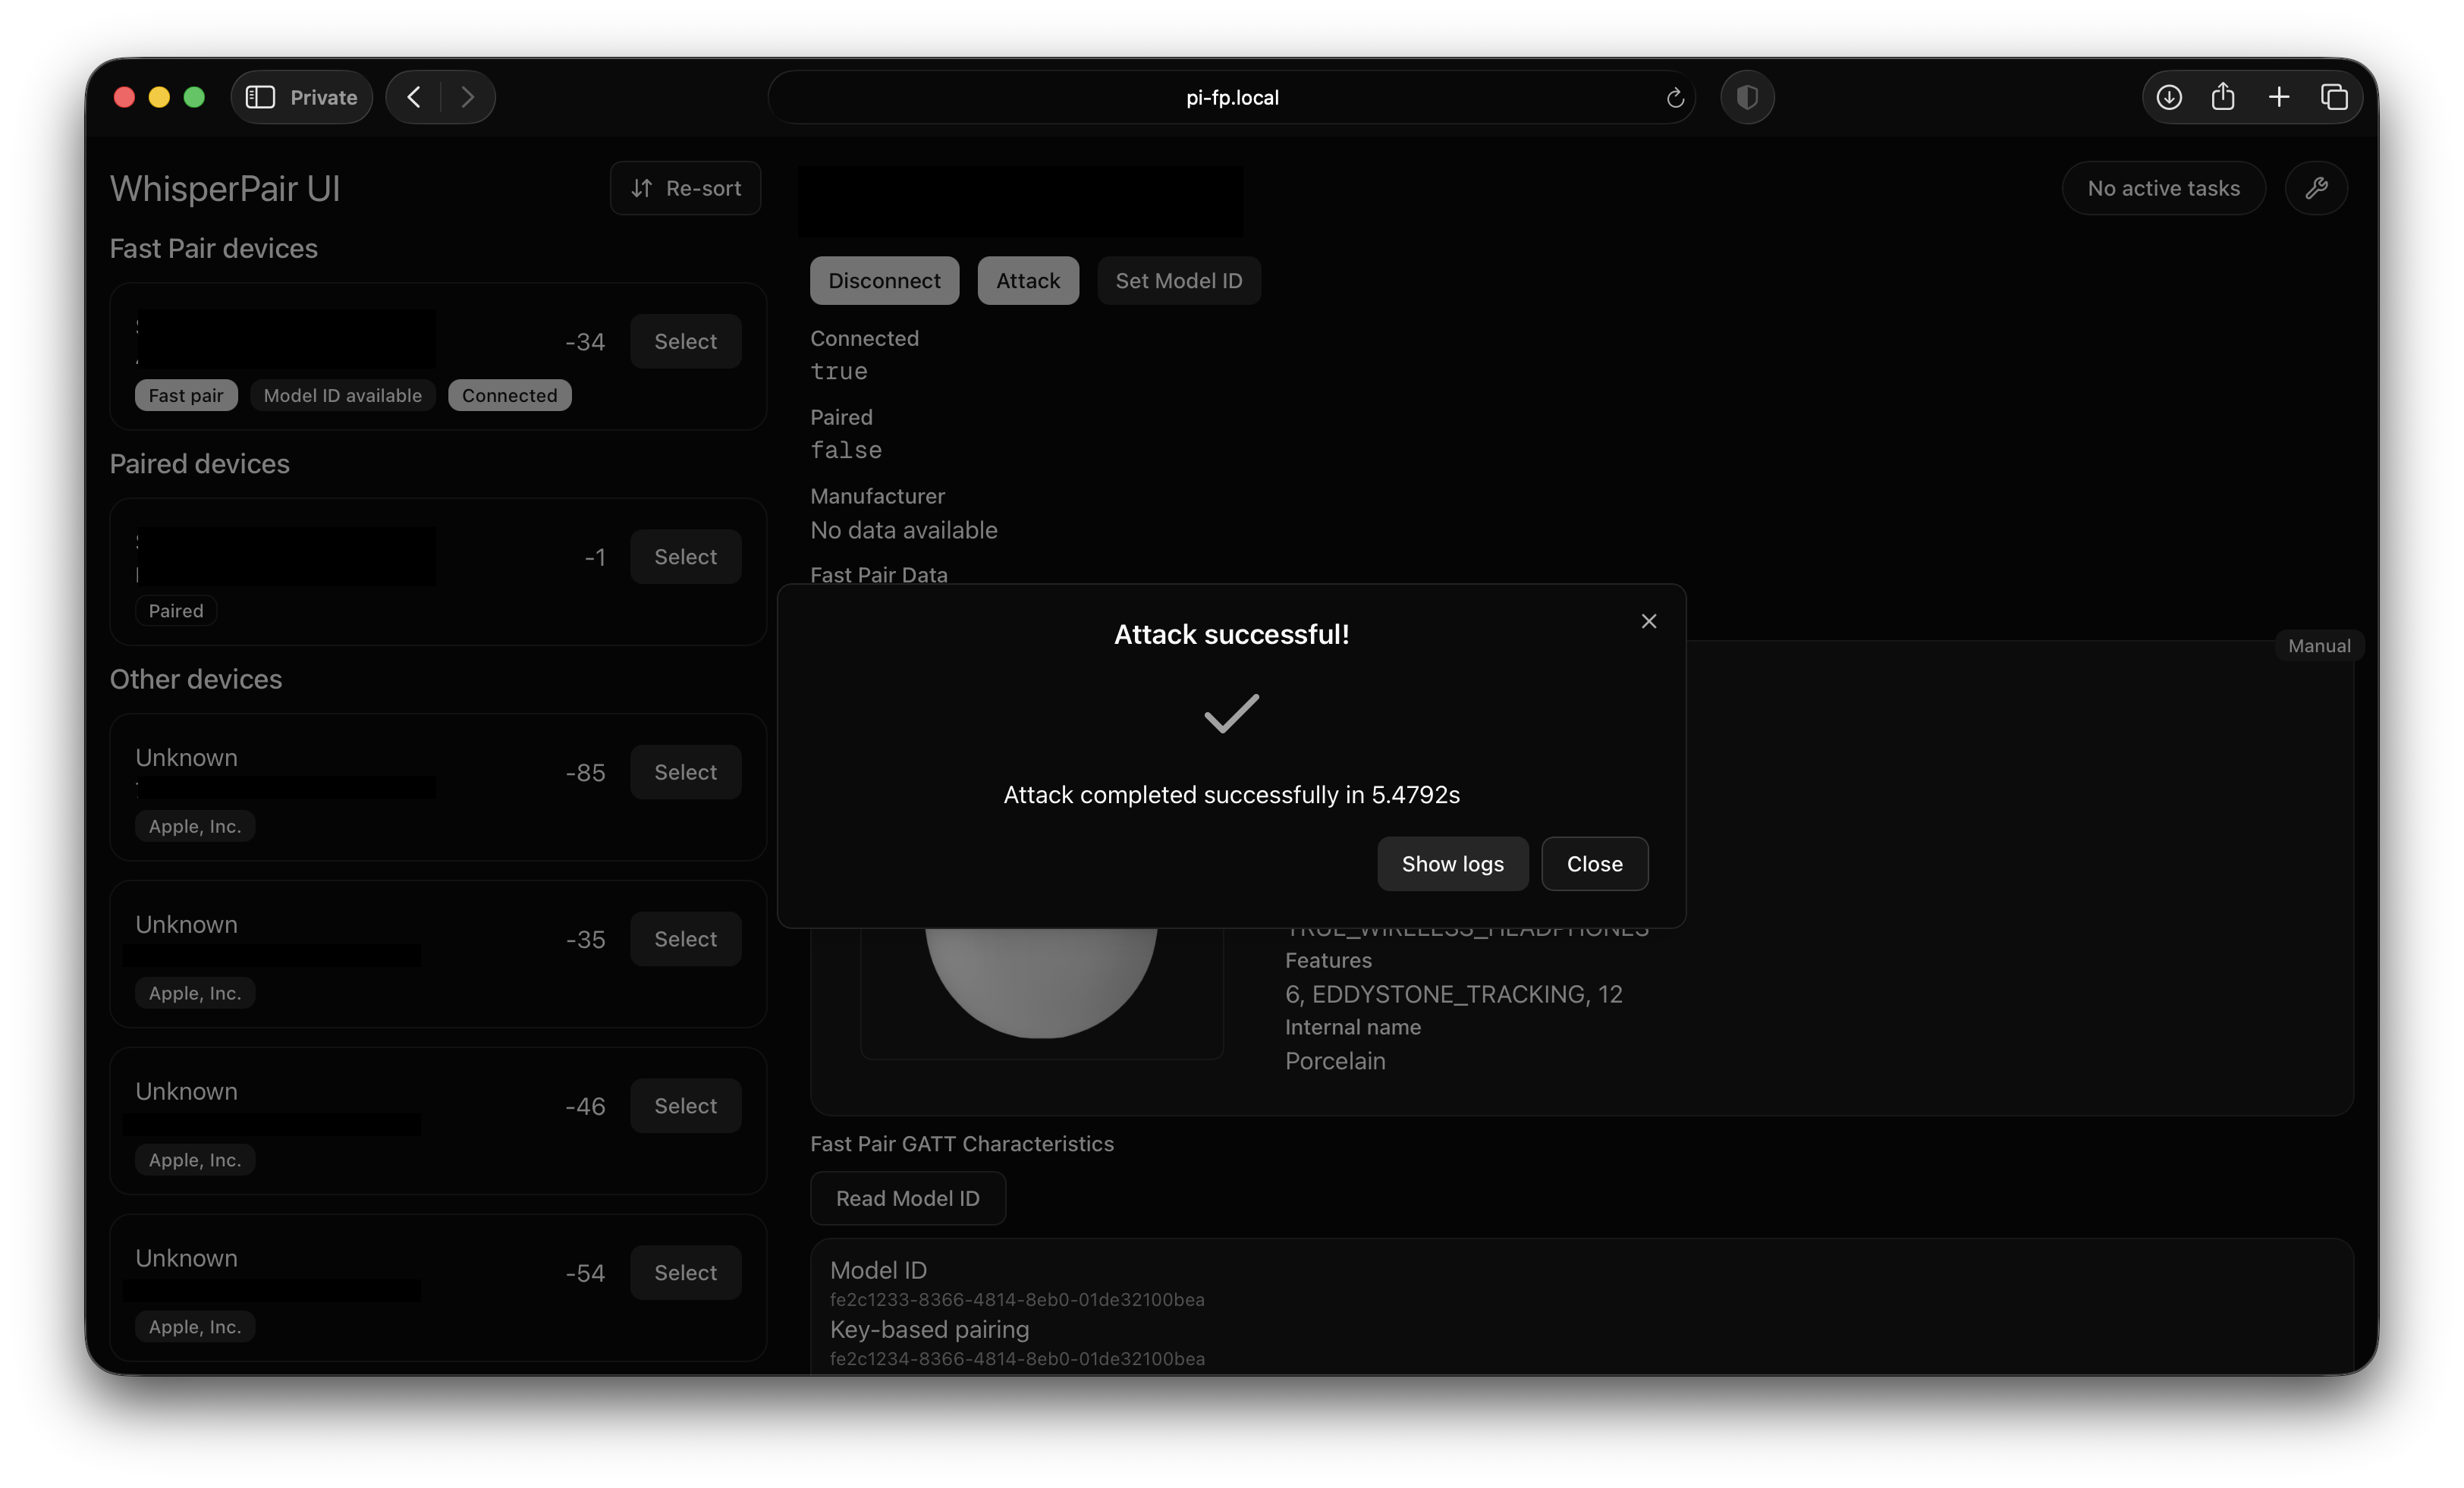 kuleuven-cosic/whisperpair
The official reference implementation & vulnerability verification of our attack WhisperPair (CVE-2025-36911) which affects Google's Fast Pair…
 antoinet/obike
Reverse engineering of the oBike protocol communication (BLE and HTTP)