
ATFuzzer
 sysnets/atfuzzer
Grammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…
android-securitybluetooth-securitydynamic-analysis-sandboxing+2
158
sysnets/atfuzzerGrammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…
 ojasookert/cve-2017-0781
Blueborne CVE-2017-0781 Android heap overflow vulnerability
 leommxj/cve-2020-0022
Proof-of-concept exploit for CVE-2020-0022, targeting Android Bluetooth stack to trigger a buffer overflow via crafted L2CAP packets, causing denial…
 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 k3vinlusec/bluefrag_cve-2020-0022
This is a RCE bluetooth vulnerability on Android 8.0 and 9.0
 zhuowei/blueshrimp
Proof-of-concept for CVE-2025-48593
 alwentiu/covidsafe-cve-2020-12856
A bluetooth-related vulnerability in some contact tracing apps
 mretallack/androidauto
Open-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…
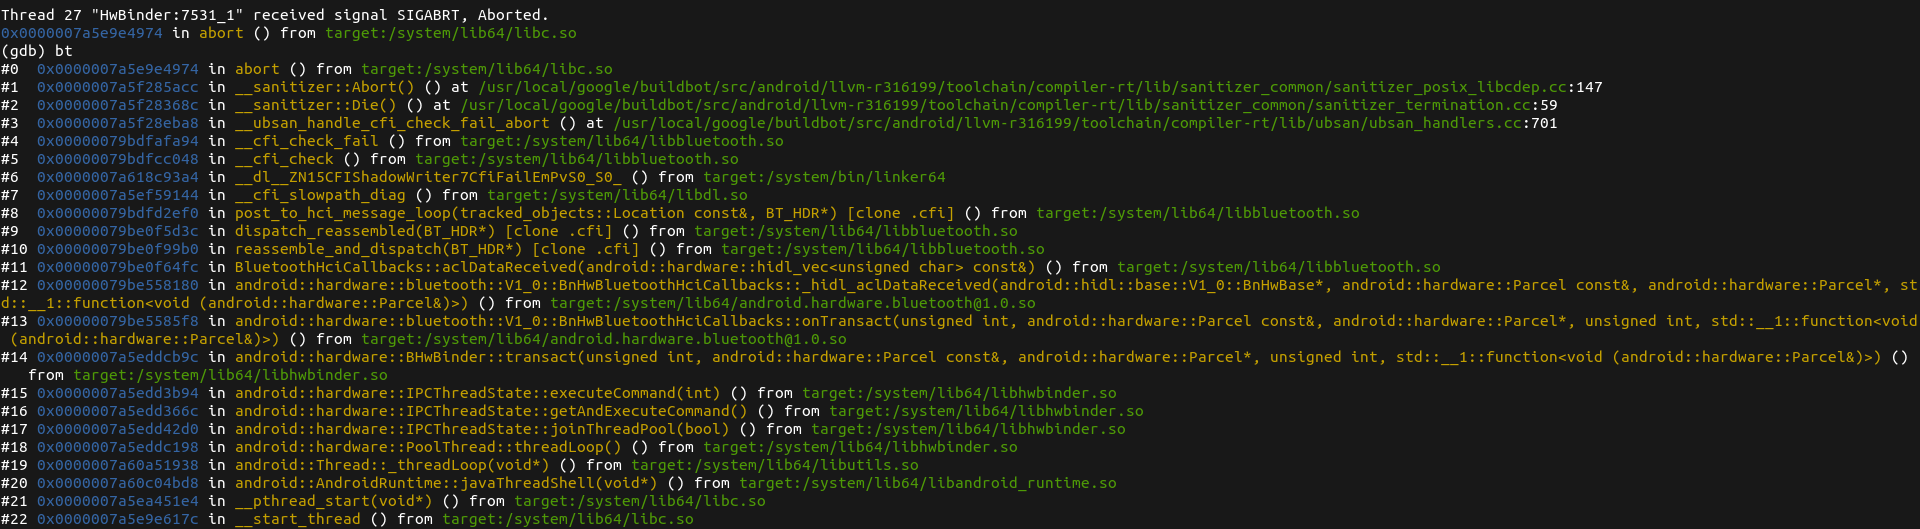 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
 irsl/lgosp-poc
LG On Screen Phone authentication bypass PoC (CVE-2014-8757)
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025
 x3ero0/android712-blueborne
Android Blueborne RCE CVE-2017-0781
 bloodcode-spasov/ble-cve2025-attack-new-version
# android-ble-cve-2025-4866 🔐 **PoC za CVE-2025-4866 — Android BLE ranjivost (javna verzija)** 📡 Iskorišćavanje slabosti u BLE autorizaciji na…
 trinadh465/packages_apps_bluetooth_aosp10_r33_cve-2022-20126
Android Bluetooth package with a patch for CVE-2022-20126, addressing a security vulnerability in AOSP 10.
 avishekdhakal/cve-2023-45866_exploits
Exploits Tested in Mi A2 Lite and Realme 2 pro
 shaikusaf/system_bt_aosp10_r33_cve-2022-20229
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2022-20229, providing a vulnerable version for security research and exploit…
 satheesh575555/system_bt_aosp_10_r33_cve-2021-0316
Patched Bluetooth stack for Android 10 (AOSP r33) fixing buffer overflow vulnerability CVE-2021-0316.