
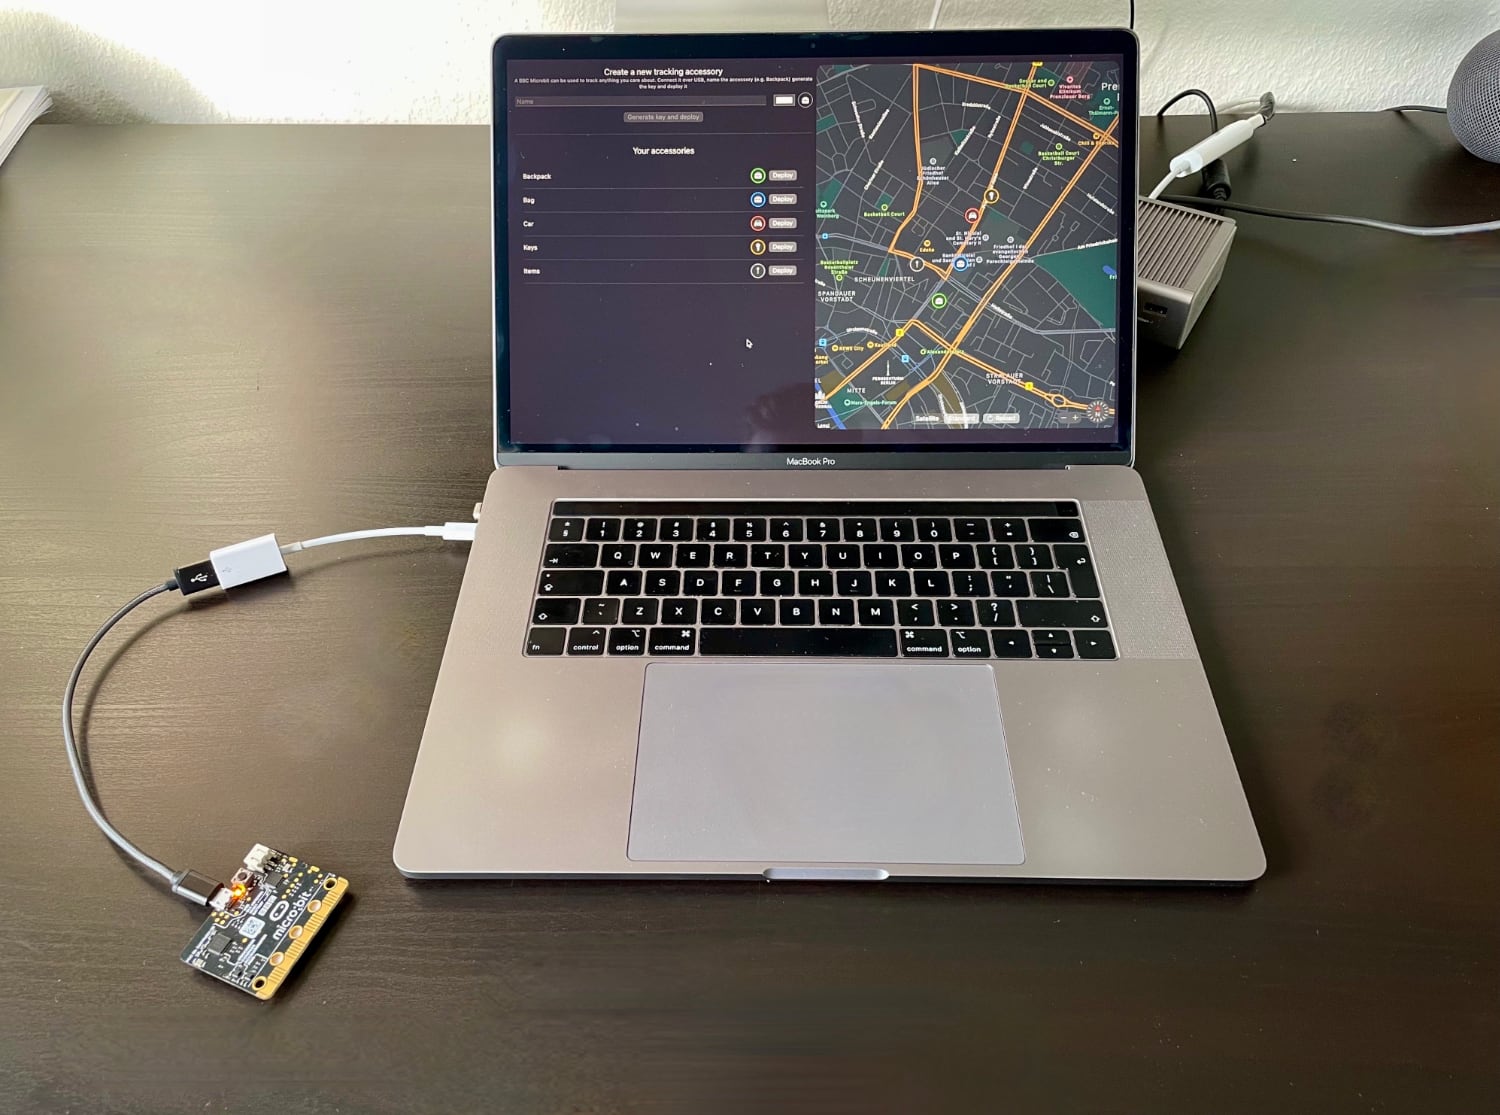
openhaystack
 seemoo-lab/openhaystack
Build your own 'AirTags' 🏷 today! Framework for tracking personal Bluetooth devices via Apple's massive Find My network.
bluetooth-securitycryptographyeducation+5
13.8k
seemoo-lab/openhaystackBuild your own 'AirTags' 🏷 today! Framework for tracking personal Bluetooth devices via Apple's massive Find My network.
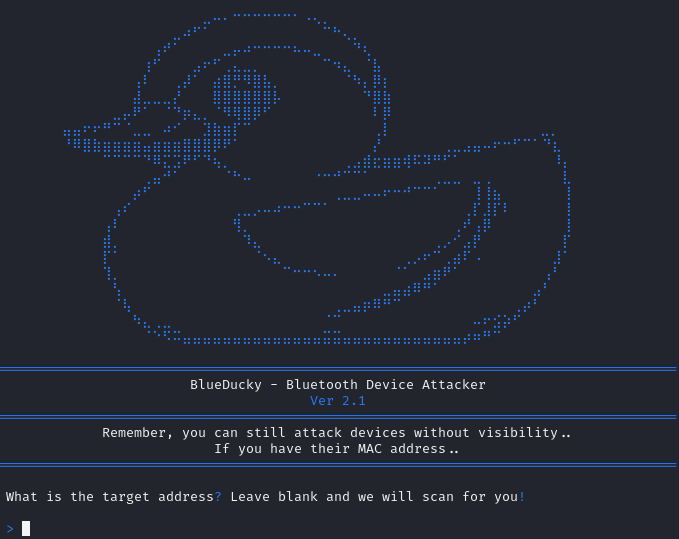 pentestfunctions/blueducky
🚨 CVE-2023-45866 - BlueDucky Implementation (Using DuckyScript) 🔓 Unauthenticated Peering Leading to Code Execution (Using HID Keyboard)
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
 0ct0sec/m5porkchop
ON NO! Someone put an RPG in a packet sniffer
 sensepost/snoopy-ng
Snoopy v2.0 - modular digital terrestrial tracking framework
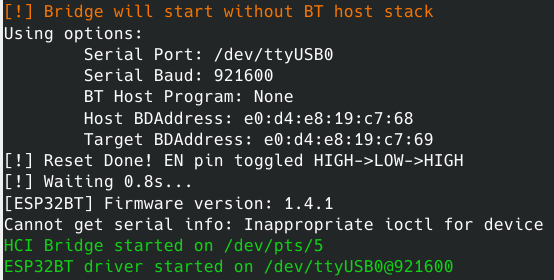 matheus-garbelini/esp32_bluetooth_classic_sniffer
Active Bluetooth BR/EDR Sniffer/Injector as cheap as any ESP32 board can get. Works with Scapy ;-)
 fo-000/bluing
An intelligence gathering tool for hacking Bluetooth
 ojasookert/cve-2017-0785
Blueborne CVE-2017-0785 Android information leak vulnerability
 wh00hw/pyflipper
Flipper Zero Python CLI Wrapper
 hackingdave/btrpa-scan
Bluetooth Low Energy (BLE) scanner with Resolvable Private Address (RPA) resolution using Identity Resolving Keys (IRKs)
 insecurityofthings/uc_mousejack
Mousejack for ATmega32u4
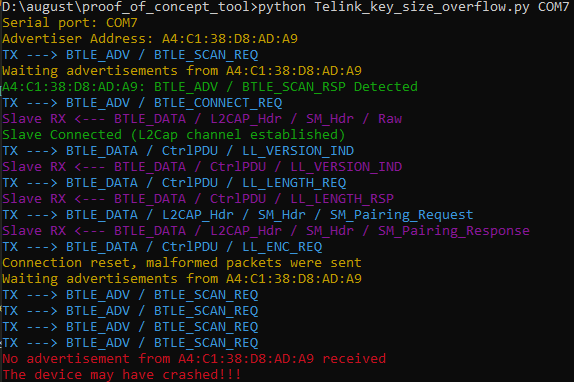 matheus-garbelini/sweyntooth_bluetooth_low_energy_attacks
Proof of Concept of Sweyntooth Bluetooth Low Energy (BLE) vulnerabilities.
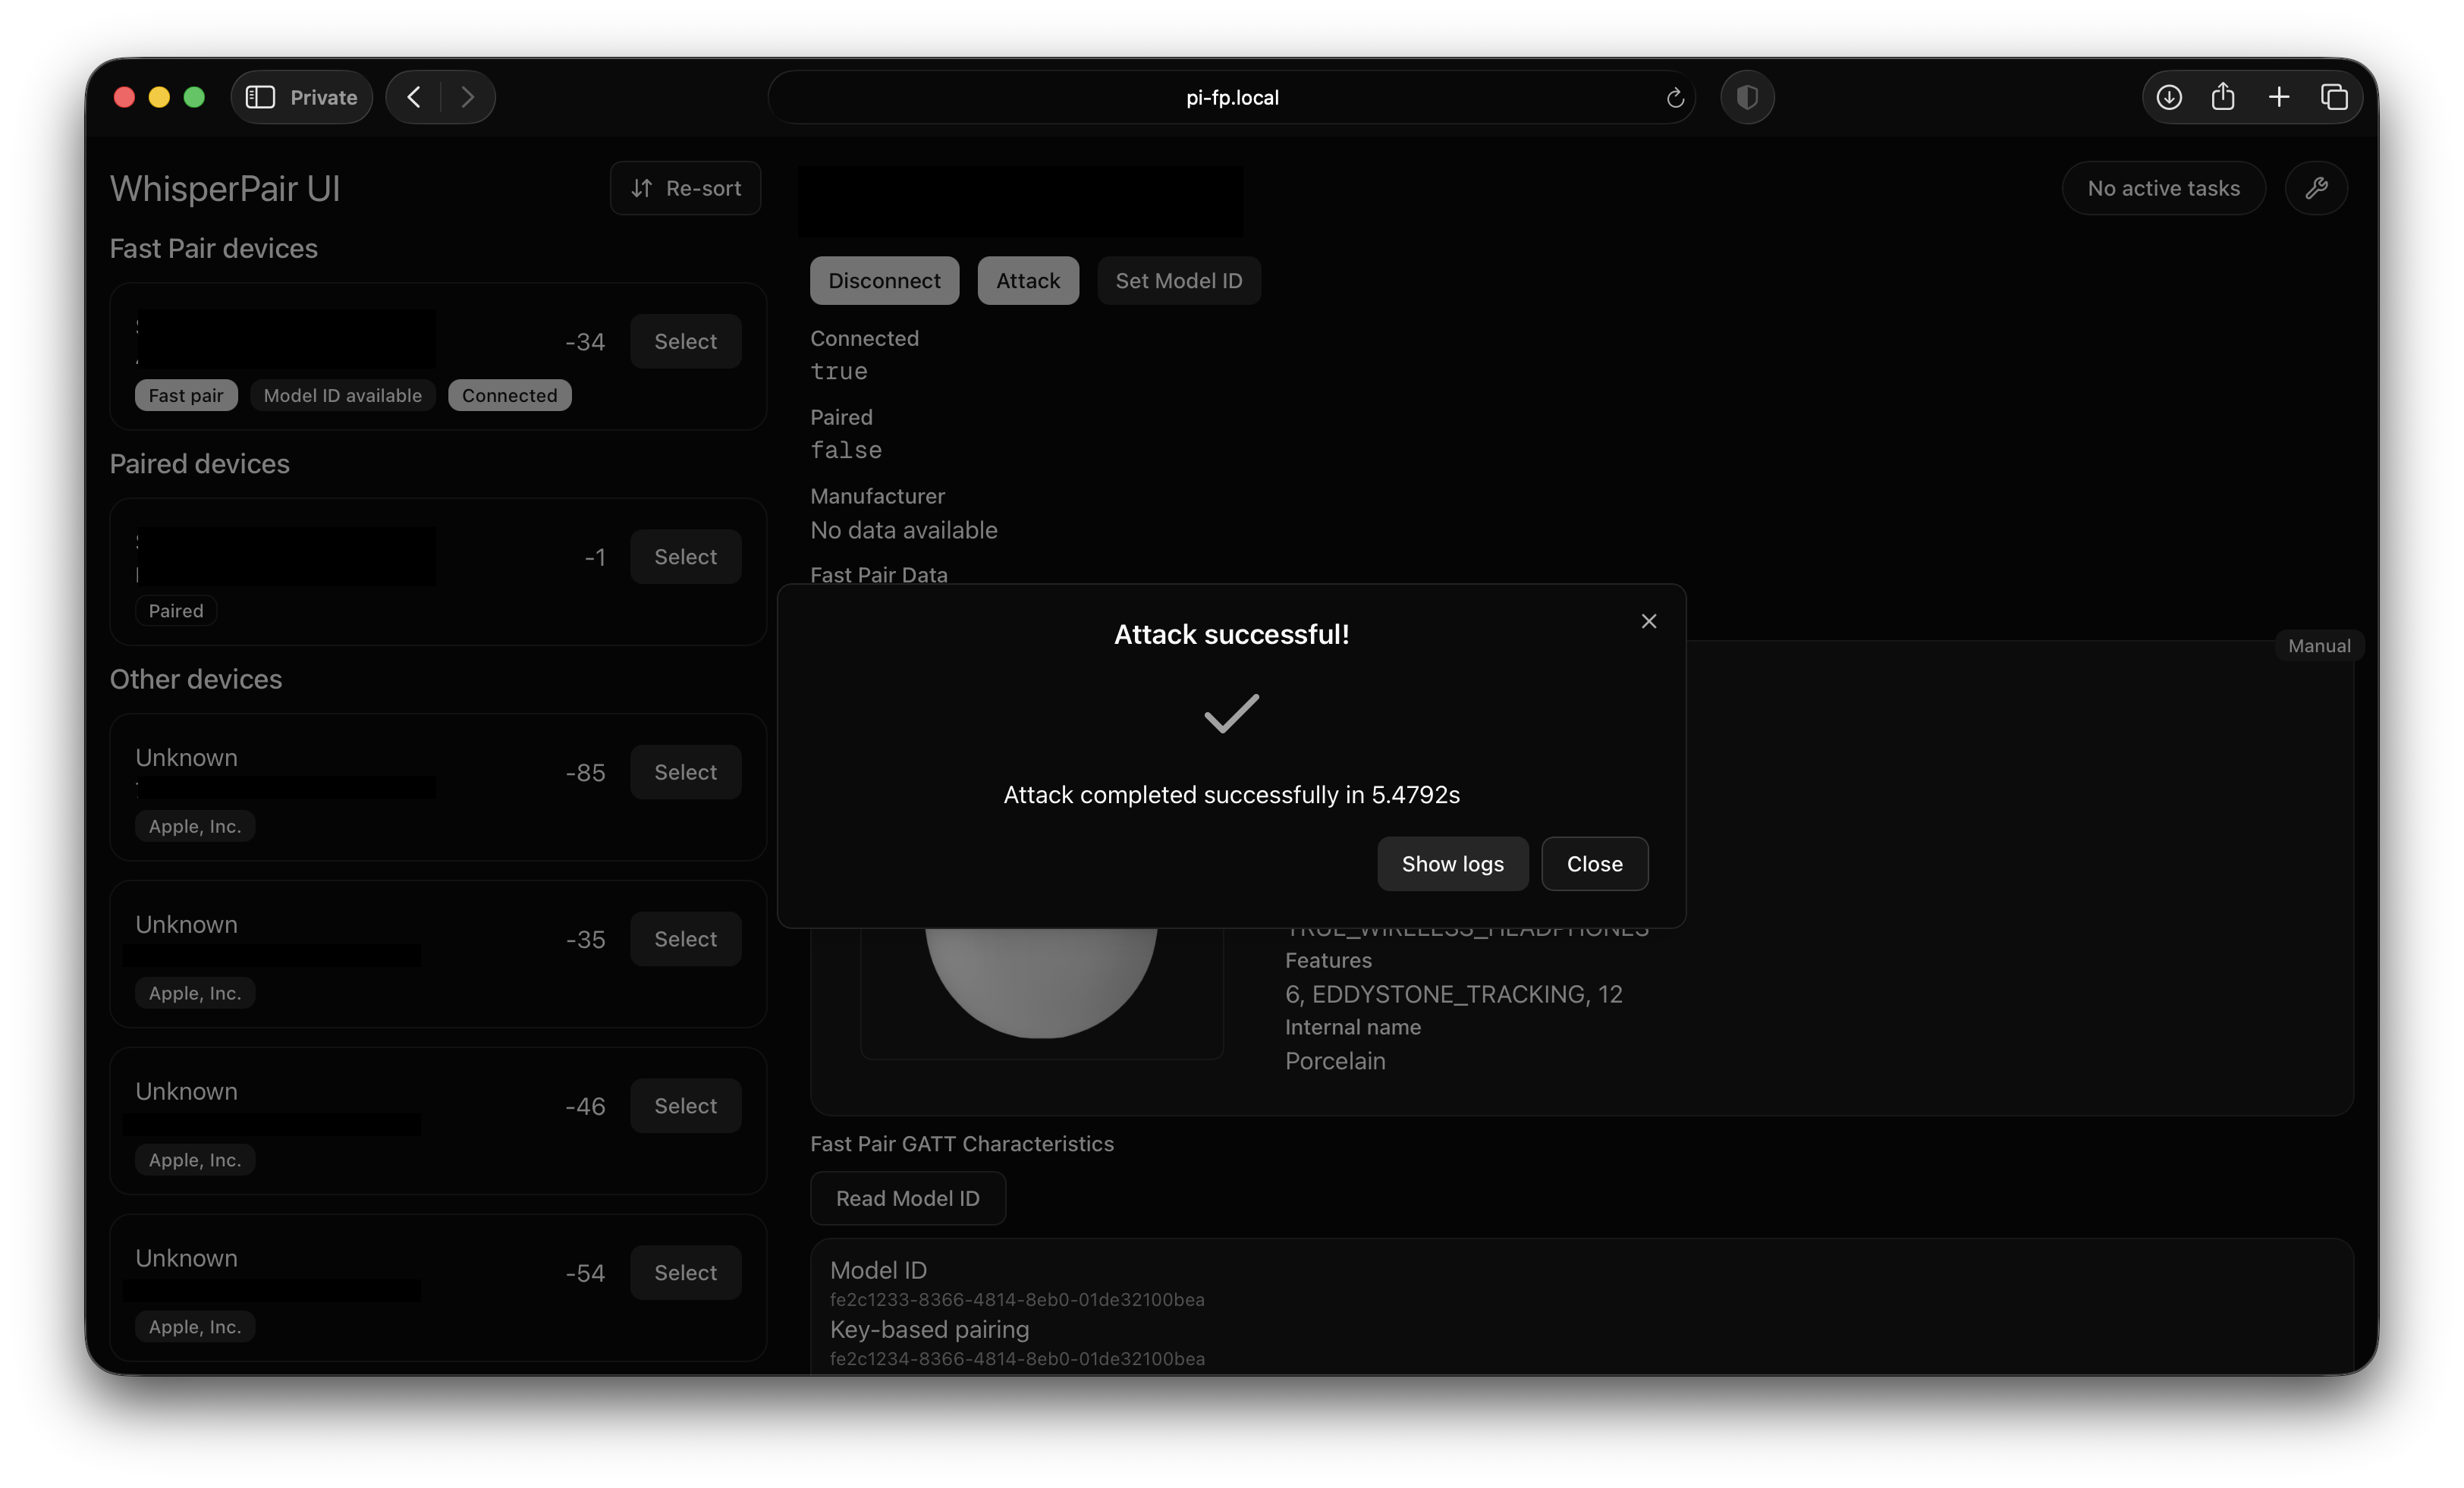 kuleuven-cosic/whisperpair
The official reference implementation & vulnerability verification of our attack WhisperPair (CVE-2025-36911) which affects Google's Fast Pair…
 ojasookert/cve-2017-0781
Blueborne CVE-2017-0781 Android heap overflow vulnerability
 nccgroup/ble-replay
BLE-Replay is a Bluetooth Low Energy (BLE) peripheral assessment tool
 spectrixdev/diy_whisperpair
Hijacking Bluetooth Accessories Using Google Fast Pair: WhisperPair CVE-2025-36911 Reference Implementation & Vulnerability Verification Toolkit
 anssi-fr/ultrablue
User-friendly Lightweight TPM Remote Attestation over Bluetooth
 leommxj/cve-2020-0022
Proof-of-concept exploit for CVE-2020-0022, targeting Android Bluetooth stack to trigger a buffer overflow via crafted L2CAP packets, causing denial…