

hakkuframework
 4shadoww/hakkuframework
Hakku Framework penetration testing
bluetooth-securityexploitationinformation-gathering+7
4shadoww/hakkuframeworkHakku Framework penetration testing
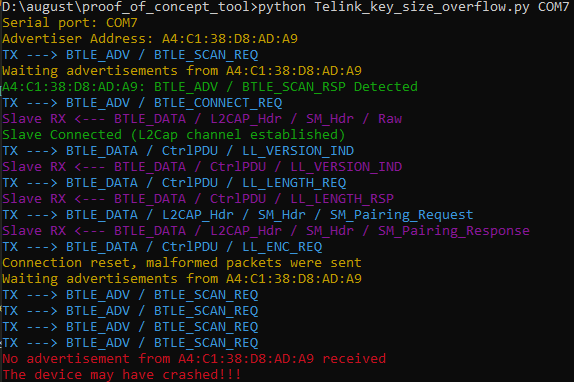 matheus-garbelini/sweyntooth_bluetooth_low_energy_attacks
Proof of Concept of Sweyntooth Bluetooth Low Energy (BLE) vulnerabilities.
 generaldussduss/poseidon
80+ feature pentesting firmware for M5Stack Cardputer-Adv. WiFi, BLE, sub-GHz (CC1101), 2.4GHz (nRF24), LoRa (SX1262), IR, BadUSB, DHCP attacks,…
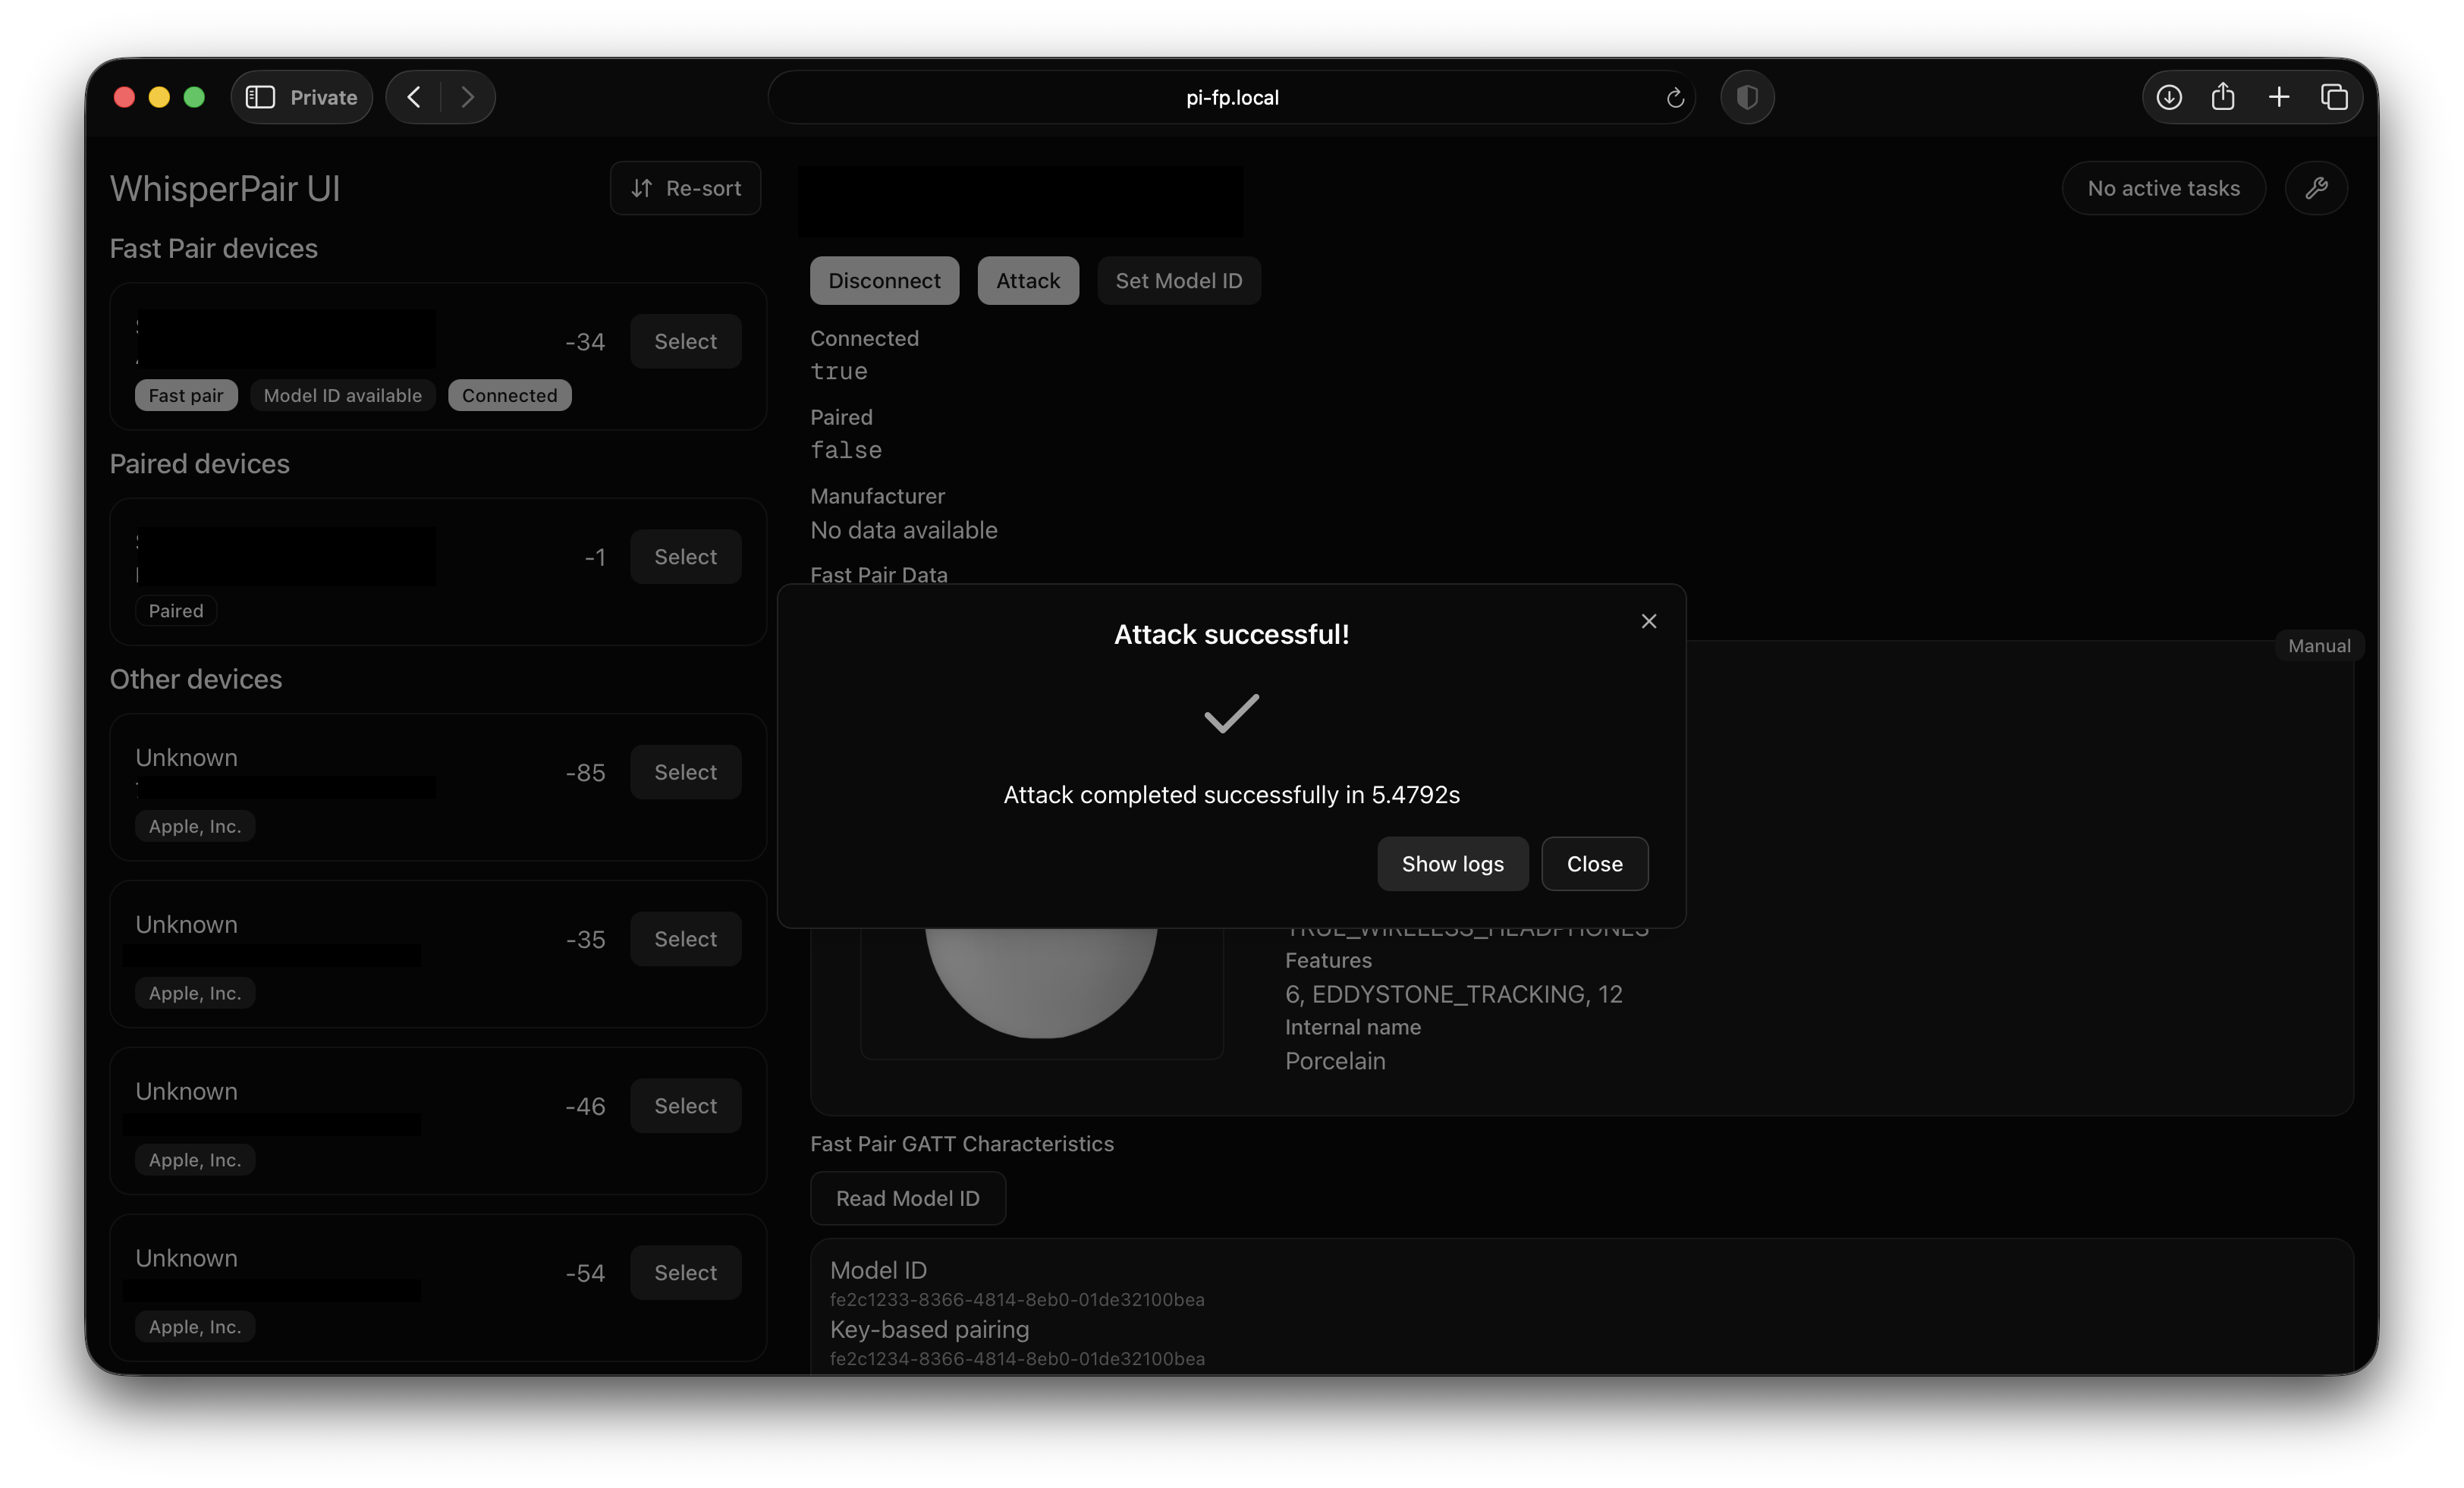 kuleuven-cosic/whisperpair
The official reference implementation & vulnerability verification of our attack WhisperPair (CVE-2025-36911) which affects Google's Fast Pair…
 ojasookert/cve-2017-0781
Blueborne CVE-2017-0781 Android heap overflow vulnerability
 nccgroup/ble-replay
BLE-Replay is a Bluetooth Low Energy (BLE) peripheral assessment tool
 spectrixdev/diy_whisperpair
Hijacking Bluetooth Accessories Using Google Fast Pair: WhisperPair CVE-2025-36911 Reference Implementation & Vulnerability Verification Toolkit
 anssi-fr/ultrablue
User-friendly Lightweight TPM Remote Attestation over Bluetooth
 leommxj/cve-2020-0022
Proof-of-concept exploit for CVE-2020-0022, targeting Android Bluetooth stack to trigger a buffer overflow via crafted L2CAP packets, causing denial…

 lrh2000/cve-2023-2002
Linux Bluetooth - Run arbitrary management commands as an unprivileged user
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 ymsniper/whisper_bully
Three-stage Bluetooth BDADDR extraction, DoS & hijack on Fast Pair devices; unpatched primitives outside CVE-2025-36911 scope (no Ubertooth needed)
 omerporze/brokentooth
POC for CVE-2018-4327
 nccgroup/blesuite-cli
BLESuite_CLI is a command line tool to enable an easier way to test Bluetooth Low Energy (BLE) devices
 saimanish1/logitech-ipc-protocol
Reverse-engineered Logi Options+ agent IPC protocol. Switch Logitech multi-host devices programmatically via Unix socket (macOS) or named pipe…
 zhuowei/blueshrimp
Proof-of-concept for CVE-2025-48593
 butterflyhack/cve-2019-10207
PoC for CVE-2019-10207