
bitchat-android
Decentralized, encrypted peer-to-peer messaging app over Bluetooth mesh networks. No internet, servers, or phone numbers required. Features X25519 +…

Decentralized, encrypted peer-to-peer messaging app over Bluetooth mesh networks. No internet, servers, or phone numbers required. Features X25519 +…

The open-source wireless research platform for ESP32.

AirPods liberated from Apple's ecosystem.

attempting to detect smart glasses nearby and warn you

Modular Bluetooth Classic (BR/EDR) vulnerability testing framework with reconnaissance, exploit modules for 43 public attacks/CVEs, and structured…

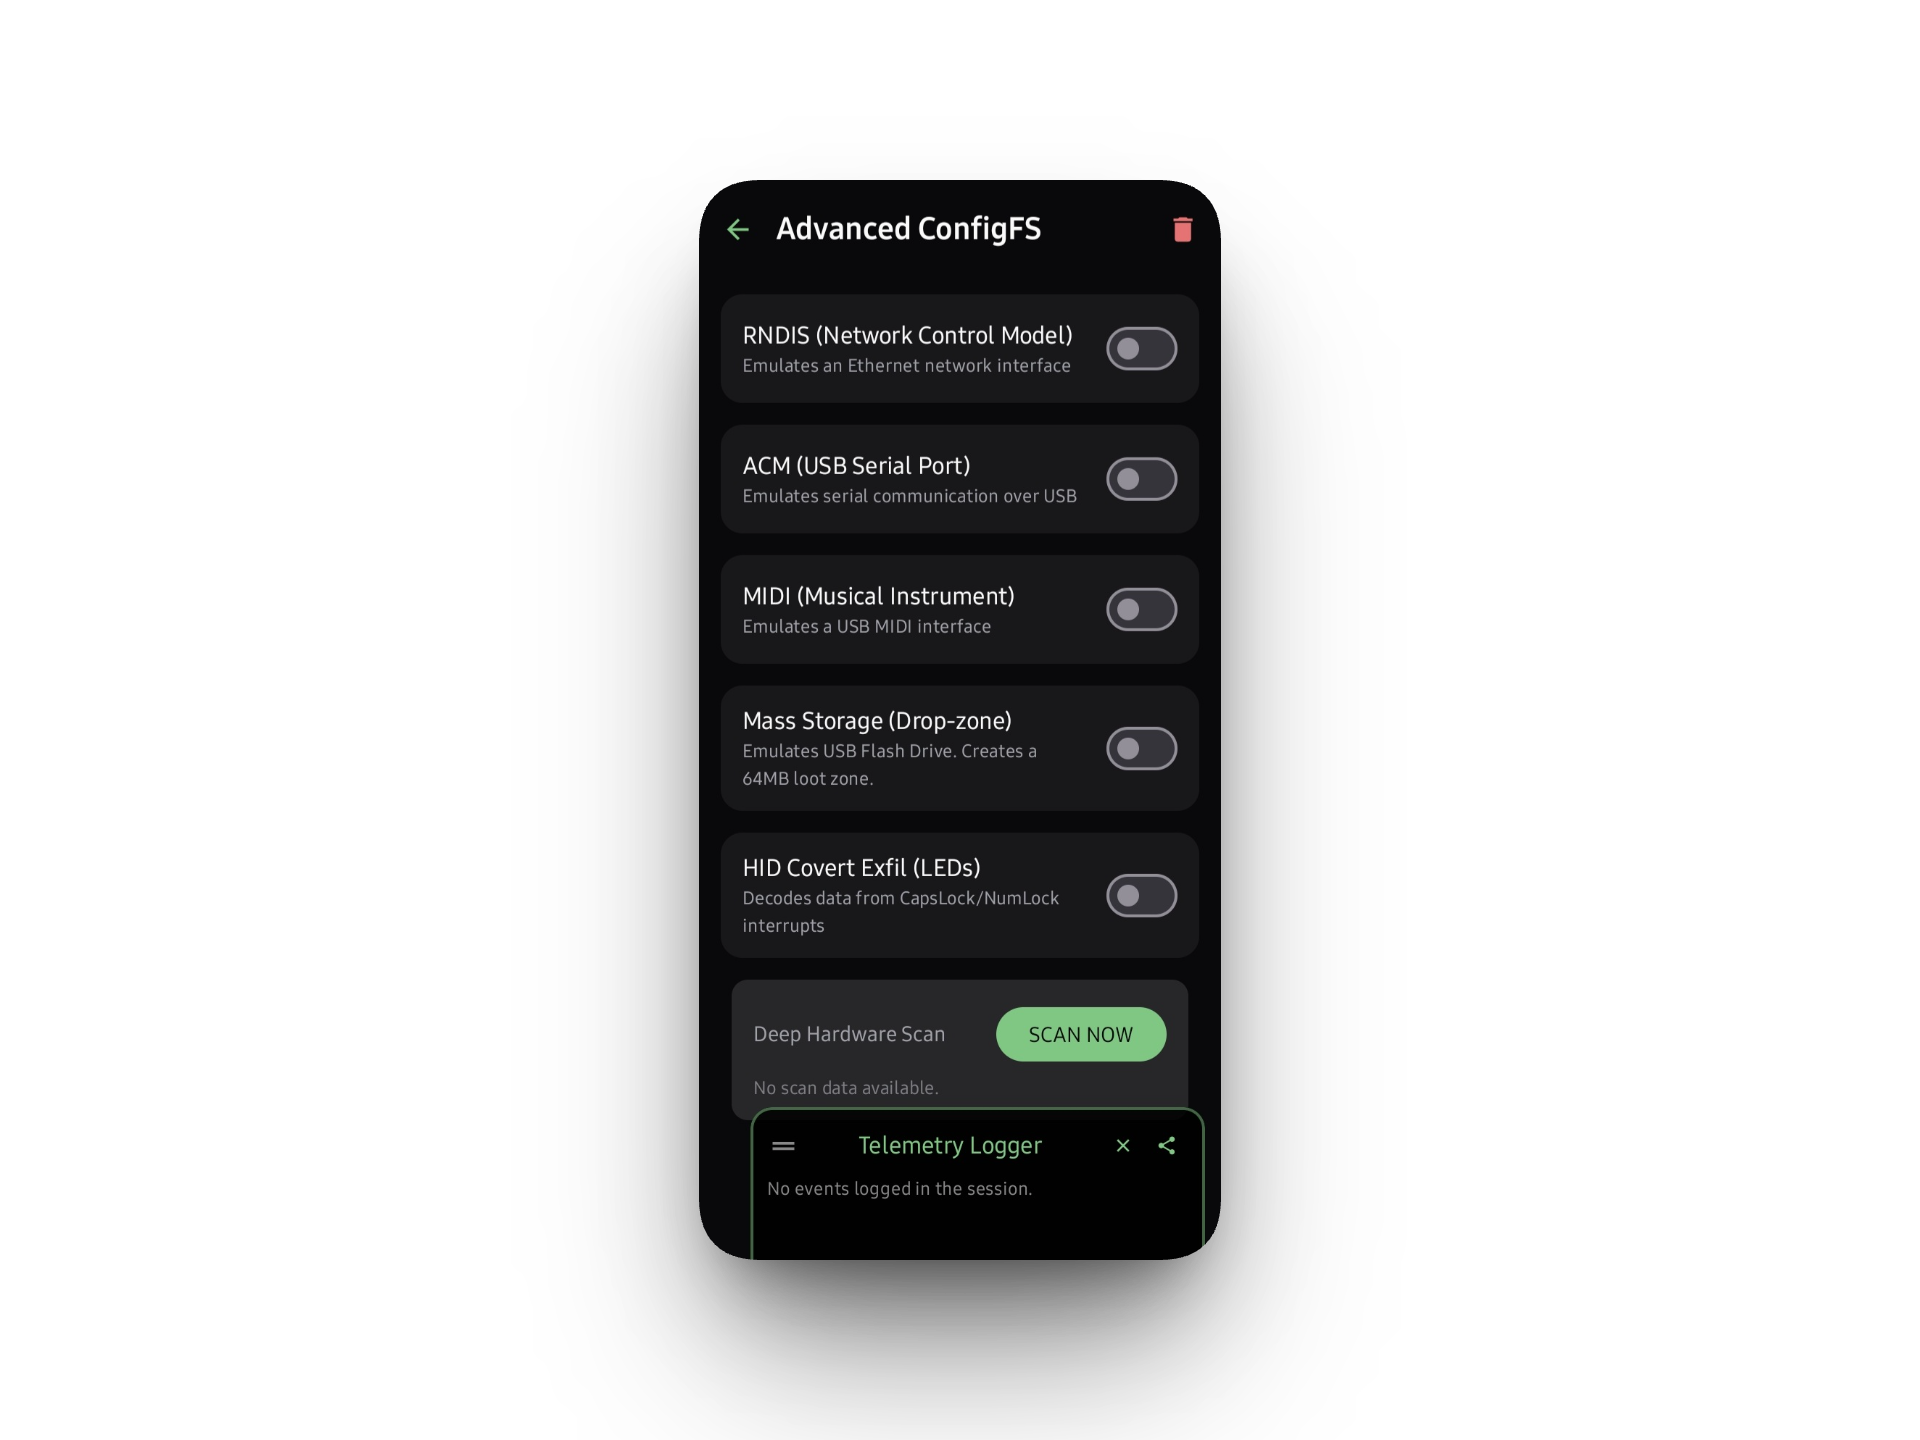
Payload injector and HID emulator for Android like Hak5 and rubber ducky

Open-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…

"A single malicious packet can own your device." — Android Security Team, Nov 2025

Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…

Exploit of the CVE-2025-36911 vulnerability in Python for testing our own equipment

WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…

Proof-of-concept for CVE-2025-48593

A Virtual environment for Pentesting IoT Devices

WITCHCRAFT is a cyberdeck toolkit built for runners who dive deep into the mesh. It’s your all-in-one rig for data-ghosting, ICE-breaking, and…

# android-ble-cve-2025-4866 🔐 **PoC za CVE-2025-4866 — Android BLE ranjivost (javna verzija)** 📡 Iskorišćavanje slabosti u BLE autorizaciji na…

Targeted reference for CVE-2023-21125, an Android BlueDroid Bluetooth vulnerability, with code and documentation focused on the affected component.

Exploits Tested in Mi A2 Lite and Realme 2 pro

Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…