
oxasploits
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
binary-exploitationbluetooth-securityexploitation+6
oxasploits/oxasploitsA number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
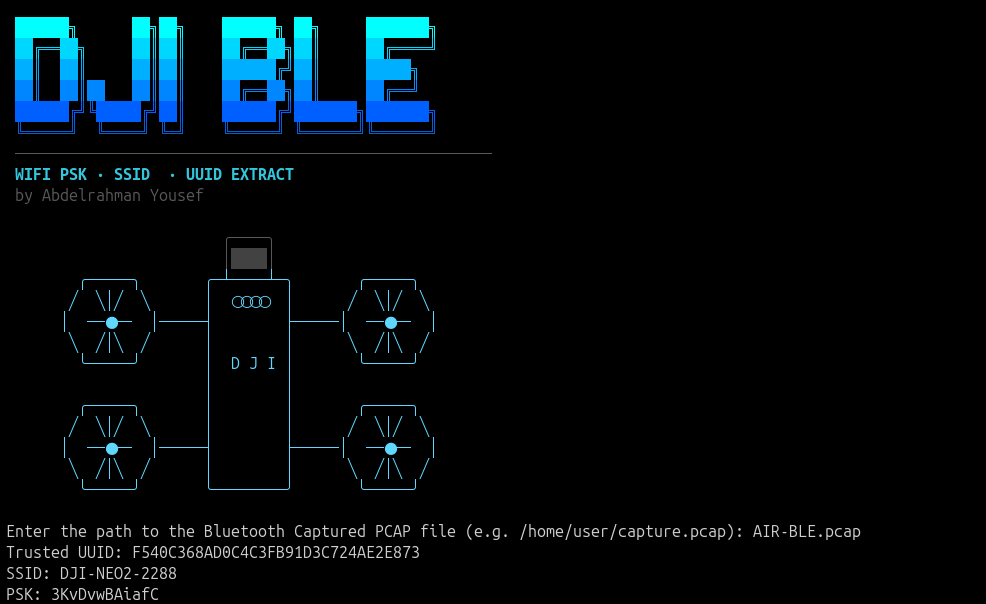 wh02m1/cve-2026-77812
Proof-of-concept that passively sniffs cleartext BLE DUML traffic from DJI drones to recover Wi-Fi PSK and trusted session UUIDs, demonstrating…
 whad-team/whad-client
Protocol client and CLI framework for interacting with wireless hacking devices, enabling security researchers to explore, test, and automate…
 olivierlaflamme/unibleed
Unitree G1 RCE PoC & Scripts (CVE-2026-76639 / CVE-2026-76640) technical details at boschko.ca/g1-ble-rce/
 wh00hw/pyflipper
Flipper Zero Python CLI Wrapper
 ymsniper/whisper_bully
Three-stage Bluetooth BDADDR extraction, DoS & hijack on Fast Pair devices; unpatched primitives outside CVE-2025-36911 scope (no Ubertooth needed)
 nicholas-howland/cve-2026-6992-poc
Vulnerability proof of concept reworked from https://github.com/utmost3/cve/issues/2 I take no credit for discovering the vulnerability. This is for…
 hegaz0y/-bul
EDSEC_BKIF is a keystroke injection tool for Android, Linux, and iOS. With the help of CVE-2023-45866, it grants users unprecedented control over…
 jgoyd/ios-attack-chain-cve-2025-31200-cve-2025-31201
CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s AudioConverterService, triggered by a malicious audio file via iMessage/SMS.…
 threat9/routersploit
Exploitation Framework for Embedded Devices
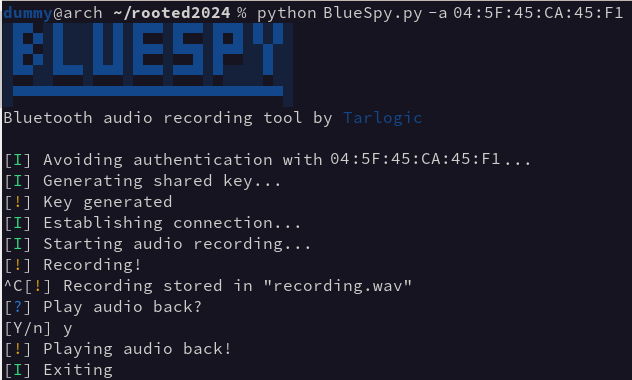 tarlogicsecurity/bluespy
PoC to record audio from a Bluetooth device
 cipherx1802/cve-2026-31280-insecure-bluetooth-rfcomm-leading-to-device-crash-in-parani-m10-intercom
Proof-of-concept demonstrating an unauthenticated Bluetooth RFCOMM service in Parani M10 Intercom that allows arbitrary payload delivery, leading to…
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.
 scramblr/rf-chaos
RF CHAOS is an Android App That Is Designed To Cause Chaos via All RF Adapters Possible - Enjoy!
 barghest-ngo/cve-2026-51376
Proof-of-concept exploit for BLE cache poisoning in Bitchat 1.15.0, demonstrating a man-in-the-middle attack that poisons the Bluetooth Low Energy…
 pentestfunctions/blueducky
🚨 CVE-2023-45866 - BlueDucky Implementation (Using DuckyScript) 🔓 Unauthenticated Peering Leading to Code Execution (Using HID Keyboard)
 pivotchip/frostedfastpair
WhisperPair (CVE-2025-36911) POC for ESP32 device
 penthertz/cve-2025-36911-exploit
Exploit of the CVE-2025-36911 vulnerability in Python for testing our own equipment