

wireshark
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
bluetooth-securitydata-exfiltrationdigital-forensics+11
10.1k
wireshark/wiresharkCapture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 bluez/bluez
Linux Bluetooth protocol stack with daemons, command-line clients, HCI monitor, and support for BR/EDR, LE, Mesh, audio profiles, providing device…
 phantom-brigade1/wifisting
GTK4 and CLI wireless security toolkit with 57 standalone modules for Wi-Fi, Bluetooth, 802.15.4, SDR/RF, NFC and router-side or network MITM testing…
 ymsniper/whisper_bully
Three-stage Bluetooth BDADDR extraction, DoS & hijack on Fast Pair devices; unpatched primitives outside CVE-2025-36911 scope (no Ubertooth needed)
 hegaz0y/-bul
EDSEC_BKIF is a keystroke injection tool for Android, Linux, and iOS. With the help of CVE-2023-45866, it grants users unprecedented control over…
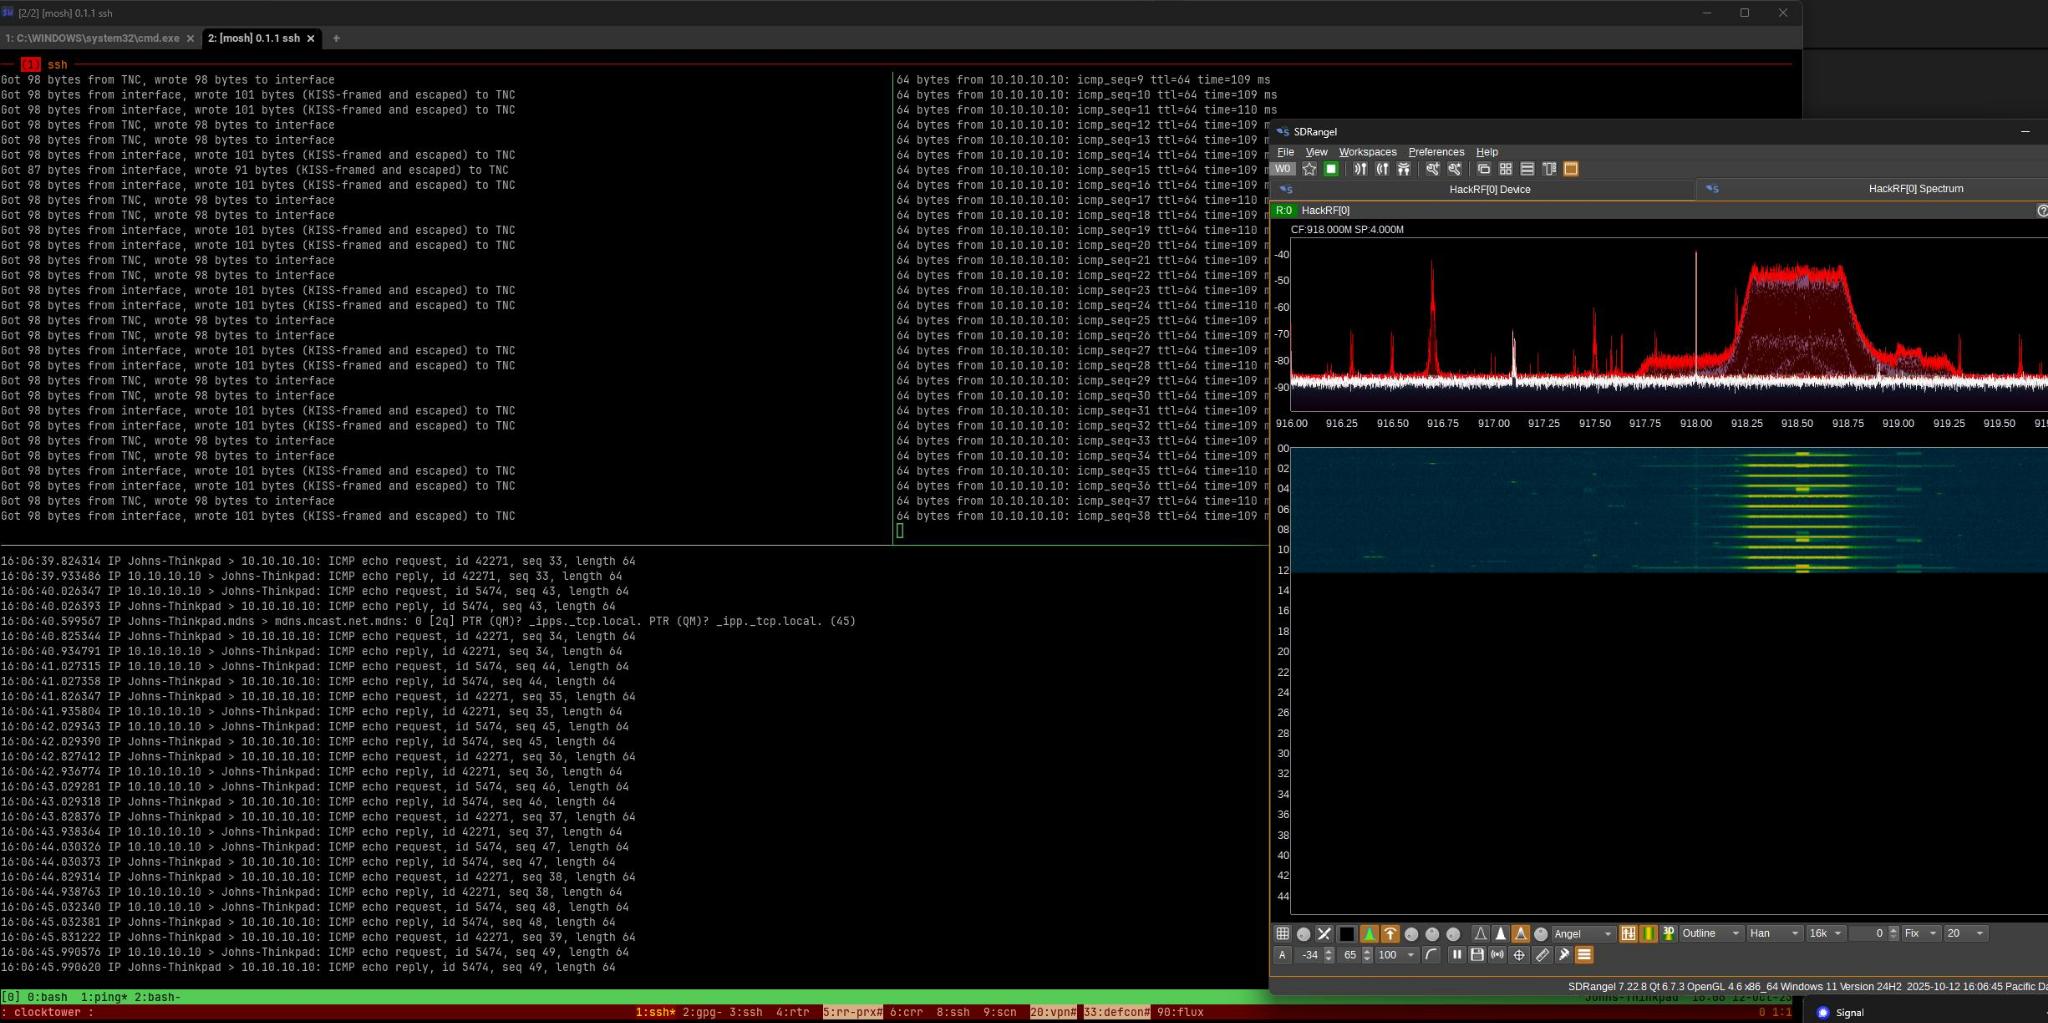 datapartyjs/meshtnc
Firmware for converting consumer LoRa radios into KISS TNC modems with serial CLI, BLE packet sniffing, and APRS/AX.25 compatibility for packet radio…
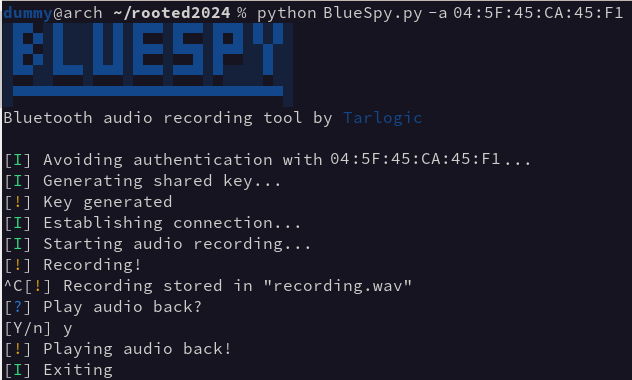 tarlogicsecurity/bluespy
PoC to record audio from a Bluetooth device
 v3ilsm1th/cve-2023-45866_wip
Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…
 seemoo-lab/internalblue
Bluetooth experimentation framework for Broadcom and Cypress chips.
 cisnarfu/bluepop
Bluetooth Classic HID injection exploit for CVE-2023-45866, enabling unauthenticated keystroke injection against vulnerable BlueZ-based Linux systems.
 chapoly1305/cve-2023-46870
Detailed analysis and proof-of-concept for CVE-2023-46870, a local privilege escalation in Nordic Semiconductor nRF Sniffer for Bluetooth LE due to…
 francozappa/bluffs
Toolkit for testing Bluetooth session establishment against forward and future secrecy attacks, using firmware patching, PCAP analysis, and automated…
 pybluez/pybluez
Python extension module providing Bluetooth access: device inquiry, SDP service browsing, RFCOMM/L2CAP sockets, and experimental BLE scanning and…
 hayzamjs/blueborne-cve-2017-1000251
Proof-of-concept exploit for Blueborne CVE-2017-1000251 enabling Bluetooth denial-of-service attacks on Linux machines via crafted L2CAP packets.
 francozappa/knob
Key Negotiation Of Bluetooth (KNOB) attacks on Bluetooth BR/EDR and BLE [CVE-2019-9506]
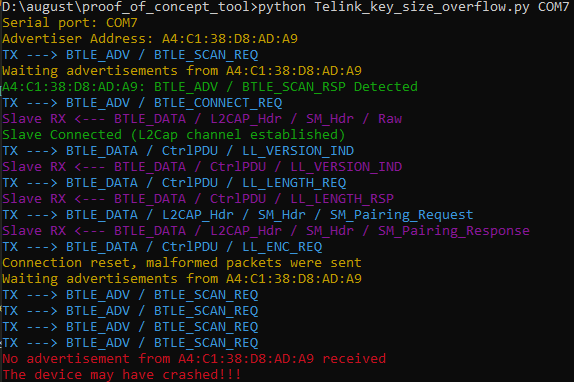 matheus-garbelini/sweyntooth_bluetooth_low_energy_attacks
Proof of Concept of Sweyntooth Bluetooth Low Energy (BLE) vulnerabilities.