
wireshark
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
bluetooth-securitydata-exfiltrationdigital-forensics+11
9.9k
wireshark/wiresharkCapture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
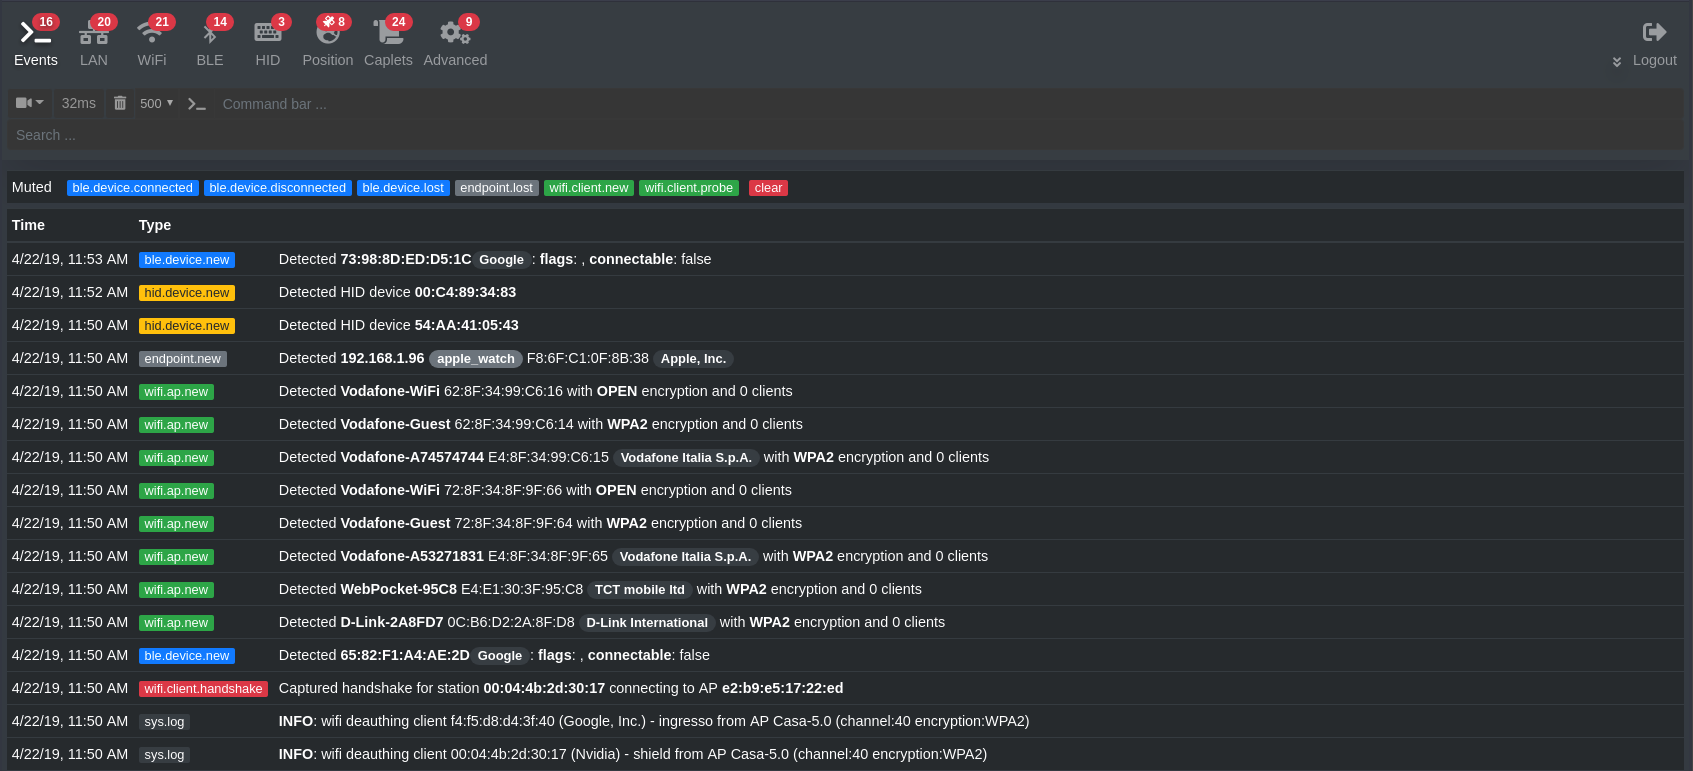 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 george0papasotiriou/cve-2026-22017-firmware-update-via-ble-without-authentication
Simulated BLE peripheral exposing an unauthenticated GATT firmware-update characteristic; demonstrates critical CVE-2026-22017 device-takeover…
 f4r3sx0/ios-bluetooth-ethernet-exploit
iOS Bluetooth PAN vulnerability that opens USB port 62078 and displays Ethernet icon without any adapter (€0). Apple sells a €89.95 adapter for the…
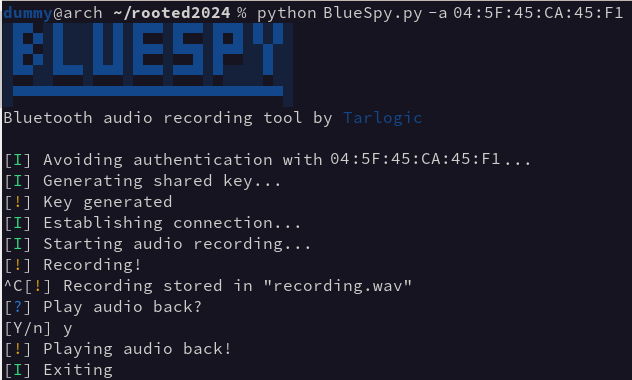 tarlogicsecurity/bluespy
PoC to record audio from a Bluetooth device
 cipherx1802/cve-2026-31280-insecure-bluetooth-rfcomm-leading-to-device-crash-in-parani-m10-intercom
Proof-of-concept demonstrating an unauthenticated Bluetooth RFCOMM service in Parani M10 Intercom that allows arbitrary payload delivery, leading to…
 cipherx1802/cve-2025-69821-beat-xp-vega-smartwatch-security-assessment
A security assessment of the Beat XP VEGA Smartwatch (Firmware RB303ATV006229) focused on Bluetooth Low Energy (BLE) connectivity revealed a design…
 sastraadiwiguna-purpleeliteteaming/cve-2025-13834-a-bluetooth-rfcomm-out-of-bounds-read-vulnerability-in-modern-wireless-devices
CVE-2025-13834 Technical Summary Vulnerability Type: Memory Disclosure / Out-of-Bounds (OOB) Read (CWE-125). CVSS Score: 7.5–8.1 (High/Critical). …
 zalexdev/wpair-app
WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…
 jclarkcom/ble_proxy
BLE-based HTTP proxy system routing browser traffic through an iOS device. Supports HTTP/HTTPS, data compression, and mock mode for testing without…
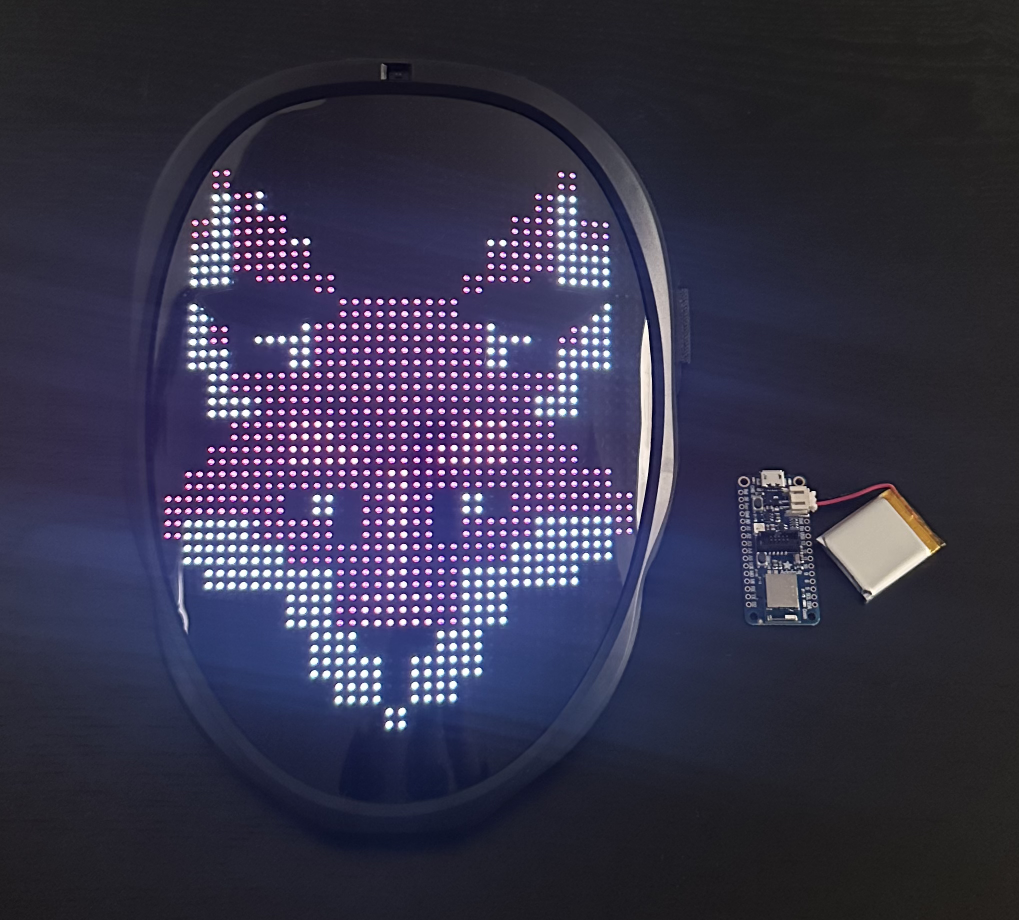 bishopfox/shining-mask
BLE-based tool that automatically discovers and exploits Shining LED Masks by uploading a custom image without user interaction, proving security…
 sergeb250/blueducky
BlueDucky exploits a Bluetooth vulnerability, specifically CVE-2023-45866, which allows an attacker to inject keystrokes into a target device. The…