
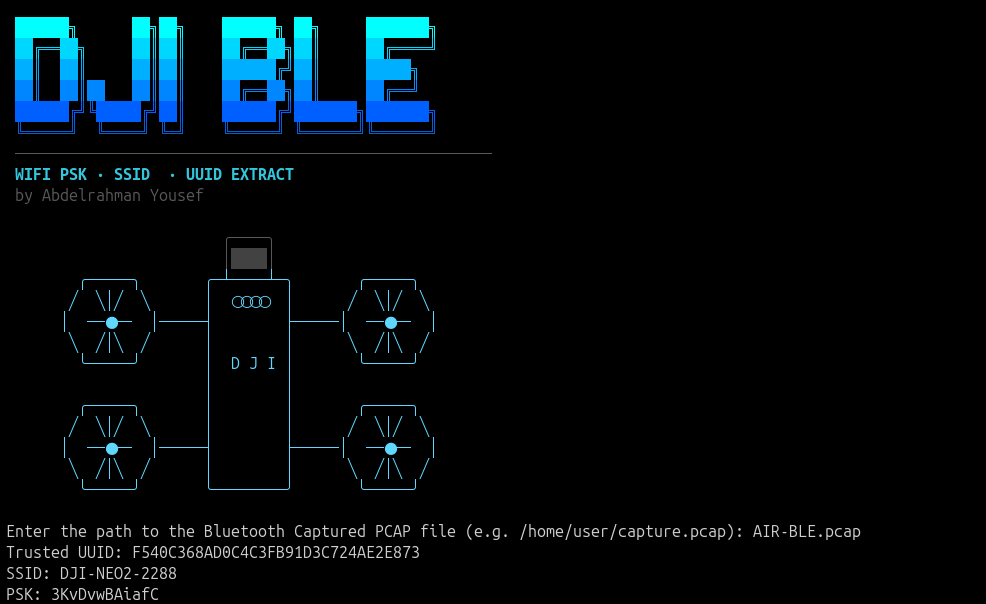
CVE-2026-77812
 wh02m1/cve-2026-77812
Proof-of-concept that passively sniffs cleartext BLE DUML traffic from DJI drones to recover Wi-Fi PSK and trusted session UUIDs, demonstrating…
bluetooth-securityexploitationhardware-iot-security+4
1
wh02m1/cve-2026-77812Proof-of-concept that passively sniffs cleartext BLE DUML traffic from DJI drones to recover Wi-Fi PSK and trusted session UUIDs, demonstrating…
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
 barghest-ngo/cve-2026-51376
Proof-of-concept exploit for BLE cache poisoning in Bitchat 1.15.0, demonstrating a man-in-the-middle attack that poisons the Bluetooth Low Energy…
 v3ilsm1th/cve-2023-45866_wip
Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…
 v3ilsm1th/cve-2025-27840-wip
Work-in-progress PoC for CVE-2025-27840, an ESP32 Bluetooth vulnerability involving undocumented HCI commands enabling memory access and device…
 davidrxchester/smart-sketcher-upload
Exploits Bluetooth authentication bypass on smART Sketcher 2.0 toy projector, allowing unauthenticated connection and image upload via Python scripts.
 shaikusaf/system_bt_aosp10_r33_cve-2021-0435
AOSP Bluetooth stack repository modified for CVE-2021-0435, providing a patched or vulnerable version for analysis and testing of Bluetooth…
 eason-zz/bluetoothducky
Exploit implementation for CVE-2023-45866 enabling unauthenticated Bluetooth keyboard injection using DuckyScript payloads on Raspberry Pi.
 cipherx1802/cve-2026-31280-insecure-bluetooth-rfcomm-leading-to-device-crash-in-parani-m10-intercom
Proof-of-concept demonstrating an unauthenticated Bluetooth RFCOMM service in Parani M10 Intercom that allows arbitrary payload delivery, leading to…
 jjjjjjjj987/cve-2023-45866-py
Python-based proof-of-concept for CVE-2023-45866, a Bluetooth vulnerability, demonstrating exploitation techniques for security research and testing.
 olivierlaflamme/unibleed
Unitree G1 RCE PoC & Scripts (CVE-2026-76639 / CVE-2026-76640) technical details at boschko.ca/g1-ble-rce/
 toxy4ny/rinhit
Collects macOS and iOS artifacts to build timelines of network activity, cross-device identity, and physical location correlation for reconnaissance…
 greatscottgadgets/libbtbb
C library for decoding Bluetooth baseband packets and extracting piconet information from Ubertooth and USRP hardware for wireless analysis.
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 francozappa/bluffs
Toolkit for testing Bluetooth session establishment against forward and future secrecy attacks, using firmware patching, PCAP analysis, and automated…
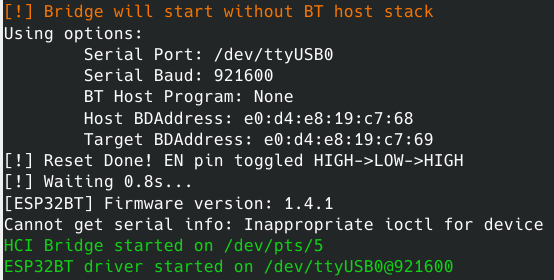 matheus-garbelini/esp32_bluetooth_classic_sniffer
Active Bluetooth BR/EDR Sniffer/Injector as cheap as any ESP32 board can get. Works with Scapy ;-)
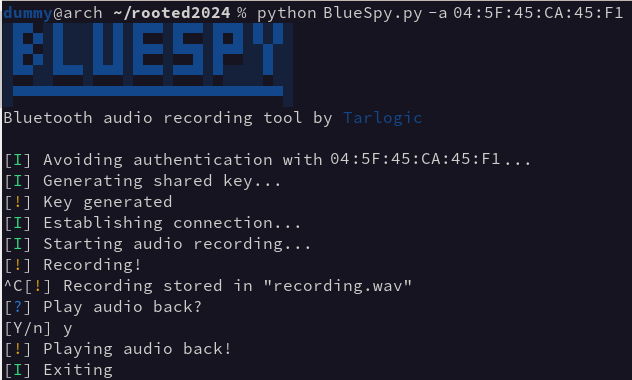 tarlogicsecurity/bluespy
PoC to record audio from a Bluetooth device
 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…