
CVE-2023-45866_WIP
Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…

Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…

Toolkit for testing Bluetooth session establishment against forward and future secrecy attacks, using firmware patching, PCAP analysis, and automated…

Bluetooth experimentation framework for Broadcom and Cypress chips.

Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…

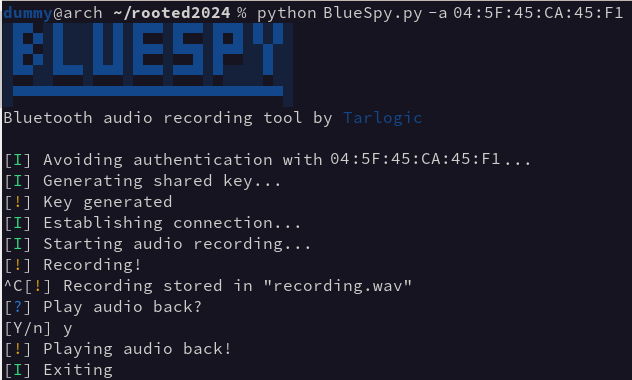
PoC to record audio from a Bluetooth device

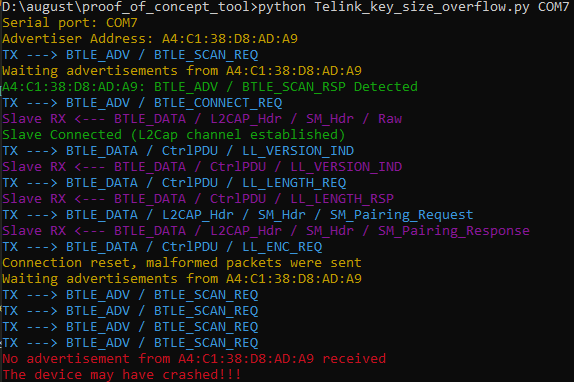
Proof of Concept of Sweyntooth Bluetooth Low Energy (BLE) vulnerabilities.

A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast

CVE 2020-10135 a.k.a BIAS (Bluetooth Impersonation Attack)

CVE-2025-13834 Technical Summary Vulnerability Type: Memory Disclosure / Out-of-Bounds (OOB) Read (CWE-125). CVSS Score: 7.5–8.1 (High/Critical). …

Exploit for CVE-2020-0225 in the Android Fluoride Bluetooth stack, enabling remote code execution via a crafted Bluetooth packet. Includes build…

Rust implementation of Marc Newlin's keystroke injection proof of concept (CVE-2023-45866).

CVE-2020-12351

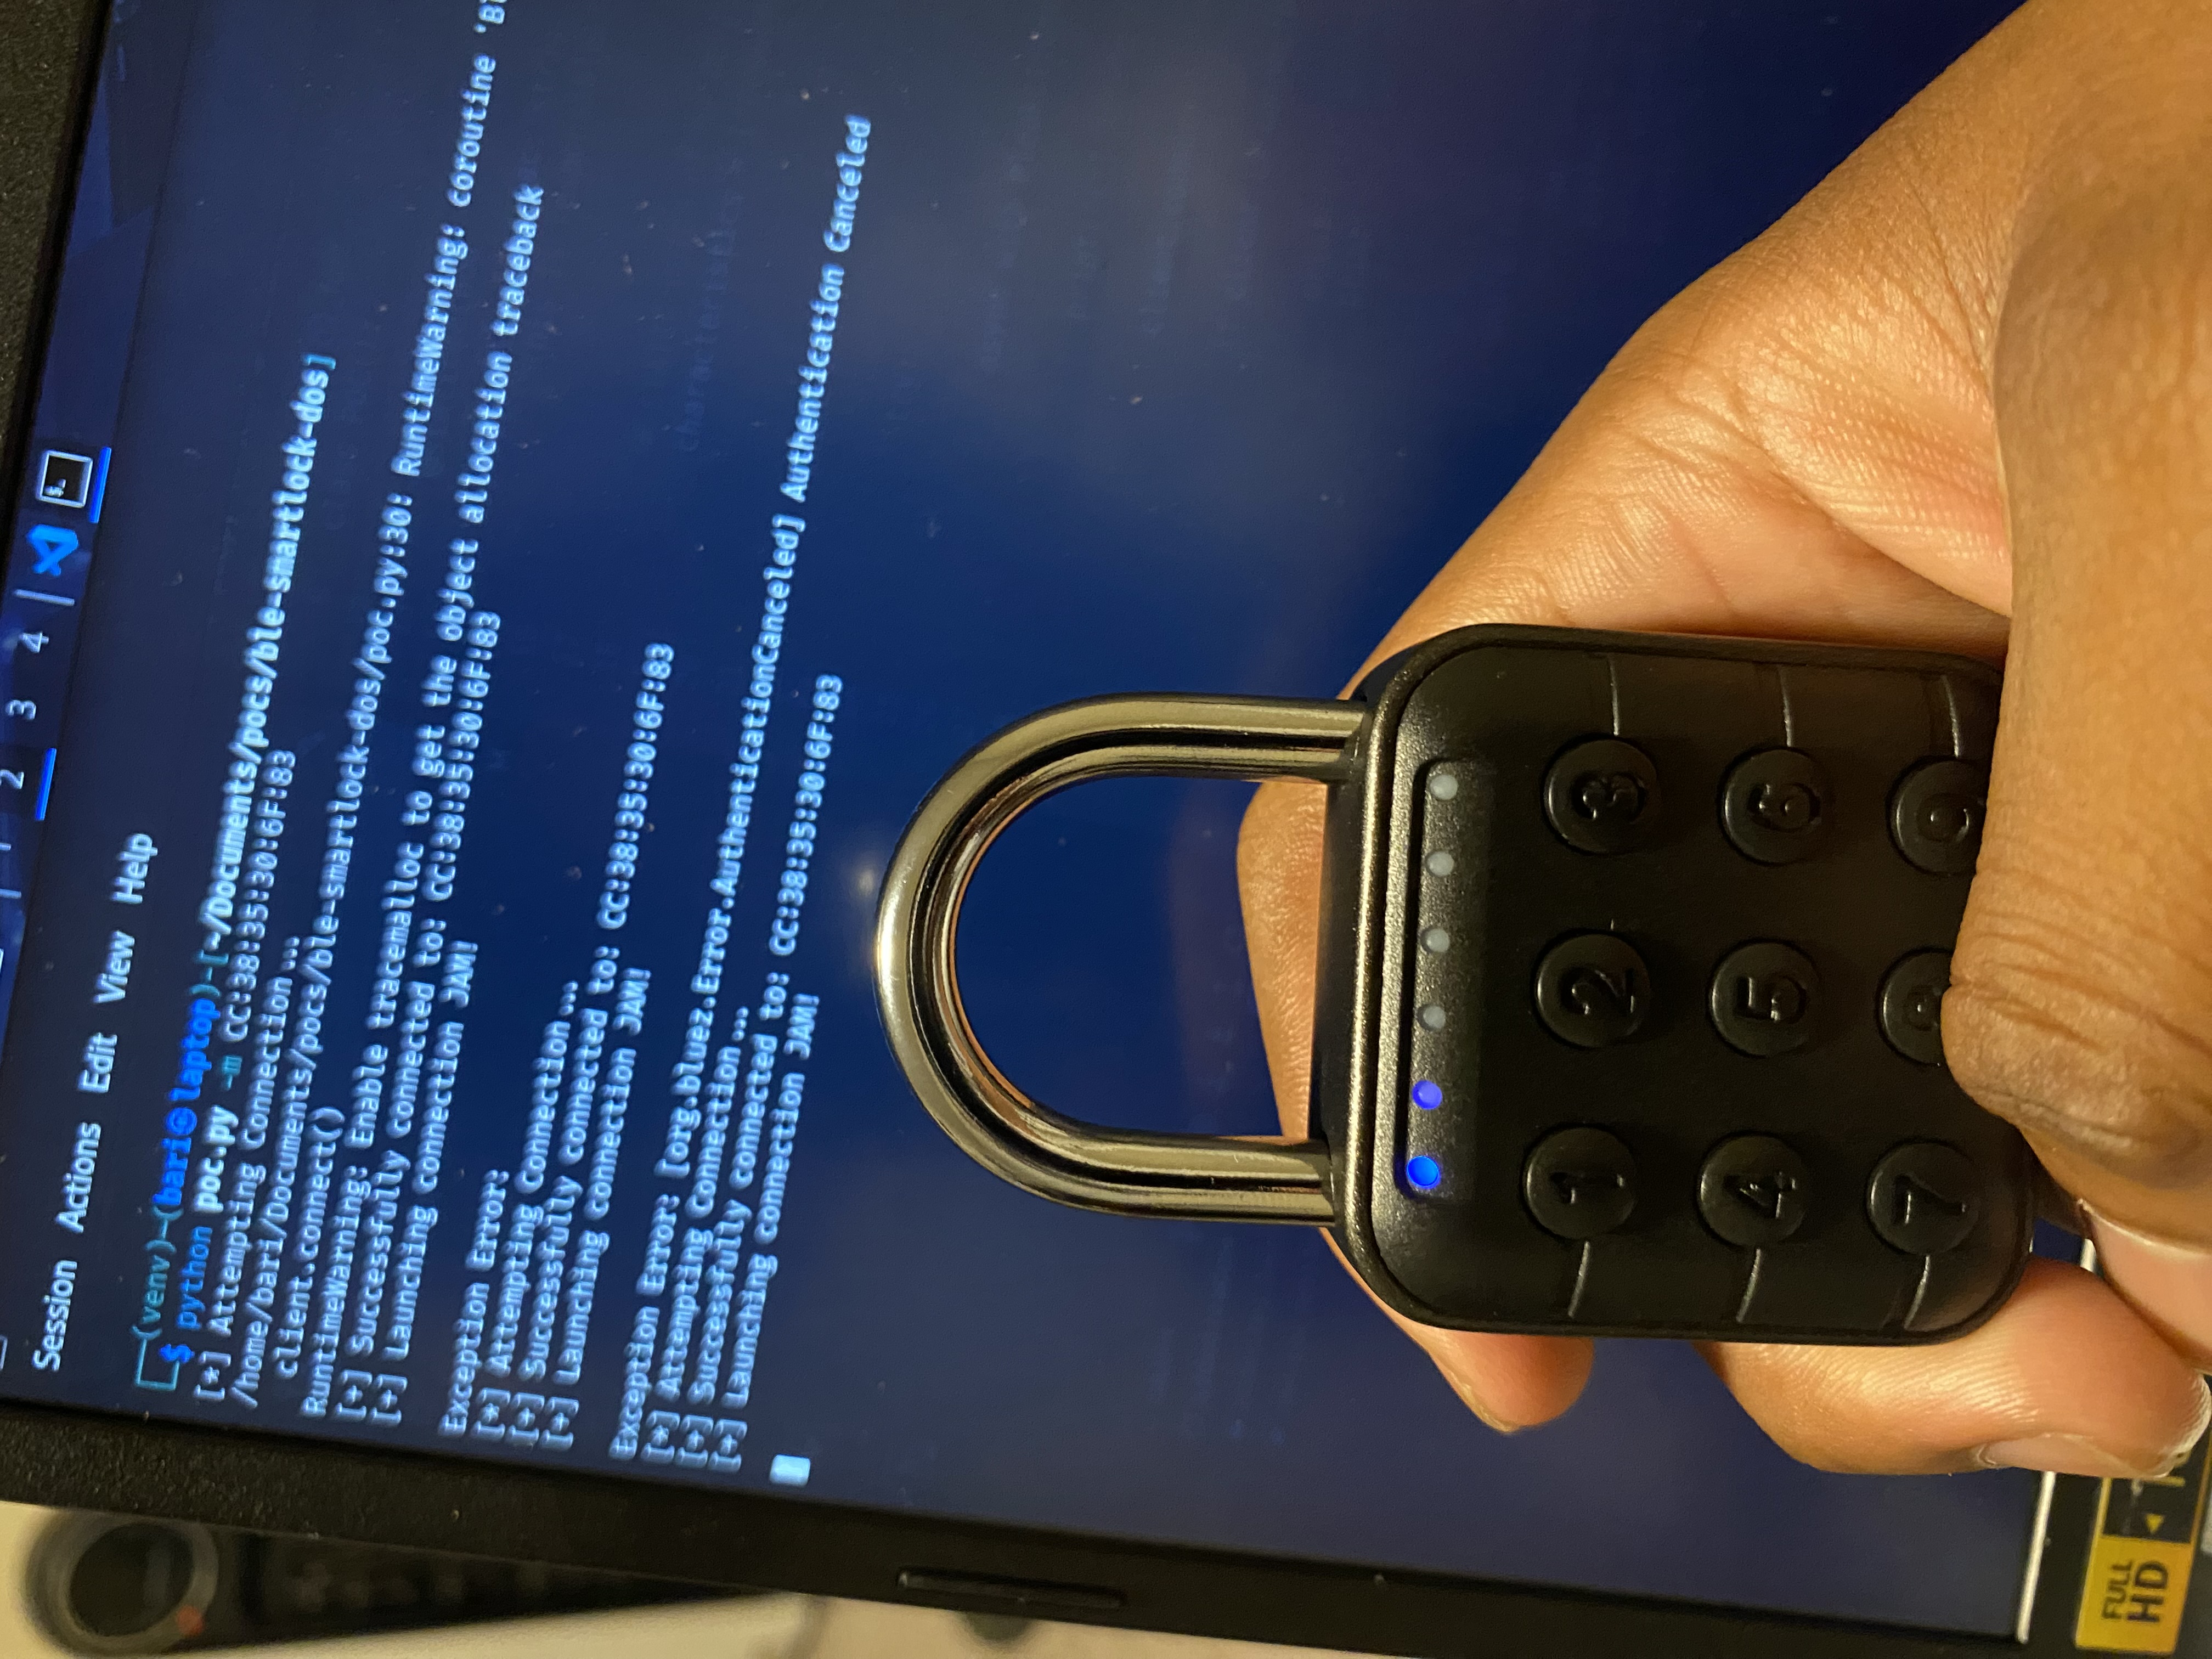
A denial-of-service vulnerability in the AuntyFey BLE smart padlock allows unauthenticated connection floods to lock out legitimate users. …

Advanced Wiimote remapping software

Linux Bluetooth - Run arbitrary management commands as an unprivileged user

Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…

AirPods liberated from Apple's ecosystem.

Linux Kernel < 4.13.1 - BlueTooth Buffer Overflow (PoC) BlueBorne - Proof of Concept - Unarmed/Unweaponized - DoS (Crash) only