smart-sketcher-upload

Exploits Bluetooth authentication bypass on smART Sketcher 2.0 toy projector, allowing unauthenticated connection and image upload via Python scripts.

Exploits Bluetooth authentication bypass on smART Sketcher 2.0 toy projector, allowing unauthenticated connection and image upload via Python scripts.

Python-based proof-of-concept for CVE-2023-45866, a Bluetooth vulnerability, demonstrating exploitation techniques for security research and testing.

Protocol client and CLI framework for interacting with wireless hacking devices, enabling security researchers to explore, test, and automate…

Bluetooth Low Energy (BLE) packet sniffer and transmitter for both standard and non standard (raw bit) based on Software Defined Radio (SDR).

Quarkslab conference talks

PoC to record audio from a Bluetooth device

Python simulation of the Bluetooth Classic KNOB attack, showing encryption key-size downgrade and brute-force decryption of intercepted Bluetooth…

BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…

Firmware for getting a power trace of the behavior of the bluetooth module on the ESP32 when the ESP32 is sent the undocumented hci bluetooth…

Simulated BLE peripheral exposing an unauthenticated GATT firmware-update characteristic; demonstrates critical CVE-2026-22017 device-takeover…

Python PoC for CVE-2026-0101 demonstrating BLE address spoofing via replay of a captured Resolvable Private Address to impersonate a trusted…

Reverse engineering of the oBike protocol communication (BLE and HTTP)

BLESuite is a Python package that provides an easier way to test Bluetooth Low Energy (BLE) device

BLESuite_CLI is a command line tool to enable an easier way to test Bluetooth Low Energy (BLE) devices

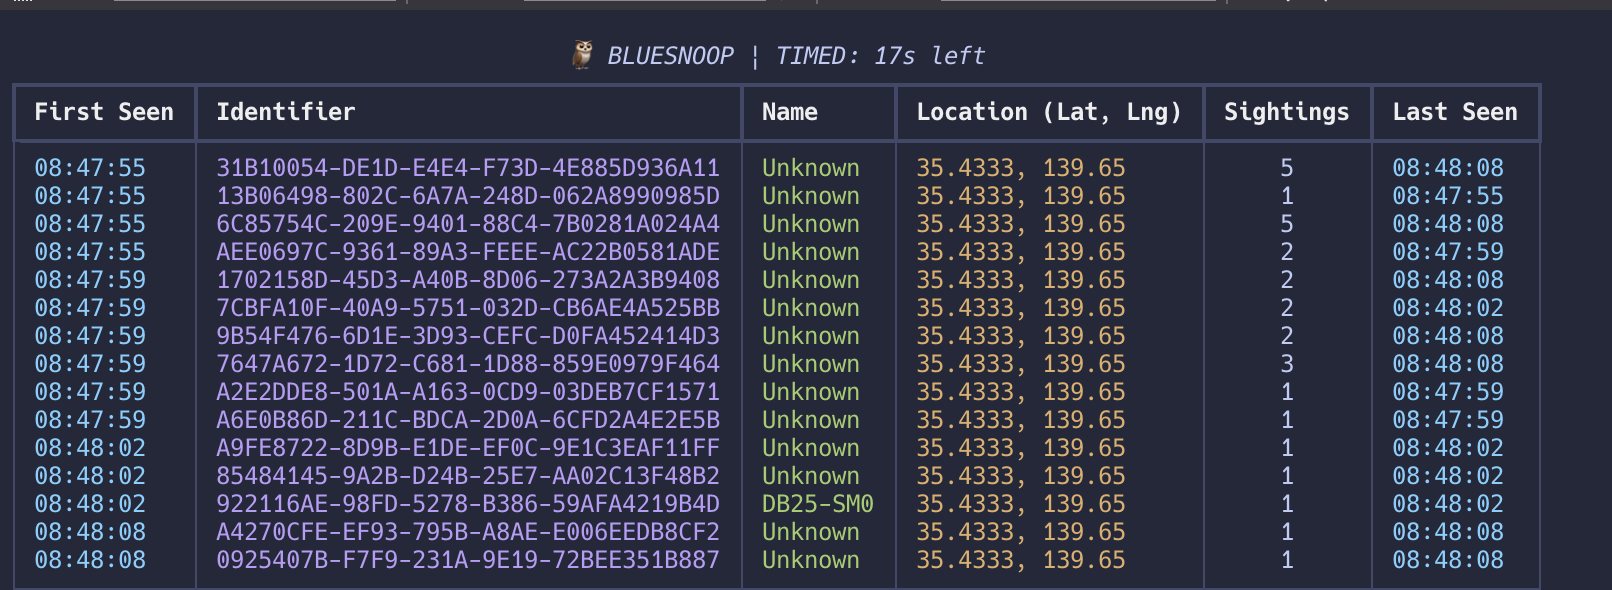
A TUI bluetooth utility for radar analysis and war driving 🦉

Source code for the book "Violent Python" by TJ O'Connor. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…

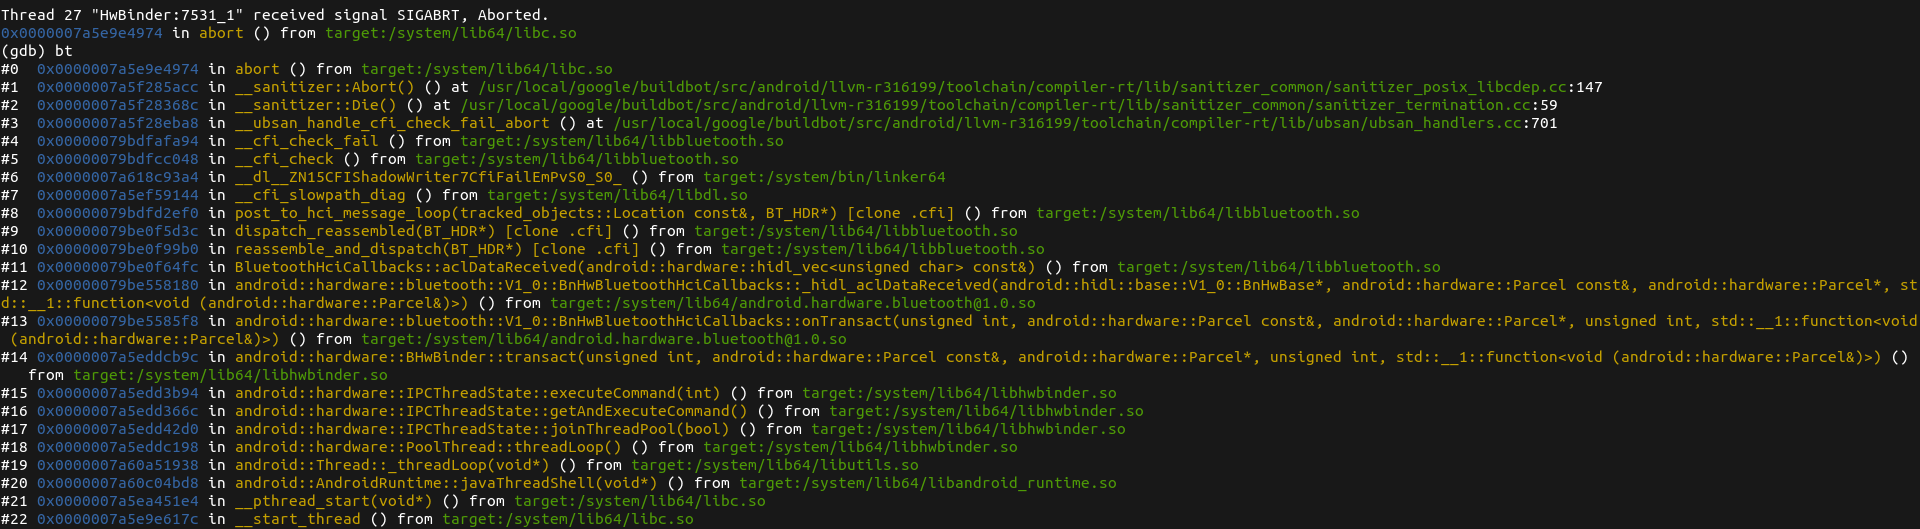
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)

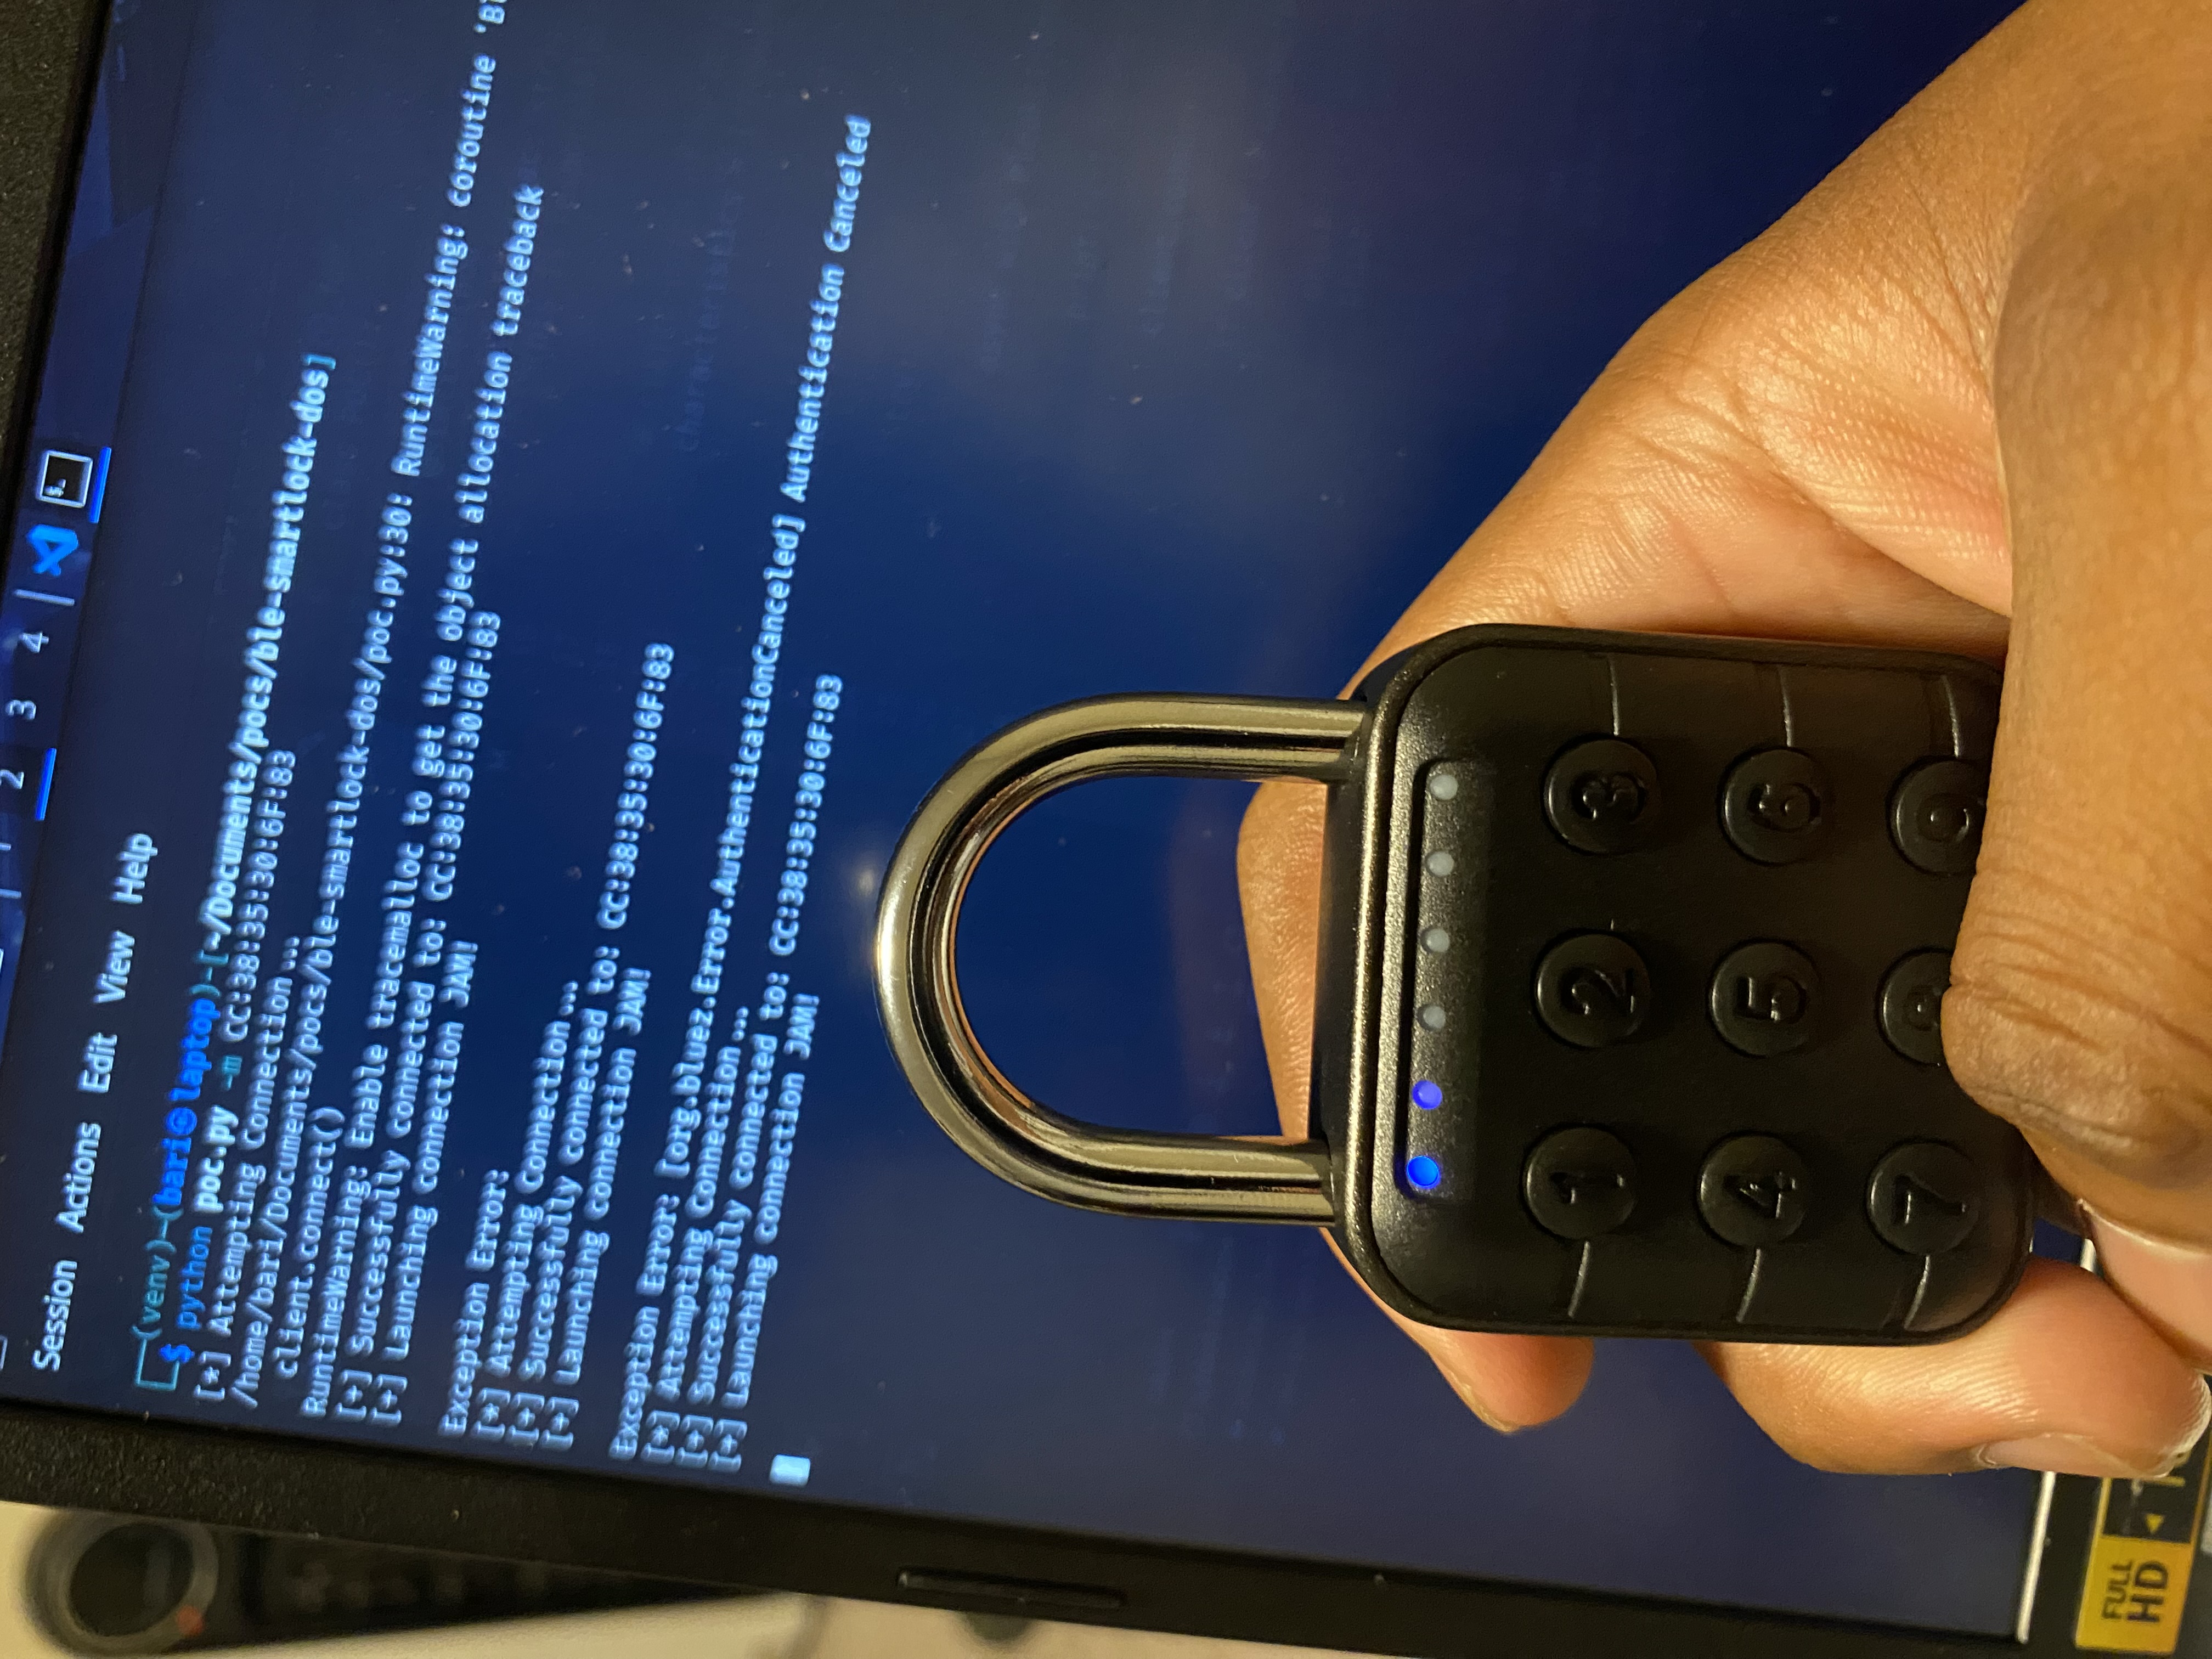
A denial-of-service vulnerability in the AuntyFey BLE smart padlock allows unauthenticated connection floods to lock out legitimate users. …