
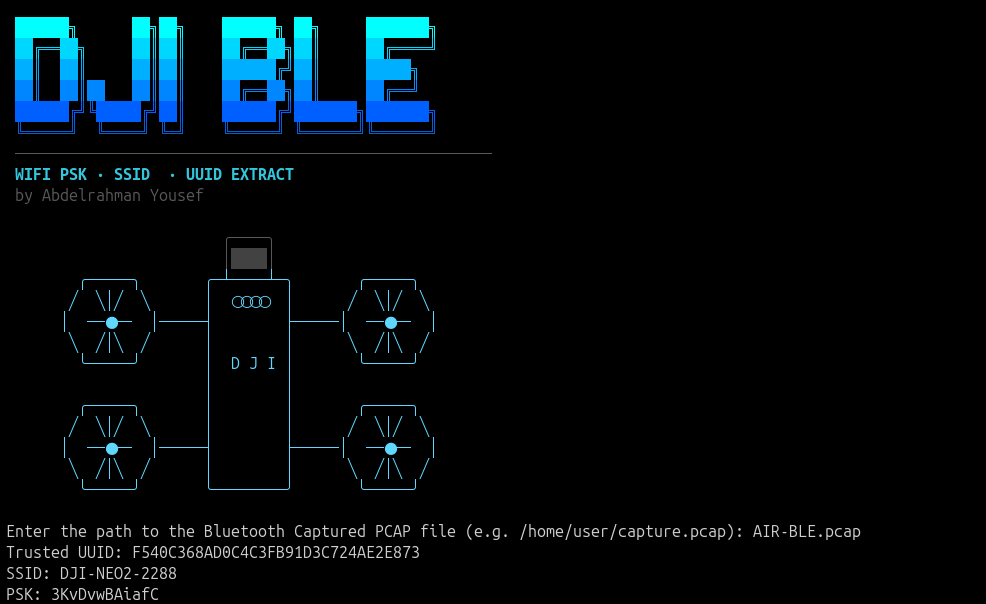
CVE-2026-77812
 wh02m1/cve-2026-77812
Proof-of-concept that passively sniffs cleartext BLE DUML traffic from DJI drones to recover Wi-Fi PSK and trusted session UUIDs, demonstrating…
bluetooth-securityexploitationhardware-iot-security+4
3
wh02m1/cve-2026-77812Proof-of-concept that passively sniffs cleartext BLE DUML traffic from DJI drones to recover Wi-Fi PSK and trusted session UUIDs, demonstrating…
 v3ilsm1th/cve-2025-27840-wip
Work-in-progress PoC for CVE-2025-27840, an ESP32 Bluetooth vulnerability involving undocumented HCI commands enabling memory access and device…
 davidrxchester/smart-sketcher-upload
Exploits Bluetooth authentication bypass on smART Sketcher 2.0 toy projector, allowing unauthenticated connection and image upload via Python scripts.
 eason-zz/bluetoothducky
Exploit implementation for CVE-2023-45866 enabling unauthenticated Bluetooth keyboard injection using DuckyScript payloads on Raspberry Pi.
 olivierlaflamme/unibleed
Unitree G1 RCE PoC & Scripts (CVE-2026-76639 / CVE-2026-76640) technical details at boschko.ca/g1-ble-rce/
 m4rm0k/cve-2020-10135-bias
CVE 2020-10135 a.k.a BIAS (Bluetooth Impersonation Attack)
 danyw24/bluexploit
Exploit basado en vulnerabilidades criticas Bluetooth (CVE-2023-45866, CVE-2024-21306)
 zalexdev/wpair-app
WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…
 manaswijaiswal/reproducing-connman-1.34
CVE-2017-12865 exploit
 naren-jayram/linux-heap-based-type-confusion-in-l2cap
CVE-2020-12351
 jgoyd/ios-attack-chain-cve-2025-31200-cve-2025-31201
CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s AudioConverterService, triggered by a malicious audio file via iMessage/SMS.…
 xen0bit/fwbt
Proof of Concept code for interaction with Firewalla via Bluetooth Low-Energy and exploitation of CVE-2024-40892 / CVE-2024-40893
 nicholas-howland/cve-2026-6992-poc
Vulnerability proof of concept reworked from https://github.com/utmost3/cve/issues/2 I take no credit for discovering the vulnerability. This is for…
 goldenticketlabs/cve-2025-52413
repo for CVE-2025-52413
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025
 penthertz/cve-2025-36911-exploit
Exploit of the CVE-2025-36911 vulnerability in Python for testing our own equipment
 ynwarcs/cve-2023-23388
poc for CVE-2023-23388 (LPE in Windows 10/11 bthserv service)
 pivotchip/frostedfastpair
WhisperPair (CVE-2025-36911) POC for ESP32 device