
librepods
 librepods-org/librepods
AirPods liberated from Apple's ecosystem.
android-securitybluetooth-securityembedded-systems-security+3
30.4k5 days ago
librepods-org/librepodsAirPods liberated from Apple's ecosystem.
 yjeanrenaud/yj_nearbyglasses
attempting to detect smart glasses nearby and warn you
 sysnets/atfuzzer
Grammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…
 mretallack/androidauto
Open-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 zhuowei/blueshrimp
Proof-of-concept for CVE-2025-48593
 permissionlesstech/bitchat-android
Decentralized, encrypted peer-to-peer messaging app over Bluetooth mesh networks. No internet, servers, or phone numbers required. Features X25519 +…
 satheesh575555/system_bt_aosp10_r33_cve-2020-0413
Android Bluetooth stack (Fluoride) source code for AOSP 10, modified for CVE-2020-0413 analysis and patching.
 alwentiu/cve-2020-14292
Details of CVE-2020-14292
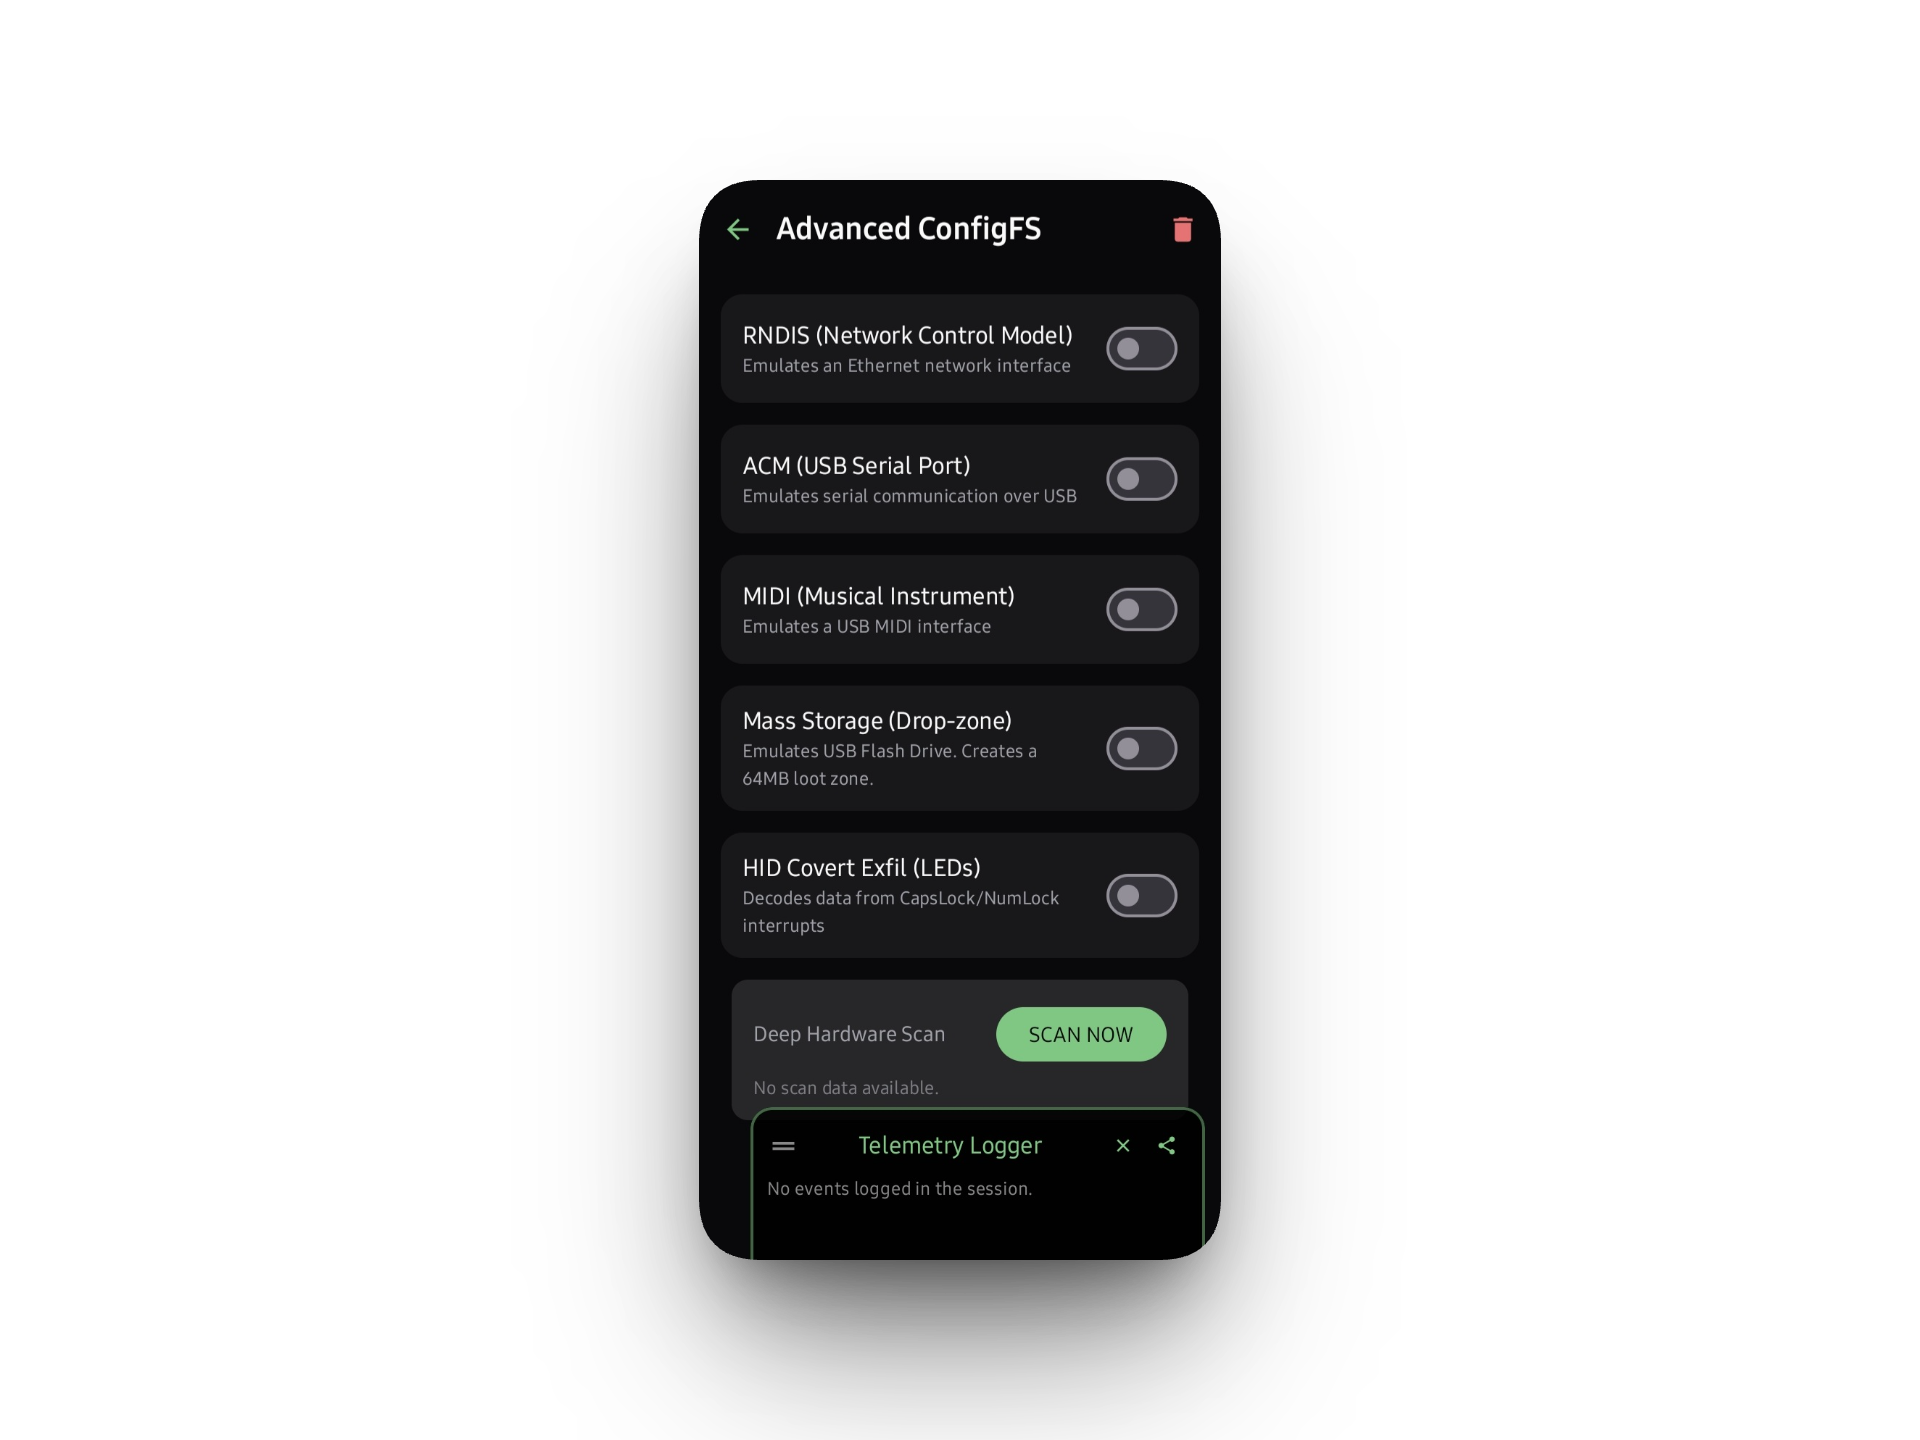 cipher-attack/chimera
Payload injector and HID emulator for Android like Hak5 and rubber ducky
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 shaikusaf/system_bt_aosp10_r33_cve-2021-0475
Android Bluetooth stack (Fluoride) with build instructions for AOSP and Linux, including dependency setup and GN/Ninja build steps.
 fo-000/bluing
An intelligence gathering tool for hacking Bluetooth
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025
 mjancek/bluebornedetection
Simple detection tool for Blueborne vulnerability found on Android devices --- CVE-2017-0781.
 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…
 nanopathi/system_bt_aosp10_r33_cve-2021-0476
Android Bluetooth stack (AOSP 10 r33) containing CVE-2021-0476 for vulnerability analysis, exploitation testing, and security research.