
flipper-mcp
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
ai-securitybluetooth-securitycommand-and-control+9
29
roostercoopllc/flipper-mcpAI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
 nccgroup/sniffle
Bluetooth 5 and 4.x LE sniffer for TI CC1352/CC26x2 hardware with support for extended advertising, all PHY modes, MAC/RSSI filtering, and PCAP…
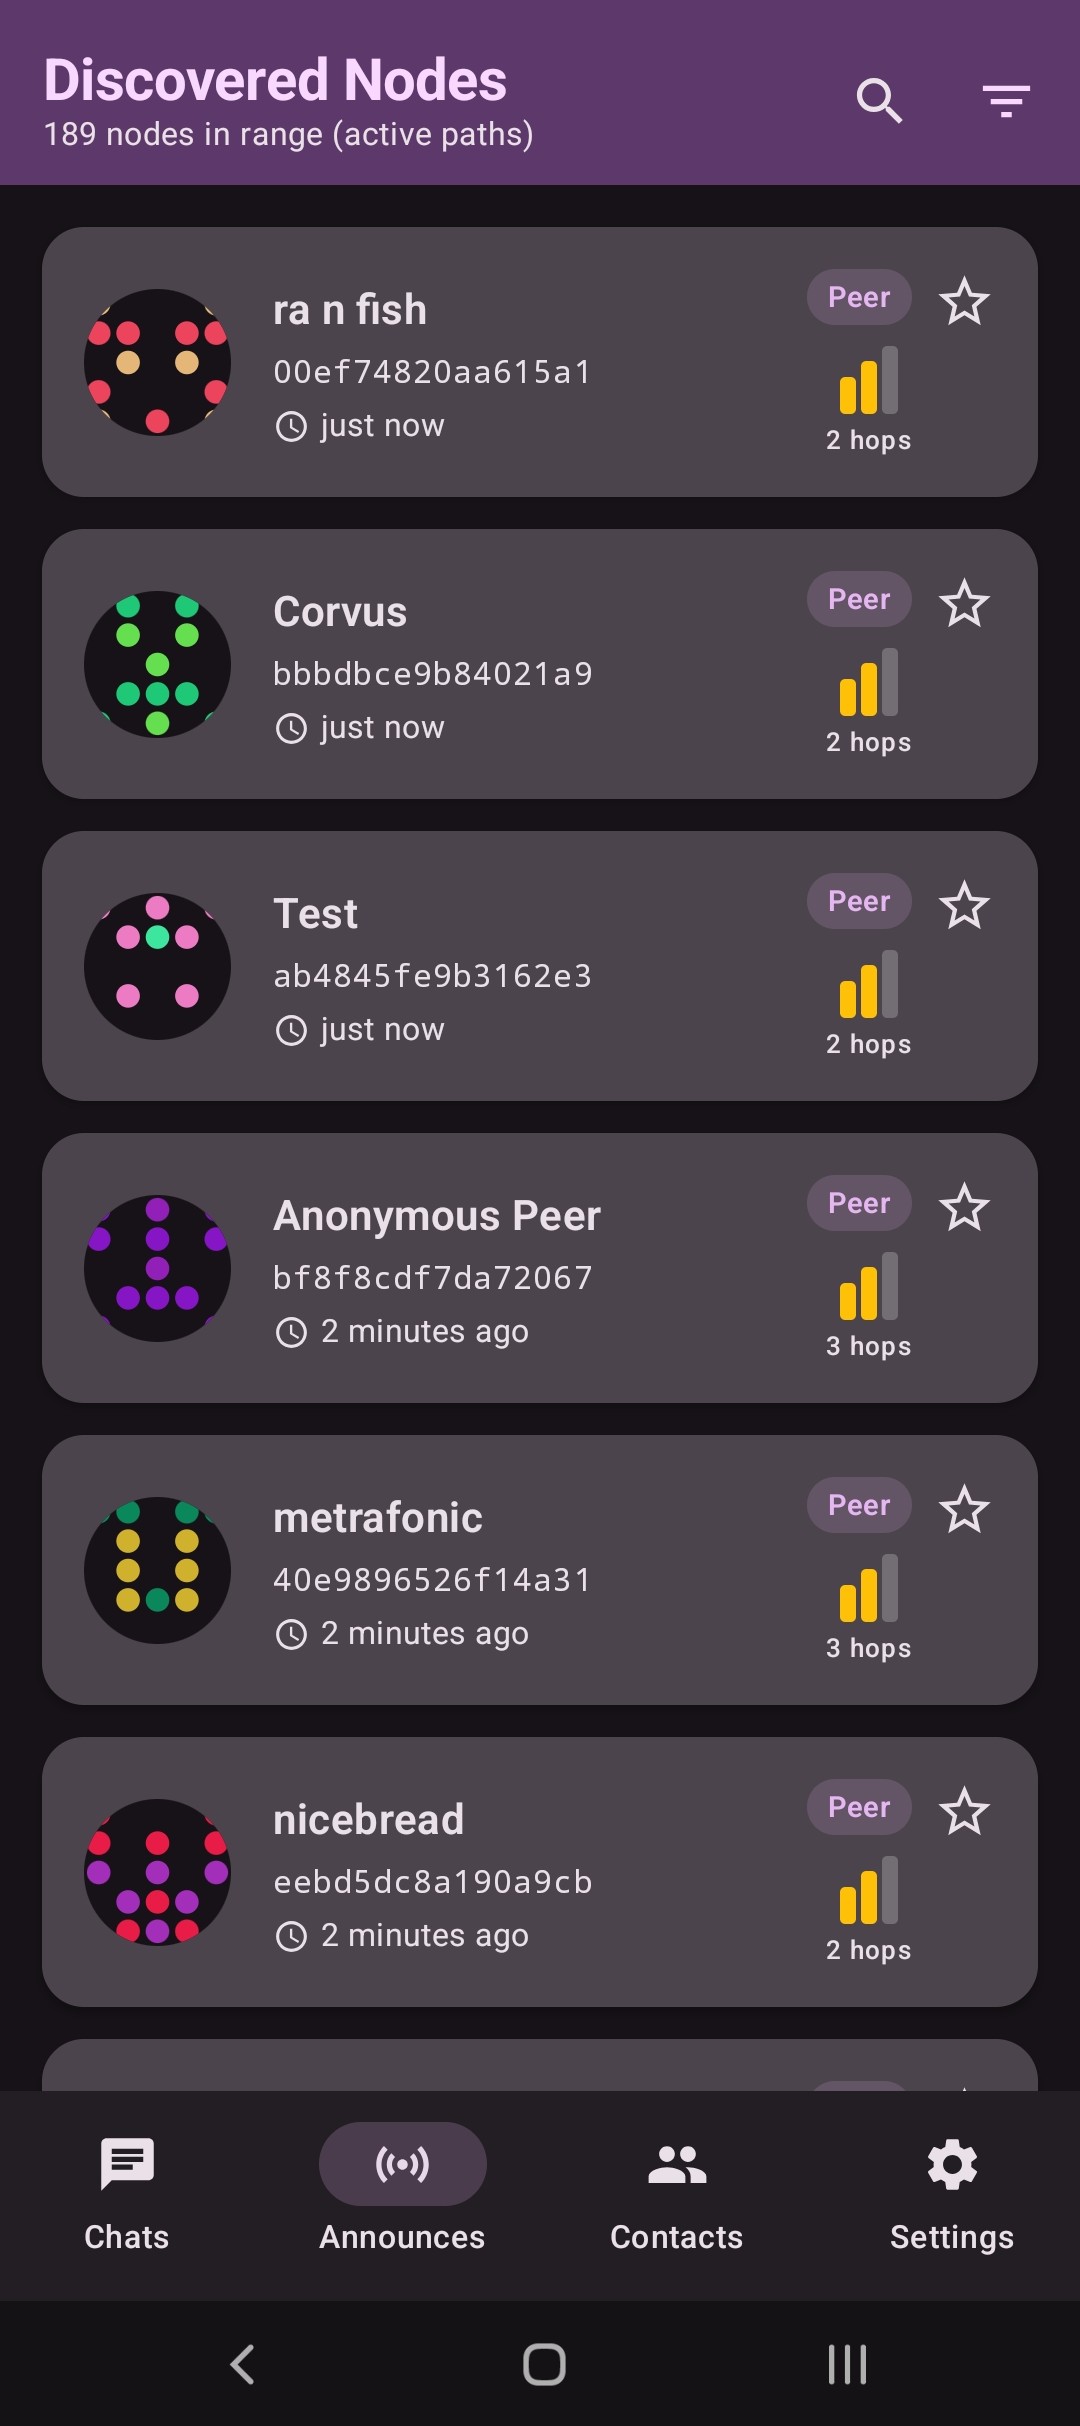 torlando-tech/columba
Native Android messaging app using Bluetooth LE, TCP, or RNode (LoRa) over LXMF and Reticulum
 wiglenet/wigle-wifi-wardriving
Nethugging client for Android, from wigle.net
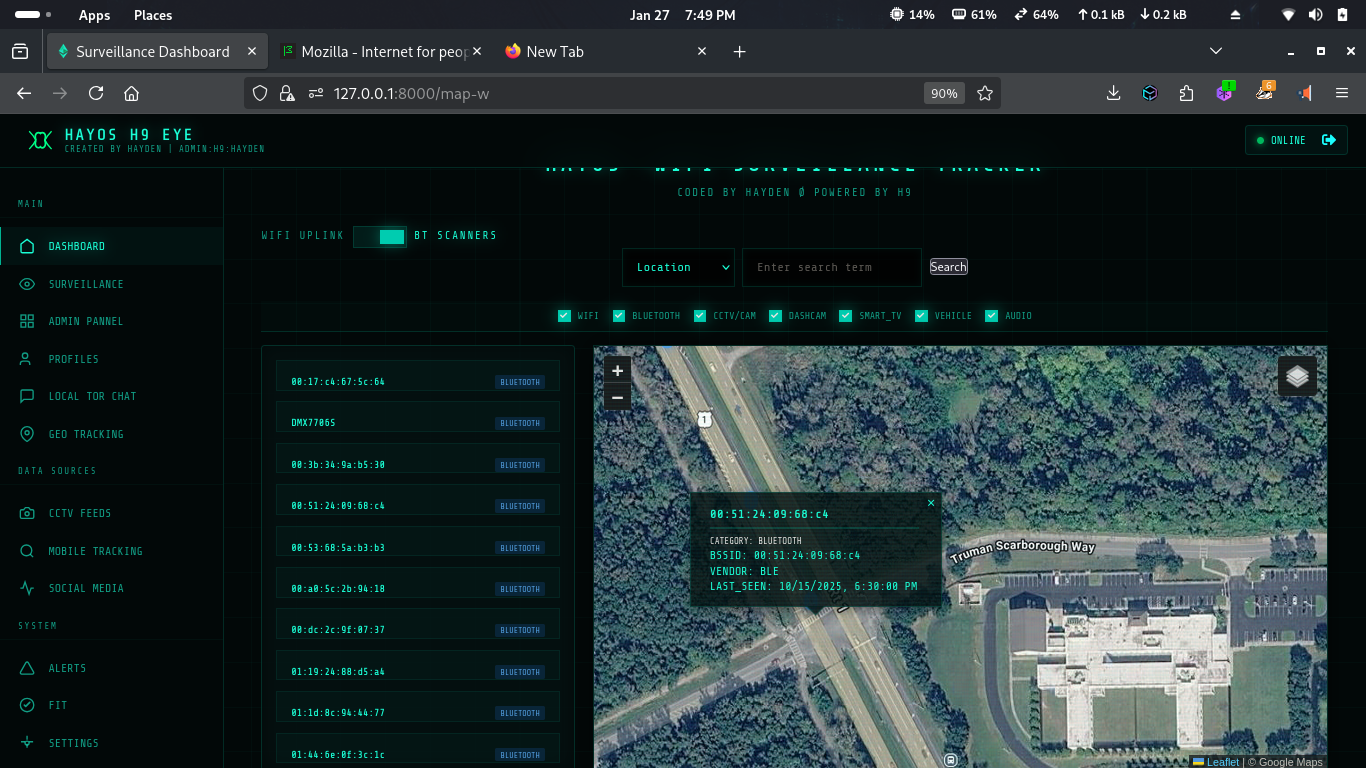 h9zdev/wiretapper
Passive wireless OSINT platform that detects and maps Wi-Fi, Bluetooth, CCTV, IoT devices, and cell towers using radio signal intelligence for…
 seemoo-lab/toothpicker
Coverage-guided in-process fuzzer for iOS Bluetooth daemon (bluetoothd) using FRIDA, with over-the-air fuzzing for MagicPairing protocol and crash…
 eternityforest/lazymesh
Proof of concept IoT/Ham Radio mesh network with global routing over the internet
 francozappa/bluffs
Toolkit for testing Bluetooth session establishment against forward and future secrecy attacks, using firmware patching, PCAP analysis, and automated…
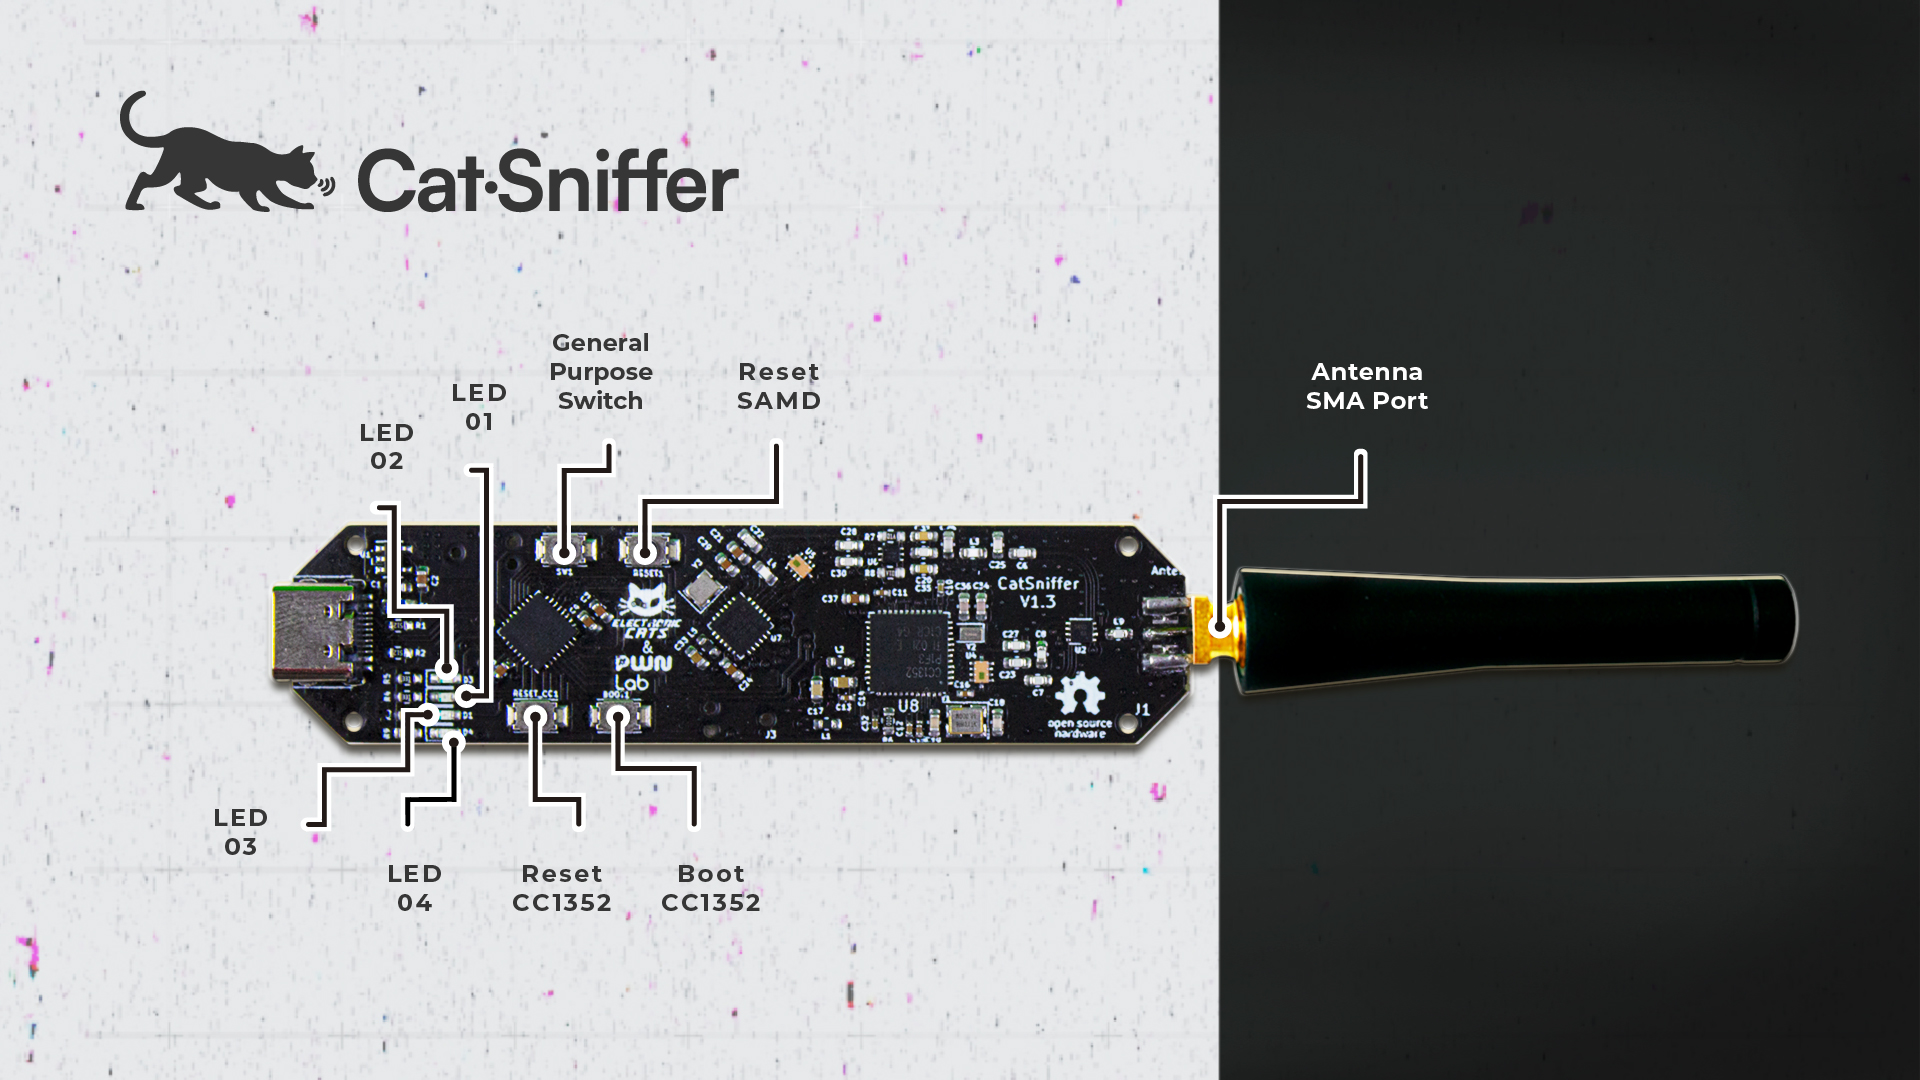 electroniccats/catsniffer
CatSniffer is an original multiprotocol and multiband board for sniffing, communicating, and attacking IoT (Internet of Things) devices using the…
 fusion1110/ebpf-hid_guard
Linux kernel-space HID injection attack detector using eBPF. Monitors USB and Bluetooth HID devices for anomalous keystroke timing and automatically…
 spectrixdev/diy_whisperpair
Hijacking Bluetooth Accessories Using Google Fast Pair: WhisperPair CVE-2025-36911 Reference Implementation & Vulnerability Verification Toolkit
 cracksoft900/blue-borne
BlueBorne Exploits & Framework This repository contains a PoC code of various exploits for the BlueBorne vulnerabilities. Under 'android' exploits…
 hackingdave/btrpa-scan
Bluetooth Low Energy (BLE) scanner with Resolvable Private Address (RPA) resolution using Identity Resolving Keys (IRKs)
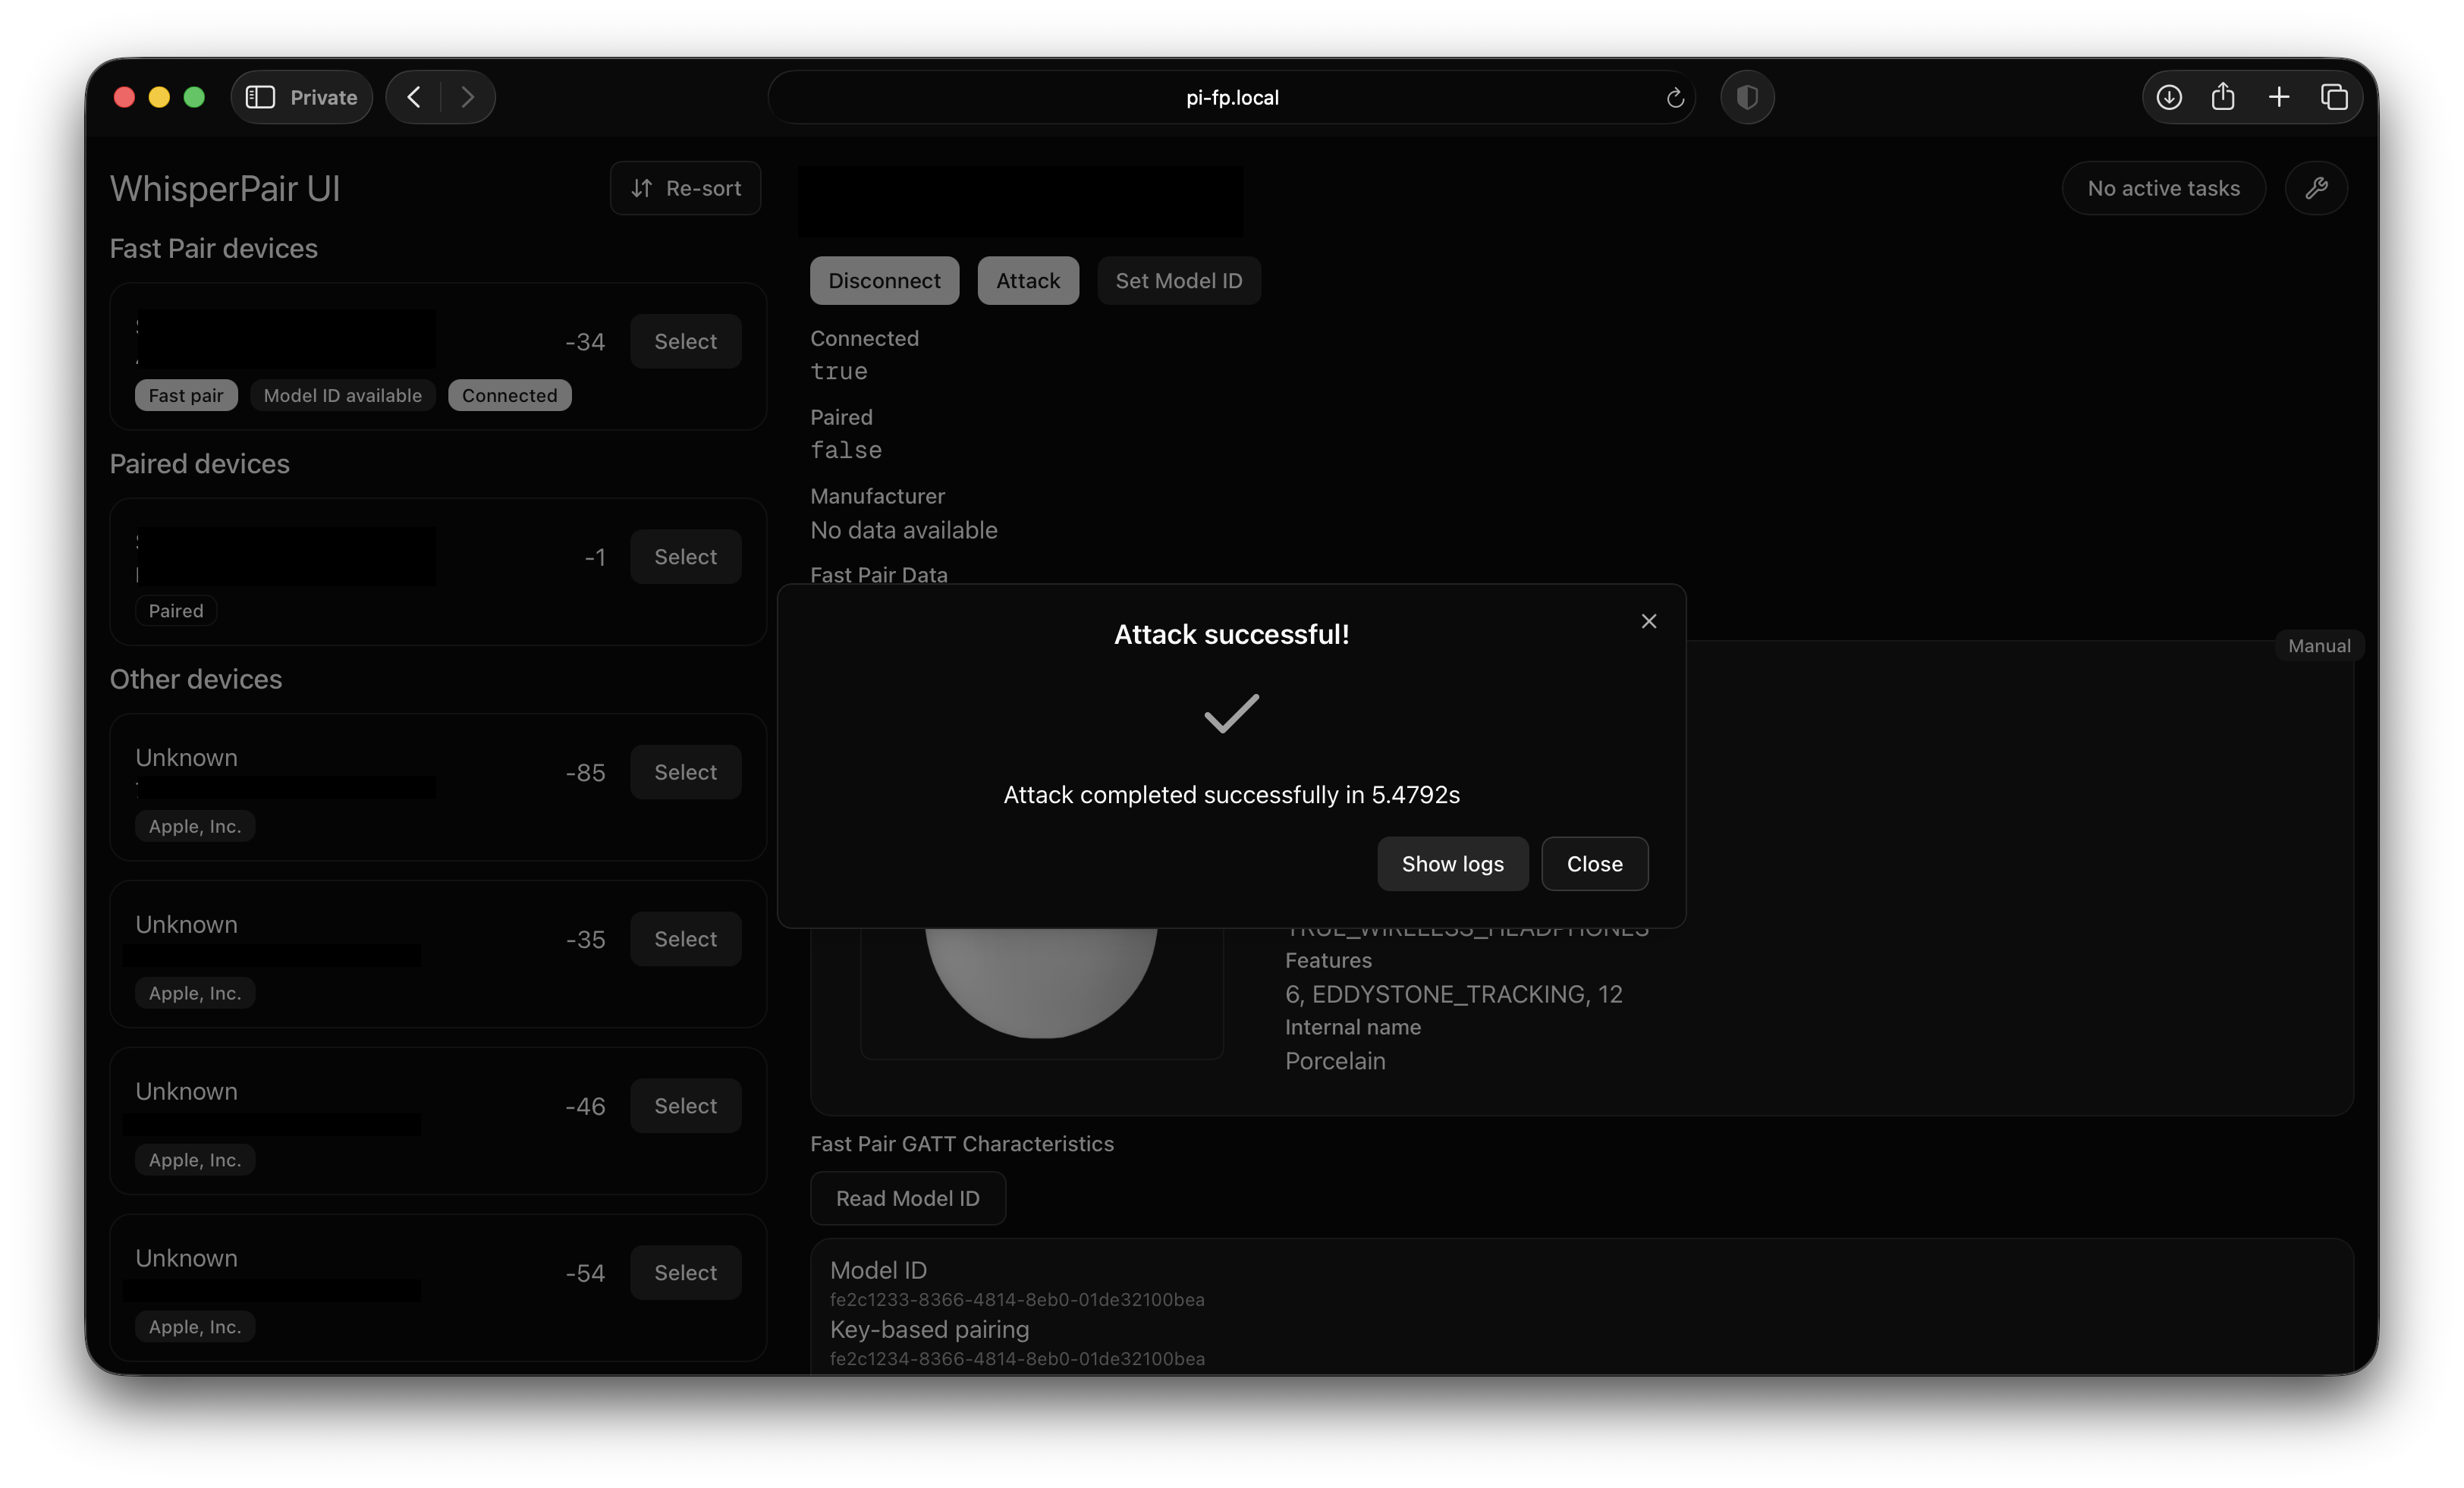 kuleuven-cosic/whisperpair
The official reference implementation & vulnerability verification of our attack WhisperPair (CVE-2025-36911) which affects Google's Fast Pair…
 steampunk424/cve-2025-36911-wisper_pair_target_finder
This is not an exploit for CVE-2025-36911!!! This is a detector for finding potentially vulnerable devices! Only use on your own devices! I am not…
 securing/gattacker
A Node.js package for BLE (Bluetooth Low Energy) security assessment using Man-in-the-Middle and other attacks
 d4rks1d33/c-poc-for-cve-2024-21306
Proof-of-concept exploit for CVE-2024-21306 targeting Bluetooth stacks. Demonstrates vulnerability exploitation via Bluetooth interface manipulation…
 pentestfunctions/blueducky
🚨 CVE-2023-45866 - BlueDucky Implementation (Using DuckyScript) 🔓 Unauthenticated Peering Leading to Code Execution (Using HID Keyboard)