
CVE-2025-8088-Winrar-Tool
 onlytoxi/cve-2025-8088-winrar-tool
Advanced WinRAR Path Traversal Exploit Tool for CVE-2025-8088
binary-exploitationeducationexploitation+5
55
onlytoxi/cve-2025-8088-winrar-toolAdvanced WinRAR Path Traversal Exploit Tool for CVE-2025-8088
 redcrazyghost/cve-2026-42945
Go-based exploit tool for CVE-2026-42945 (nginx HTTP/2) with detection, crash probing, command execution, and reverse shell capabilities for…
 io12/pwninit
Automates setup of binary exploitation challenges by patching ELF binaries, fetching matching linkers, unstripping libc, and generating pwntools…
 kitsuneshade/winrar-exploit-tool---rust-edition
A high-performance, memory-safe implementation of the WinRAR CVE-2025-8088 exploit tool, rewritten in Rust for better reliability and performance.
 chanbin/cve-2017-11882
Microsoft Equation 3.0/Convert python2 to python3
 techcorp/cve-2025-8088-exploit
A proof-of-concept exploit for WinRAR vulnerability (CVE-2025-8088) affecting versions 7.12 and lower. This tool creates a malicious RAR archive that…
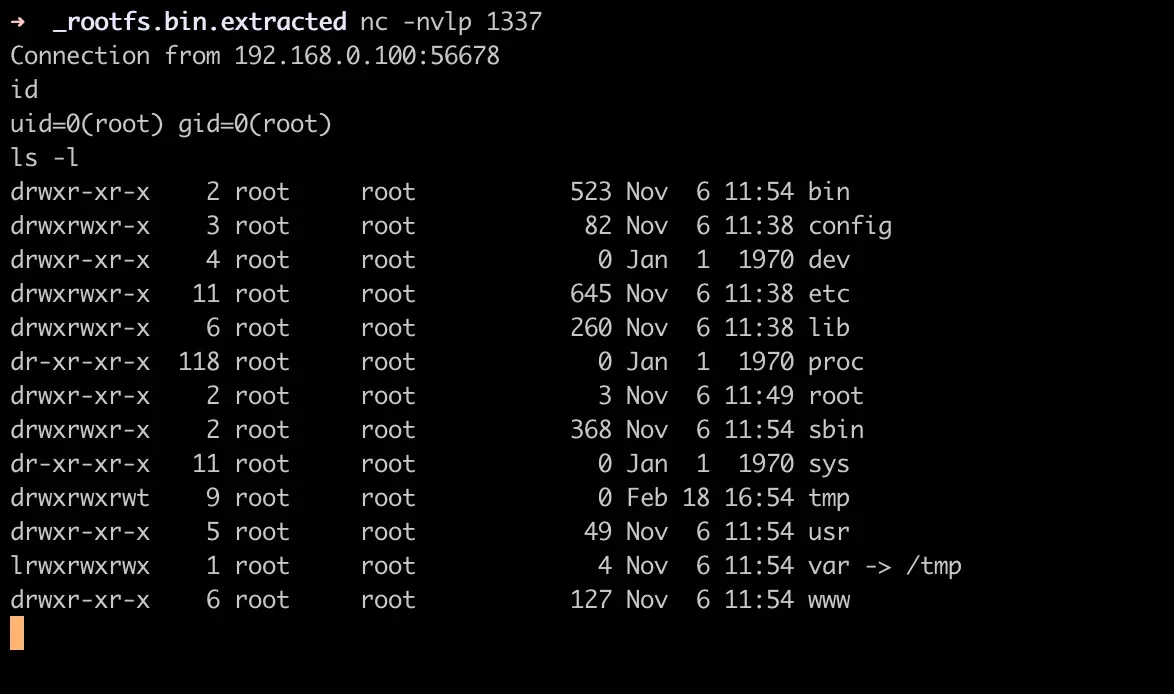 ii4gsp/cve-2026-1457
Provides a detailed analysis and proof-of-concept for CVE-2026-1457, an authenticated buffer overflow in TP-Link VIGI C385 web API leading to remote…
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
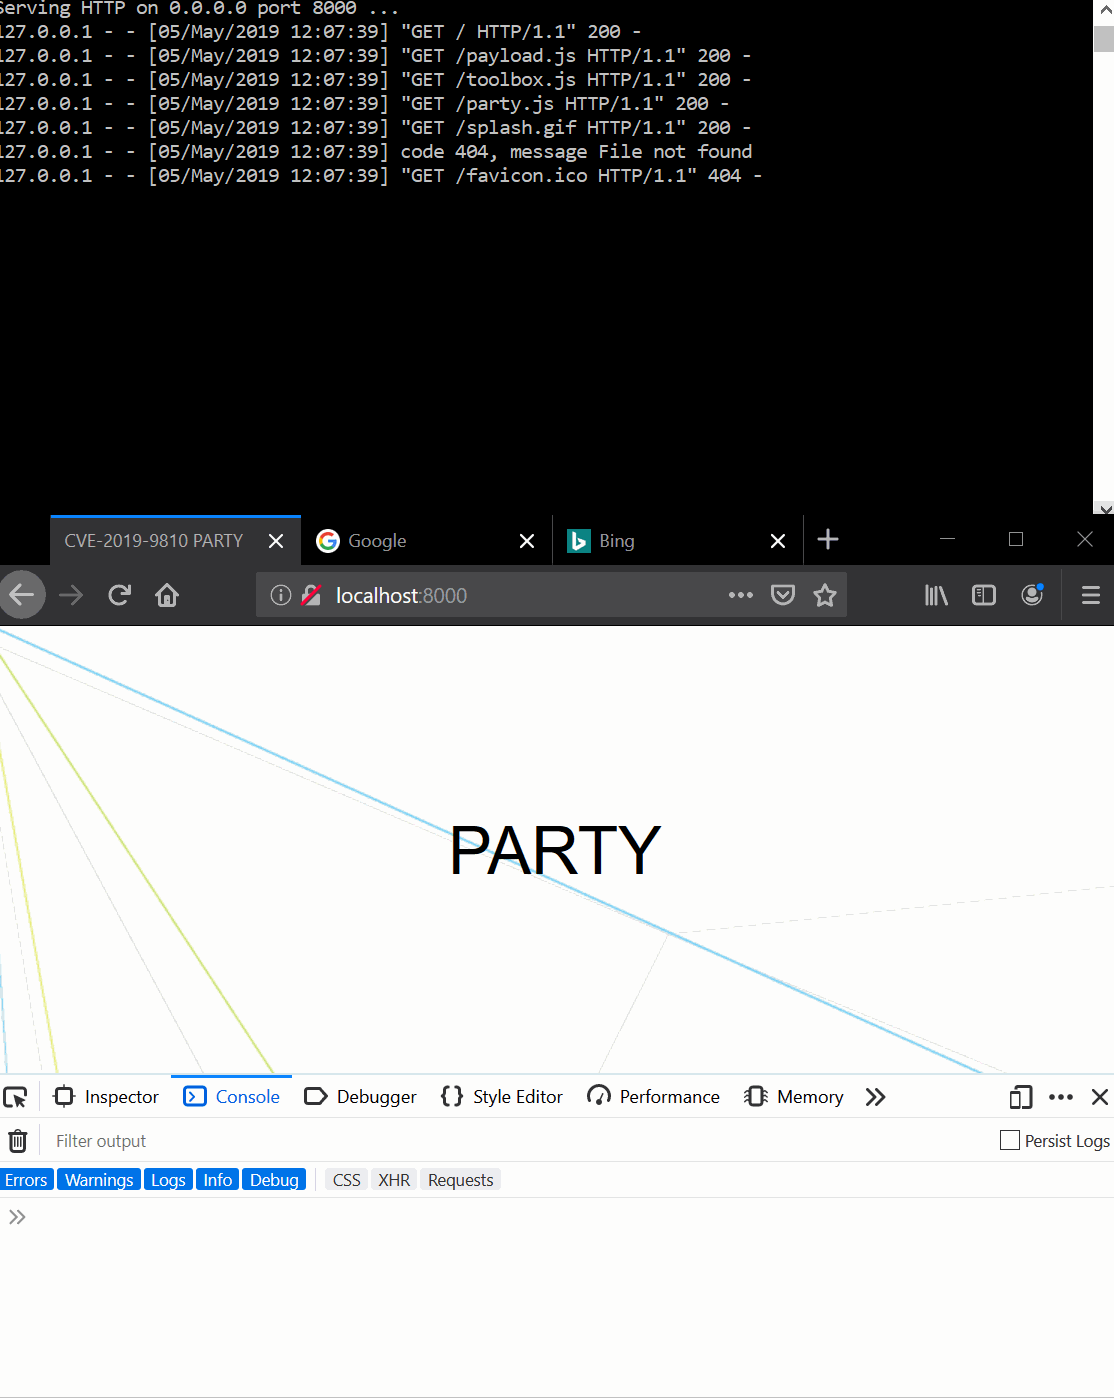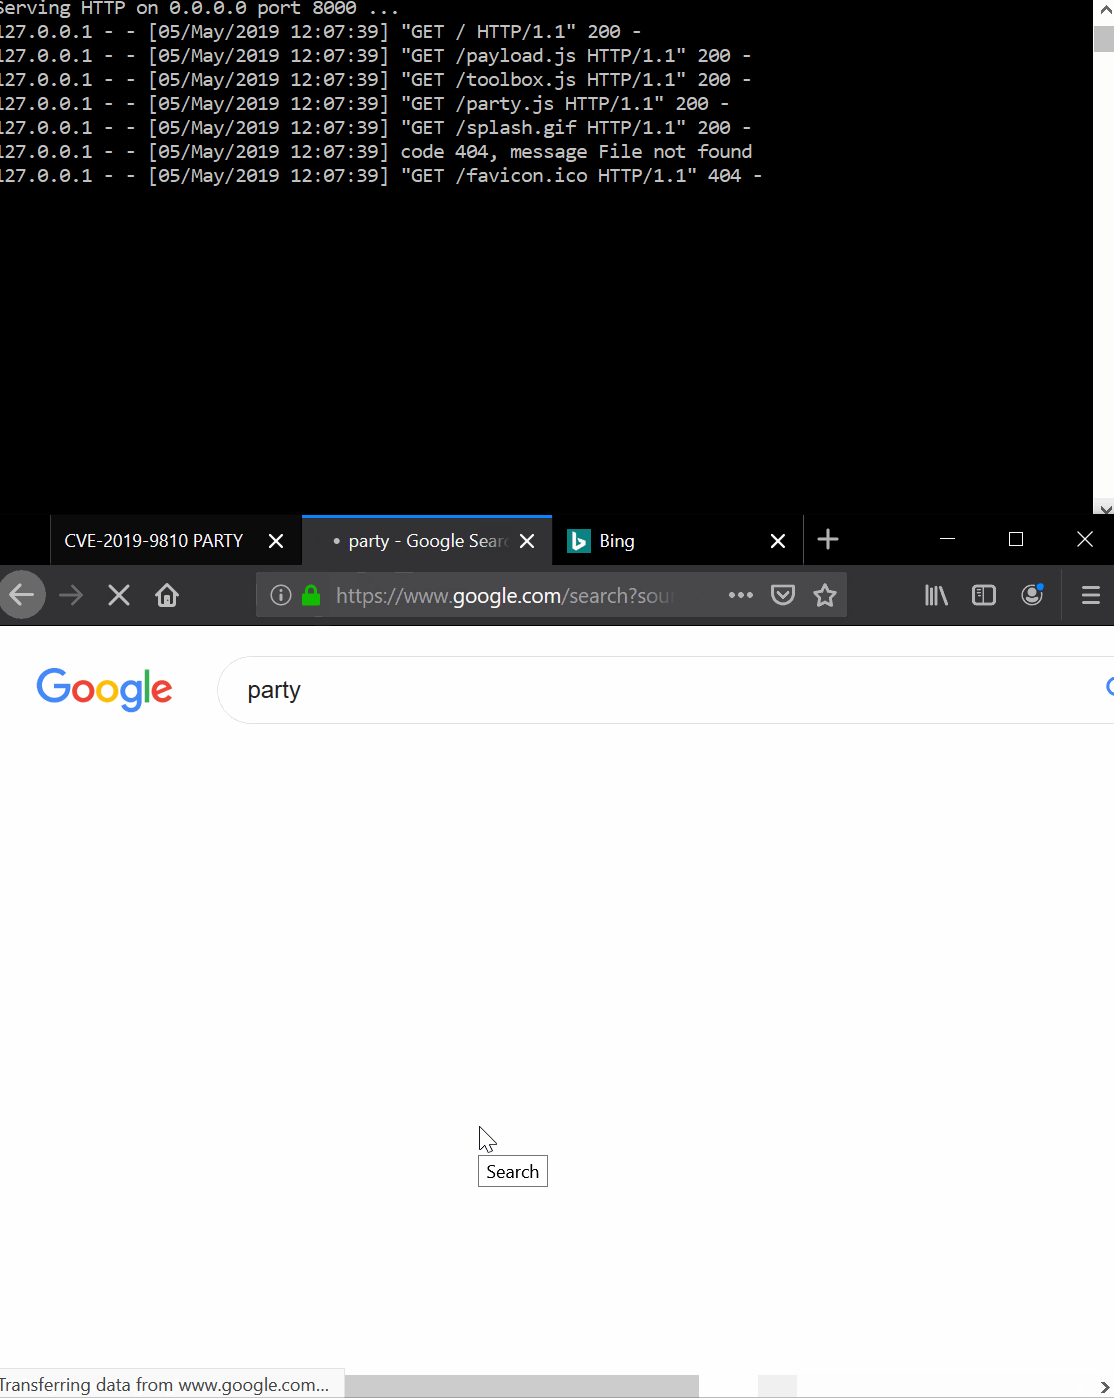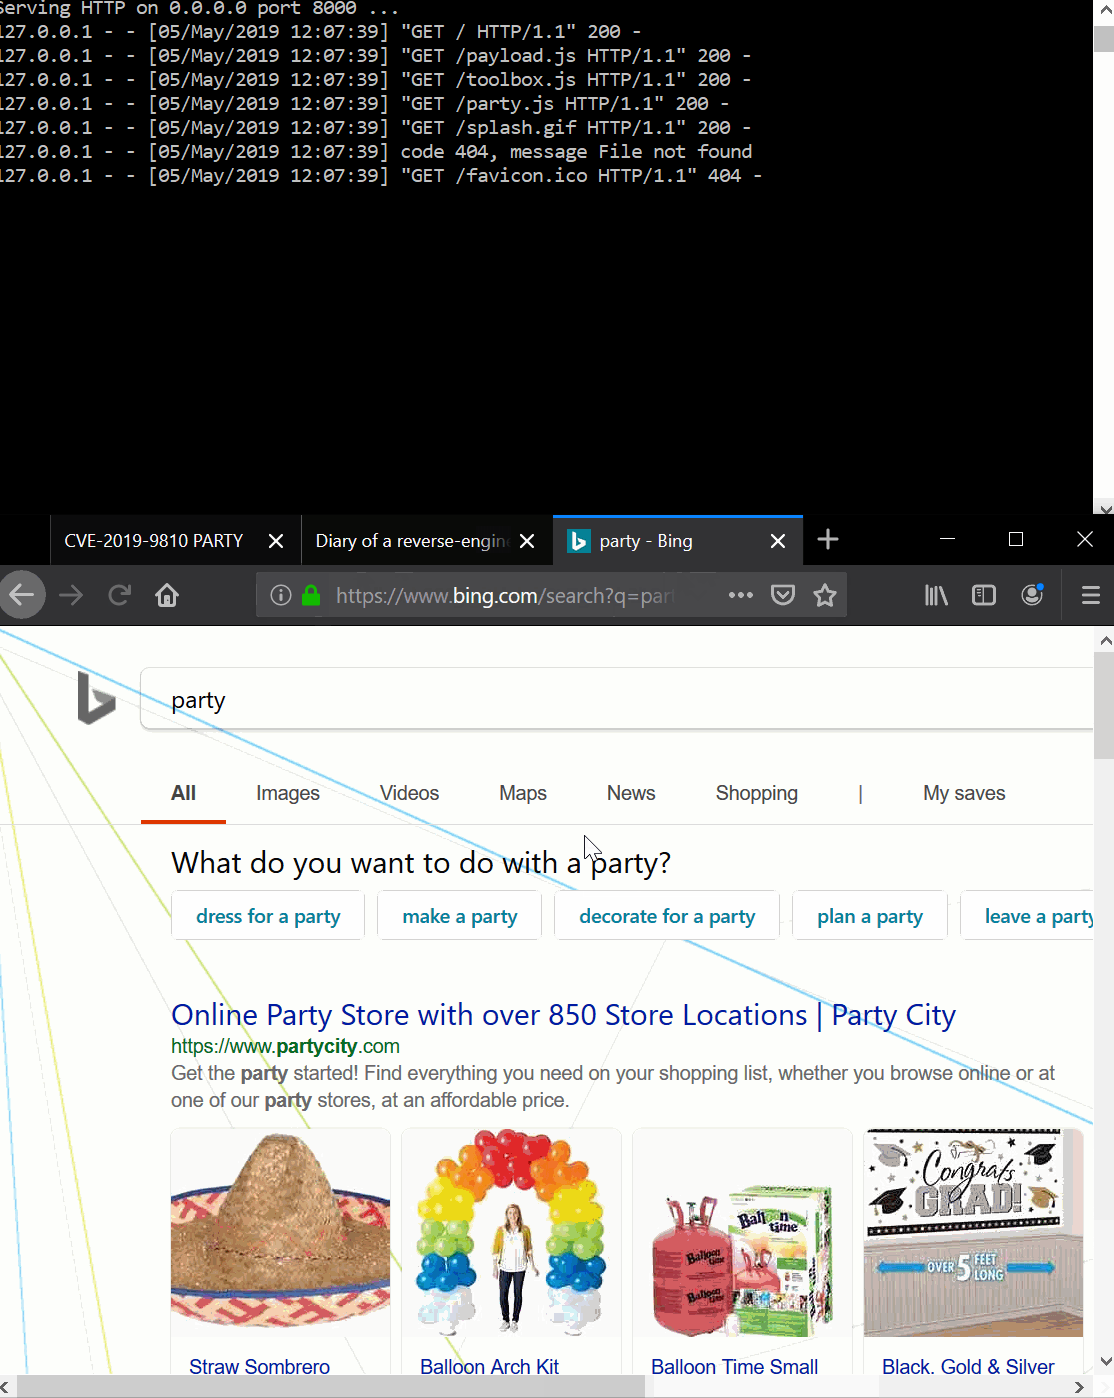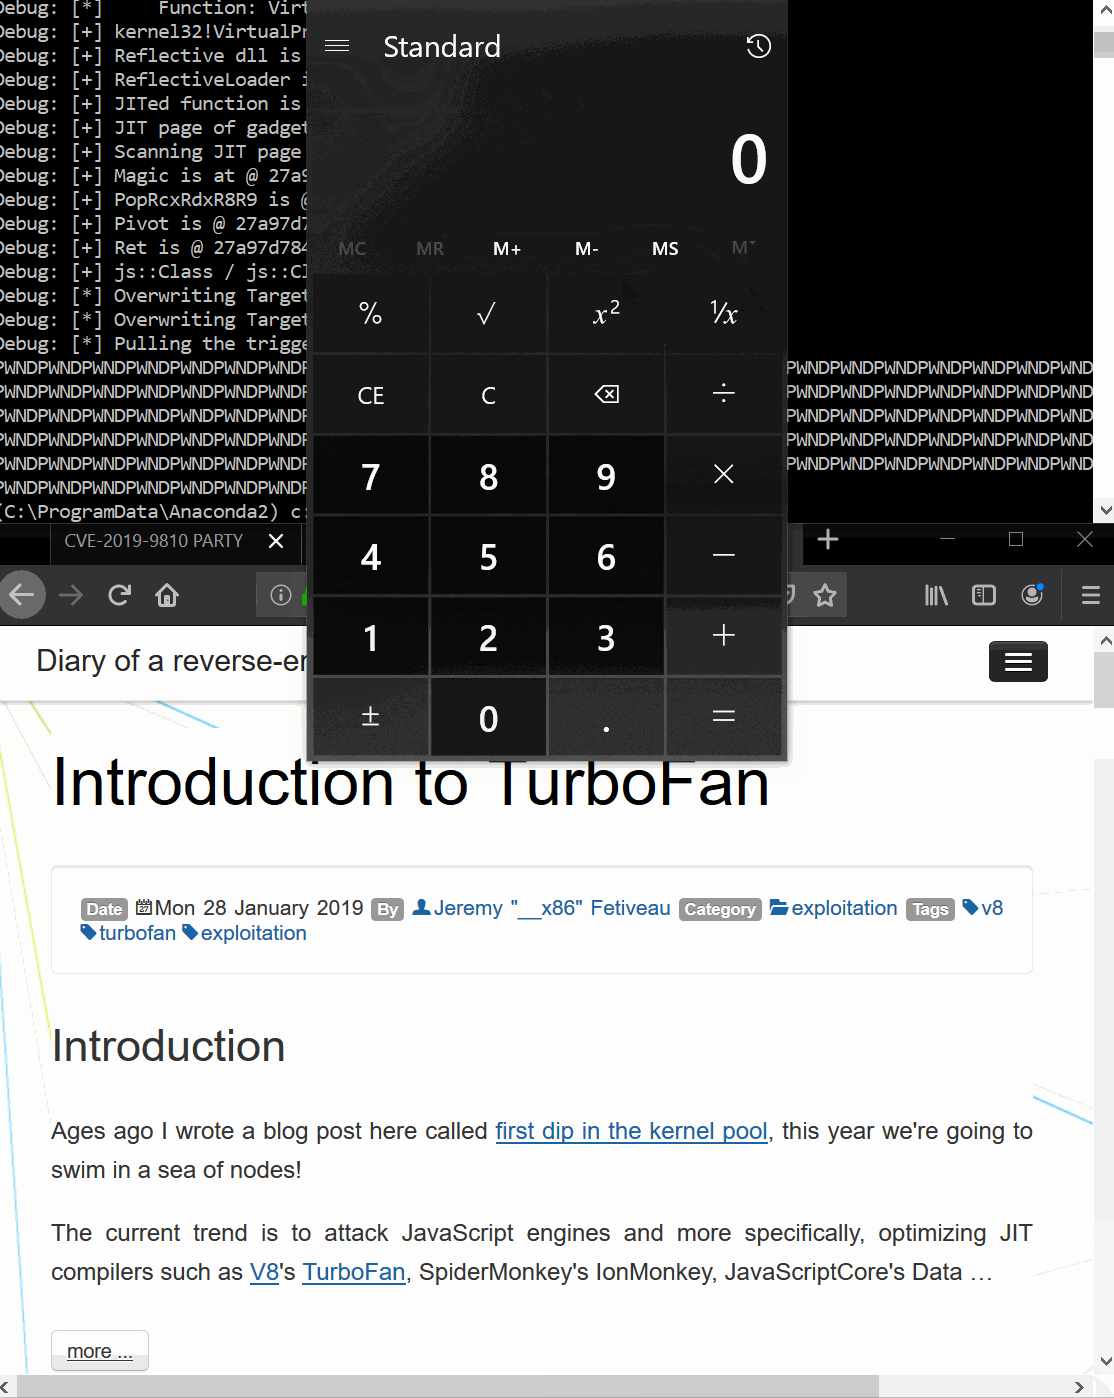 0vercl0k/cve-2019-9810
Exploit for CVE-2019-9810 Firefox on Windows 64-bit.
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 jbaines-r7/badblood
SonicWall SMA-100 Unauth RCE Exploit (CVE-2021-20038)
 threedr3am/learnjavabug
Java安全相关的漏洞和技术demo,原生Java、Fastjson、Jackson、Hessian2、XML反序列化漏洞利用和Spring、Dubbo、Shiro、CAS、Tomcat、RMI、Nexus等框架\中间件\功能的exploits以及Java Security…
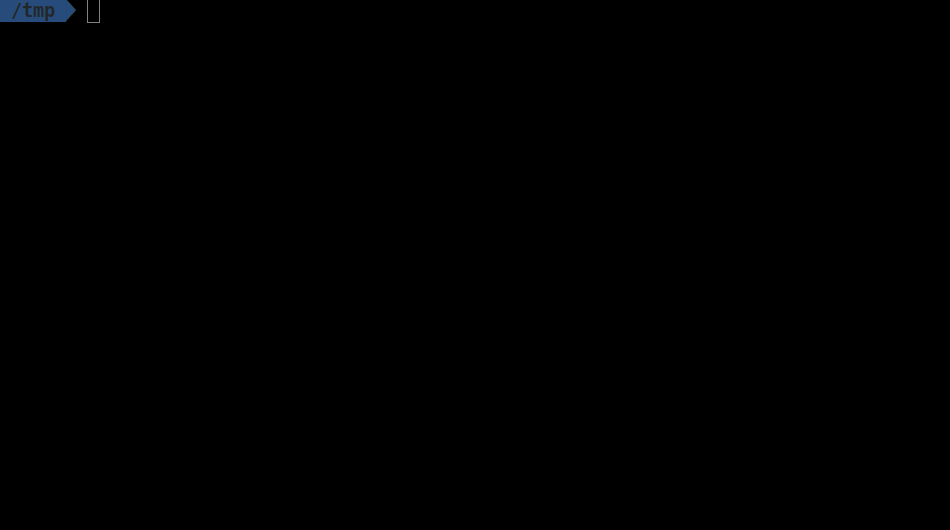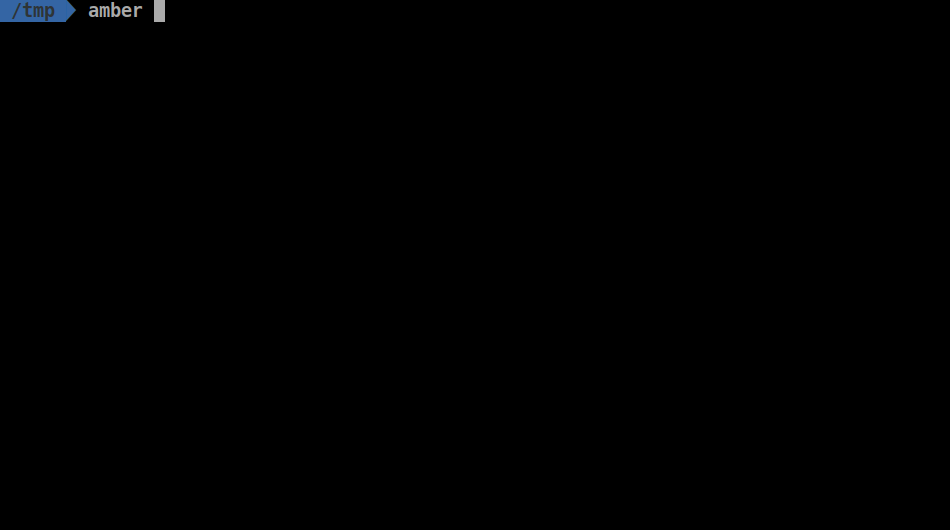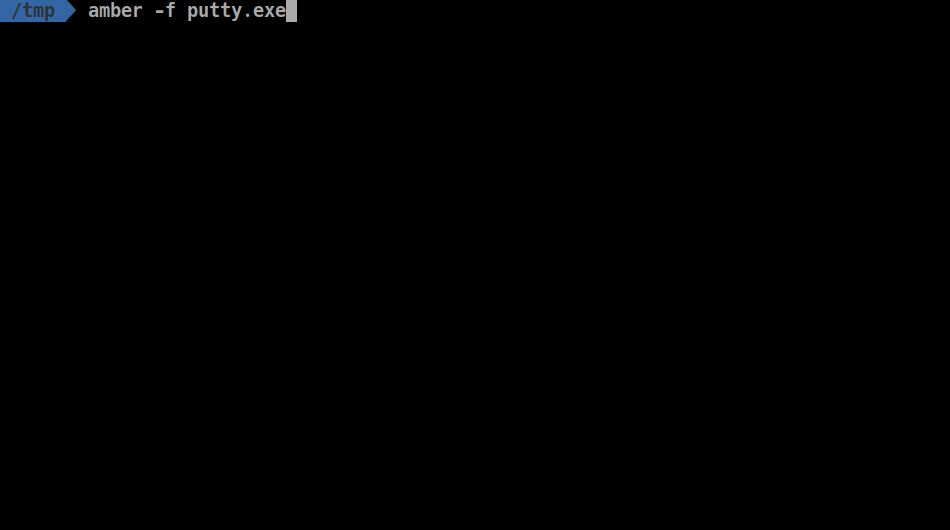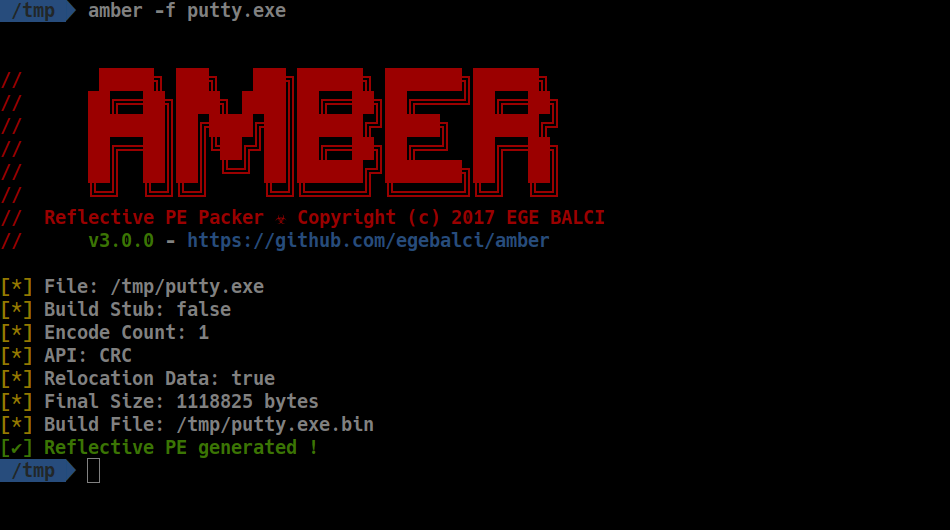 egebalci/amber
Reflective PE packer.
 h4x0r-dz/cve-2024-21762
out-of-bounds write in Fortinet FortiOS CVE-2024-21762 vulnerability
 dkstar11q/cve-2024-27130-poc
CVE-2024-27130是影响QNAP网络附加存储(NAS)设备的一个严重漏洞。该漏洞源于QTS操作系统中share.cgi脚本的No_Support_ACL函数中不安全地使用strcpy函数,导致堆栈缓冲区溢出。攻击者可以利用此漏洞,通过精心构造的请求在目标系统上执行任意代码,进而完全控制受影…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 vyahello/cve-2026-31431
Linux local privilege escalation exploit for CVE-2026-31431, abusing the AF_ALG crypto API with splice() to modify page cache and spawn a root shell.