
CVE-2021-35211
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
binary-exploitationexploitationexploit-frameworks+6
39
bishopfox/cve-2021-35211Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 ycdxsb/cve-2020-0668
Make CVE-2020-0668 exploit work for version < win10 v1903 and version >= win10 v1903
 jmousqueton/cve-2023-21716
POC : CVE-2023-21716 Microsoft Word RTF Font Table Heap Corruption
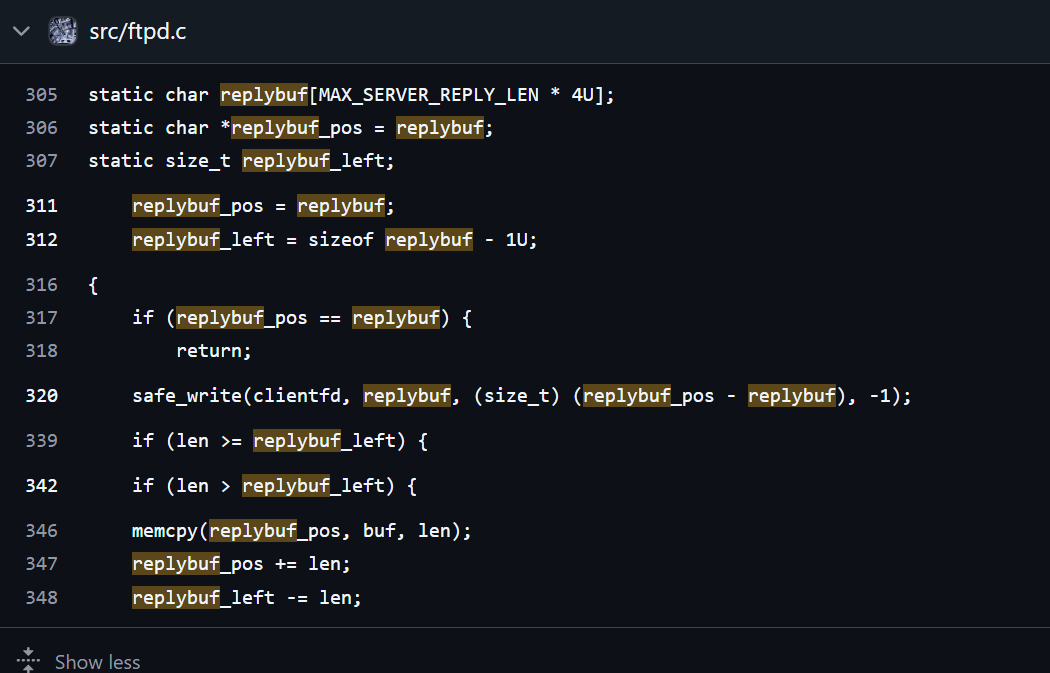 rohilchaudhry/cve-2024-48208
This repo contains all the work surrounding the development of the PoC for CVE-2024-48208, and how a simple OOB(Out-of-bound) read can result in jail…
 hv0l/cve-2023-21716_exploit
Proof-of-concept exploit for CVE-2023-21716, a critical remote code execution vulnerability in Microsoft Word. Demonstrates exploitation of the…
 0xrootpls/givemekernel
CVE-2024-35250 PoC - Optimized & Condensed Form of Varwara's PoC
 bugel/cve-2026-43499-m3q-azf1
This package is not a complete root. It flips SELinux to Permissive and holds reclaim long enough for follow-on work. Host `uid=0` is not achieved…
 ronf98/cve-2023-21716-poc
Proof Of Concept for CVE-2023-21716 Microsoft Word Heap Corruption
 gmh5225/cheat-engine-undetectable
Academic Research Edition - T1: User-mode evasion (obfuscation + syscall gateway), T2: BYOVD kernel bridge, T3: DMA hardware (future work).
 tufanturhan/cve-2022-21971-windows-runtime-rce
Proof-of-concept exploit for CVE-2022-21971, an uninitialized pointer free vulnerability in Windows Runtime's prauthproviders.dll, triggered via…
 spiralbl0ck/nday_cve_2016_8823
PoC under work, CVE-2016-8823
 wired0ut/cve-2020-0423
An exploit to CVE-2020-0423, which is a Binder deffered work UAF.
 it19083124/snp-assignment
Exploit work Privilege Escalation CVE-2017-1000112
 reggyraider/cve-2023-21716
CVE-2023-21716 - Microsoft Word RTF fonttbl Heap Corruption RCE exploit with reverse shell payload
 spiralbl0ck/cve-2022-37332-rce-
CURRENTLY UNDER WORK... ALL I NEED TO IMPLEMENT IS JIT SPRAYING .....
 bad3r/cve-2021-3156-without-ip-command
fork of worawit/CVE-2021-3156 exploit_nss.py modified to work with ifconfig instead of the ip command
 p4x1s/cve-2023-21716-poc
Microsoft Word 远程代码执行漏洞
 tiagob0b/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…