ElfDoor-gcc
LD_PRELOAD-based tool that hijacks gcc to inject malicious code into binaries during linking, enabling stealthy backdoor deployment without source…

LD_PRELOAD-based tool that hijacks gcc to inject malicious code into binaries during linking, enabling stealthy backdoor deployment without source…

DirtyPipe: Exploit for a new Linux vulnerability known as 'Dirty Pipe(CVE-2022-0847)' allows local users to gain root privileges. The vulnerability…

A Bash-based privilege escalation exploit targeting the `below` system performance monitoring tool. This refurbished exploit leverages a symlink…

Injects code into ELF executables post-build


I'll submit the poc after blackhat

Proof-of-concept exploit for CVE-2015-1528 demonstrating privilege escalation on Android 5.0 via binder call fuzzing, with staged code injection into…

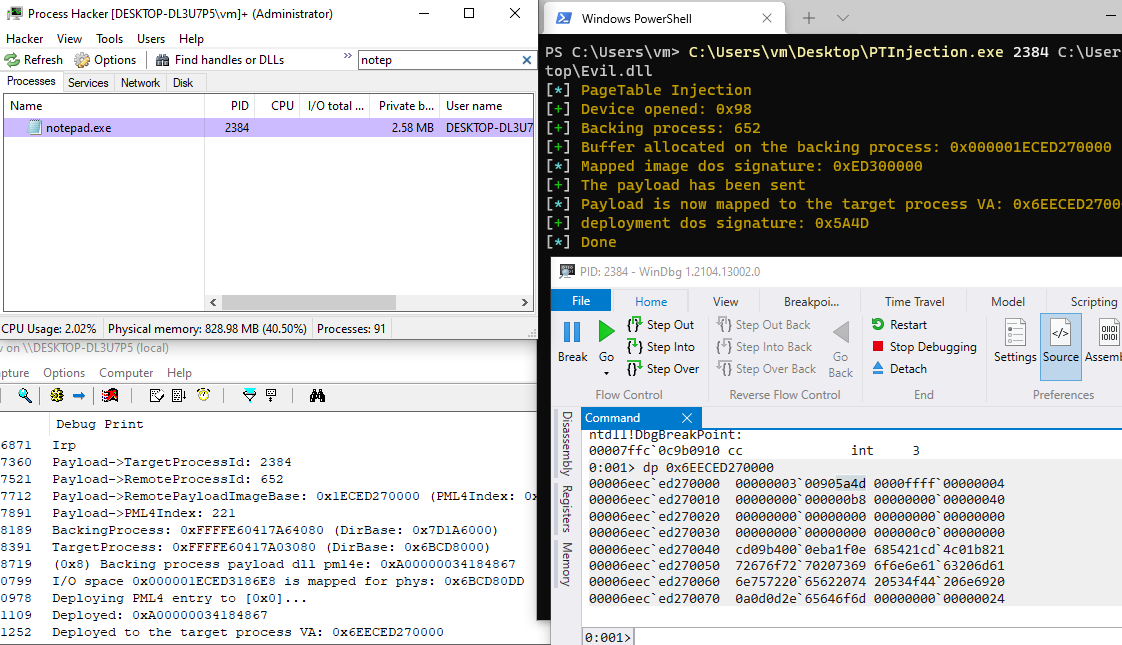
Code Injection, Inject malicious payload via pagetables pml4.