
cve-2015-1592
 lightsey/cve-2015-1592
Metasploit modules and payload generation files from my Houston Perl Mongers talk about this vulnerability.
binary-exploitationeducationexploit-frameworks+3
6
lightsey/cve-2015-1592Metasploit modules and payload generation files from my Houston Perl Mongers talk about this vulnerability.
 etahen/etahen
PS5 homebrew enabler payload offering post-exploitation features: custom plugin/payload loading, unsigned fself/fpkg support, debug settings, FTP…
 johnhammond/cve-2021-34527
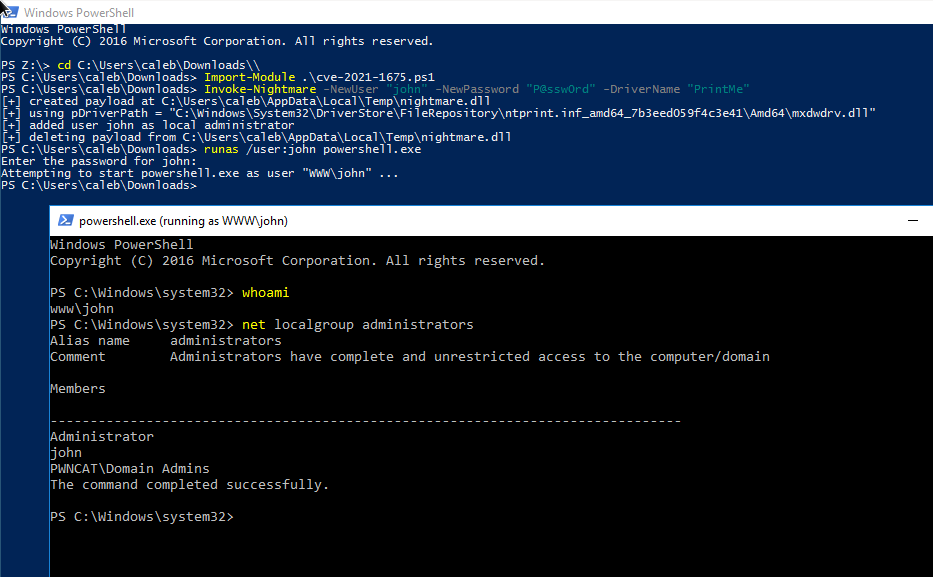
PowerShell script for local privilege escalation via PrintNightmare (CVE-2021-34527). Injects a custom DLL payload to add a local admin user,…
 hexx0r/cve-2016-0051
Proof-of-concept exploit for CVE-2016-0051 (MS16-016) achieving local privilege escalation to SYSTEM on Windows 7, with compiled binaries and…
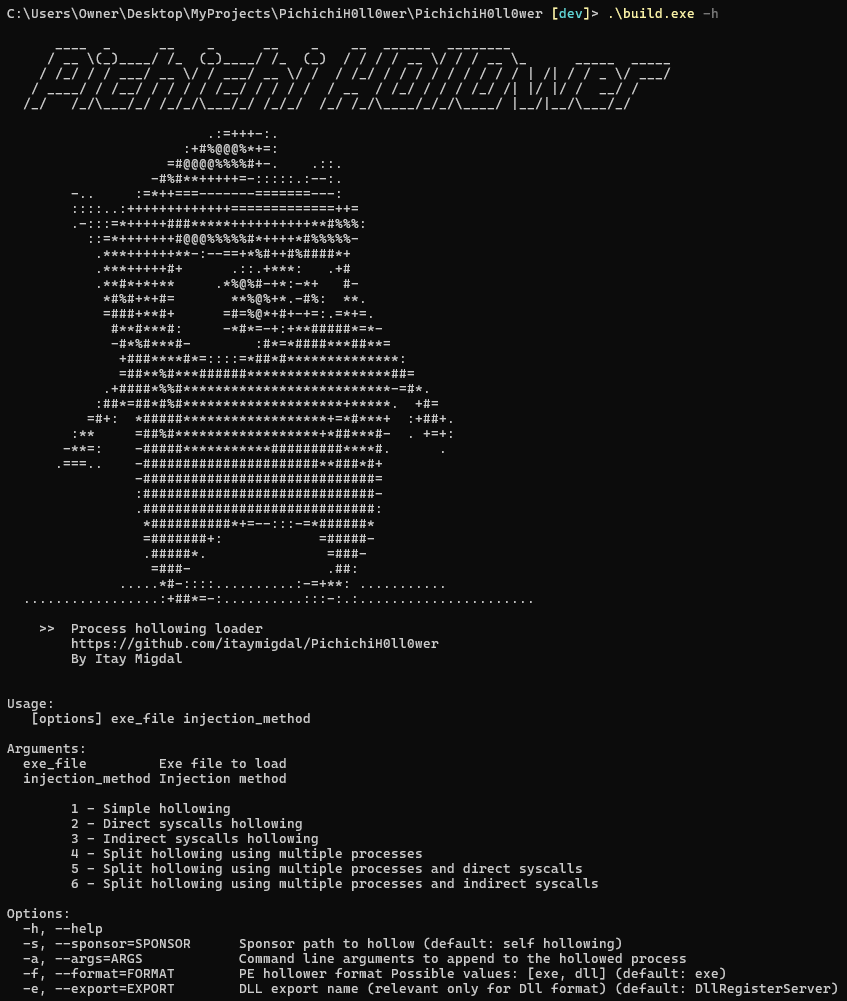 itaymigdal/pichichih0ll0wer
Nim-based process hollowing loader for PE executables with configurable injection methods, direct/indirect syscalls, anti-debug, payload encryption,…
 watchtowrlabs/watchtowr-vs-watchguard-cve-2025-9242
Python-based detection artifact generator and exploit for WatchGuard Fireware OS CVE-2025-9242, an unauthenticated IKEv2 out-of-bounds write…
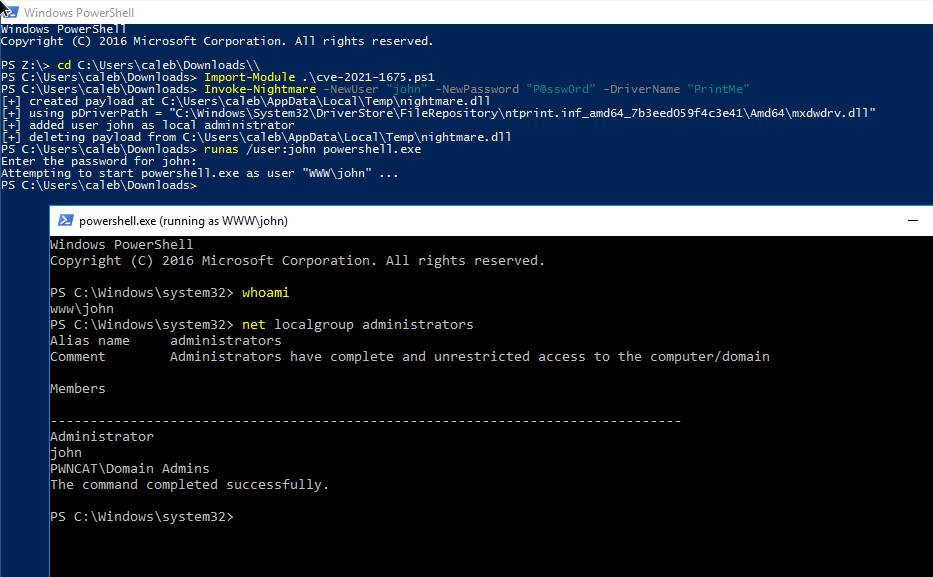 thomasgeens/cve-2021-1675
PowerShell exploit for CVE-2021-1675 (PrintNightmare) performing local privilege escalation via Print Spooler, with custom DLL payload injection to…
 dgndrn/cve-2023-4590
Proof-of-concept exploit for a SEH buffer overflow vulnerability (CVE-2023-4590) in Frhed hex editor v1.6.0. Generates a malicious payload file to…
 lipeozyy/cve-2017-14980_syncbreeze_10.0.28_bof
Proof-of-concept buffer overflow exploit for Sync Breeze Enterprise v10.0.28 (CVE-2017-14980). Sends crafted HTTP POST payload to overwrite EIP and…
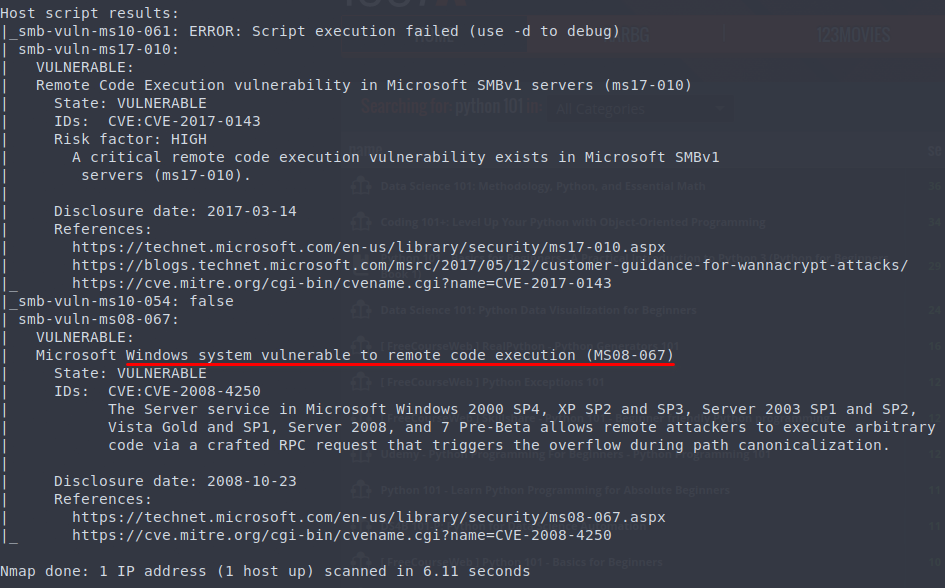 h3x0v3rl0rd/ms08-067
Python-based exploit for MS08-067 (CVE-2008-4250) providing remote code execution via SMB with reverse shell payload generation and automatic target…
 helios973/cve-2026-31431_exp.c
C exploit for CVE-2026-31431 providing privilege escalation through a custom binary payload. Designed for testing and validation of the vulnerability.
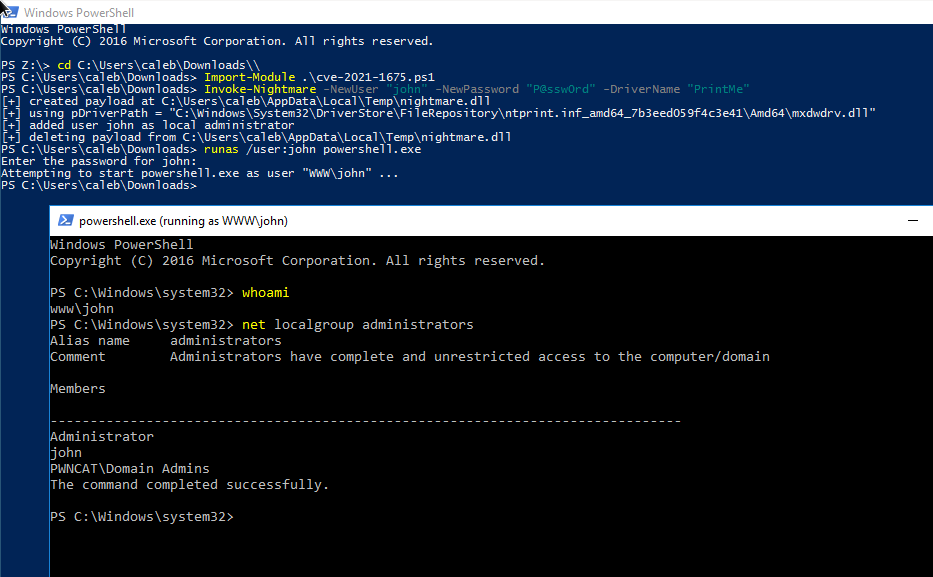 whoami-chmod777/cve-2021-1675-cve-2021-34527
PowerShell exploit for PrintNightmare (CVE-2021-1675) performing local privilege escalation via Print Spooler, with custom DLL payload injection to…
 cyb3rpeace/cve-2021-34527
PowerShell local privilege escalation exploit for PrintNightmare (CVE-2021-34527) targeting Windows Print Spooler. Embeds custom DLL payload to add…
 mr-alperen/cve-2022-26810
Remote code execution exploit for CVE-2022-26809 targeting Windows RPC heap buffer overflow with msfvenom shellcode integration and meterpreter…
 nikip72/cve-2021-4034
Statically linked implementation of the CVE-2021-4034 privilege escalation exploit, with encoded payload written to disk and no gcc dependency.
 rnnsz/cve-2017-15950
Proof-of-concept exploit for CVE-2017-15950, a stack-based buffer overflow in SyncBreeze XML parser and sync functionality. Includes Python payload…
 rnnsz/cve-2008-4654
PoC exploit generator for CVE-2008-4654, a stack-based buffer overflow in VLC Media Player via crafted .ty+ files. Generates malicious payload file…
 rnnsz/cve-2017-8367
Python-based proof-of-concept exploit for CVE-2017-8367, a stack-based buffer overflow in Easy Mov Converter. Generates a payload file for local…